Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
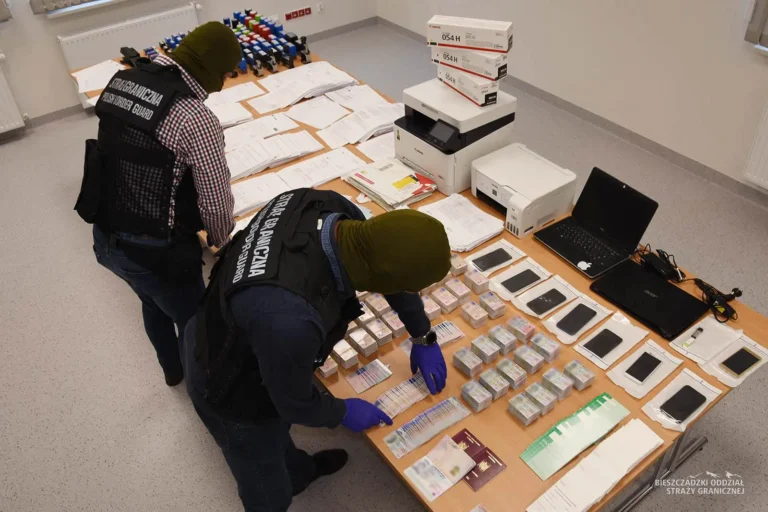
Europol Cracks Down on European Document Forgery and Smuggling Ring Criminal group
  • Cyber Security

Europol Cracks Down on European Document Forgery and Smuggling Ring

Do Son February 21, 2025 0

Europol's recent operation dismantled a criminal group involved in forgery and smuggling within the European Union.

Apple’s Spyware Detection: Only 50% Effective? Pegasus spyware sample
  • Malware

Apple’s Spyware Detection: Only 50% Effective?

Do Son February 21, 2025 0

iVerify underscores that relying solely on Apple’s detection mechanisms is insufficient, as Apple’s detection rate is estimated to be only around 50%

ChatGPT Hits 400 Million Weekly Users ChatGPT active user
  • Technology

ChatGPT Hits 400 Million Weekly Users

Do Son February 21, 2025 0

Discover the rise of ChatGPT active users, surging from 200 million to 400 million in just months. What’s next?

Apple C2 Modem: Next-Gen 5G in the Works? Apple C2 modem Apple Product Roadmap, iPhone 17
  • Technology

Apple C2 Modem: Next-Gen 5G in the Works?

Do Son February 21, 2025 0

Learn about the Apple C2, the next-generation chip set to enhance connectivity in future iPhones, following Apple C1's debut.

Amazon Appstore on Android to Shut Down in 2025: What It Means for Users and Developers Amazon Appstore Android
  • Technology

Amazon Appstore on Android to Shut Down in 2025: What It Means for Users and Developers

Do Son February 20, 2025 0

Learn about the Amazon Appstore Android, its integration with Windows 11, and the upcoming shutdown in 2025.

Google Releases PoC for CVE-2025-0110 Command Injection in PAN-OS Firewalls CVE-2024-5921 - CVE-2025-0103 CVE-2025-0110 PoC
  • Vulnerability

Google Releases PoC for CVE-2025-0110 Command Injection in PAN-OS Firewalls

Do Son February 20, 2025 0

Explore the CVE-2025-0110 PoC exploit details for Palo Alto Networks' PAN-OS firewall and its security implications.

CVE-2025-23115 & CVE-2025-23116: Hackers Can Hijack Ubiquiti UniFi Protect Cameras CVE-2025-23115 & CVE-2025-23116
  • Vulnerability

CVE-2025-23115 & CVE-2025-23116: Hackers Can Hijack Ubiquiti UniFi Protect Cameras

Do Son February 20, 2025 0

Stay informed about CVE-2025-23116: a critical vulnerability in UniFi Protect that could compromise user device security.

CVE-2025-0111 & CVE-2025-23209: Palo Alto Firewalls and Craft CMS Under Active Attack Ivanti EPMM Vulnerability CVE-2026-1340 CISA KEV Catalog CVE-2026-21385 CISA KEV Update CVE-2008-0015 CISA KEV, Array Networks Command Injection CVE-2025-0111 & CVE-2025-23209 CISA, Known Exploited Vulnerabilities
  • Vulnerability

CVE-2025-0111 & CVE-2025-23209: Palo Alto Firewalls and Craft CMS Under Active Attack

Do Son February 20, 2025 0

The flaws, tracked as CVE-2025-0111 and CVE-2025-23209, pose significant risks to organizations using Palo Alto Networks' PAN-OS firewall & Craft CMS

China’s Cybersecurity Firms Reveal Alleged NSA (Equation Group) Tactics in University Hack APT-C-40 - Equation Group
  • Cyber Security

China’s Cybersecurity Firms Reveal Alleged NSA (Equation Group) Tactics in University Hack

Do Son February 20, 2025 0

Explore the allegations about the Equation Group's tactics in a new Chinese cybersecurity report regarding U.S. cyber operations.

CVE-2024-39327 (CVSS 9.9): Critical IDPKI Flaw Could Allow Illegitimate Certificate Issuance Ollama Heap Leak CVE-2026-5757 Anritsu Vulnerability Authentication Bypass Gootloader Malware Malformed ZIP Evasion Blender Malware, StealC V2 Lectora, XSS CVE-2025-9125 HFS RCE, Template Injection Arch Linux Malware, CHAOS RAT CVE-2024-56404 - CVE-2024-39327 CVE-2025-2538
  • Vulnerability

CVE-2024-39327 (CVSS 9.9): Critical IDPKI Flaw Could Allow Illegitimate Certificate Issuance

Do Son February 20, 2025 0

Explore the implications of CVE-2024-39327 vulnerabilities in IDPKI. Learn how they can compromise security and trust.

ACRStealer Malware Exploits Google Docs as Command-and-Control Infrastructure ACRStealer Infostealer malware
  • Malware

ACRStealer Malware Exploits Google Docs as Command-and-Control Infrastructure

Do Son February 20, 2025 0

Learn about ACRStealer, the new infostealer malware exploiting platforms like Google Docs and Steam for its attacks.

Fluent Bit Vulnerabilities (CVE-2024-50608 & CVE-2024-50609) Could Disrupt Millions of Enterprise Systems CVE-2024-50609 & CVE-2024-50608
  • Vulnerability

Fluent Bit Vulnerabilities (CVE-2024-50608 & CVE-2024-50609) Could Disrupt Millions of Enterprise Systems

Do Son February 20, 2025 0

Stay informed about CVE-2024-50608 & CVE-2024-50609 vulnerabilities in Fluent Bit and how it could disrupt operations for daily users.

TA2726 & TA2727: Hackers Deploy Fake Updates to Spread Malware TA2726 and TA2727 & FrigidStealer malware
  • Cyber Security
  • Malware

TA2726 & TA2727: Hackers Deploy Fake Updates to Spread Malware

Do Son February 20, 2025 0

Explore the activities of TA2726 and TA2727 as they utilize fake browser updates to spread malware and deceive users.

Updated ShadowPad Malware Facilitates Ransomware Deployment in Global Attacks CVE-2024-1212 Vulnerability
  • Malware

Updated ShadowPad Malware Facilitates Ransomware Deployment in Global Attacks

Do Son February 20, 2025 0

Explore the evolving threat of ShadowPad malware, now facilitating ransomware attacks linked to Chinese threat actors.

JavaScript-Based Malware Exploits Steganography for Covert Data Theft Stealer malware
  • Malware

JavaScript-Based Malware Exploits Steganography for Covert Data Theft

Do Son February 20, 2025 0

Discover how Stealer malware exploits JavaScript techniques to exfiltrate sensitive user data and evade detection.

Secure Boot Bypass: U-Boot Vulnerabilities Expose Embedded Devices U-Boot vulnerability - CVE-2024-57254
  • Vulnerability

Secure Boot Bypass: U-Boot Vulnerabilities Expose Embedded Devices

Do Son February 20, 2025 0

Discover the crucial update for U-Boot vulnerability affecting security in embedded devices and learn how it mitigates risks.

REF7707: Espionage Campaign Targets South America and Southeast Asia DPRK IT Workers, APT38 Crypto Forfeiture
  • Cyber Security
  • Malware

REF7707: Espionage Campaign Targets South America and Southeast Asia

Do Son February 20, 2025 0

Explore the cyber espionage campaign REF7707, revealing novel malware and operational oversights by attackers in South America and Southeast Asia.

File Forensics: Uncovering Hidden Evidence with Computer Forensics Software monitor-1307227_1280
  • Technique

File Forensics: Uncovering Hidden Evidence with Computer Forensics Software

Do Son February 20, 2025 0

Dive into the world of file forensics and learn how it helps recover deleted files, analyze digital evidence, and solve cybercrimes. Discover the role of computer forensics software in modern investigations.

Zero-Day Security Flaw in Microsoft Power Pages (CVE-2025-24989) Exposes Users to Privilege Escalation CVE-2025-24989
  • Vulnerability

Zero-Day Security Flaw in Microsoft Power Pages (CVE-2025-24989) Exposes Users to Privilege Escalation

Do Son February 20, 2025 0

Explore CVE-2025-24989, a critical zero-day vulnerability in Microsoft Power Pages affecting user registration controls.

Microsoft’s Quantum Breakthrough: Majorana 1 and the Future of Computing Majorana 1
  • Technology

Microsoft’s Quantum Breakthrough: Majorana 1 and the Future of Computing

Do Son February 20, 2025 0

Explore Microsoft’s Majorana 1, the groundbreaking quantum processor with a capacity of one million qubits.

CVE-2025-21420: Windows Disk Cleanup Tool Flaw Exploited to Gain SYSTEM Privileges, PoC Released CVE-2025-21420 PoC
  • Vulnerability
  • Windows

CVE-2025-21420: Windows Disk Cleanup Tool Flaw Exploited to Gain SYSTEM Privileges, PoC Released

Do Son February 19, 2025 0

Learn about CVE-2025-21420, a critical vulnerability in the Windows Disk Cleanup Tool that could allow SYSTEM privilege escalation.

Rhadamanthys Infostealer Exploits Microsoft Management Console Artivion cybersecurity - Zero-Day Attacks
  • Malware

Rhadamanthys Infostealer Exploits Microsoft Management Console

Do Son February 19, 2025 0

Learn about the Rhadamanthys Infostealer and its new distribution method using MSC extension files to target sensitive information.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-61949CVSS 9.3
    Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in Bookly Bookly bookly-responsive-appointment-booking-tool allows...
    📅 Updated: Nov 10, 2026
  • CVE-2026-13312CVSS 9.9
    A vulnerability that could allow an attacker to compromise a system.
    📅 Updated: Nov 10, 2026
  • CVE-2026-72868CVSS 9.9
    Dokploy is a free, self-hostable Platform as a Service (PaaS). Prior to 0.29.13, apps/dokploy/server/api/routers/destination.ts interpolates the accessKey, secretAccessKey,...
    📅 Updated: Nov 10, 2026
  • CVE-2026-6715CVSS 9.8
    IBM Concert 1.0 through 3.0.1.1 allows an attacker can supply crafted input that is incorporated into an operating...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17403CVSS 9.0
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to gain full...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17402CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17392CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to gain...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.