Skip to content
October 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Data Exfiltration and RCE Risks Found in Azure Data Factory’s Airflow Integration Azure Data Factory Apache Airflow - Dirty DAG vulnerabilities
  • Vulnerability

Data Exfiltration and RCE Risks Found in Azure Data Factory’s Airflow Integration

Do Son December 18, 2024 0
Read More Read more about Data Exfiltration and RCE Risks Found in Azure Data Factory’s Airflow Integration
High-Severity Vulnerabilities Fixed in Latest Chrome Release CVE-2024-12692 & CVE-2024-12695
  • Vulnerability

High-Severity Vulnerabilities Fixed in Latest Chrome Release

Do Son December 18, 2024 0
Read More Read more about High-Severity Vulnerabilities Fixed in Latest Chrome Release
Fake CAPTCHAs Deliver Lumma Infostealer Malware in Massive Malvertising Campaign Lumma infostealer malware
  • Cyber Security
  • Malware

Fake CAPTCHAs Deliver Lumma Infostealer Malware in Massive Malvertising Campaign

Do Son December 18, 2024 0
Read More Read more about Fake CAPTCHAs Deliver Lumma Infostealer Malware in Massive Malvertising Campaign
RisePro and PrivateLoader Threat Actors Strike Again with RiseLoader BlueNoroff macOS Attack GhostCall Campaign Carding Underground Bulletproof Hosting DPRK Contagious Interview, npm Flood Stonefly group -HiatusRAT Actors
  • Cyber Security
  • Malware

RisePro and PrivateLoader Threat Actors Strike Again with RiseLoader

Do Son December 18, 2024 0
Read More Read more about RisePro and PrivateLoader Threat Actors Strike Again with RiseLoader
Discover the Advanced Techniques and Capabilities of Nova: A Snake Keylogger Fork Snake Keylogger family
  • Malware

Discover the Advanced Techniques and Capabilities of Nova: A Snake Keylogger Fork

Do Son December 18, 2024 0
Read More Read more about Discover the Advanced Techniques and Capabilities of Nova: A Snake Keylogger Fork
RCE and DoS Vulnerabilities Addressed in Apache Tomcat: CVE-2024-50379 and CVE-2024-54677 CVE-2024-50379 & CVE-2024-54677 Apache Tomcat Vulnerabilities
  • Vulnerability

RCE and DoS Vulnerabilities Addressed in Apache Tomcat: CVE-2024-50379 and CVE-2024-54677

Do Son December 17, 2024 0
Read More Read more about RCE and DoS Vulnerabilities Addressed in Apache Tomcat: CVE-2024-50379 and CVE-2024-54677
CVE-2024-53376: CyberPanel Flaw Exposes Systems to Full Compromise, PoC Published CVE-2024-53376 PoC
  • Vulnerability

CVE-2024-53376: CyberPanel Flaw Exposes Systems to Full Compromise, PoC Published

Do Son December 17, 2024 0
Read More Read more about CVE-2024-53376: CyberPanel Flaw Exposes Systems to Full Compromise, PoC Published
New Malware “I2PRAT” Exploits Anonymous I2P Network for Stealthy Command and Control DriverFixer0428, Contagious Interview Cache Smuggling, ClickFix Evasion North Korean Cyber Espionage
  • Malware

New Malware “I2PRAT” Exploits Anonymous I2P Network for Stealthy Command and Control

Do Son December 17, 2024 0
Read More Read more about New Malware “I2PRAT” Exploits Anonymous I2P Network for Stealthy Command and Control
CVE-2024-55949 (CVSS 9.3): Critical MinIO Flaw Allows Any User to Gain Full Admin Privileges MinIO Signature Bypass Unauthenticated Object Write MinIO Privilege Escalation, Policy Bypass CVE-2024-55949
  • Vulnerability

CVE-2024-55949 (CVSS 9.3): Critical MinIO Flaw Allows Any User to Gain Full Admin Privileges

Do Son December 17, 2024 0
Read More Read more about CVE-2024-55949 (CVSS 9.3): Critical MinIO Flaw Allows Any User to Gain Full Admin Privileges
HiatusRAT Campaign Targets Web Cameras and DVRs: FBI Warns of Rising IoT Exploits BlueNoroff macOS Attack GhostCall Campaign Carding Underground Bulletproof Hosting DPRK Contagious Interview, npm Flood Stonefly group -HiatusRAT Actors
  • Cyber Security
  • Malware
  • Vulnerability

HiatusRAT Campaign Targets Web Cameras and DVRs: FBI Warns of Rising IoT Exploits

Do Son December 17, 2024 0
Read More Read more about HiatusRAT Campaign Targets Web Cameras and DVRs: FBI Warns of Rising IoT Exploits
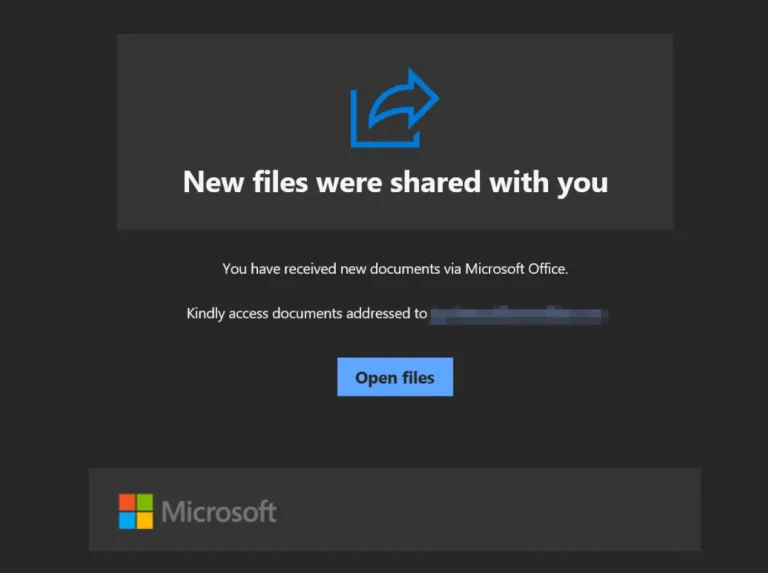
Xloader Malware Delivered via Sophisticated SharePoint Attack Xloader malware - Formbook
  • Malware

Xloader Malware Delivered via Sophisticated SharePoint Attack

Do Son December 17, 2024 0
Read More Read more about Xloader Malware Delivered via Sophisticated SharePoint Attack
Spring Boot Actuator Misconfigurations: The Hidden Security Risks in Cloud Environments Spring Boot Actuator Misconfigurations
  • Vulnerability

Spring Boot Actuator Misconfigurations: The Hidden Security Risks in Cloud Environments

Do Son December 17, 2024 0
Read More Read more about Spring Boot Actuator Misconfigurations: The Hidden Security Risks in Cloud Environments
CoinLurker Malware Targets Crypto Users via Fake Browser Updates Citrix NetScaler attack
  • Malware

CoinLurker Malware Targets Crypto Users via Fake Browser Updates

Do Son December 17, 2024 0
Read More Read more about CoinLurker Malware Targets Crypto Users via Fake Browser Updates
Multiple Vulnerabilities in SHARP Routers Demand Urgent Firmware Updates CVE-2024-46873 and CVE-2024-45721
  • Vulnerability

Multiple Vulnerabilities in SHARP Routers Demand Urgent Firmware Updates

Do Son December 17, 2024 0
Read More Read more about Multiple Vulnerabilities in SHARP Routers Demand Urgent Firmware Updates
Massive Ransomware Campaign Targets DrayTek Routers Osiris Ransomware Inc Ransomware Connection CountLoader Massive Ransomware Campaign CVE-2025-0289
  • Malware
  • Vulnerability

Massive Ransomware Campaign Targets DrayTek Routers

Do Son December 17, 2024 0
Read More Read more about Massive Ransomware Campaign Targets DrayTek Routers
From Taiwan to Korea: TIDRONE Threat Actor Targets ERP Software CLNTEND backdoor - threat actor
  • Cyber Security
  • Malware

From Taiwan to Korea: TIDRONE Threat Actor Targets ERP Software

Do Son December 17, 2024 0
Read More Read more about From Taiwan to Korea: TIDRONE Threat Actor Targets ERP Software
Russian State Actors Target UK Critical Infrastructure in New Cyber Campaign PHP RCE vulnerability
  • Cyber Security

Russian State Actors Target UK Critical Infrastructure in New Cyber Campaign

Do Son December 17, 2024 0
Read More Read more about Russian State Actors Target UK Critical Infrastructure in New Cyber Campaign
DLL Side-Loading Strikes Again: Yokai Backdoor Bypasses Security exfiltrating AWS credentials - fabrice package
  • Cyber Security
  • Malware

DLL Side-Loading Strikes Again: Yokai Backdoor Bypasses Security

Do Son December 17, 2024 0
Read More Read more about DLL Side-Loading Strikes Again: Yokai Backdoor Bypasses Security
Why Merchant Management Software is a Must-Have for Modern Banks and Payment Service Providers real_927d7428-06a7-415b-9e9c-4ad8c5f9f537
  • Technique

Why Merchant Management Software is a Must-Have for Modern Banks and Payment Service Providers

Do Son December 17, 2024 0
Read More Read more about Why Merchant Management Software is a Must-Have for Modern Banks and Payment Service Providers
CVE-2024-49112 (CVSS 9.8): Critical Windows LDAP Flaw Puts Networks at Risk of Remote Takeover PlayReady Leak, DRM Certificates Windows Server 2022 update Hyper-V confidential VM fix CVE-2024-49112 Microsoft Authenticator, password manager
  • Vulnerability

CVE-2024-49112 (CVSS 9.8): Critical Windows LDAP Flaw Puts Networks at Risk of Remote Takeover

Do Son December 16, 2024 0
Read More Read more about CVE-2024-49112 (CVSS 9.8): Critical Windows LDAP Flaw Puts Networks at Risk of Remote Takeover
Zero-Click HomeKit Exploit Used to Spy on Serbian Journalists HomeKit zero-click exploit
  • Malware
  • Vulnerability

Zero-Click HomeKit Exploit Used to Spy on Serbian Journalists

Do Son December 16, 2024 0
Read More Read more about Zero-Click HomeKit Exploit Used to Spy on Serbian Journalists
Hackers exploit critical Apache Struts RCE flaw (CVE-2024-53677) after PoC exploit release CoinMarketCap Hack, Inferno Drainer CVE-2024-53677 PoC Exploit
  • Vulnerability

Hackers exploit critical Apache Struts RCE flaw (CVE-2024-53677) after PoC exploit release

Do Son December 16, 2024 0
Read More Read more about Hackers exploit critical Apache Struts RCE flaw (CVE-2024-53677) after PoC exploit release
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-94504CVSS 7.2
    Ninja Forms 3.15.3 stores an anonymous non-RTE textarea value and renders it without safe HTML encoding in the...
    Admin intel📅 Updated: Oct 7, 2026
  • CVE-2026-93836CVSS 7.2
    The WPC Product Bundles for WooCommerce plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the \'qty\'...
    Admin intel📅 Updated: Oct 7, 2026
  • CVE-2026-21589CVSS 9.3
    This is a vulnerability in Bitbucket Data Center, Confluence Data Center, Jira Service Management Data Center, Jira Software...
    Admin intel📅 Updated: Oct 7, 2026
  • CVE-2026-61500CVSS 9.3
    Rejetto HFS 3.0.0 through 3.2.0 derives its session-cookie signing key from the non-cryptographic Math.random() generator and discloses outputs...
    Admin intel📅 Updated: Oct 7, 2026
  • CVE-2026-88779CVSS 8.7
    Vulnerability in NetScaler ADC and NetScaler Gateway. This issue affects ADC: before 14.1-73.41, before 13.1-64.28, before 14.1-73.41 FIPS,...
    Admin intelCISA KEV📅 Added to KEV: Oct 4, 2026📅 Updated: Oct 4, 2026
  • CVE-2026-102490CVSS 8.5
    All versions of Zammad including the latest alpha enable the local zammad user to escalate privileges to root.
    Admin intelCISA KEV📅 Added to KEV: Oct 2, 2026📅 Updated: Oct 2, 2026
  • CVE-2026-102489CVSS 8.7
    Zammad versions 6.3.0 to 6.5.4 are vulnerable a session hijack vulnerability that leads to remote code execution as...
    Admin intelCISA KEV📅 Added to KEV: Oct 2, 2026📅 Updated: Oct 2, 2026
  • CVE-2026-100382CVSS 10.0
    Improper Neutralization of Special Elements used in an OS Command (\'OS Command Injection\') vulnerability in Wikimedia Foundation Mediawiki...
    Admin intel📅 Updated: Oct 1, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-102782CVSS 9.3
    Joomla Extension - ordasoft.com - Unauthenticated SQL injection in OrdaSoft Simple Membership < 7.4.0 - site/simplemembership.php dispatches task=checkLoginPass...
    📅 Updated: Oct 8, 2026
  • CVE-2026-48908CVSS 10.0
    A vulnerability in SP Page Builder for Joomla allows unauthenticated users to upload arbitrary files, ultimately resulting in...
    CISA KEV📅 Added to KEV: Jul 7, 2026📅 Updated: Oct 8, 2026
  • CVE-2026-56290CVSS 10.0
    Joomla Extension - joomlack.fr - Unauthenticated file upload in Page Builder CK extension < 3.6.0 - The Joomla...
    CISA KEV📅 Added to KEV: Jul 7, 2026📅 Updated: Oct 8, 2026
  • CVE-2026-17609CVSS 9.1
    The Super Forms – Drag & Drop Form Builder plugin for WordPress is vulnerable to Arbitrary Directory Deletion...
    📅 Updated: Oct 8, 2026
  • CVE-2026-93674CVSS 9.8
    IBM Langflow OSS 1.0.0 through 1.12.2 could allow a remote attacker to execute arbitrary code due to improper...
    📅 Updated: Oct 8, 2026
  • CVE-2026-79805CVSS 9.8
    An authenticated path traversal vulnerability exists in ClearPass Policy Manager. Successful exploitation could allow an attacker to read...
    📅 Updated: Oct 8, 2026
  • CVE-2026-79801CVSS 9.8
    A missing integrity verification vulnerability in the client agent software of HPE Networking ClearPass Policy Manager could allow...
    📅 Updated: Oct 8, 2026
  • CVE-2026-79798CVSS 9.9
    SQL injection vulnerabilities in the web-based management interface of ClearPass Policy Manager could allow a low-privileged authenticated remote...
    📅 Updated: Oct 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.