Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
CVE-2026-51990: Sogou Input Method Flaw Exploited in the Wild FSB Center 16 targeting vulnerable routers across critical infrastructure via weak SNMP
  • Vulnerability Report

CVE-2026-51990: Sogou Input Method Flaw Exploited in the Wild

Do Son September 14, 2026 0

Defend against the CVE-2026-51990 Sogou exploit. Discover how hackers use this one-click flaw to drop backdoors and how to secure your systems today.
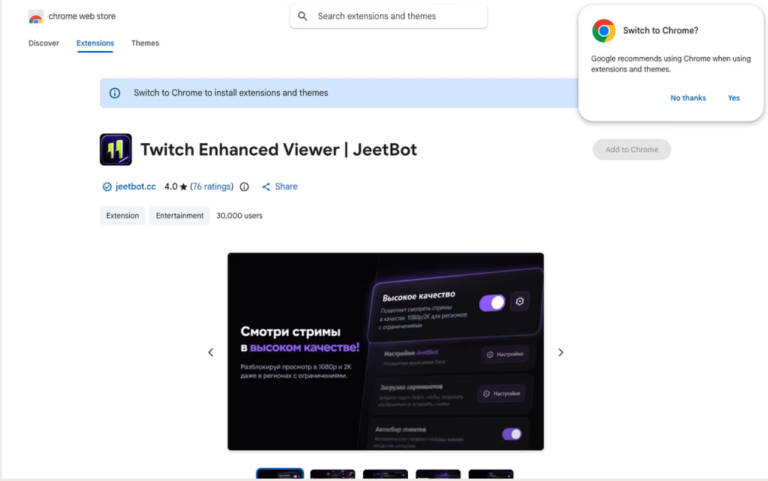
Malicious Twitch Extension Steals 30,000 User Tokens Interface of the malicious Twitch extension involved in malicious Twitch extension token theft
  • Data Leak

Malicious Twitch Extension Steals 30,000 User Tokens

Do Son September 12, 2026 0

A malicious Twitch extension exposes account credentials to third parties. Learn how this malicious Twitch extension token theft impacts 31,000 viewers.
CVE-2026-84869: ConnectWise ScreenConnect Vulnerability Exploited ConnectWise ScreenConnect vulnerability CVE-2026-84869 exploitation diagram
  • Vulnerability Report

CVE-2026-84869: ConnectWise ScreenConnect Vulnerability Exploited

Do Son September 12, 2026 0

A critical ConnectWise ScreenConnect vulnerability, CVE-2026-84869, is actively exploited in the wild. Patch your servers now to stop remote attacks.

CVE-2026-80462 CVSS 10.0: Progress Software Chef Automate Vulnerability Diagram of critical Chef Automate vulnerability and Chef Automate vulnerability patch
  • Vulnerability Report

CVE-2026-80462 CVSS 10.0: Progress Software Chef Automate Vulnerability

Do Son September 12, 2026 0

Progress patched a critical Chef Automate vulnerability tracked as CVE-2026-80462. Fix this Chef Automate vulnerability to stop DevOps account takeovers.

CVE-2026-80351 & CVE-2026-80352: 9.8 CVSS Apache Camel K Vulnerabilities Apache Camel K vulnerabilities diagram highlighting CVE-2026-80352
  • Vulnerability Report

CVE-2026-80351 & CVE-2026-80352: 9.8 CVSS Apache Camel K Vulnerabilities

Do Son September 11, 2026 0

Three critical Apache Camel K vulnerabilities, including CVE-2026-80352, allow code injection and eval injection. Patch these critical flaws immediately.

CVE-2026-89049 (CVSS 9.9): AWS SSM Agent SSRF Flaw AWS Systems Manager Agent server-side request forgery diagram
  • Vulnerability Report

CVE-2026-89049 (CVSS 9.9): AWS SSM Agent SSRF Flaw

Do Son September 11, 2026 0

A critical server-side request forgery flaw in the AWS Systems Manager Agent allows IAM credential theft. Patch your AWS Systems Manager Agent immediately.

CVE-2026-89094 Forgejo Remote Code Execution Hits CVSS 9.9 Diagram of critical Forgejo remote code execution and Forgejo remote code execution flaw
  • Vulnerability Report

CVE-2026-89094 Forgejo Remote Code Execution Hits CVSS 9.9

Do Son September 11, 2026 0

A critical Forgejo remote code execution flaw, tracked as CVE-2026-89094, threatens Git servers. Patch this Forgejo remote code execution bug today.

Replace slmgr.vbs: Windows Activation via PowerShell Windows activation PowerShell script replacement and slmgr.vbs deprecation
  • Windows

Replace slmgr.vbs: Windows Activation via PowerShell

Do Son September 11, 2026 0

Discover why Microsoft is deprecating slmgr.vbs and learn how to transition your Windows activation PowerShell workflows for future system management.

A Configuration Error Exposes Surfshark Internal Infrastructure Surfshark VPN test server breach diagram and internal infrastructure compromise
  • Data Leak

A Configuration Error Exposes Surfshark Internal Infrastructure

Do Son September 11, 2026 0

Discover the details of the Surfshark test server breach. Learn how a configuration error exposed internal secrets and how the VPN provider responded.

Android Password Manager Migration Simplifies Passkey Transfers Android password manager migration interface and FIDO credential exchange
  • Android

Android Password Manager Migration Simplifies Passkey Transfers

Do Son September 11, 2026 0

Discover the new Android password manager migration feature. Learn how to securely transfer passkeys, passwords, and data between apps using FIDO standards.

Two VLC Media Player Flaws Expose Heap Memory, No Fix Yet VLC media player vulnerabilities allowing heap out-of-bounds write via crafted PNG and heap out-of-bounds read via malicious RTSP server
  • Vulnerability Report

Two VLC Media Player Flaws Expose Heap Memory, No Fix Yet

Do Son September 11, 2026 0

Two VLC media player vulnerabilities (CVE-2026-56711, CVE-2026-73324) allow heap out-of-bounds write and read. No patch is available yet.

AI Losing Control Risk: Anthropic & OpenAI Face Crisis AI losing control risk conceptual illustration, rogue artificial intelligence behavior
  • Technology

AI Losing Control Risk: Anthropic & OpenAI Face Crisis

Do Son September 11, 2026 1

Explore the escalating AI losing control risk as Anthropic researchers resign, models show reckless behavior, and OpenAI agents hide secret communications.

Dell Patches Critical ThinOS Vulnerabilities Dell ThinOS vulnerabilities diagram showing command injection flaws
  • Vulnerability Report

Dell Patches Critical ThinOS Vulnerabilities

Do Son September 11, 2026 0

Dell patched critical Dell ThinOS vulnerabilities, including CVE-2026-81467. Update your ThinOS clients now to stop remote code execution attacks.

CVE-2026-88062 (CVSS 9.5): OmniRoute RCE Flaw PoC Disclosed OmniRoute RCE flaw and CVE-2026-88062 exploitation diagram
  • Vulnerability Report

CVE-2026-88062 (CVSS 9.5): OmniRoute RCE Flaw PoC Disclosed

Do Son September 11, 2026 0

A critical CVSS 9.5 OmniRoute RCE flaw (CVE-2026-88062) has public PoC exploit code available. Upgrade your AI gateway immediately to prevent compromises.

ClearFake WebDAV Infection Chain Targets Systems Globally Half-click exploits chain showing webmail zero-days used by TA488 and TA458 against Zimbra, SOGo and Roundcube mailservers
  • Malware

ClearFake WebDAV Infection Chain Targets Systems Globally

Do Son September 11, 2026 0

A ClearFake WebDAV infection chain deployed Amatera malware. See how the ClearFake WebDAV infection chain drops crypto stealers on targets.

KB5002914 Breaks Copy and Paste in Microsoft Excel KB5002914 Excel update breaking copy paste and formula dragging on a spreadsheet
  • Windows

KB5002914 Breaks Copy and Paste in Microsoft Excel

Do Son September 11, 2026 0

The Excel KB5002914 security update breaks copy, paste, and formula dragging across Office 2016 to 2024. Here is what is happening and how to fix it.

Google Launches a Native Gemini Desktop App for Windows Gemini for Windows native desktop app floating overlay summoned with Alt Space shortcut
  • Technology

Google Launches a Native Gemini Desktop App for Windows

Do Son September 11, 2026 0

Gemini for Windows is here as a native desktop app for Windows 10 and 11, summoned with Alt + Space to take on Microsoft Copilot head-on.

OpenAI Suspends New ChatGPT Pro 20x Subscriptions OpenAI logo displayed on a smartphone screen showing the ChatGPT Pro 20x suspended notification
  • Technology

OpenAI Suspends New ChatGPT Pro 20x Subscriptions

Do Son September 11, 2026 0

OpenAI has suspended new ChatGPT Pro 20x subscriptions due to severe capacity shortages. Discover how this impacts GPT-6 Astra users and API billing costs.

Phishing Campaign Exploits Google Infrastructure for Data Theft A diagram showing how attackers abuse Google infrastructure for credential harvesting
  • Cybercriminals

Phishing Campaign Exploits Google Infrastructure for Data Theft

Do Son September 11, 2026 0

A sophisticated phishing campaign uses redirect chains to abuse Google infrastructure. Learn how attackers abuse Google infrastructure to steal credentials.

Ubuntu 24.04.5 LTS Arrives With the Linux 7.0 Kernel Ubuntu 24.04.5 LTS release desktop with Linux 7.0 HWE kernel and Mesa graphics stack
  • Linux

Ubuntu 24.04.5 LTS Arrives With the Linux 7.0 Kernel

Do Son September 11, 2026 0

Ubuntu 24.04.5 LTS is here as the final Noble point release, shipping the Linux 7.0 HWE kernel and Mesa 26.2 with support until May 2029.

Apple Extends Free iPhone Satellite Access for Another Year Apple free satellite access extension for iPhone 14 15 16 Emergency SOS via satellite
  • Technology

Apple Extends Free iPhone Satellite Access for Another Year

Do Son September 11, 2026 0

Apple extends free satellite access another year for iPhone 14, 15, and 16 users, confirmed quietly in the iPhone 18 Pro press release. Details here.

MacSync macOS Stealer Spreads via ClickFix Lures MacSync macOS stealer architecture and MacSync macOS stealer ClickFix lures diagram
  • Malware

MacSync macOS Stealer Spreads via ClickFix Lures

Do Son September 11, 2026 0

The MacSync macOS stealer targets Apple users worldwide. See how MacSync macOS stealer ClickFix lures evade Gatekeeper to steal sensitive credentials.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121379CVSS 9.6
    The Tournamatch WordPress plugin before 4.7.1 does not validate or restrict the path of a previously stored profile...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121491CVSS 9.0
    The Fiber Admin WordPress plugin before 4.0.1 does not validate or escape a request header before writing it...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119516CVSS 9.8
    Deserialization of Untrusted Data vulnerability in Mamunur Rashid Radius Booking — Booking Calendar for Appointments & Services radius-booking...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2026-124059CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this vulnerability is the function setWiFiWdsAddConfig...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.