Skip to content
September 15, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Greenhat Announces Successful Delegation at Web Summit Vancouver 2026 WebSummit_178395613180DohtofDR
  • Press Release

Greenhat Announces Successful Delegation at Web Summit Vancouver 2026

cybernewswire July 14, 2026 0
Read More Read more about Greenhat Announces Successful Delegation at Web Summit Vancouver 2026
SAP Patches CVE-2026-44747 (CVSS 9.9): Critical Memory Corruption Flaw in NetWeaver AS ABAP SAP Security Patch Day July 2026 CVE-2026-44747 memory corruption vulnerability in NetWeaver AS ABAP
  • Vulnerability Report

SAP Patches CVE-2026-44747 (CVSS 9.9): Critical Memory Corruption Flaw in NetWeaver AS ABAP

Do Son July 14, 2026 0
Read More Read more about SAP Patches CVE-2026-44747 (CVSS 9.9): Critical Memory Corruption Flaw in NetWeaver AS ABAP
CrowdStrike Details New Prompt Injection Attacks on AI Diagram showing how prompt injection attacks and prompt injection techniques threaten AI security.
  • Vulnerability Report

CrowdStrike Details New Prompt Injection Attacks on AI

Do Son July 14, 2026 0
Read More Read more about CrowdStrike Details New Prompt Injection Attacks on AI
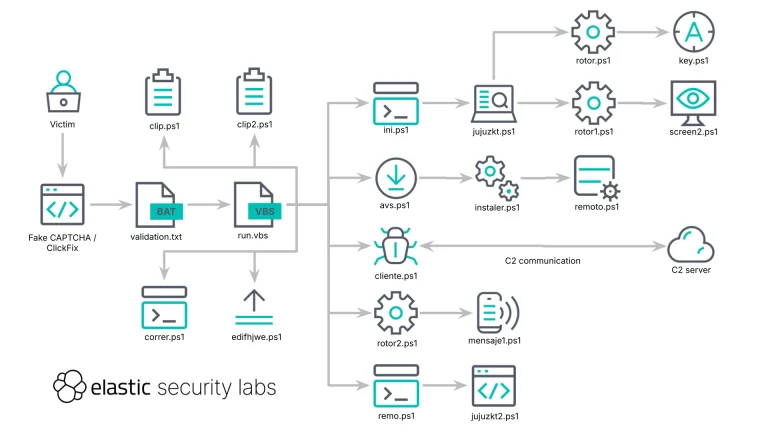
Mexican Banking Fraud: REF6045 Operation Exposed Diagram of the REF6045 operation executing Mexican banking fraud using SCMBANKER.
  • Cybercriminals

Mexican Banking Fraud: REF6045 Operation Exposed

Do Son July 14, 2026 0
Read More Read more about Mexican Banking Fraud: REF6045 Operation Exposed
WinFsp Patches Two Privilege Escalation Flaws: CVE-2026-3006 and CVE-2026-7162 (CVSS 7.8) WinFsp vulnerabilities CVE-2026-3006 and CVE-2026-7162 enabling local privilege escalation on Windows
  • Vulnerability Report

WinFsp Patches Two Privilege Escalation Flaws: CVE-2026-3006 and CVE-2026-7162 (CVSS 7.8)

Do Son July 14, 2026 0
Read More Read more about WinFsp Patches Two Privilege Escalation Flaws: CVE-2026-3006 and CVE-2026-7162 (CVSS 7.8)
Windows Search Box Improvements Roll Out in Windows 11 Windows search box improvements and refined Windows Search settings in Windows 11
  • Windows

Windows Search Box Improvements Roll Out in Windows 11

Do Son July 14, 2026 0
Read More Read more about Windows Search Box Improvements Roll Out in Windows 11
Telegram t.me Domain Blocked by .ME Registry Links Down Telegram t.me domain serverHold status blocking all contact links and shared content URLs
  • Technology

Telegram t.me Domain Blocked by .ME Registry Links Down

Do Son July 14, 2026 0
Read More Read more about Telegram t.me Domain Blocked by .ME Registry Links Down
The Grok Build Privacy Controversy: Unauthorized Repository Uploads Grok Build privacy settings interface showing how to disable automated repository data uploads
  • Data Leak

The Grok Build Privacy Controversy: Unauthorized Repository Uploads

Do Son July 14, 2026 0
Read More Read more about The Grok Build Privacy Controversy: Unauthorized Repository Uploads
Netwrix Password Secure Flaws Enable Authenticated Remote Code Execution (CVSS 9.9), Update to 26.6.100 Netwrix Password Secure vulnerabilities enabling authenticated remote code execution on the server
  • Vulnerability Report

Netwrix Password Secure Flaws Enable Authenticated Remote Code Execution (CVSS 9.9), Update to 26.6.100

Do Son July 14, 2026 0
Read More Read more about Netwrix Password Secure Flaws Enable Authenticated Remote Code Execution (CVSS 9.9), Update to 26.6.100
CVE-2026-6875: Critical ServiceNow Sandbox Escape Allows Unauthenticated Remote Code Execution ServiceNow sandbox escape CVE-2026-6875 remote code execution vulnerability in the AI Platform
  • Vulnerability Report

CVE-2026-6875: Critical ServiceNow Sandbox Escape Allows Unauthenticated Remote Code Execution

Do Son July 14, 2026 0
Read More Read more about CVE-2026-6875: Critical ServiceNow Sandbox Escape Allows Unauthenticated Remote Code Execution
Better Auth SSRF Flaw CVE-2026-53513 (CVSS 9.6) Threatens 19M-Download Auth Library Better Auth SSRF vulnerability CVE-2026-53513 in the SSO plugin exposing OIDC provider registration
  • Vulnerability Report

Better Auth SSRF Flaw CVE-2026-53513 (CVSS 9.6) Threatens 19M-Download Auth Library

Do Son July 14, 2026 0
Read More Read more about Better Auth SSRF Flaw CVE-2026-53513 (CVSS 9.6) Threatens 19M-Download Auth Library
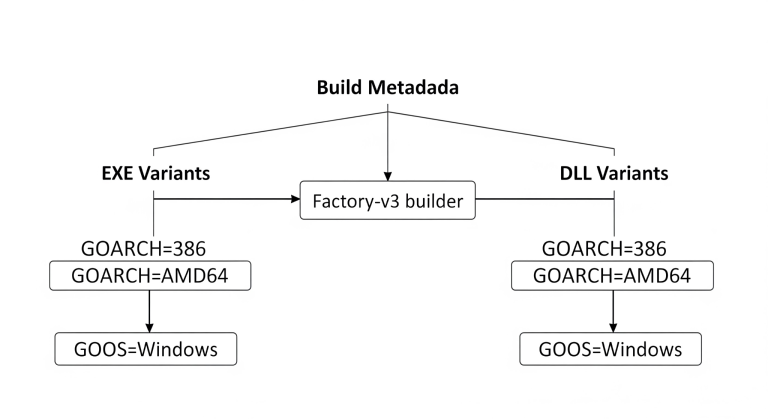
Vidar Stealer Campaign Uses Factory-v3 Loader Diagram showing how a Vidar stealer campaign uses the Factory-v3 loader to infect systems.
  • Malware

Vidar Stealer Campaign Uses Factory-v3 Loader

Do Son July 13, 2026 0
Read More Read more about Vidar Stealer Campaign Uses Factory-v3 Loader
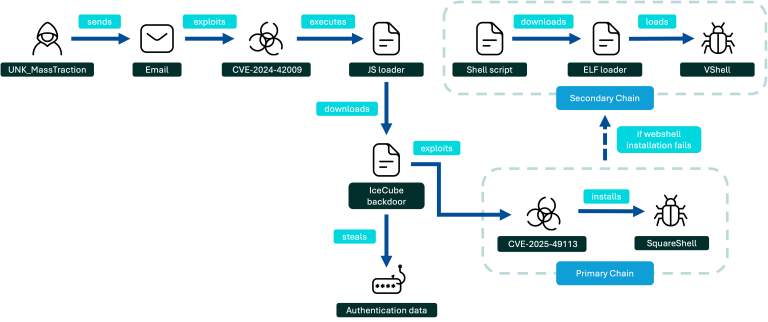
UNK_MassTraction Exploits Roundcube Webmail to Hit University Physics Departments UNK_MassTraction Roundcube exploitation infection chain deploying the VShell backdoor at universities
  • Cybercriminals

UNK_MassTraction Exploits Roundcube Webmail to Hit University Physics Departments

Do Son July 13, 2026 0
Read More Read more about UNK_MassTraction Exploits Roundcube Webmail to Hit University Physics Departments
Torq and Criminal IP Partner to Deliver Decision-Ready Threat Intelligence for Autonomous SOC Operations 1200_700_1783643174kG3odfUo4d
  • Press Release

Torq and Criminal IP Partner to Deliver Decision-Ready Threat Intelligence for Autonomous SOC Operations

cybernewswire July 13, 2026 0
Read More Read more about Torq and Criminal IP Partner to Deliver Decision-Ready Threat Intelligence for Autonomous SOC Operations
UAT-7810 Expands Its LapDogs ORB Network With New Router Malware GemStuffer RubyGems Campaign RubyGems Data Exfiltration TanStack npm Compromise Supply Chain Attack DNS Hijacking APT28 (Fancy Bear) OpenVSX Supply Chain Attack Checkmarx Plugin Breach Stryker Cyberattack CISA Alert Trans-Regional Cyber Conflict Operation Epic Fury Cyber Operation MacroMaze APT28 Cyber Espionage Notepad++ Supply Chain Attack Lotus Blossom Group Defense Industrial Base Threats GTIG Report APT28 Operation Neusploit CVE-2026-21509 Bookworm Malware
  • Cybercriminals

UAT-7810 Expands Its LapDogs ORB Network With New Router Malware

Do Son July 13, 2026 0
Read More Read more about UAT-7810 Expands Its LapDogs ORB Network With New Router Malware
CVE-2026-20744: Privilege Escalation in EV Chargers Diagram of CVE-2026-20744 privilege escalation flaw in Hydro-Québec charging stations alongside CVE-2026-42952 and CVE-2026-44383.
  • Vulnerability Report

CVE-2026-20744: Privilege Escalation in EV Chargers

Do Son July 13, 2026 0
Read More Read more about CVE-2026-20744: Privilege Escalation in EV Chargers
Defending Against Vishing and HUMINT: Best Practices for Security Teams DCMTK vulnerabilities enabling path traversal file write in the DICOM toolkit (CVE-2026-50003)
  • Technique

Defending Against Vishing and HUMINT: Best Practices for Security Teams

Do Son July 13, 2026 0
Read More Read more about Defending Against Vishing and HUMINT: Best Practices for Security Teams
ScreenConnect AsyncRAT Campaign Hides Inside Fake Freeware ScreenConnect AsyncRAT Campaign infrastructure and remote monitoring tools
  • Malware

ScreenConnect AsyncRAT Campaign Hides Inside Fake Freeware

Do Son July 13, 2026 0
Read More Read more about ScreenConnect AsyncRAT Campaign Hides Inside Fake Freeware
Evolving Windows Vulnerability Management with AI Windows vulnerability management using AI code scanning tools
  • Windows

Evolving Windows Vulnerability Management with AI

Do Son July 13, 2026 0
Read More Read more about Evolving Windows Vulnerability Management with AI
Critical Veeam Remote Code Execution Flaw: CVE-2026-44963 Diagram showing Veeam Backup server affected by CVE-2026-44963 and related CVE-2023-27532 remote code execution vulnerabilities.
  • Vulnerability Report

Critical Veeam Remote Code Execution Flaw: CVE-2026-44963

Do Son July 13, 2026 0
Read More Read more about Critical Veeam Remote Code Execution Flaw: CVE-2026-44963
StatCounter Corrects Flawed Windows Market Share Data StatCounter report showing corrected Windows market share and operating system statistics
  • Windows

StatCounter Corrects Flawed Windows Market Share Data

Do Son July 13, 2026 0
Read More Read more about StatCounter Corrects Flawed Windows Market Share Data
FSB Center 16 Targets Routers Across Critical Sectors FSB Center 16 targeting vulnerable routers across critical infrastructure via weak SNMP
  • Cyber Security

FSB Center 16 Targets Routers Across Critical Sectors

Do Son July 13, 2026 0
Read More Read more about FSB Center 16 Targets Routers Across Critical Sectors
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📧

Email Delivery
Get threat intel straight to your inbox.

♾️

Unlimited Vendors
Track every technology in your stack.

🚨

All New CVE Alerts
Be the first to know about new flaws.

⚙️

Custom EPSS Threshold
Filter noise, focus on real risks.

💬

Slack & Teams Webhook
Integrate directly into your SecOps.

🚫

100% Ad-Free
Enjoy an uninterrupted reading experience.

$7/mo
Subscribe Now

🚨 Active Exploits in the Wild

  • CVE-2026-51990
    A critical remote code execution vulnerability in Sogou Input Method, one of the most widely used Chinese-language input...
    Admin intel📅 Updated: Sep 12, 2026
  • CVE-2026-85706CVSS 10.0
    GitLab has remediated an issue that, under certain conditions, an unauthenticated user could have read arbitrary files from...
    Admin intelCISA KEV📅 Added to KEV: Sep 11, 2026📅 Updated: Sep 11, 2026
  • CVE-2026-42016CVSS 8.1
    JFrog Artifactory (Self Hosted) versions before 7.133.11 are vulnerable to a privilege escalation attack due to a validation...
    Admin intelCISA KEV📅 Added to KEV: Sep 11, 2026📅 Updated: Sep 11, 2026
  • CVE-2026-42018CVSS 7.5
    JFrog Artifactory could return an internal anonymous-user token to an unauthenticated caller when anonymous access is disabled, potentially...
    Admin intelCISA KEV📅 Added to KEV: Sep 11, 2026📅 Updated: Sep 11, 2026
  • CVE-2026-84869CVSS 9.9
    A condition in the ScreenConnect client may allow files to be transferred and executed through an active remote...
    CISA KEV📅 Added to KEV: Sep 11, 2026
  • CVE-2026-20079CVSS 10.0
    A vulnerability in the web interface of Cisco Secure Firewall Management Center (FMC) Software could allow an unauthenticated,...
    Admin intelCISA KEV📅 Added to KEV: Sep 9, 2026📅 Updated: Sep 9, 2026
  • CVE-2025-25249CVSS 8.1
    A heap-based buffer overflow vulnerability in Fortinet FortiOS 7.6.0 through 7.6.3, FortiOS 7.4.0 through 7.4.8, FortiOS 7.2.0 through...
    Admin intelCISA KEV📅 Added to KEV: Sep 9, 2026📅 Updated: Sep 9, 2026
  • CVE-2026-87491
    Out of bounds write in V8 in Google Chrome prior to 153.0.8010.36 allowed a remote attacker to execute...
    Admin intelCISA KEV📅 Added to KEV: Sep 9, 2026📅 Updated: Sep 9, 2026
Powered by CVE Watchtower

🔴 Live Critical Threats

  • CVE-2026-12944CVSS 9.6
    IBM Langflow OSS 1.0.0 through 1.10.0 can allow attackers to execute arbitrary...
  • CVE-2026-16338CVSS 9.9
    IBM DataStage on Cloud Pak for Data 5.4.0.0 IBM DataStage could allow...
  • CVE-2026-59178CVSS 9.8
    ESPHome Device Builder Dashboard is a dashboard for the ESPHome home management...
  • CVE-2026-90945CVSS 9.8
    Crawlab through 0.6.3 uses a hard-coded HMAC-SHA256 secret for JWT token signing...
  • CVE-2026-90942CVSS 9.6
    Casdoor through 4.4.0 fails to properly mask the instance-wide built-in certificate private...
  • CVE-2026-76461CVSS 9.8
    A vulnerability in the email parsing of Cisco AsyncOS Software for Cisco...
  • CVE-2026-76443CVSS 9.8
    As part of Cisco's ongoing commitment to proactive security and product quality,...
  • CVE-2026-76441CVSS 9.8
    As part of Cisco's ongoing commitment to proactive security and product quality,...
  • CVE-2026-76440CVSS 9.8
    As part of Cisco's ongoing commitment to proactive security and product quality,...
  • CVE-2026-20353CVSS 9.8
    As part of Cisco's ongoing commitment to proactive security and product quality,...
Powered by CVE WATCHTOWER

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.