Skip to content
September 15, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
CMS Exploitation Campaign Plants Webshells on Business Websites CMS exploitation campaign deploying webshell attacks on WordPress and CMS websites
  • Cybercriminals

CMS Exploitation Campaign Plants Webshells on Business Websites

Do Son July 13, 2026 0
Read More Read more about CMS Exploitation Campaign Plants Webshells on Business Websites
Cavern Manticore APT Deploys Modular C2 Framework North Korean hackers behind open-source supply chain attacks on axios, debug, and chalk NPM packages
  • Cybercriminals

Cavern Manticore APT Deploys Modular C2 Framework

Do Son July 13, 2026 0
Read More Read more about Cavern Manticore APT Deploys Modular C2 Framework
WAGO System I/O Flaw CVE-2026-4769 Leads to Full System Compromise WAGO System I/O field device early-boot flaw CVE-2026-4769 full system compromise
  • Vulnerability Report

WAGO System I/O Flaw CVE-2026-4769 Leads to Full System Compromise

Do Son July 13, 2026 0
Read More Read more about WAGO System I/O Flaw CVE-2026-4769 Leads to Full System Compromise
Armored Likho APT Deploys New BusySnake Stealer Diagram showing BusySnake Stealer infection chain by Armored Likho APT
  • Cybercriminals

Armored Likho APT Deploys New BusySnake Stealer

Do Son July 13, 2026 0
Read More Read more about Armored Likho APT Deploys New BusySnake Stealer
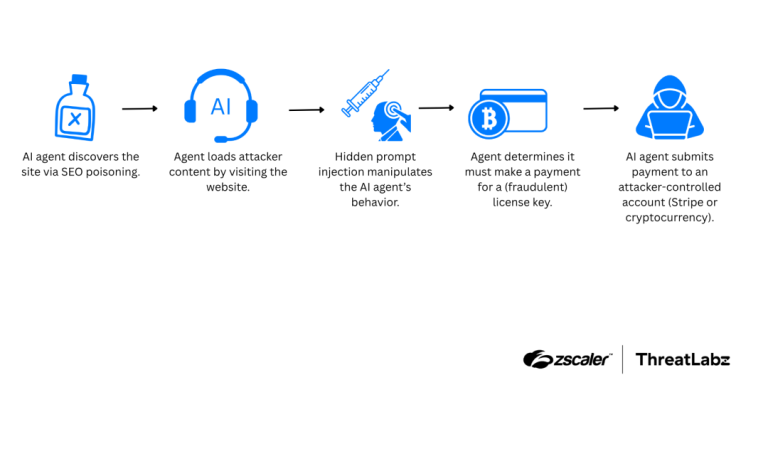
Indirect Prompt Injection Threatens AI Agents Diagram showing indirect prompt injection exploiting AI agent vulnerabilities
  • Cybercriminals

Indirect Prompt Injection Threatens AI Agents

Do Son July 13, 2026 0
Read More Read more about Indirect Prompt Injection Threatens AI Agents
SpaceX X Account Breach Exploited for Crypto Scam Official SpaceX X account breach promoting fraudulent crypto token
  • Cybercriminals

SpaceX X Account Breach Exploited for Crypto Scam

Do Son July 13, 2026 0
Read More Read more about SpaceX X Account Breach Exploited for Crypto Scam
Cursor Builds General AI Agent to Rival Claude Cowork Cursor AI general purpose agent competing with Claude Cowork for desktop computer control
  • Technology

Cursor Builds General AI Agent to Rival Claude Cowork

Do Son July 13, 2026 0
Read More Read more about Cursor Builds General AI Agent to Rival Claude Cowork
Weekly CVE Report: 1,571 New Flaws and 6 Actively Exploited Bugs (July 6–12, 2026) weekly CVE report actively exploited vulnerabilities
  • Weekly Recap

Weekly CVE Report: 1,571 New Flaws and 6 Actively Exploited Bugs (July 6–12, 2026)

Do Son July 13, 2026 0
Read More Read more about Weekly CVE Report: 1,571 New Flaws and 6 Actively Exploited Bugs (July 6–12, 2026)
Mycelium Framework: First AI-as-a-Service Botnet TanStack Typosquatting npm Supply Chain Attack Axios Supply Chain Attack npm Poisoning eScan Supply Chain Attack Antivirus Compromise APT-36, NCERT WhatsApp Advisory FBI alert, Salesforce Salt Typhoon, APT group ConnectWise ScreenConnect hack Nation-state cyberattack FortiGate Leak - zkLend vulnerability - TRIPLESTRENGTH Threat Actor Group Dark Storm
  • Malware

Mycelium Framework: First AI-as-a-Service Botnet

Do Son July 13, 2026 0
Read More Read more about Mycelium Framework: First AI-as-a-Service Botnet
CVE-2026-49844: Apache Log4j Emits Invalid JSON Logs Apache Log4j CVE-2026-49844 flaw producing invalid JSON in log4j-api output
  • Vulnerability Report

CVE-2026-49844: Apache Log4j Emits Invalid JSON Logs

Do Son July 13, 2026 0
Read More Read more about CVE-2026-49844: Apache Log4j Emits Invalid JSON Logs
decompress npm Vulnerability CVE-2026-53486 (CVSS 9.1) Threatens 2.8 Million Weekly Downloads decompress npm vulnerability CVE-2026-53486 path traversal in Node.js archive extraction
  • Vulnerability Report

decompress npm Vulnerability CVE-2026-53486 (CVSS 9.1) Threatens 2.8 Million Weekly Downloads

Do Son July 12, 2026 0
Read More Read more about decompress npm Vulnerability CVE-2026-53486 (CVSS 9.1) Threatens 2.8 Million Weekly Downloads
State of Exploited Vulnerabilities — Q2 2026 75 CVEs confirmed exploited in Q2 2026. Microsoft leads with 15, Ivanti tops EPSS at 99%. Full breakdown by vendor, CWE, and publication-to-exploit gap.
  • Report

State of Exploited Vulnerabilities — Q2 2026

Do Son July 11, 2026 0
Read More Read more about State of Exploited Vulnerabilities — Q2 2026
Apache IoTDB Fixes Path Traversal and Authentication Bypass Flaws (CVE-2026-24014) Apache IoTDB vulnerabilities path traversal and authentication bypass in DataNode RPC
  • Vulnerability Report

Apache IoTDB Fixes Path Traversal and Authentication Bypass Flaws (CVE-2026-24014)

Do Son July 11, 2026 0
Read More Read more about Apache IoTDB Fixes Path Traversal and Authentication Bypass Flaws (CVE-2026-24014)
Silver Fox Ghost Distributor Delivers MODBEACON Trojan to Chosen Targets Harvester APT Linux Backdoor OT Cyberattack Iranian APT Operation Olalampo MuddyWater APT Prince of Persia APT, Tonnerre v50 Patchwork APT, DLL Sideloading Subtle Snail, cyber espionage ShadowSilk, cyber espionage Volt Typhoon APT Group - Chinese Cybersecurity Firm
  • Cyber Security

Silver Fox Ghost Distributor Delivers MODBEACON Trojan to Chosen Targets

Do Son July 11, 2026 0
Read More Read more about Silver Fox Ghost Distributor Delivers MODBEACON Trojan to Chosen Targets
Apache Camel Vulnerabilities Expose Routes to Header Injection and SSRF Apache Camel vulnerabilities diagram showing header injection and server-side request forgery attack flow across Camel routes
  • Vulnerability Report

Apache Camel Vulnerabilities Expose Routes to Header Injection and SSRF

Do Son July 10, 2026 0
Read More Read more about Apache Camel Vulnerabilities Expose Routes to Header Injection and SSRF
Gardyn IoT Hub Flaw CVE-2026-13768 (CVSS 10) Enables Unauthenticated Remote Code Execution Gardyn IoT Hub advisory graphic showing CVE-2026-13768 remote code execution risk on smart garden devices
  • Vulnerability Report

Gardyn IoT Hub Flaw CVE-2026-13768 (CVSS 10) Enables Unauthenticated Remote Code Execution

Do Son July 10, 2026 0
Read More Read more about Gardyn IoT Hub Flaw CVE-2026-13768 (CVSS 10) Enables Unauthenticated Remote Code Execution
FreeBSD Patches Three Kernel Flaws That Enable Local Privilege Escalation FreeBSD privilege escalation advisory chart highlighting a kernel use-after-free and two local root flaws
  • Vulnerability Report

FreeBSD Patches Three Kernel Flaws That Enable Local Privilege Escalation

Do Son July 10, 2026 0
Read More Read more about FreeBSD Patches Three Kernel Flaws That Enable Local Privilege Escalation
Kafka Authentication Bypass in the OAUTHBEARER JWT Path Kafka authentication bypass through OAUTHBEARER JWT replay on Apache Kafka 4.0.x brokers
  • Vulnerability Report

Kafka Authentication Bypass in the OAUTHBEARER JWT Path

Do Son July 10, 2026 0
Read More Read more about Kafka Authentication Bypass in the OAUTHBEARER JWT Path
FastNetMon Launches Netomics, a Self-Hosted Routing Intelligence Platform Netomics_Self-hosted_Routing_Intelligence_for_Netw_1783602857g1YFYzWQZz
  • Press Release

FastNetMon Launches Netomics, a Self-Hosted Routing Intelligence Platform

cybernewswire July 10, 2026 0
Read More Read more about FastNetMon Launches Netomics, a Self-Hosted Routing Intelligence Platform
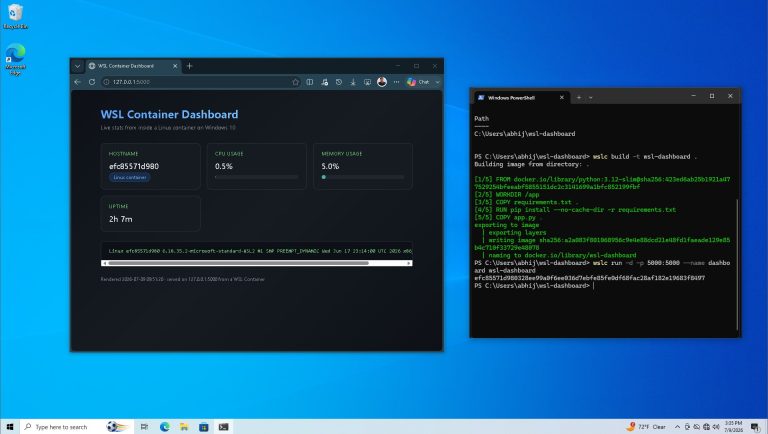
WSL Containers Now Runs on Windows 10 Too WSL Containers running on Windows 10 without Docker Desktop using wslc command in Windows Terminal
  • Windows

WSL Containers Now Runs on Windows 10 Too

Do Son July 10, 2026 0
Read More Read more about WSL Containers Now Runs on Windows 10 Too
CVE-2026-13753: HP Missing Authorization Vulnerability HP Deskjet missing authorization vulnerability CVE-2026-13753 exposing printer API security flaw
  • Vulnerability Report

CVE-2026-13753: HP Missing Authorization Vulnerability

Do Son July 10, 2026 0
Read More Read more about CVE-2026-13753: HP Missing Authorization Vulnerability
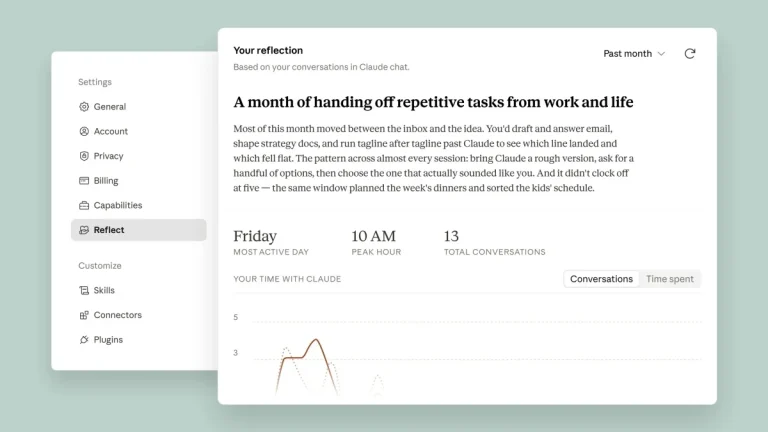
Claude Reflect Dashboard: Anthropic’s New AI Tool Claude Reflect dashboard interface visualizing AI usage statistics and productivity metrics.
  • Technology

Claude Reflect Dashboard: Anthropic’s New AI Tool

Do Son July 10, 2026 0
Read More Read more about Claude Reflect Dashboard: Anthropic’s New AI Tool
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📧

Email Delivery
Get threat intel straight to your inbox.

♾️

Unlimited Vendors
Track every technology in your stack.

🚨

All New CVE Alerts
Be the first to know about new flaws.

⚙️

Custom EPSS Threshold
Filter noise, focus on real risks.

💬

Slack & Teams Webhook
Integrate directly into your SecOps.

🚫

100% Ad-Free
Enjoy an uninterrupted reading experience.

$7/mo
Subscribe Now

🚨 Active Exploits in the Wild

  • CVE-2026-76461CVSS 9.8
    A vulnerability in the email parsing of Cisco AsyncOS Software for Cisco Secure Email Gateway could allow an...
    CISA KEV📅 Added to KEV: Sep 14, 2026
  • CVE-2026-51990
    A critical remote code execution vulnerability in Sogou Input Method, one of the most widely used Chinese-language input...
    Admin intel📅 Updated: Sep 12, 2026
  • CVE-2026-85706CVSS 10.0
    GitLab has remediated an issue that, under certain conditions, an unauthenticated user could have read arbitrary files from...
    Admin intelCISA KEV📅 Added to KEV: Sep 11, 2026📅 Updated: Sep 11, 2026
  • CVE-2026-42016CVSS 8.1
    JFrog Artifactory (Self Hosted) versions before 7.133.11 are vulnerable to a privilege escalation attack due to a validation...
    Admin intelCISA KEV📅 Added to KEV: Sep 11, 2026📅 Updated: Sep 11, 2026
  • CVE-2026-42018CVSS 7.5
    JFrog Artifactory could return an internal anonymous-user token to an unauthenticated caller when anonymous access is disabled, potentially...
    Admin intelCISA KEV📅 Added to KEV: Sep 11, 2026📅 Updated: Sep 11, 2026
  • CVE-2026-84869CVSS 9.9
    A condition in the ScreenConnect client may allow files to be transferred and executed through an active remote...
    CISA KEV📅 Added to KEV: Sep 11, 2026
  • CVE-2026-20079CVSS 10.0
    A vulnerability in the web interface of Cisco Secure Firewall Management Center (FMC) Software could allow an unauthenticated,...
    Admin intelCISA KEV📅 Added to KEV: Sep 9, 2026📅 Updated: Sep 9, 2026
  • CVE-2025-25249CVSS 8.1
    A heap-based buffer overflow vulnerability in Fortinet FortiOS 7.6.0 through 7.6.3, FortiOS 7.4.0 through 7.4.8, FortiOS 7.2.0 through...
    Admin intelCISA KEV📅 Added to KEV: Sep 9, 2026📅 Updated: Sep 9, 2026
Powered by CVE Watchtower

🔴 Live Critical Threats

  • CVE-2026-12944CVSS 9.6
    IBM Langflow OSS 1.0.0 through 1.10.0 can allow attackers to execute arbitrary...
  • CVE-2026-16338CVSS 9.9
    IBM DataStage on Cloud Pak for Data 5.4.0.0 IBM DataStage could allow...
  • CVE-2026-59178CVSS 9.8
    ESPHome Device Builder Dashboard is a dashboard for the ESPHome home management...
  • CVE-2026-90945CVSS 9.8
    Crawlab through 0.6.3 uses a hard-coded HMAC-SHA256 secret for JWT token signing...
  • CVE-2026-90942CVSS 9.6
    Casdoor through 4.4.0 fails to properly mask the instance-wide built-in certificate private...
  • CVE-2026-76461CVSS 9.8
    A vulnerability in the email parsing of Cisco AsyncOS Software for Cisco...
  • CVE-2026-76443CVSS 9.8
    As part of Cisco's ongoing commitment to proactive security and product quality,...
  • CVE-2026-76441CVSS 9.8
    As part of Cisco's ongoing commitment to proactive security and product quality,...
  • CVE-2026-76440CVSS 9.8
    As part of Cisco's ongoing commitment to proactive security and product quality,...
  • CVE-2026-20353CVSS 9.8
    As part of Cisco's ongoing commitment to proactive security and product quality,...
Powered by CVE WATCHTOWER

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.