Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
The Real Cost of a Data Breach vs. Building Security In From Day One Browser fingerprint
  • Technique

The Real Cost of a Data Breach vs. Building Security In From Day One

Do Son September 9, 2026 0

What a data breach actually costs vs. what building security in from day one costs — a line-item comparison for security and IT leaders.
Trojanized Fake macOS Installers Spread OtterCookie Backdoor Trojanized fake macOS installers used in Contagious Interview campaign
  • Cybercriminals

Trojanized Fake macOS Installers Spread OtterCookie Backdoor

Do Son September 9, 2026 0

Security teams uncovered trojanized fake macOS installers tied to North Korean campaigns that deploy OtterCookie malware on Apple devices.
Microsoft Unveils Unmetered Intelligence for Windows 11 Microsoft unmetered intelligence vision presentation at IFA 2026.
  • Windows

Microsoft Unveils Unmetered Intelligence for Windows 11

Do Son September 9, 2026 0

Discover Microsoft's unmetered intelligence vision. Learn how local AI agents on Windows 11 PCs will replace cloud reliance and token economics.
OpenAI Launches ChatGPT Images 2.5 with 50% Lower Latency and Precision Editing ChatGPT Images 2.5 with GPT-Image-2.5 Flare and Sunburst for faster image generation and precision editing
  • Technology

OpenAI Launches ChatGPT Images 2.5 with 50% Lower Latency and Precision Editing

Do Son September 9, 2026 0

ChatGPT Images 2.5 cuts generation latency by 50%, improves transparent backgrounds and multi-turn editing, with Flare and Sunburst API models.
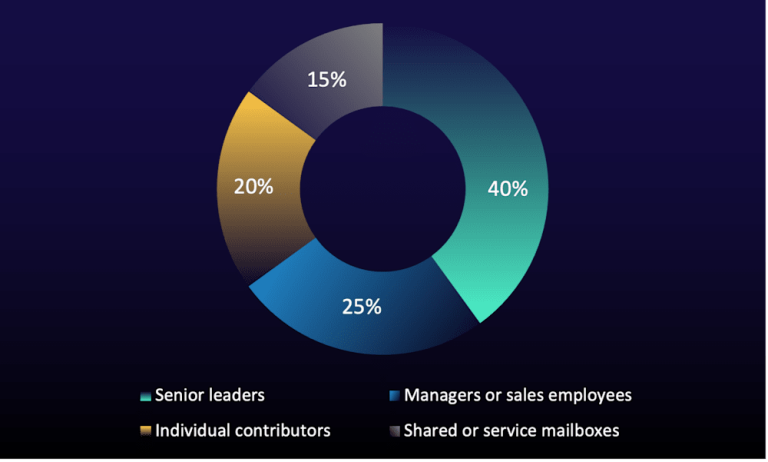
Microsoft 365 RejectDirectSend Bypass Lets Attackers Spoof Internal Emails Diagram illustrating the Microsoft 365 RejectDirectSend bypass method
  • Cybercriminals

Microsoft 365 RejectDirectSend Bypass Lets Attackers Spoof Internal Emails

Do Son September 9, 2026 0

A Microsoft 365 RejectDirectSend bypass lets attackers spoof internal emails. Learn how this RejectDirectSend bypass works and how to protect your tenant.
ClickFix Browser Attack Steals Crypto via Google Sheets ClickFix browser attack diagram showing Google Sheets C2 injecting a crypto web skimmer into Chrome
  • Malware

ClickFix Browser Attack Steals Crypto via Google Sheets

Do Son September 9, 2026 0

A ClickFix browser attack uses Google Sheets C2 to inject a crypto web skimmer into Chrome. See how Cisco Talos traced the theft.
Windows 11 Is Finally Getting Automatic Light and Dark Theme Switching Windows 11 auto dark mode switching between light and dark themes by sunrise and sunset
  • Windows

Windows 11 Is Finally Getting Automatic Light and Dark Theme Switching

Do Son September 9, 2026 0

Windows 11 auto dark mode switching surfaces in preview builds, with scheduled and sunrise-to-sunset options for light and dark themes.
Authentication Is Not Session Security: Why Passkeys, 2FA, QR Login and Active Sessions Protect Different Layers Telegram t.me domain serverHold status blocking all contact links and shared content URLs
  • Technique

Authentication Is Not Session Security: Why Passkeys, 2FA, QR Login and Active Sessions Protect Different Layers

Do Son September 9, 2026 0
A user can enable a passkey, protect an account with Telegram’s Two-Step Verification and still lose control...
Read More Read more about Authentication Is Not Session Security: Why Passkeys, 2FA, QR Login and Active Sessions Protect Different Layers
Apache Impala Vulnerabilities Expose Big Data to Remote Code Execution Apache Impala vulnerabilities including authentication bypass and CVE-2026-65181
  • Vulnerability Report

Apache Impala Vulnerabilities Expose Big Data to Remote Code Execution

Do Son September 9, 2026 0

Four Apache Impala vulnerabilities expose systems to remote code execution and authentication bypass. Upgrade to Impala 4.5.2 to secure your clusters now.
Asahi Linux M3 Support Reaches the Mainline Kernel, but GPU and Display Remain Gaps Asahi Linux M3 support progress for Apple Silicon MacBook feature table
  • Linux

Asahi Linux M3 Support Reaches the Mainline Kernel, but GPU and Display Remain Gaps

Do Son September 9, 2026 0

Asahi Linux M3 support reaches the mainline kernel with Wi-Fi and storage working, but GPU, Thunderbolt, and display remain in development.
CVE-2026-84372 PoC Disclosed: Predis Command Injection Flaw Predis command injection flaw CVE-2026-84372 Predis CRLF smuggling
  • Vulnerability Report

CVE-2026-84372 PoC Disclosed: Predis Command Injection Flaw

Do Son September 9, 2026 0

Details and PoC for CVE-2026-84372 are publicly disclosed. This Predis command injection flaw via CRLF smuggling allows complete cluster compromise.
2.7M Users Exposed to CVE-2026-85061: Critical 10.0 CVSS MapLibre Flaw MapLibre XSS vulnerability CVE-2026-85061 mechanism
  • Vulnerability Report

2.7M Users Exposed to CVE-2026-85061: Critical 10.0 CVSS MapLibre Flaw

Do Son September 9, 2026 0

A critical MapLibre XSS vulnerability allows zero-click code execution in 2.7M weekly downloads. Discover how CVE-2026-85061 works and how to patch now.
Chrome Moves to a Two-Week Release Cycle Starting with Chrome 153 Chrome two-week release cycle starting with Chrome 153 across desktop and mobile
  • Technology

Chrome Moves to a Two-Week Release Cycle Starting with Chrome 153

Do Son September 9, 2026 0

Chrome's two-week release cycle begins with Chrome 153, doubling the pace of features and security patches while Extended Stable stays at 8 weeks.
CVE-2026-67401: cPanel Flaw Grants Full Control of the Server cPanel SQL injection flaw exploit diagram showing CVE-2026-67401
  • Vulnerability Report

CVE-2026-67401: cPanel Flaw Grants Full Control of the Server

Do Son September 9, 2026 0

A critical CVE-2026-67401 cPanel SQL injection flaw in EmailTrack allows authenticated users to gain full control of the server. Patch your system today.
Redis Cryptomining Botnet Hijacks 3,562 Servers for Monero Liquid Network hack diagram showing Bitcoin transfer and white hat bounty negotiation
  • Malware

Redis Cryptomining Botnet Hijacks 3,562 Servers for Monero

Do Son September 9, 2026 0

A Redis cryptomining botnet used a rogue replication attack to hijack 3,562 servers for Monero mining. See how the campaign worked.
CVE-2026-41870: Unauthenticated RCE in Apache Nutch Apache Nutch vulnerability alert showing unauthenticated remote code execution flaw CVE-2026-41870 in the Nutch REST API
  • Vulnerability Report

CVE-2026-41870: Unauthenticated RCE in Apache Nutch

Do Son September 9, 2026 0

Apache Nutch vulnerabilities include CVE-2026-41870, an unauthenticated remote code execution flaw. See affected versions and fixes.
Critical Siemens Vulnerabilities Hit Industrial Edge and OIS Siemens vulnerabilities advisory dashboard showing CVE-2026-18963 authentication bypass and CVE-2026-50093 file upload flaws
  • Vulnerability Report

Critical Siemens Vulnerabilities Hit Industrial Edge and OIS

Do Son September 9, 2026 0

Two critical Siemens vulnerabilities (CVE-2026-18963, CVE-2026-50093) allow account takeover and root access. See affected versions and fixes.
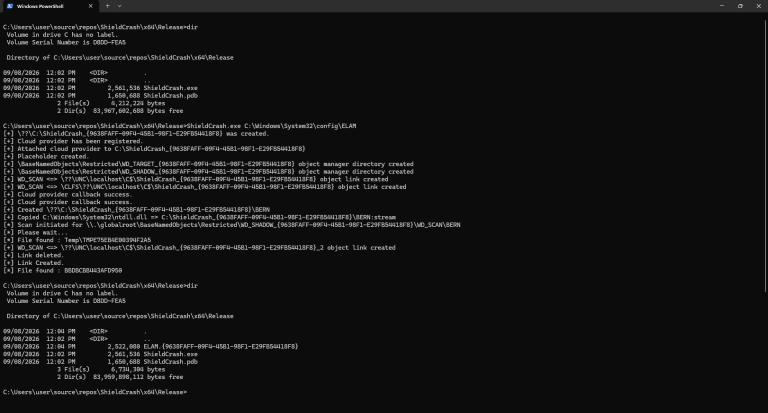
ShieldCrash: Windows Defender 0day With Public PoC Exploit Windows Defender 0day CVE-2026-69414 ShieldCrash proof-of-concept exploit reading files as SYSTEM
  • Vulnerability Report

ShieldCrash: Windows Defender 0day With Public PoC Exploit

Do Son September 9, 2026 0

A Windows Defender 0day, CVE-2026-69414, has public PoC exploit code. ShieldCrash reads files as SYSTEM on all supported Windows versions.
CVE-2026-78234 (CVSS 9.9): Critical Hawtio Operator Vulnerability Exposes Service Impersonation Hawtio Operator vulnerability CVE-2026-78234 exploitation mechanism
  • Vulnerability Report

CVE-2026-78234 (CVSS 9.9): Critical Hawtio Operator Vulnerability Exposes Service Impersonation

Do Son September 9, 2026 0

A critical Hawtio Operator vulnerability, tracked as CVE-2026-78234, allows in-cluster service impersonation. Discover the impact and mitigation steps.
Chrome 153 Patches Zero-Day CVE-2026-87491 Exploited in the Wild Chrome zero-day CVE-2026-87491 V8 flaw exploited in the wild patched in Chrome 153 stable update
  • Vulnerability Report

Chrome 153 Patches Zero-Day CVE-2026-87491 Exploited in the Wild

Do Son September 9, 2026 0

Google patched a Chrome zero-day, CVE-2026-87491, exploited in the wild. Chrome 153 fixes 230 flaws including critical WebGL bugs. Update now.

Attackers Use AI Tools to Hit Latin American Orgs Seedworm Espionage Campaign 2026 ChromElevator Stealer DLL Sideloading SIM Swapping Crypto Theft Lazarus Comebacker, Aerospace Espionage Delete PlugX Malware
  • Cybercriminals

Attackers Use AI Tools to Hit Latin American Orgs

Do Son September 9, 2026 0

Unit 42 exposes AI-powered cyberattacks across Latin America, where LLM-assisted actors hit government, water, and financial targets.
US Agencies Warn of Malicious AI Distillation Campaigns Diagram showing malicious AI distillation campaigns targeting frontier models
  • Cybercriminals

US Agencies Warn of Malicious AI Distillation Campaigns

Do Son September 8, 2026 0

US agencies warn of malicious AI distillation campaigns. New data shows systematic extraction of US frontier AI models.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59360CVSS 9.8
    The killProcesses mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59361CVSS 9.8
    The cleanIptables mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2026-119923CVSS 9.3
    A heap-based buffer overflow in the TDS prelogin parser in the Babelfish for PostgreSQL extension versions 1.0-1.5, 2.1-2.15,...
    📅 Updated: Nov 7, 2026
  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121379CVSS 9.6
    The Tournamatch WordPress plugin before 4.7.1 does not validate or restrict the path of a previously stored profile...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.