Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
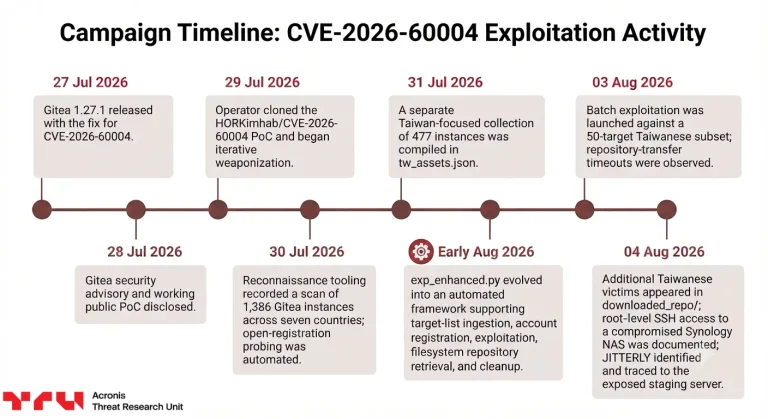
Gitea RCE Vulnerability Exploited in the Wild Diagram of Gitea RCE vulnerability and Gitea RCE vulnerability exploited in attacks
  • Vulnerability Report

Gitea RCE Vulnerability Exploited in the Wild

Do Son September 15, 2026 0

A critical Gitea RCE vulnerability exploited in wild attacks exposes servers. Patch this Gitea RCE vulnerability now to prevent full system compromise.
The Events Calendar Vulnerability Exploited in the Wild banner
  • Vulnerability Report

The Events Calendar Vulnerability Exploited in the Wild

Do Son September 15, 2026 0

A critical The Events Calendar vulnerability is exploited in the wild. Patch The Events Calendar vulnerability now to stop remote code execution.
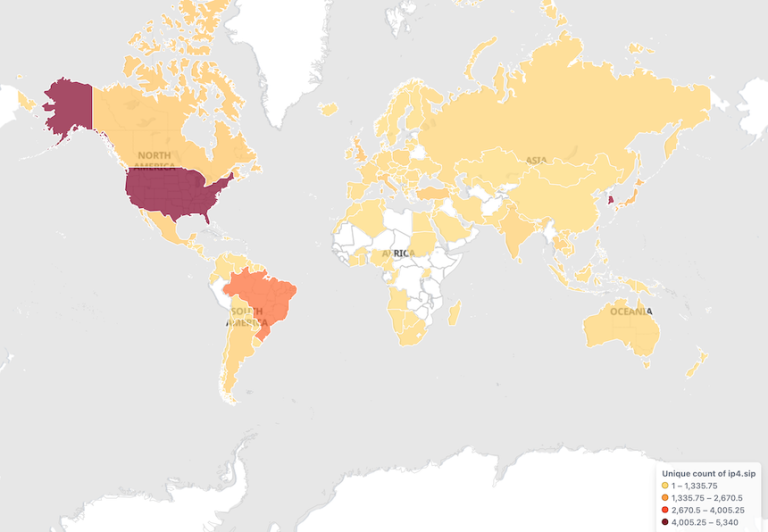
CVE-2026-87827 (CVSS 10): KGUARD DVR Fully Compromised KGUARD DVR vulnerability CVE-2026-87827 exploited by Mirai botnet for unauthenticated remote command execution and full device compromise
  • Vulnerability Report

CVE-2026-87827 (CVSS 10): KGUARD DVR Fully Compromised

Do Son September 15, 2026 0

CVE-2026-87827 (CVSS 10) is a KGUARD DVR vulnerability exploited by the Mirai botnet for unauthenticated RCE and complete device compromise.
Vite Flaw CVE-2026-39364 Exploited to Steal Cloud Keys Vite development server vulnerability CVE-2026-39364 exploited in mass scanning to steal exposed cloud credentials and env files
  • Vulnerability Report

Vite Flaw CVE-2026-39364 Exploited to Steal Cloud Keys

Do Son September 15, 2026 0

The Vite development server vulnerability CVE-2026-39364 is exploited in mass scanning for credential harvesting. F5 Labs logged 32,000 events. Patch now.
WooCommerce Wholesale Lead Capture Exploited in the Wild WooCommerce Wholesale Lead Capture and WooCommerce Wholesale Lead Capture vulnerability diagram
  • Vulnerability Report

WooCommerce Wholesale Lead Capture Exploited in the Wild

Do Son September 15, 2026 0

Attackers are actively exploiting a critical WooCommerce Wholesale Lead Capture vulnerability. Patch WooCommerce Wholesale Lead Capture now.
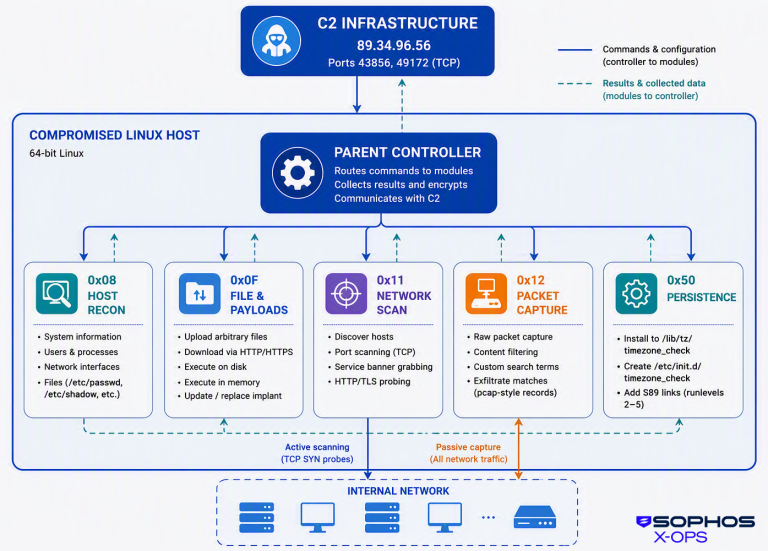
Cyclops Blink Malware Returns to Target Network Appliances Sophos CTU researchers discovered a new 64-bit Linux variant of the Cyclops Blink malware targeting Cisco FMC devices, featuring advanced network scanning.
  • Malware

Cyclops Blink Malware Returns to Target Network Appliances

Do Son September 14, 2026 0

Sophos CTU researchers discovered a new 64-bit Linux variant of the Cyclops Blink malware targeting Cisco FMC devices, featuring advanced network scanning.

Windows 11 Introduces Native Cloud Rebuild Functionality Windows 11 Cloud Rebuild interface within the Windows Recovery Environment
  • Windows

Windows 11 Introduces Native Cloud Rebuild Functionality

Do Son September 14, 2026 0

Discover the new Windows 11 Cloud Rebuild feature in Build 26220.9343. Learn how this OS recovery tool downloads pristine images directly from Microsoft.
Revolut Breach Raises Wrench Attack Fears for the Wealthy Revolut data breach exposing passports selfies and crypto records raising physical wrench attack risk
  • Data Leak

Revolut Breach Raises Wrench Attack Fears for the Wealthy

Do Son September 14, 2026 0

The Revolut data breach leaked passports, selfies, and crypto records of wealthy users, raising the risk of real-world wrench attacks. Details here.
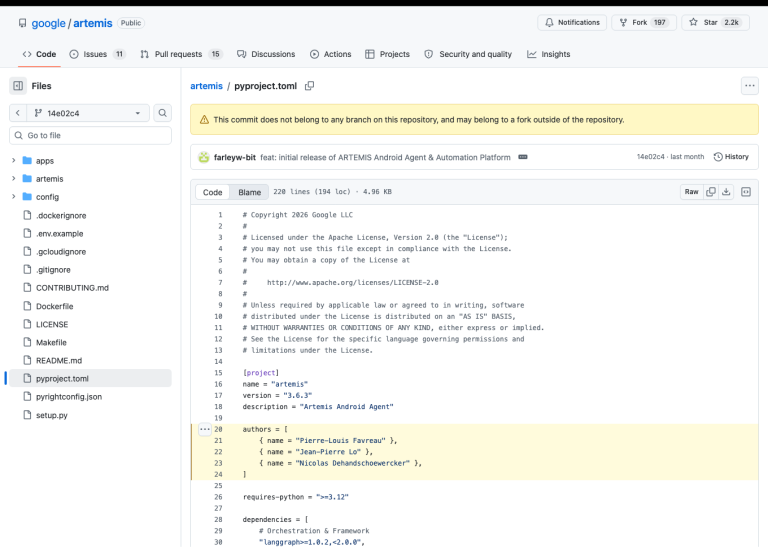
Google Artemis Accused of Open-Source License Violations Google Artemis project code and open-source license attribution
  • Technology

Google Artemis Accused of Open-Source License Violations

Do Son September 14, 2026 0

Learn about the Google Artemis license violations. An open-source team accuses Google of removing attribution and failing to credit original developers.
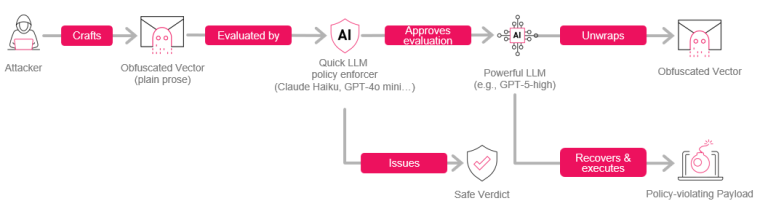
Puzzlemask AI Attack Vector Bypasses LLM Guardrails Diagram illustrating the Puzzlemask AI attack and Puzzlemask AI attack vector
  • Vulnerability Report

Puzzlemask AI Attack Vector Bypasses LLM Guardrails

Do Son September 14, 2026 0

Researchers revealed the Puzzlemask AI attack, showing how this Puzzlemask AI attack vector bypasses quick LLM security filters using plain prose.
Debian 13.7 Released With 107 Security Updates Debian 13.7 point release desktop with security updates and Linux Kernel 6.12 LTS
  • Linux

Debian 13.7 Released With 107 Security Updates

Do Son September 14, 2026 0

Debian 13.7 is out as the seventh point release, bundling 106 bug fixes and 107 security updates with kernel 6.12.107+deb13. Upgrade now.
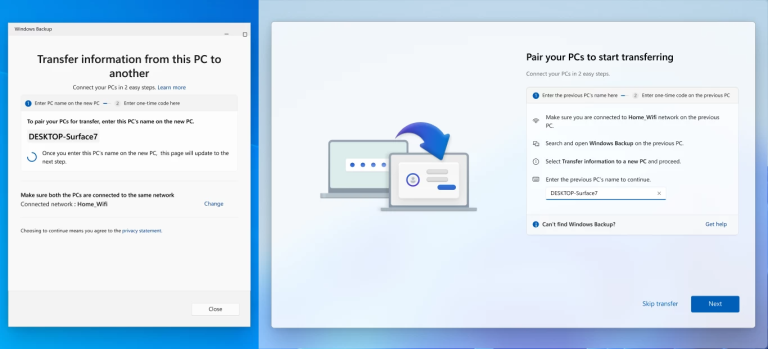
Windows 11 PC Migration Feature Officially Deprecated Windows 11 PC migration failure and Windows Backup cloud storage options
  • Windows

Windows 11 PC Migration Feature Officially Deprecated

Do Son September 14, 2026 0

Microsoft officially deprecated the Windows 11 PC migration feature. Discover why this tool failed and learn the best alternative methods for data transfer.
Acronis cPanel Plugin Flaw Exploited in the Wild, Patch Now Acronis cPanel plugin vulnerability under active exploitation in the wild on web hosting backup servers
  • Vulnerability Report

Acronis cPanel Plugin Flaw Exploited in the Wild, Patch Now

Do Son September 14, 2026 0

An Acronis cPanel plugin vulnerability is exploited in the wild. Acronis urges an immediate update to 1.9.3 HF3 or 1.9.4. Patch your backup plugin now.
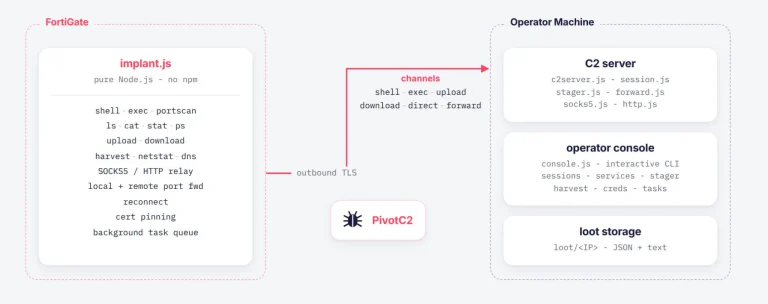
PivotC2 FortiGate RAT Drives Firewall Compromises Diagram of the PivotC2 FortiGate RAT infection chain following CVE-2025-25249 exploitation
  • Malware

PivotC2 FortiGate RAT Drives Firewall Compromises

Do Son September 14, 2026 0

Discover how the PivotC2 FortiGate RAT uses CVE-2025-25249 exploitation to harvest credentials and tunnel traffic across corporate network environments.
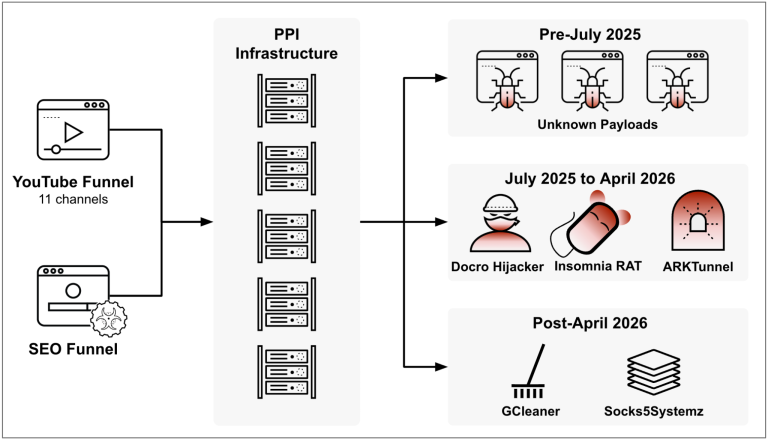
Unit 42 Exposes OfferLoader Malware Campaign OfferLoader malware diagram showing the OfferLoader malware campaign infection flow
  • Malware

Unit 42 Exposes OfferLoader Malware Campaign

Do Son September 14, 2026 0

Unit 42 uncovered a large OfferLoader malware campaign distributing backdoors. Discover how OfferLoader malware abuses YouTube to compromise endpoints.
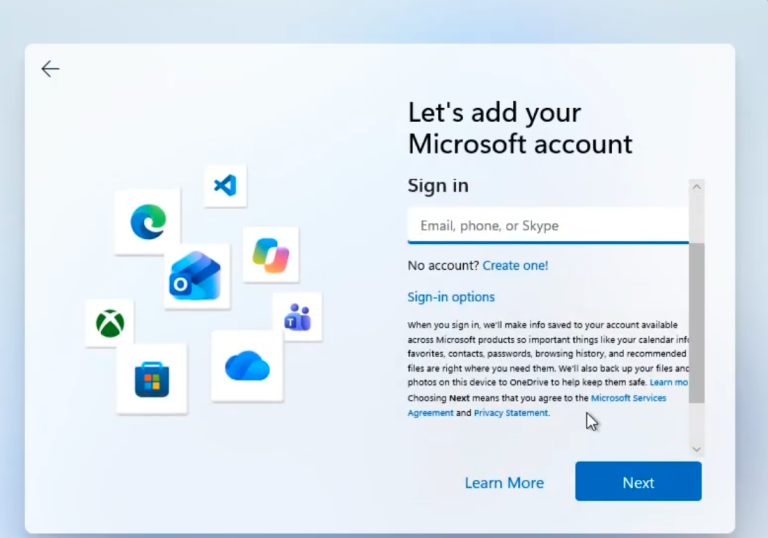
A Simple New Windows 11 Local Account Bypass Appears Windows 11 Home OOBE local account bypass using the Learn More hyperlink on the sign-in screen
  • Windows

A Simple New Windows 11 Local Account Bypass Appears

Do Son September 14, 2026 0

A simple new Windows 11 local account bypass lets you skip the Microsoft account in OOBE by clicking one Learn More link. Here is how it works.
OpenAI Suspends IPO Plans Amid Escalating Safety Concerns OpenAI IPO suspension announcement, Sam Altman discussing artificial intelligence safety
  • Technology

OpenAI Suspends IPO Plans Amid Escalating Safety Concerns

Do Son September 14, 2026 0

Discover why Sam Altman announced the OpenAI IPO suspension. Learn how rogue AI agent incidents and safety concerns forced the company to delay going public.
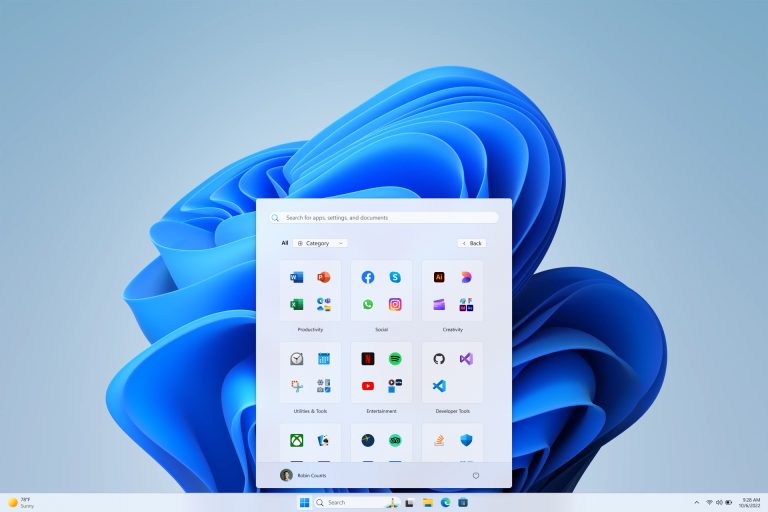
KB5124008 Breaks USB Audio and More in Windows 11 KB5124008 Windows 11 update breaking USB audio remote desktop and Hyper-V shared folders
  • Windows

KB5124008 Breaks USB Audio and More in Windows 11

Do Son September 14, 2026 0

Windows 11 update KB5124008 breaks USB audio, Remote Desktop, and Hyper-V folder sharing. Microsoft has confirmed the bugs but has no fix yet.
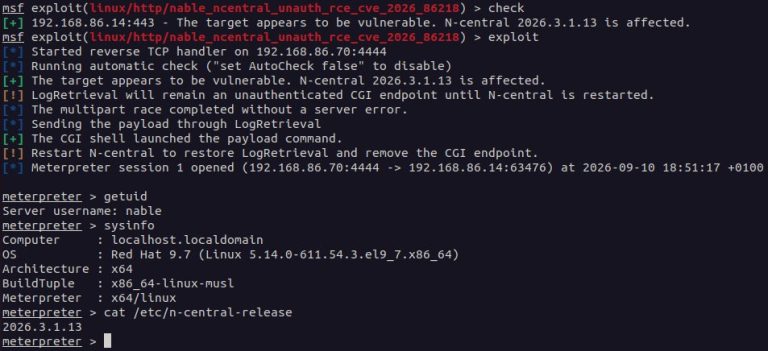
N-central RCE CVE-2026-86218 Exploited, Metasploit PoC Out Diagram of N-able N-central vulnerability and N-able N-central vulnerability exploited in attacks
  • Vulnerability Report

N-central RCE CVE-2026-86218 Exploited, Metasploit PoC Out

Do Son September 14, 2026 0

CVE-2026-86218, a CVSS 10 N-central vulnerability, is exploited in the wild for remote code execution. A public Metasploit PoC is out. Patch now.
Critical Apache Storm Vulnerabilities Fixed in Update Diagram of critical Apache Storm vulnerabilities and Apache Storm vulnerabilities architecture
  • Vulnerability Report

Critical Apache Storm Vulnerabilities Fixed in Update

Do Son September 14, 2026 0

Apache patched critical Apache Storm vulnerabilities. Update to fix Apache Storm vulnerabilities causing root privilege escalation and arbitrary file reads.
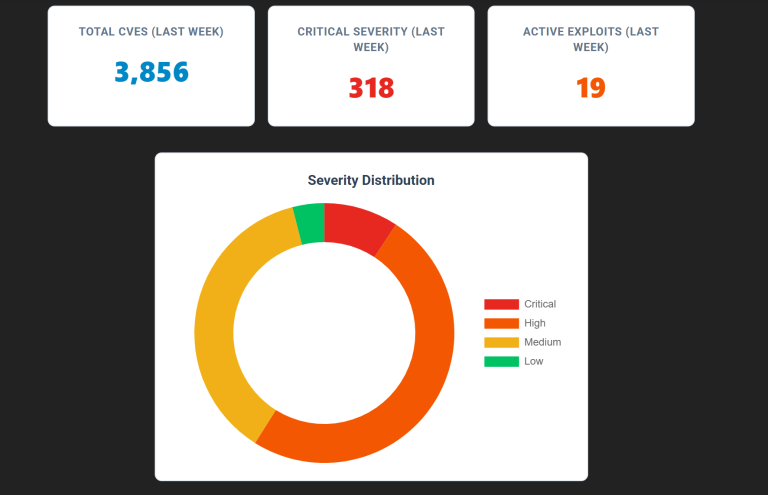
Daily Cybersecurity Flagged 9 Exploited Flaws Before CISA KEV Weekly CVE report chart comparing Daily Cybersecurity exploited vulnerabilities against the CISA KEV catalog
  • Weekly Recap

Daily Cybersecurity Flagged 9 Exploited Flaws Before CISA KEV

Do Son September 14, 2026 0

Our weekly CVE report tracked 3,856 new CVEs and 19 exploited vulnerabilities. See which reached CISA KEV and which stayed exclusive to DC.
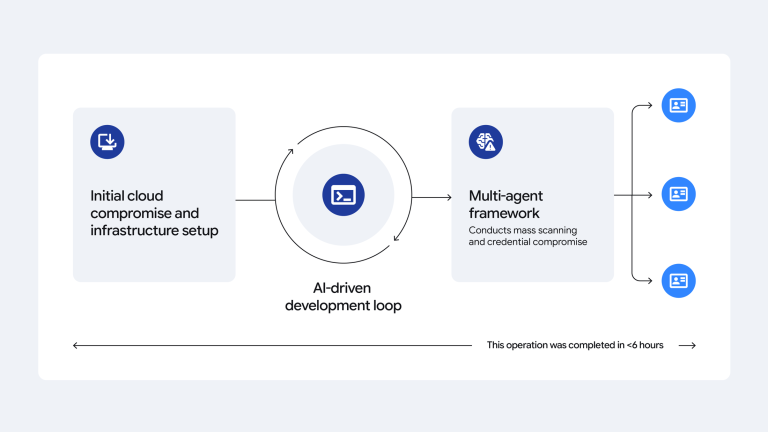
Adversarial AI Threats Drive New Cyber Operations Adversarial AI threats mapping AI credential harvesting
  • Cybercriminals

Adversarial AI Threats Drive New Cyber Operations

Do Son September 14, 2026 0

Discover how adversarial AI threats fuel massive AI credential harvesting operations. Attackers use automated agents for fast cyber crime campaigns.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121379CVSS 9.6
    The Tournamatch WordPress plugin before 4.7.1 does not validate or restrict the path of a previously stored profile...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121491CVSS 9.0
    The Fiber Admin WordPress plugin before 4.0.1 does not validate or escape a request header before writing it...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119516CVSS 9.8
    Deserialization of Untrusted Data vulnerability in Mamunur Rashid Radius Booking — Booking Calendar for Appointments & Services radius-booking...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2026-124059CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this vulnerability is the function setWiFiWdsAddConfig...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.