CheapSSLWEB Review: Best Place to Buy Cheap SSL Certificates with SSL Automation Technique CheapSSLWEB Review: Best Place to Buy Cheap SSL Certificates with SSL Automation Do Son July 18, 2026 0 Read More Read more about CheapSSLWEB Review: Best Place to Buy Cheap SSL Certificates with SSL Automation
Certera Review: A Trusted Leader in SSL Certificates, PKI, and Digital Trust Solutions Technique Certera Review: A Trusted Leader in SSL Certificates, PKI, and Digital Trust Solutions Do Son July 18, 2026 0 Read More Read more about Certera Review: A Trusted Leader in SSL Certificates, PKI, and Digital Trust Solutions
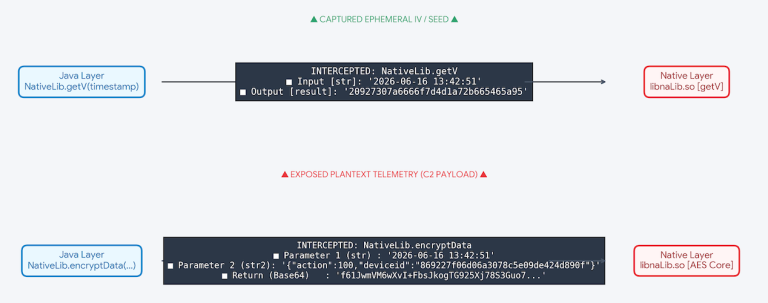
GoldPickaxe Banking Trojan Returns to Steal Faces and Bank Logins Malware GoldPickaxe Banking Trojan Returns to Steal Faces and Bank Logins Do Son July 17, 2026 0 Read More Read more about GoldPickaxe Banking Trojan Returns to Steal Faces and Bank Logins
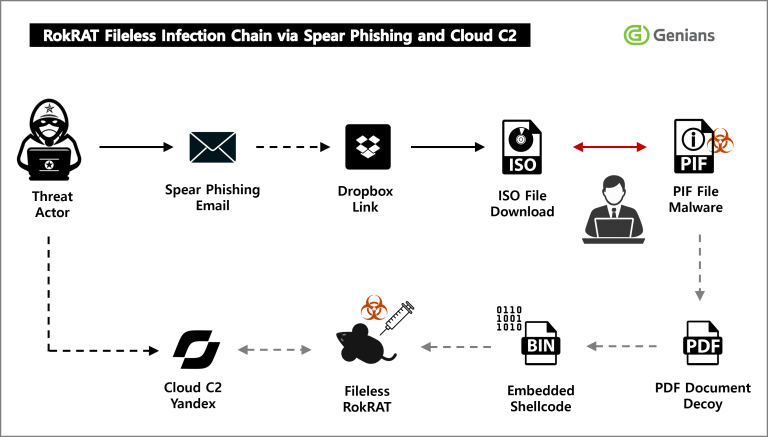
RokRAT Malware Hides in Fake PDF Files to Spy on Academics Malware RokRAT Malware Hides in Fake PDF Files to Spy on Academics Do Son July 17, 2026 0 Read More Read more about RokRAT Malware Hides in Fake PDF Files to Spy on Academics
CVE-2026-54523 (CVSS 9.6): Public PoC Exploit Enables Kyverno Privilege Escalation to Admin in Any Namespace Vulnerability Report CVE-2026-54523 (CVSS 9.6): Public PoC Exploit Enables Kyverno Privilege Escalation to Admin in Any Namespace Do Son July 17, 2026 0 Read More Read more about CVE-2026-54523 (CVSS 9.6): Public PoC Exploit Enables Kyverno Privilege Escalation to Admin in Any Namespace
Citrix Secure Access Vulnerability Lets Local Users Gain SYSTEM Privileges Vulnerability Report Citrix Secure Access Vulnerability Lets Local Users Gain SYSTEM Privileges Do Son July 17, 2026 0 Read More Read more about Citrix Secure Access Vulnerability Lets Local Users Gain SYSTEM Privileges
Misconfigured Server Exposes Three AiTM Phishing Operators Cybercriminals Misconfigured Server Exposes Three AiTM Phishing Operators Do Son July 17, 2026 0 Read More Read more about Misconfigured Server Exposes Three AiTM Phishing Operators
292 Fake GitHub Repositories Deliver BoryptGrab Infostealer to Windows Users Malware 292 Fake GitHub Repositories Deliver BoryptGrab Infostealer to Windows Users Do Son July 17, 2026 0 Read More Read more about 292 Fake GitHub Repositories Deliver BoryptGrab Infostealer to Windows Users
EU Orders Google to Open Android to Rival AI Assistants and Share Search Data Under the DMA Technology EU Orders Google to Open Android to Rival AI Assistants and Share Search Data Under the DMA Do Son July 17, 2026 0 Read More Read more about EU Orders Google to Open Android to Rival AI Assistants and Share Search Data Under the DMA
Farewell NotebookLM: Google Rebrands Its AI Research Tool as Gemini Notebook, Adds Native Code Execution Technology Farewell NotebookLM: Google Rebrands Its AI Research Tool as Gemini Notebook, Adds Native Code Execution Do Son July 17, 2026 0 Read More Read more about Farewell NotebookLM: Google Rebrands Its AI Research Tool as Gemini Notebook, Adds Native Code Execution
Chrome Security Update Patches Three Critical Use-After-Free Flaws in CameraCapture, GPU, and Network Vulnerability Report Chrome Security Update Patches Three Critical Use-After-Free Flaws in CameraCapture, GPU, and Network Do Son July 17, 2026 0 Read More Read more about Chrome Security Update Patches Three Critical Use-After-Free Flaws in CameraCapture, GPU, and Network
Supply Chain Trojan Targets Software Developers Through Project Files Malware Supply Chain Trojan Targets Software Developers Through Project Files Do Son July 17, 2026 0 Read More Read more about Supply Chain Trojan Targets Software Developers Through Project Files
CVE-2026-9770: Information Disclosure Vulnerability Exposes Admin Credentials on TP-Link Kasa Cameras Vulnerability Report CVE-2026-9770: Information Disclosure Vulnerability Exposes Admin Credentials on TP-Link Kasa Cameras Do Son July 17, 2026 0 Read More Read more about CVE-2026-9770: Information Disclosure Vulnerability Exposes Admin Credentials on TP-Link Kasa Cameras
CISA Adds FortiSandbox and SharePoint Flaws to KEV Catalog After Confirming Active Exploitation Vulnerability Report CISA Adds FortiSandbox and SharePoint Flaws to KEV Catalog After Confirming Active Exploitation Do Son July 17, 2026 0 Read More Read more about CISA Adds FortiSandbox and SharePoint Flaws to KEV Catalog After Confirming Active Exploitation
7-Zip Vulnerability CVE-2026-14266 Allows Remote Code Execution Through Crafted XZ Data Vulnerability Report 7-Zip Vulnerability CVE-2026-14266 Allows Remote Code Execution Through Crafted XZ Data Do Son July 16, 2026 0 Read More Read more about 7-Zip Vulnerability CVE-2026-14266 Allows Remote Code Execution Through Crafted XZ Data
Grok Build Goes Open Source for Community Audits but GitHub Issues and PRs Stay Closed Technology Grok Build Goes Open Source for Community Audits but GitHub Issues and PRs Stay Closed Do Son July 16, 2026 0 Read More Read more about Grok Build Goes Open Source for Community Audits but GitHub Issues and PRs Stay Closed
CVE-2026-15378: Blind SSRF Flaw in Red Hat OpenShift AI Vulnerability Report CVE-2026-15378: Blind SSRF Flaw in Red Hat OpenShift AI Do Son July 16, 2026 0 Read More Read more about CVE-2026-15378: Blind SSRF Flaw in Red Hat OpenShift AI
Microsoft Untangles Its Messy Windows Update Terminology: B Releases, Quality Updates, and More Windows Microsoft Untangles Its Messy Windows Update Terminology: B Releases, Quality Updates, and More Do Son July 16, 2026 0 Read More Read more about Microsoft Untangles Its Messy Windows Update Terminology: B Releases, Quality Updates, and More
Metabase Fixes CVE-2026-59827 and CVE-2026-59826 Remote Code Execution Flaws Vulnerability Report Metabase Fixes CVE-2026-59827 and CVE-2026-59826 Remote Code Execution Flaws Do Son July 16, 2026 0 Read More Read more about Metabase Fixes CVE-2026-59827 and CVE-2026-59826 Remote Code Execution Flaws
Apache IoTDB Patches Five Security Flaws, Upgrade to 2.0.10 Vulnerability Report Apache IoTDB Patches Five Security Flaws, Upgrade to 2.0.10 Do Son July 16, 2026 0 Read More Read more about Apache IoTDB Patches Five Security Flaws, Upgrade to 2.0.10
SonicWall SMA1000 CVE-2026-15409 (CVSS 10.0) RCE Exploited in the Wild as Public PoC Drops Vulnerability Report SonicWall SMA1000 CVE-2026-15409 (CVSS 10.0) RCE Exploited in the Wild as Public PoC Drops Do Son July 16, 2026 0 Read More Read more about SonicWall SMA1000 CVE-2026-15409 (CVSS 10.0) RCE Exploited in the Wild as Public PoC Drops
Dell PowerFlex Manager Flaw CVE-2026-56688 Allows Root Command Execution Vulnerability Report Dell PowerFlex Manager Flaw CVE-2026-56688 Allows Root Command Execution Do Son July 16, 2026 0 Read More Read more about Dell PowerFlex Manager Flaw CVE-2026-56688 Allows Root Command Execution

 Do Son