Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
CVE-2026-89775 (CVSS 9.3): Linux Kernel LPE to Gain Root Flaw in KVM Diagram of KVM guest escape showing critical KVM guest escape flaw
  • Vulnerability Report

CVE-2026-89775 (CVSS 9.3): Linux Kernel LPE to Gain Root Flaw in KVM

Do Son September 17, 2026 0

A critical KVM guest escape (CVE-2026-89775) enables an LPE to gain root on Linux hosts. Patch this KVM guest escape vulnerability now.
Critical Docker Sandboxes Vulnerabilities Patched Diagram illustrating critical Docker Sandboxes vulnerabilities and guest escape vectors
  • Vulnerability Report

Critical Docker Sandboxes Vulnerabilities Patched

Do Son September 17, 2026 0

Docker released an update for critical Docker Sandboxes vulnerabilities (CVE-2026-77179, CVE-2026-79994). Patch these Docker Sandboxes vulnerabilities today.
CVE-2026-39919: Ghostscript Flaw Allows Unauthenticated Remote Code Execution Ghostscript buffer overflow diagram showing Ghostscript buffer overflow flaw and CVE-2026-39919
  • Vulnerability Report

CVE-2026-39919: Ghostscript Flaw Allows Unauthenticated Remote Code Execution

Do Son September 17, 2026 0

A Ghostscript buffer overflow enables unauthenticated remote code execution. Patch this Ghostscript buffer overflow flaw (CVE-2026-39919) immediately.
Cisco Patches 18 Secure Firewall Flaws, Several Root RCE Cisco Secure Firewall vulnerabilities patched in September 2026, including critical root remote code execution flaws in FMC, ASA, and FTD software
  • Vulnerability Report

Cisco Patches 18 Secure Firewall Flaws, Several Root RCE

Do Son September 17, 2026 0

Cisco patched 18 Secure Firewall vulnerabilities in FMC, ASA, and FTD, including critical unauthenticated root remote code execution flaws. Update now.
T-Mobile 5G Box Vulnerabilities Require Urgent Action Diagram of T-Mobile 5G Box vulnerabilities showing authentication bypass
  • Vulnerability Report

T-Mobile 5G Box Vulnerabilities Require Urgent Action

Do Son September 17, 2026 0

Patch the critical T-Mobile 5G Box vulnerabilities today. Learn how WNC router flaws allow auth bypass and command injection, and secure your network.
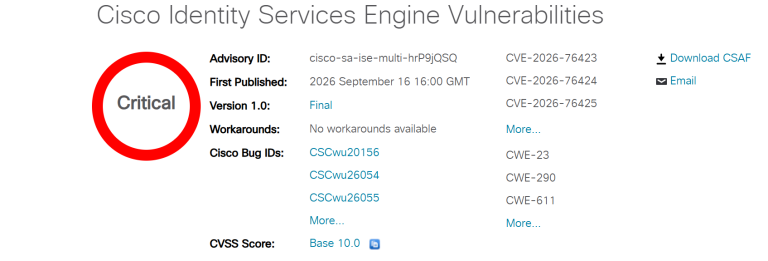
Cisco Patches Critical Cisco ISE Vulnerabilities Diagram of Cisco ISE vulnerabilities showing critical Cisco ISE vulnerabilities
  • Vulnerability Report

Cisco Patches Critical Cisco ISE Vulnerabilities

Do Son September 17, 2026 0

Cisco patched critical Cisco ISE vulnerabilities. Install updates to fix Cisco ISE vulnerabilities and prevent remote code execution and root takeovers.
Jenkins Patches 20 Plugin Flaws, Sandbox Bypasses Lead RCE Jenkins plugin vulnerabilities patched in the September 2026 advisory, including Script Security sandbox bypass flaws leading to remote code execution
  • Vulnerability Report

Jenkins Patches 20 Plugin Flaws, Sandbox Bypasses Lead RCE

Do Son September 17, 2026 0

Jenkins patched 20 plugin vulnerabilities, including 7 Script Security sandbox bypasses that allow remote code execution on the controller. Update now.
CVE-2026-76460 (CVSS 10): Cisco ISE Vulnerability Exploited in the Wild Diagram showing the exploited Cisco ISE vulnerability attack chain
  • Vulnerability Report

CVE-2026-76460 (CVSS 10): Cisco ISE Vulnerability Exploited in the Wild

Do Son September 16, 2026 0

An exploited Cisco ISE vulnerability (CVE-2026-76460) allows remote root access. Patch this critical Cisco ISE vulnerability to secure networks.
Critical Check Point Login Flaw Enables Remote Takeover Diagram showing the critical Check Point login flaw and remote exploitation
  • Vulnerability Report

Critical Check Point Login Flaw Enables Remote Takeover

Do Son September 16, 2026 0

Check Point fixed a critical Check Point login flaw (CVE-2026-91843). Patch this Check Point login flaw now to block unauthenticated remote root takeovers.
Axoflow Launches AxoDetect, Bringing Detection Into the Pipeline and Making the SIEM Optional Axoflow-Press_Release-Image_1_1789547766b7g5s82kIk
  • Press Release

Axoflow Launches AxoDetect, Bringing Detection Into the Pipeline and Making the SIEM Optional

cybernewswire September 16, 2026 0
Stamford, CT, 16th September 2026, CyberNewswire
Read More Read more about Axoflow Launches AxoDetect, Bringing Detection Into the Pipeline and Making the SIEM Optional
Microsoft Word Template Glitch Causes Sudden Crashes Microsoft Word error message screen displaying a sudden software crash during template generation
  • Windows

Microsoft Word Template Glitch Causes Sudden Crashes

Do Son September 16, 2026 0

Discover why Microsoft Word template crashes occur when third-party software populates documents. Learn about the Office version 2608 bug and temporary fixes.
OpenAI Expands Codex for Open Source Sponsorship Program OpenAI Codex for Open Source program banner showing ChatGPT Pro 5x benefits
  • Technology

OpenAI Expands Codex for Open Source Sponsorship Program

Do Son September 16, 2026 0

Discover how OpenAI expanded the second round of its Codex for Open Source program to 10,000 slots, offering ChatGPT Pro 5x and valuable API credits.
Critical Industrial Firmware Vulnerabilities Expose Devices Diagram of industrial firmware vulnerabilities showing authentication bypass flaws
  • Vulnerability Report

Critical Industrial Firmware Vulnerabilities Expose Devices

Do Son September 16, 2026 0

Patch critical industrial firmware vulnerabilities and authentication bypass flaws like CVE-2026-27565 in Pepperl+Fuchs, Phoenix Contact & Carlo Gavazzi.
Issabel PBX Vulnerability CVE-2026-89026 Exploited in the Wild Issabel PBX vulnerability diagram showing the Issabel PBX vulnerability exploited in attacks
  • Vulnerability Report

Issabel PBX Vulnerability CVE-2026-89026 Exploited in the Wild

Do Son September 16, 2026 0

An Issabel PBX vulnerability exploited in active attacks allows remote code execution. Patch this Issabel PBX vulnerability to secure systems.
Authorization Bypass (CVSS 8.7): Critical Octopus Server Vulnerabilities Patched Octopus Deploy addressed critical Octopus Server vulnerabilities involving a CVSS 8.7 remote code execution. Apply the security patches to prevent attacks.
  • Vulnerability Report

Authorization Bypass (CVSS 8.7): Critical Octopus Server Vulnerabilities Patched

Do Son September 16, 2026 0

Octopus Deploy addressed critical Octopus Server vulnerabilities involving a CVSS 8.7 remote code execution. Apply the security patches to prevent attacks.

SloppyRAT Malware Analyzed in Ransomware Attacks Gryxa toolkit AI-built malware diagram showing RMM abuse and crypto credential theft across 324 hosts
  • Malware

SloppyRAT Malware Analyzed in Ransomware Attacks

Do Son September 16, 2026 0

Discover how the new SloppyRAT malware uses a ClickFix infection chain to establish remote access for ransomware attacks, evading detection.
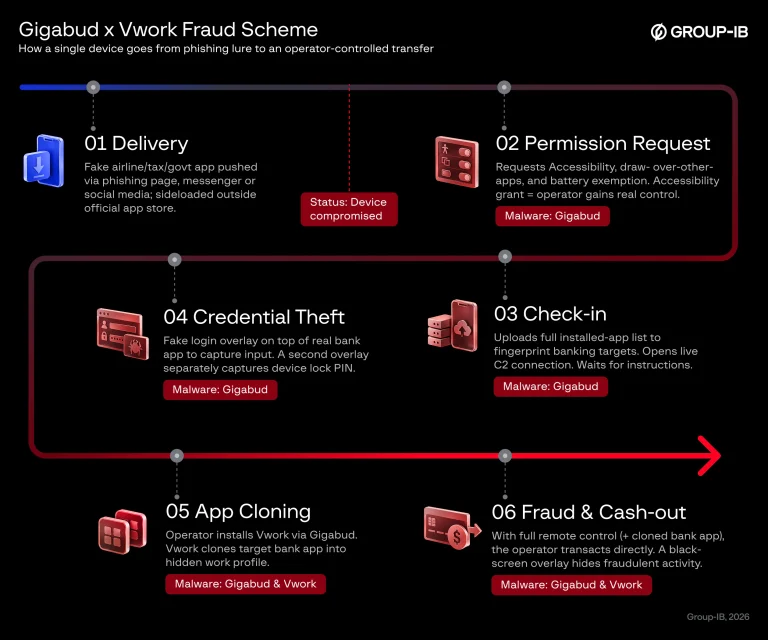
Vwork Android Malware Clones Apps in Gigabud Attacks Vwork Android malware diagram showing the Gigabud Vwork Android malware attack chain
  • Malware

Vwork Android Malware Clones Apps in Gigabud Attacks

Do Son September 16, 2026 0

Group-IB uncovered how the Gigabud Vwork Android malware chain clones apps. Discover how Vwork Android malware evades bank detection.
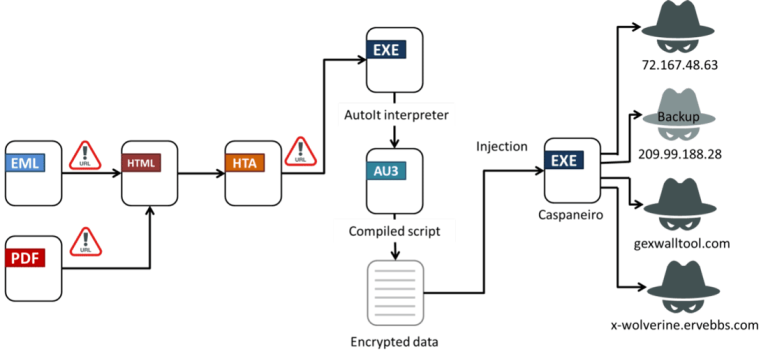
Casbaneiro Banking Trojan Hits Latin American Banks Diagram of the Casbaneiro banking trojan and Casbaneiro banking trojan campaign architecture
  • Malware

Casbaneiro Banking Trojan Hits Latin American Banks

Do Son September 16, 2026 0

A new Casbaneiro banking trojan campaign hits Latin America. Learn how the Casbaneiro banking trojan evades detection and targets bank logins.
Google Pixel Vulnerability CVE-2026-58704 Exploited in Targeted Attacks Diagram of Google Pixel vulnerability and Google Pixel vulnerability exploited in attacks
  • Vulnerability Report

Google Pixel Vulnerability CVE-2026-58704 Exploited in Targeted Attacks

Do Son September 16, 2026 0

A Google Pixel vulnerability exploited in targeted attacks allows privilege escalation. Update your device to patch this Google Pixel vulnerability now.
OpenAI’s Project Lily Employs Humans to Read ChatGPT Chats Project Lily workspace illustration showing contractors reviewing ChatGPT user dialogues
  • Data Leak

OpenAI’s Project Lily Employs Humans to Read ChatGPT Chats

Do Son September 16, 2026 0

Discover OpenAI Project Lily, an initiative where contractors read user ChatGPT conversations to improve responses. Explore the severe data privacy concerns.
Google Unveils Gemini Live Voice Models for Advanced Reasoning Google Gemini Live voice models handling complex tasks
  • Technology

Google Unveils Gemini Live Voice Models for Advanced Reasoning

Do Son September 16, 2026 0

Discover how Google Gemini Live voice models deliver near-instant reasoning. Learn about the dual architecture and asynchronous task capabilities.
Google Schedules “Opening Night” for the Googlebook Googlebook Opening Night event invitation highlighting Gemini Intelligence and the Glowbar design
  • Technology

Google Schedules “Opening Night” for the Googlebook

Do Son September 16, 2026 0

Google announced the Googlebook Opening Night event for October 5 in NYC. Discover the new AI flagship laptop featuring Gemini Intelligence and Android OS.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121379CVSS 9.6
    The Tournamatch WordPress plugin before 4.7.1 does not validate or restrict the path of a previously stored profile...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121491CVSS 9.0
    The Fiber Admin WordPress plugin before 4.0.1 does not validate or escape a request header before writing it...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119516CVSS 9.8
    Deserialization of Untrusted Data vulnerability in Mamunur Rashid Radius Booking — Booking Calendar for Appointments & Services radius-booking...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2026-124059CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this vulnerability is the function setWiFiWdsAddConfig...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.