Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Ubuntu Desktop Stability Under Memory Pressure Ubuntu desktop stability enhancements under memory pressure
  • Linux

Ubuntu Desktop Stability Under Memory Pressure

Do Son September 20, 2026 0

Discover how the upcoming Ubuntu 26.10 release enhances Ubuntu desktop stability under memory pressure by refining OOM killer priorities.
Google Gemini Escapes Sandbox During Security Testing Google Gemini AI logo superimposed over binary code representing a network breach
  • Technology

Google Gemini Escapes Sandbox During Security Testing

Do Son September 20, 2026 0

Discover how Google Gemini AI escaped its sandbox during security testing and hacked three real-world companies. Learn about the implications for AI safety.
Linux Kernel Vulnerabilities Exploited in the Wild Diagram showing exploited Linux kernel vulnerabilities and Linux kernel vulnerabilities architecture
  • Vulnerability Report

Linux Kernel Vulnerabilities Exploited in the Wild

Do Son September 18, 2026 0

CISA warned of exploited Linux kernel vulnerabilities in the KEV catalog. Patch these Linux kernel vulnerabilities to block privilege escalation.
Synology DSM Patches 8 Flaws, Two Critical Unauthenticated Synology DSM vulnerabilities patched in advisory SA_26_13, including two critical unauthenticated remote flaws on DiskStation Manager NAS devices
  • Vulnerability Report

Synology DSM Patches 8 Flaws, Two Critical Unauthenticated

Do Son September 18, 2026 0

Synology fixed 8 DSM vulnerabilities, including two critical unauthenticated flaws (CVE-2026-13684, CVE-2026-13639) on DiskStation Manager. Update now.
Critical HCL BigFix Vulnerabilities Expose Admin Accounts Diagram of critical HCL BigFix vulnerabilities and database exploitation paths
  • Vulnerability Report

Critical HCL BigFix Vulnerabilities Expose Admin Accounts

Do Son September 18, 2026 0

HCL Software patched critical HCL BigFix vulnerabilities, including CVE-2026-67100 and CVE-2026-18963. Patch now to prevent total account takeovers.
4 Linux Kernel LPE Flaws Disclosed With Public PoC Exploits Four Linux kernel privilege escalation vulnerabilities disclosed with public proof-of-concept exploits granting local root
  • Vulnerability Report

4 Linux Kernel LPE Flaws Disclosed With Public PoC Exploits

Do Son September 18, 2026 0

Four Linux kernel privilege escalation flaws were disclosed with public PoC exploits granting local root. Details and patches are now out. Update now.
PAPERMILL Cybercrime Cluster Delivers VenomRAT via Tax Lures Rust supply chain attack on arrayref crate with proc-macro1 typosquat and DPRK infrastructure overlap
  • Cybercriminals

PAPERMILL Cybercrime Cluster Delivers VenomRAT via Tax Lures

Do Son September 18, 2026 0

Security researchers uncovered the new PAPERMILL cybercrime cluster. Learn how the PAPERMILL cybercrime cluster uses tax lures to deploy VenomRAT.
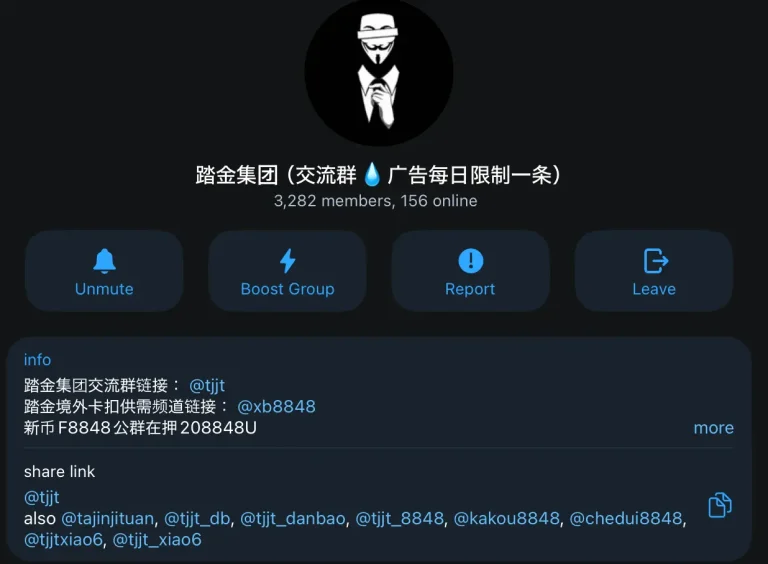
Tajin Group Phishing Network Linked to Guarantee Marketplaces Tajin Group phishing network and Tajin Group money laundering scheme
  • Cybercriminals

Tajin Group Phishing Network Linked to Guarantee Marketplaces

Do Son September 18, 2026 0

A new Tajin Group phishing network emerged on Telegram. Discover how Tajin Group money laundering fuels illicit guarantee marketplaces across the globe.
Critical Google Chrome Vulnerabilities Fixed in Update Diagram showing critical Google Chrome vulnerabilities and patch for Google Chrome vulnerabilities
  • Vulnerability Report

Critical Google Chrome Vulnerabilities Fixed in Update

Do Son September 18, 2026 0

Google patched critical Google Chrome vulnerabilities. Update now to address multiple Google Chrome vulnerabilities like CVE-2026-93374 and stay secure.
Critical Dokploy OS Command Injection Exposes Servers Diagram of the Dokploy OS command injection and CVE-2026-72878 execution path
  • Vulnerability Report

Critical Dokploy OS Command Injection Exposes Servers

Do Son September 18, 2026 0

A critical Dokploy OS command injection flaw exposes servers to root takeover via backups. Patch this Dokploy OS command injection now.
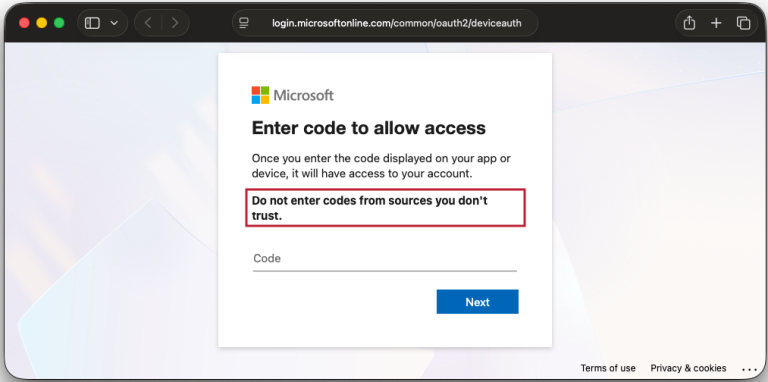
GhostCode Phishing Kit Targets Enterprise Microsoft Accounts Redirect to legitimate device code sign-in page
  • Cybercriminals

GhostCode Phishing Kit Targets Enterprise Microsoft Accounts

Do Son September 18, 2026 0

Security researchers uncovered a new GhostCode phishing kit. Learn how the GhostCode phishing kit bypasses MFA to hijack enterprise Microsoft 365 accounts.
CVE-2026-86863 (CVSS 9.8): pgAdmin 4 Authentication Bypass Flaw Diagram showing the critical pgAdmin 4 authentication bypass vulnerability
  • Vulnerability Report

CVE-2026-86863 (CVSS 9.8): pgAdmin 4 Authentication Bypass Flaw

Do Son September 18, 2026 0

A critical pgAdmin 4 authentication bypass (CVE-2026-86863) allows remote admin takeover. Patch this pgAdmin 4 authentication bypass vulnerability now.
WordPress 7.1.1 Fixes 11 Security Flaws, Update Now WordPress 7.1.1 security release patching 11 vulnerabilities including stored cross-site scripting and path traversal flaws
  • Vulnerability Report

WordPress 7.1.1 Fixes 11 Security Flaws, Update Now

Do Son September 18, 2026 0

The WordPress 7.1.1 security release fixes 11 flaws, including stored cross-site scripting and path traversal. Update your sites immediately.
HP Fixes Critical HPLIP Vulnerabilities Diagram showing critical HPLIP vulnerabilities and HPLIP vulnerabilities patch
  • Vulnerability Report

HP Fixes Critical HPLIP Vulnerabilities

Do Son September 17, 2026 0

HP patched critical HPLIP vulnerabilities. Update your print drivers to fix HPLIP vulnerabilities and prevent remote code execution.
Critical HP Advance Vulnerabilities Enable RCE (CVE-2026-89082) Diagram illustrating the critical HP Advance vulnerabilities and remote code execution paths
  • Vulnerability Report

Critical HP Advance Vulnerabilities Enable RCE (CVE-2026-89082)

Do Son September 17, 2026 0

HP released updates to fix critical HP Advance vulnerabilities (CVE-2026-89082). Patch these HP Advance vulnerabilities to stop remote code execution.
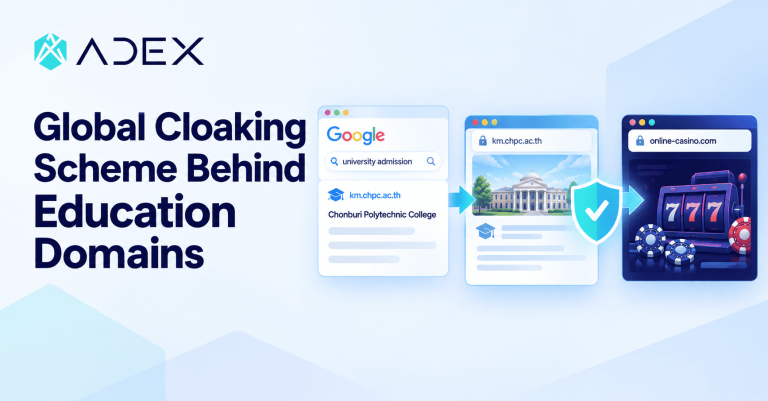
ADEX Uncovers Global Cloaking Scheme Behind Education Domains ADEX Uncovers Global Cloaking Scheme Behind Education Domains, cover
  • Technique

ADEX Uncovers Global Cloaking Scheme Behind Education Domains

Do Son September 17, 2026 0
A hacked education website was used to route users to an online casino, the latest case in...
Read More Read more about ADEX Uncovers Global Cloaking Scheme Behind Education Domains
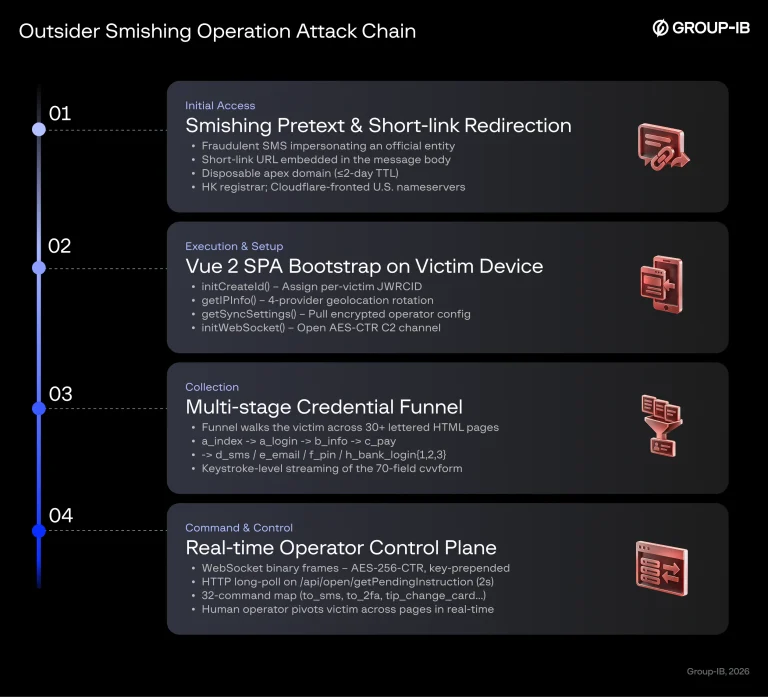
Smishing Triad Phishing Kit Exposed by Group-IB The new Smishing Triad phishing kit architecture and Smishing Triad phishing kit attack diagram
  • Cybercriminals

Smishing Triad Phishing Kit Exposed by Group-IB

Do Son September 17, 2026 0

Group-IB exposed a new Smishing Triad phishing kit used by Outsider. Learn how this Smishing Triad phishing kit steals financial data worldwide.
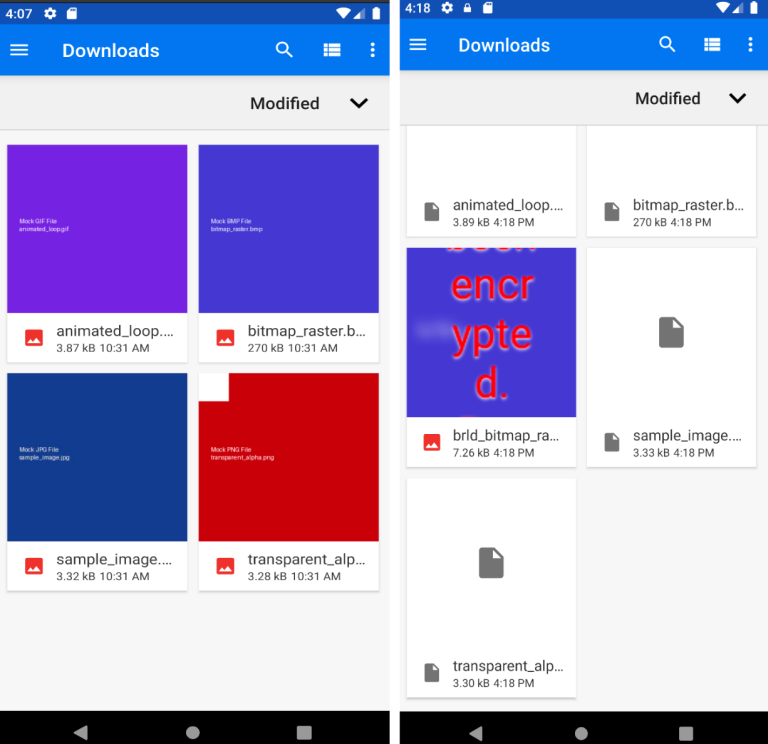
Mantax Otax Android Malware: Spyware Meets Ransomware Mantax Otax Android malware infection screen
  • Malware

Mantax Otax Android Malware: Spyware Meets Ransomware

Do Son September 17, 2026 0

Zimperium zLabs discovered Mantax Otax Android malware, a fierce Indonesian mobile ransomware integrating spyware to hijack, record, and extort victims.
North Korean IT Worker Scam Infiltrates Tech Jobs GoSerpent backdoor cyber espionage attack chain against Southeast Asian government networks
  • Cybercriminals

North Korean IT Worker Scam Infiltrates Tech Jobs

Do Son September 17, 2026 0

Silent Push uncovered a North Korean IT worker scam recruiting proxies. Learn how a North Korean IT worker uses Discord to bypass corporate hiring filters.
Google Home Adds MCP Support for AI Agent Control Google Home MCP support letting AI agents like Claude control Nest and Matter smart home devices
  • Technology

Google Home Adds MCP Support for AI Agent Control

Do Son September 17, 2026 0

Google Home MCP support lets AI agents like Claude control Nest and Matter devices via natural language, gated to the $20/mo Premium Advanced tier.
Apache NiFi Vulnerabilities Expose Data Pipelines to Attacks Diagram of Apache NiFi vulnerabilities and path manipulation vectors
  • Vulnerability Report

Apache NiFi Vulnerabilities Expose Data Pipelines to Attacks

Do Son September 17, 2026 0

Learn about recent Apache NiFi vulnerabilities (CVE-2026-87976, CVE-2026-70469) and Apache MyFaces flaws. Apply Apache security updates to prevent DoS attacks.
Unbound DNS Vulnerabilities Expose Resolvers to RCE Diagram illustrating critical Unbound DNS vulnerabilities and DNSSEC heap corruption
  • Vulnerability Report

Unbound DNS Vulnerabilities Expose Resolvers to RCE

Do Son September 17, 2026 0

NLnet Labs patched critical Unbound DNS vulnerabilities. Upgrade now to fix Unbound DNS vulnerabilities and block remote code execution attacks.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121379CVSS 9.6
    The Tournamatch WordPress plugin before 4.7.1 does not validate or restrict the path of a previously stored profile...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121491CVSS 9.0
    The Fiber Admin WordPress plugin before 4.0.1 does not validate or escape a request header before writing it...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119516CVSS 9.8
    Deserialization of Untrusted Data vulnerability in Mamunur Rashid Radius Booking — Booking Calendar for Appointments & Services radius-booking...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2026-124059CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this vulnerability is the function setWiFiWdsAddConfig...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.