Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Google Play Protect: Safeguarding Billions of Users in 2024 Google Play Protect
  • Android
  • Technology

Google Play Protect: Safeguarding Billions of Users in 2024

Do Son January 30, 2025 0

Explore the strong security measures implemented by Google to protect the Android ecosystem. Discover how Google Play Protect uses AI to block malicious apps.

Zero-Day Alert: Mirai Botnet Exploiting Unpatched Zyxel CPE Vulnerability (CVE-2024-40891) Weaver E-cology RCE CVE-2026-22679 CVE-2026-20127 Cisco SD-WAN Exploitation AI-Driven Cyberattack ARXON Malware React Server Components Vulnerability CVE-2025-55182 FortiWeb Auth Bypass, Unauthenticated Admin Takeover RayInitiator Bootkit, LINE VIPER CVE-2025-59689 Department of the Treasury cybersecurity - CVE-2025-0108 PoC CVE-2025-31103 Dior Data Breach SK Telecom data breach, long-term intrusion
  • Vulnerability

Zero-Day Alert: Mirai Botnet Exploiting Unpatched Zyxel CPE Vulnerability (CVE-2024-40891)

Do Son January 30, 2025 0

Critical zero-day vulnerability on Zyxel CPE devices (CVE-2024-40891): Unauthenticated remote attackers can execute arbitrary commands. Stay protected!

CVE-2024-23953 and CVE-2024-29869: Apache Hive Patches Two Important Security Flaws CVE-2024-23953 and CVE-2024-29869
  • Vulnerability

CVE-2024-23953 and CVE-2024-29869: Apache Hive Patches Two Important Security Flaws

Do Son January 30, 2025 0

Protect your data lake systems from potential security threats. Understand the impact of CVE-2024-23953 and CVE-2024-29869 on Apache Hive and take necessary precautions.

Phorpiex Botnet Now Deploying LockBit Ransomware in Automated Attacks Phorpiex botnet Attack
  • Malware

Phorpiex Botnet Now Deploying LockBit Ransomware in Automated Attacks

Do Son January 30, 2025 0

Uncover the unique attack method involving the Phorpiex botnet and LockBit Black Ransomware. Find out how automation is changing the landscape of ransomware deployment.

ISC Patches Two Vulnerabilities – CVE-2024-11187 and CVE-2024-12705 Kea DHCPv4 DoS, Hostname Validation CVE-2024-11187 and CVE-2024-12705
  • Vulnerability

ISC Patches Two Vulnerabilities – CVE-2024-11187 and CVE-2024-12705

Do Son January 30, 2025 0

Critical vulnerabilities in BIND DNS software: CVE-2024-11187 and CVE-2024-12705. Understand the risks of denial-of-service attacks on DNS servers and resolvers.

Phishing Alert: Cybercriminals Deploy SapphireRAT via Legal Notices SapphireRAT
  • Malware

Phishing Alert: Cybercriminals Deploy SapphireRAT via Legal Notices

Do Son January 30, 2025 0

Protect your organization from the SapphireRAT phishing attack. Discover how cybercriminals are evading traditional security measures with fake legal notices.

VMware Aria Operations Flaws Expose Credentials, Enable Privilege Escalation CVE-2025-22217 - CVE-2025-22218 Broadcom, VMware Licensing
  • Vulnerability

VMware Aria Operations Flaws Expose Credentials, Enable Privilege Escalation

Do Son January 30, 2025 0

Learn about the security risks in VMware Aria Operations and Logs. Discover the potential consequences and how to mitigate the threats.

Europol Smashing Cybercrime Hubs: Cracked & Nulled Taken Down Nulled Taken Down
  • Cyber Security

Europol Smashing Cybercrime Hubs: Cracked & Nulled Taken Down

Do Son January 30, 2025 0

Discover how Europol took down two major cybercrime forums: Cracked and Nulled. Learn about the impact on illegal goods and services.

China-Nexus Espionage: ScatterBrain Obfuscation Tactics Revealed ScatterBrain - POISONPLUG.SHADOW
  • Malware

China-Nexus Espionage: ScatterBrain Obfuscation Tactics Revealed

Do Son January 30, 2025 0

Discover ScatterBrain, a powerful obfuscating compiler employed by APT41. Understand its role in protecting the advanced modular backdoor POISONPLUG.SHADOW.

FAQs About Game Server Hosting and Security Answered network-2402637_1280
  • Technique

FAQs About Game Server Hosting and Security Answered

Do Son January 30, 2025 0
When it comes to game server hosting, many players and game administrators face questions about performance, security,...
Read More Read more about FAQs About Game Server Hosting and Security Answered
Aquabotv3: The Mirai-Based Botnet Exploiting CVE-2024-41710 for DDoS Attacks CVE-2025-23093 & CVE-2025-23094
  • Malware
  • Vulnerability

Aquabotv3: The Mirai-Based Botnet Exploiting CVE-2024-41710 for DDoS Attacks

Do Son January 30, 2025 0

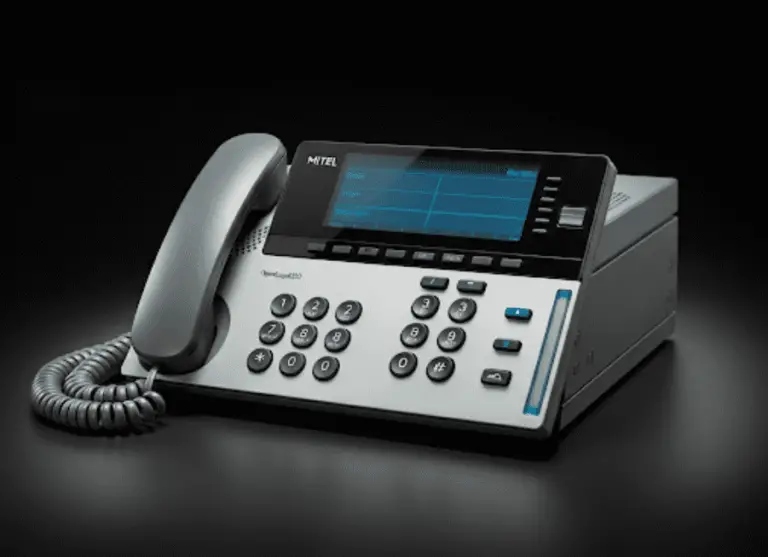
Mitel SIP phones under active exploitation by Aquabotv3, a new variant of the Mirai-based botnet. Learn about the undisclosed vulnerability CVE-2024-41710.

DeepSeek’s Exposed Database Leaks Sensitive User Information DeepSeek database Leak
  • Data Leak

DeepSeek’s Exposed Database Leaks Sensitive User Information

Do Son January 30, 2025 0

Learn about the major security lapse in DeepSeek, a Chinese AI startup, and the exposure of sensitive user information and internal data.

DeepSeek R1: China’s Advanced AI Model Raises Security Concerns DeepSeek R1 Vulnerability
  • Vulnerability

DeepSeek R1: China’s Advanced AI Model Raises Security Concerns

Do Son January 30, 2025 0

Discover the security vulnerabilities in DeepSeek R1, a new AI model developed in China. Learn about its potential for misuse and implications for cybersecurity.

Microsoft Edge Takes on Scareware Scams with New AI-Powered Blocker Scareware blocker
  • Technology

Microsoft Edge Takes on Scareware Scams with New AI-Powered Blocker

Do Son January 29, 2025 0

Protect yourself from scareware scams with Microsoft's new Edge feature. Help refine the capabilities of the Scareware Blocker and stay safe online.

CVE-2024-56614 & CVE-2024-56615: PoC Exploits Released for Severe eBPF Vulnerabilities in Linux Kernel CVE-2024-56614 and CVE-2024-56615
  • Linux
  • Vulnerability

CVE-2024-56614 & CVE-2024-56615: PoC Exploits Released for Severe eBPF Vulnerabilities in Linux Kernel

Do Son January 29, 2025 0

Uncover the latest Linux kernel vulnerabilities affecting eBPF framework with AF_XDP sockets. Learn about CVE-2024-56614 and CVE-2024-56615 and their potential security risks.

New Cyber-Espionage Campaign Hits Europe: UAC-0063 Threat Actor Expands Operations UAC-0063 Threat Actor
  • Cyber Security

New Cyber-Espionage Campaign Hits Europe: UAC-0063 Threat Actor Expands Operations

Do Son January 29, 2025 0

Stay informed about the latest cyber-espionage threat actor, UAC-0063. Learn about their activities in Central Asia and Europe and the cybersecurity concerns they raise.

Unpacking the Latest Obfuscation Techniques in Xloader Versions 6 and 7 Xloader Versions 6 & 7
  • Malware

Unpacking the Latest Obfuscation Techniques in Xloader Versions 6 and 7

Do Son January 29, 2025 0

Xloader is known for its ability to steal sensitive information from web browsers, email clients, and FTP applications

CVE-2024-12647 (CVSS 9.8): Canon Printers at Risk of Remote Code Execution CVE-2024-12647, CVE-2024-12648, and CVE-2024-12649
  • Vulnerability

CVE-2024-12647 (CVSS 9.8): Canon Printers at Risk of Remote Code Execution

Do Son January 29, 2025 0

Find out about the high-severity vulnerabilities CVE-2024-12647, CVE-2024-12648, and CVE-2024-12649 in Canon Laser Printers and Small Office Multifunction Printers. Take action to secure your devices.

TorNet: A New Backdoor That Uses TOR to Anonymize C2 Communication NATS-as-C2 Sysdig CVE-2026-33017 Langflow RCE Microsoft Phone Link Hijack CloudZ Pheno Plugin Insider Threat BlackCat (ALPHV) OFAC Sanctions DPRK IT Workers Transparent Tribe APT36 React2Shell, EtherRAT SideWinder Espionage, Netlify Phishing DDNS Abuse, C2 Infrastructure Hacking Health Club
  • Malware

TorNet: A New Backdoor That Uses TOR to Anonymize C2 Communication

Do Son January 29, 2025 0

Among the malware deployed in this campaign is a previously undocumented backdoor called TorNet, which is being distributed via PureCrypter malware

DeepSeek Disrupts AI Landscape: High Performance at Low Cost DeepSeek r1
  • Technology

DeepSeek Disrupts AI Landscape: High Performance at Low Cost

Do Son January 29, 2025 0

Explore the game-changing DeepSeek app by Chinese AI startup. See how it delivers superior performance to industry rivals at a fraction of the cost.

From Victim Profiles to Data Leaks: Inside the Lynx Ransomware-as-a-Service Ecosystem Lynx Ransomware-as-a-Service
  • Malware

From Victim Profiles to Data Leaks: Inside the Lynx Ransomware-as-a-Service Ecosystem

Do Son January 29, 2025 0

Discover the sophisticated operations of Lynx Ransomware-as-a-Service (RaaS) and its impact on businesses worldwide. Dive into the report by Group-IB.

ABB Advisory Warns of CVE-2024-48841: RCE Threat with CVSS 10.0 Severity ABB T-MAC Plus vulnerabilities terminal system flaws ABB OPTIMAX Vulnerability CVE-2025-14510 ABB Edgenius Auth Bypass, Critical RCE ABB, ASPECT BMS CVE-2024-48841, CVE-2024-48849, and CVE-2024-48852 CVE-2024-48510
  • Vulnerability

ABB Advisory Warns of CVE-2024-48841: RCE Threat with CVSS 10.0 Severity

Do Son January 29, 2025 0

Discover the cybersecurity advisory addressing critical vulnerabilities in ABB FLXeon controllers, including CVE-2024-48841 for remote code execution.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-119446CVSS 9.4
    Session Fixation vulnerability in the CLI login flow in nerves-hub nerves_hub_web allows an unauthenticated attacker to obtain an...
    📅 Updated: Nov 10, 2026
  • CVE-2026-61949CVSS 9.3
    Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in Bookly Bookly bookly-responsive-appointment-booking-tool allows...
    📅 Updated: Nov 10, 2026
  • CVE-2026-13312CVSS 9.9
    A vulnerability that could allow an attacker to compromise a system.
    📅 Updated: Nov 10, 2026
  • CVE-2026-72868CVSS 9.9
    Dokploy is a free, self-hostable Platform as a Service (PaaS). Prior to 0.29.13, apps/dokploy/server/api/routers/destination.ts interpolates the accessKey, secretAccessKey,...
    📅 Updated: Nov 10, 2026
  • CVE-2026-6715CVSS 9.8
    IBM Concert 1.0 through 3.0.1.1 allows an attacker can supply crafted input that is incorporated into an operating...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17403CVSS 9.0
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to gain full...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17402CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.