Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
CVE-2024-53691: PoC Exploit Released for Severe QNAP RCE Flaw CVE-2024-53691 PoC exploit
  • Vulnerability

CVE-2024-53691: PoC Exploit Released for Severe QNAP RCE Flaw

Do Son January 16, 2025 0

Security researcher c411e published a PoC exploit code for a severe vulnerability in QNAP NAS devices, identified as CVE-2024-53691

Yubico Addresses Authentication Bypass Vulnerability CVE-2025-23013 in pam-u2f Package CVE-2025-23013
  • Vulnerability

Yubico Addresses Authentication Bypass Vulnerability CVE-2025-23013 in pam-u2f Package

Do Son January 16, 2025 0

Stay informed about the latest security advisory from Yubico regarding an authentication bypass vulnerability, CVE-2025-23013.

The Rise of AI Search: Google Search Market Share Dips Below 90% Google Arkansas Investment, AI Data Center Google, privacy fine Ecosia Google Chrome Alphabet Earnings, AI Growth Google Hydropower, AI Data Centers Google Breakup Antitrust Workspace Flows Google Workspace Google remote work, return to office
  • Technology

The Rise of AI Search: Google Search Market Share Dips Below 90%

Do Son January 16, 2025 0

Discover the latest statistics on Google Search market share. Find out how its global market share has fallen below 90% for the first time since 2015.

Microsoft 365 Drops Windows 10: What You Need to Know Before the Deadline Microsoft 365 Windows 10
  • Technology
  • Windows

Microsoft 365 Drops Windows 10: What You Need to Know Before the Deadline

Do Son January 16, 2025 0

Important announcement from Microsoft: The support for Microsoft 365 applications on Windows 10 will end in 2025. Upgrade to Windows 11 for continued access.

HPE Aruba Networking Addresses Security Vulnerabilities in AOS Systems CVE-2024-26305 _ CVE-2025-23058 Aruba 5G Core Open Redirect
  • Vulnerability

HPE Aruba Networking Addresses Security Vulnerabilities in AOS Systems

Do Son January 16, 2025 0

Discover the security risks posed by vulnerabilities in HPE Aruba Networking's AOS systems and ways to mitigate them.

AWS Patches Vulnerabilities in WorkSpaces, AppStream 2.0, and DCV Clients WorkSpaces Token Leak, Local Privilege Escalation CVE-2025-0500 & CVE-2025-0501
  • Vulnerability

AWS Patches Vulnerabilities in WorkSpaces, AppStream 2.0, and DCV Clients

Do Son January 16, 2025 0

Stay secure with Amazon WorkSpaces, AppStream, and DCV. Learn about two vulnerabilities (CVE-2025-0500 and CVE-2025-0501) and how to protect your remote sessions.

CVE-2024-52281: Rancher Vulnerability Exposes Users to Stored XSS Attacks CVE-2024-52281 Rancher CLI Vulnerability CVE-2025-67601
  • Vulnerability

CVE-2024-52281: Rancher Vulnerability Exposes Users to Stored XSS Attacks

Do Son January 16, 2025 0

Stay informed about the severe vulnerability in Rancher (CVE-2024-52281) that puts Kubernetes deployments at risk. Learn how to protect your production environments.

Is Google Too Big? CMA Investigates Search Giant Competition and Markets Authority Google
  • Technology

Is Google Too Big? CMA Investigates Search Giant

Do Son January 16, 2025 0

Explore the UK's Competition and Markets Authority (CMA) investigation into Google's search and advertising practices under the Digital Markets, Competition, and Consumers Act (DMCC).

NVIDIA Releases Security Update for Container Toolkit and GPU Operator NVIDIA acquisition rumors NVIDIA AI Security AI Framework Vulnerabilities Nvidia 595.76 Hotfix NVIDIA Megatron Bridge vulnerability GPU vs ASIC AI battle NVIDIA Driver Vulnerability CVE-2025-33217 NVIDIA biggest TSMC customer 2026, NVIDIA vs Apple TSMC revenue share NVIDIA CUDA Toolkit CVE-2025-33228 Groq NVIDIA licensing deal, Jonathan Ross acquihire 2025 NeMo Code Injection, AI Framework RCE NVIDIA App Privilege Escalation, CVE-2025-23358 NVIDIA Security Update, DLS Vulnerability CVE-2025-23316 NVIDIA NVDebug, vulnerabilities NVIDIA Driver Vulnerabilities, vGPU Security Nvidia Jetson, UEFI Vulnerabilities CVE-2024-0130 - CVE-2024-0136 CVE-2024-0148 NVIDIA Driver Support, Windows 10 EOL
  • Vulnerability

NVIDIA Releases Security Update for Container Toolkit and GPU Operator

Do Son January 16, 2025 0

NVIDIA releases security update for Container Toolkit and GPU Operator software, addressing multiple vulnerabilities including CVE-2024-0136.

North Korean Hackers Linked to Crowdfunding Scam Kali365 phishing platform EmEditor Supply Chain Attack, WALSHAM INVESTMENTS LIMITED EggStreme, fileless malware North Korea Cybercrime, Remote IT Job Fraud RedDelta APT
  • Cyber Security

North Korean Hackers Linked to Crowdfunding Scam

Do Son January 16, 2025 0

Uncover the link between North Korean IT worker schemes and a 2016 crowdfunding scam. Learn about the activities of the NICKEL TAPESTRY threat group.

CVE-2024-9636: Popular WordPress Plugin ComboBlocks Exposes Thousands of Sites to Complete Takeover CVE-2024-9636
  • Vulnerability

CVE-2024-9636: Popular WordPress Plugin ComboBlocks Exposes Thousands of Sites to Complete Takeover

Do Son January 16, 2025 0

Protect your WordPress website from a critical vulnerability (CVE-2024-9636). Learn how to secure your site and prevent complete takeover.

TikTok’s Last Dance: Inside the U.S. Ban TikTok USDS Joint Venture LLC divestiture, Project Texas 2.0 ByteDance stake TikTokRefugee TikTok Ban, US Extension
  • Technology

TikTok’s Last Dance: Inside the U.S. Ban

Do Son January 16, 2025 0

Stay up to date on the latest developments regarding TikTok in the United States. Learn about the potential shutdown and how it may impact users.

Cybercriminals Exploit Fake Google Ads to Ransack Advertiser Accounts Google Ads Scam
  • Cyber Security

Cybercriminals Exploit Fake Google Ads to Ransack Advertiser Accounts

Do Son January 16, 2025 0

Beware of the Google Ads Scam targeting advertisers! Learn how cybercriminals use fraudulent ads to compromise accounts and perpetuate further scams.
Enhance Your Privacy with Rented USA Temp Numbers for SMS Img_2025_09_11_23_12_43
  • Technique

Enhance Your Privacy with Rented USA Temp Numbers for SMS

Do Son January 16, 2025
In the digital age, maintaining privacy is more important than ever. Whether you’re signing up for online...
Read More Read more about Enhance Your Privacy with Rented USA Temp Numbers for SMS
PoC Exploit Released for Ivanti Connect Secure Flaw CVE-2025-0282 Used in Attacks Salt Typhoon Teleco Hack, Cisco Academy Link CVE-2025-0282 PoC exploit
  • Vulnerability

PoC Exploit Released for Ivanti Connect Secure Flaw CVE-2025-0282 Used in Attacks

Do Son January 16, 2025 0

watchTowr Labs published a detailed analysis of the vulnerability and a proof-of-concept (PoC) exploit for CVE-2025-0282

Modern approaches to vulnerability management: MODUS X expertise in protecting businesses and critical infrastructure WD Discovery Vulnerability CVE-2025-30248 binary-parser Vulnerability CVE-2026-1245 H3C RCE Vulnerability CVE-2025-60262 Telenium RCE, CVE-2025-10659 Fuel station security, ICS vulnerabilities FreePBX vulnerability CVE-2024-9478 & CVE-2024-9479 SysTrack Vulnerability, Privilege Escalation
  • Technique

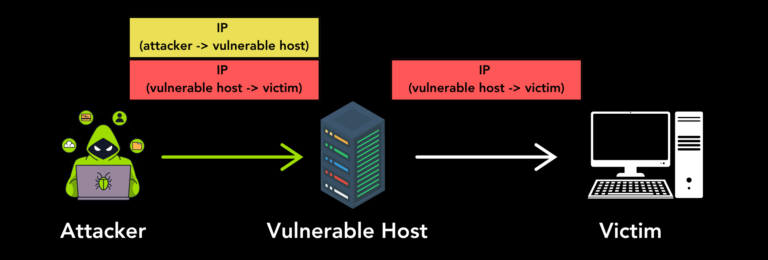
Modern approaches to vulnerability management: MODUS X expertise in protecting businesses and critical infrastructure

Do Son January 16, 2025 0
Currently, cyber ​​threats are one of the key challenges businesses and critical infrastructure face. Technological development is...
Read More Read more about Modern approaches to vulnerability management: MODUS X expertise in protecting businesses and critical infrastructure
New Tunneling Protocol Vulnerabilities Expose 4.2 Million Hosts to Cyberattacks Tunneling Protocol Vulnerability
  • Vulnerability

New Tunneling Protocol Vulnerabilities Expose 4.2 Million Hosts to Cyberattacks

Do Son January 16, 2025 0

Learn about critical vulnerabilities in tunneling protocols that could expose millions of systems to anonymous attacks and unauthorized access.

15,000 FortiGate Firewalls Exposed: Massive Leak Includes VPN Credentials LY Corporation Data Breach
  • Data Leak

15,000 FortiGate Firewalls Exposed: Massive Leak Includes VPN Credentials

Do Son January 15, 2025 0

Discover the shocking FortiGate leak exposing over 15,000 firewall configurations and VPN credentials. Learn more about the vulnerability and its impact on cybersecurity.

Microsoft Patches Outlook Zero-Click: CVE-2025-21298 Exploits RCE via Emails Smart App Control blocking Armoury Crate, ROG Ally Defender false positive 2026 Microsoft Zero-Day, Cloud Files UAF Microsoft Access end of life CVE-2025-21298 Azure Vulnerabilities
  • Vulnerability

Microsoft Patches Outlook Zero-Click: CVE-2025-21298 Exploits RCE via Emails

Do Son January 15, 2025 0

Stay informed about the latest critical vulnerability (CVE-2025-21298) in Microsoft Outlook. Learn about the high-risk nature and implications for email security.

ECOVACS Patches Critical WiFi RCE Vulnerability CVE-2024-42911 in Deebot Robot Vacuums CVE-2024-42911
  • Vulnerability

ECOVACS Patches Critical WiFi RCE Vulnerability CVE-2024-42911 in Deebot Robot Vacuums

Do Son January 15, 2025 0

Learn about the critical vulnerability CVE-2024-42911 affecting ECOVACS Deebot robot vacuums and the security measures taken to address it.
Critical Vulnerability in Rasa Framework Enables Remote Code Execution (CVE-2024-49375) CVE-2024-49375
  • Vulnerability

Critical Vulnerability in Rasa Framework Enables Remote Code Execution (CVE-2024-49375)

Do Son January 15, 2025 0

Stay informed about the critical-severity vulnerability (CVE-2024-49375) in the Rasa framework. Learn how attackers can achieve remote code execution and the impact on machine learning deployments.
Why MFA is Critical for Securing Cloud-Native SaaS in Enterprise Environments Privacy
  • Technique

Why MFA is Critical for Securing Cloud-Native SaaS in Enterprise Environments

Do Son January 15, 2025 0
As businesses depend more on cloud services and SaaS, they encounter new and changing security risks. According...
Read More Read more about Why MFA is Critical for Securing Cloud-Native SaaS in Enterprise Environments
❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-119446CVSS 9.4
    Session Fixation vulnerability in the CLI login flow in nerves-hub nerves_hub_web allows an unauthenticated attacker to obtain an...
    📅 Updated: Nov 10, 2026
  • CVE-2026-61949CVSS 9.3
    Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in Bookly Bookly bookly-responsive-appointment-booking-tool allows...
    📅 Updated: Nov 10, 2026
  • CVE-2026-13312CVSS 9.9
    A vulnerability that could allow an attacker to compromise a system.
    📅 Updated: Nov 10, 2026
  • CVE-2026-72868CVSS 9.9
    Dokploy is a free, self-hostable Platform as a Service (PaaS). Prior to 0.29.13, apps/dokploy/server/api/routers/destination.ts interpolates the accessKey, secretAccessKey,...
    📅 Updated: Nov 10, 2026
  • CVE-2026-6715CVSS 9.8
    IBM Concert 1.0 through 3.0.1.1 allows an attacker can supply crafted input that is incorporated into an operating...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17403CVSS 9.0
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to gain full...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17402CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.