Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
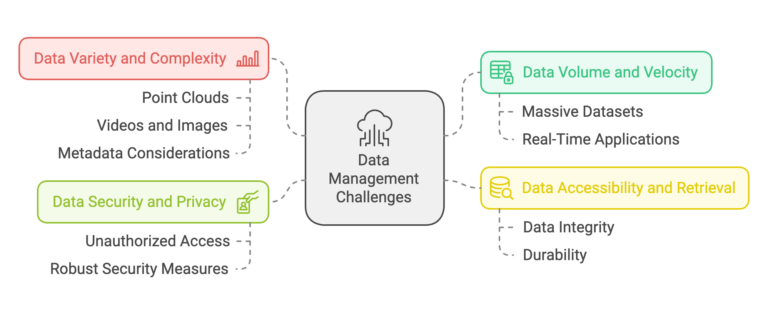
How to Store Computer Vision Data Effectively data-vision
  • Technique

How to Store Computer Vision Data Effectively

Do Son January 14, 2025 0
When computer vision algorithms like Convolutional Neural Networks (CNNs), Autoencoders, and Feature Detection and Matching are used...
Read More Read more about How to Store Computer Vision Data Effectively
Biden’s AI Chip Export Restrictions: A Strategic Move to Counter Global Tech Threats Bad Likert Judge - Artificial Intelligence Diffusion
  • Technology

Biden’s AI Chip Export Restrictions: A Strategic Move to Counter Global Tech Threats

Do Son January 14, 2025 0

Understanding the new U.S. law on artificial intelligence diffusion and export restrictions, aimed at preventing rival nations from accessing advanced American technology.

Critical SAP Flaws Revealed: CVE-2025-0070 and CVE-2025-0066 with CVSS 9.9 Demand Immediate Action SAP Security Patches CVE-2026-27685 SAP Security Update CVE-2026-0488 CVE-2024-47578 - CVE-2025-0070 and CVE-2025-0066
  • Vulnerability

Critical SAP Flaws Revealed: CVE-2025-0070 and CVE-2025-0066 with CVSS 9.9 Demand Immediate Action

Do Son January 14, 2025 0

Stay informed about the latest SAP security vulnerabilities. Learn about critical vulnerabilities like CVE-2025-0070 and CVE-2025-0066 affecting SAP NetWeaver and ABAP platforms.

Linux Kernel Privilege Escalation Vulnerability (CVE-2024-27397) Exploited: PoC Released CrackArmor AppArmor Vulnerabilities Linux Kernel UAF, Privilege Escalation PoC CVE-2024-27397 PoC
  • Linux
  • Vulnerability

Linux Kernel Privilege Escalation Vulnerability (CVE-2024-27397) Exploited: PoC Released

Do Son January 13, 2025 0

Discover the in-depth analysis and PoC exploit code for CVE-2024-27397, a critical Linux kernel vulnerability that allows local privilege escalation.

Zyxel Urges Patch Application for Privilege Escalation Vulnerability (CVE-2024-12398) CVE-2022-43389 - CVE-2024-12398 Zyxel UPnP Vulnerability CVE-2025-13942
  • Vulnerability

Zyxel Urges Patch Application for Privilege Escalation Vulnerability (CVE-2024-12398)

Do Son January 13, 2025 0

Protect your Zyxel access points and routers from CVE-2024-12398. Learn about the vulnerability and apply the necessary patches to safeguard your systems.

CISA Warns of Active Exploitation of Critical Flaws in BeyondTrust and Qlik Sense GUARDIANWALL MailSuite Exploit CVE-2026-32661 FileZen Vulnerability CVE-2026-25108 Ivanti EPMM Vulnerability Dormant Backdoor Fortinet Authentication Bypass CVE-2026-24858 VMware vCenter Server Flaw CVE-2025-21590
  • Vulnerability

CISA Warns of Active Exploitation of Critical Flaws in BeyondTrust and Qlik Sense

Do Son January 13, 2025 0

Urgent warning: Critical security vulnerabilities CVE-2024-12686 pose significant risks. BeyondTrust and Qlik Sense Enterprise impacted.

Kernel Modules and Malicious Commands: Anatomy of the sysinitd Rootkit sysinitd rootkit
  • Linux
  • Malware

Kernel Modules and Malicious Commands: Anatomy of the sysinitd Rootkit

Do Son January 13, 2025 0

Learn about the sophisticated sysinitd rootkit and how it hijacks network traffic and executes malicious commands on compromised Linux systems.
Microsoft Unveils CVE-2024-44243: A macOS System Integrity Protection Bypass Through Kernel Extensions CVE-2024-44243
  • Vulnerability

Microsoft Unveils CVE-2024-44243: A macOS System Integrity Protection Bypass Through Kernel Extensions

Do Son January 13, 2025 0

Find out how the CVE-2024-44243 macOS vulnerability enables attackers to bypass SIP and install rootkits and persistent malware.

APT28’s New Espionage Campaign Uses Double-Tap Infection Chain BingX cyberattack FortiGate SSO Attacks Firewall Config Theft
  • Cyber Security
  • Malware

APT28’s New Espionage Campaign Uses Double-Tap Infection Chain

Do Son January 13, 2025 0

Discover the UAC-0063 cyber espionage campaign: Russia's strategic interest in Central Asia's geopolitical dynamics.

CVE-2024-56511: Critical Authentication Bypass Vulnerability in DataEase CVE-2024-56511
  • Vulnerability

CVE-2024-56511: Critical Authentication Bypass Vulnerability in DataEase

Do Son January 13, 2025 0

Stay informed about the critical vulnerability (CVE-2024-56511) in the DataEase BI tool. Learn how attackers can bypass authentication and gain unauthorized access to sensitive data.

CVE-2024-41787 (CVSS 9.8): Critical IBM DOORS Next Flaw Enables Remote Code Execution IBM CCA Vulnerability CVE-2025-13375 IBM Anthropic Partnership, AI Software Development watsonx Orchestrate, SQL injection CVE-2024-49803 - CVE-2024-41787 IBM Completes Acquisition HashiCorp
  • Vulnerability

CVE-2024-41787 (CVSS 9.8): Critical IBM DOORS Next Flaw Enables Remote Code Execution

Do Son January 13, 2025 0

Critical vulnerabilities: CVE-2024-41779 and CVE-2024-41787 pose significant risks to IBM's DOORS Next software. Urgent security bulletin.

Unauthenticated Attackers Can Exploit Junos Vulnerabilities (CVE-2025-21598 & CVE-2025-21599) Junos OS Evolved CVE-2026-21902 Juniper Security Director, Critical Vulnerability Junos OS vulnerabilities - CVE-2025-21598 & CVE-2025-21599
  • Vulnerability

Unauthenticated Attackers Can Exploit Junos Vulnerabilities (CVE-2025-21598 & CVE-2025-21599)

Do Son January 13, 2025 0

Discover the flaws (CVE-2025-21598 & CVE-2025-21599) affecting Juniper Networks' Junos OS and Junos OS Evolved systems and the importance of timely patch management.
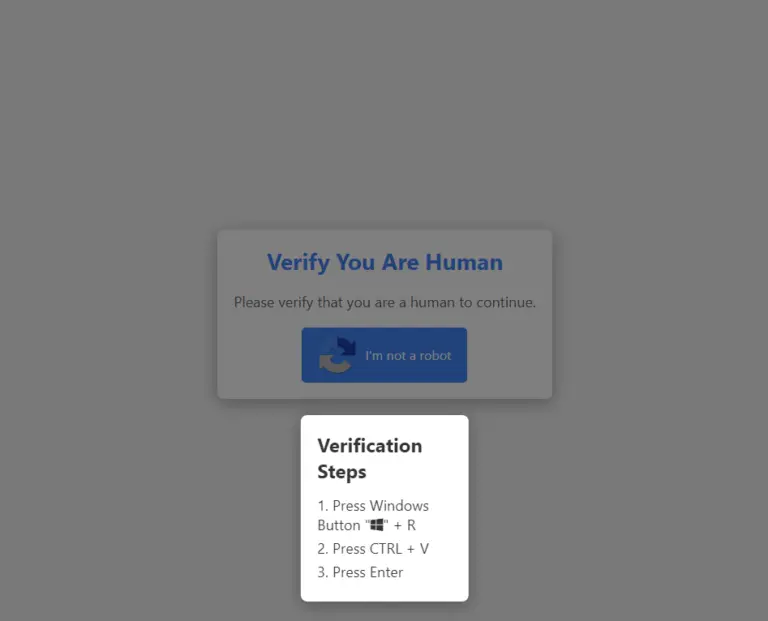
LummaC2 Infostealer Malware Spreads via Crack Programs and Phishing LummaC2 Infostealer
  • Malware

LummaC2 Infostealer Malware Spreads via Crack Programs and Phishing

Do Son January 13, 2025 0

Beware of the stealthy LummaC2 Infostealer malware. Learn how it tricks users with a fake CAPTCHA page and initiates a series of malicious steps.

Opportunities and Challenges of Leveraging AI in Software Development AI in Software Development
  • Technique

Opportunities and Challenges of Leveraging AI in Software Development

Do Son January 13, 2025 0

Let’s explore the key opportunities and challenges of using AI in software development to better understand its evolving impact.

New macOS Exploit Revealed: PoC for CVE-2024-54498 Breaks Sandbox Security CVE-2024-54498 PoC
  • Vulnerability

New macOS Exploit Revealed: PoC for CVE-2024-54498 Breaks Sandbox Security

Do Son January 12, 2025 0

Researcher has revealed a PoC exploit for CVE-2024-54498, a flaw that allows applications to escape the confines of the macOS Sandbox

0-Click Vulnerability in Samsung S24 Devices: PoC Releases for CVE-2024-49415 CVE-2024-49415
  • Vulnerability

0-Click Vulnerability in Samsung S24 Devices: PoC Releases for CVE-2024-49415

Do Son January 12, 2025 0

Critical vulnerability in Samsung S24 smartphone: CVE-2024-49415. Learn how remote attackers could execute arbitrary code and take control of the device.

Aviatrix Controller RCE CVE-2024-50603 Exploited in the Wild: Cryptojacking and Backdoors Deployed CRussian Market, "Fly" (Flyded) hange Healthcare Cyberattack - CVE-2024-50603 Exploit
  • Vulnerability

Aviatrix Controller RCE CVE-2024-50603 Exploited in the Wild: Cryptojacking and Backdoors Deployed

Do Son January 12, 2025 0

Exploitation of CVE-2024-50603 is already occurring in the wild. Wiz Research observed attackers deploying cryptocurrency miners (XMRig) and backdoors

Phishing Campaigns Exploit YouTube URLs and Microsoft 365 Themes to Steal Credentials Layoff Phishing Scam Remcos RAT Malware Aruba Phishing, Phishing-as-a-Service PyPI, phishing CVE-2024-25608 PyPI Phishing, Credential Theft
  • Cyber Security

Phishing Campaigns Exploit YouTube URLs and Microsoft 365 Themes to Steal Credentials

Do Son January 12, 2025 0

Protect yourself from YouTube phishing scams. Find out how cybercriminals trick users with legitimate-looking URLs and urgent-sounding subject lines.

HexaLocker V2: Ransomware Reborn with Advanced Tactics ransom
  • Malware

HexaLocker V2: Ransomware Reborn with Advanced Tactics

Do Son January 12, 2025 0

Unveiling the new HexaLocker V2: a more sophisticated and complex ransomware variant with advanced encryption and data theft features.

CVE-2025-22152 (CVSS 9.4): Severe Vulnerabilities Found in Atheos Web-Based IDE CVE-2025-22152
  • Vulnerability

CVE-2025-22152 (CVSS 9.4): Severe Vulnerabilities Found in Atheos Web-Based IDE

Do Son January 12, 2025 0

Learn about the critical vulnerability (CVE-2025-22152) in the Atheos IDE framework. Take action to secure your servers from unauthorized access and code execution.

ZACROS Corporation Discloses Personal Information Leak Following Ransomware Attack INC Ransom Pacific Cyber Threats OysterLoader Malware Rhysida Ransomware Black Basta Ransomware BYOVD Technique Velociraptor Abuse, Storm-2603 Ransomware Crypto24, Ransomware Ransomware Payments, UK Legislation ZACROS data breach
  • Cyber Security
  • Data Leak

ZACROS Corporation Discloses Personal Information Leak Following Ransomware Attack

Do Son January 12, 2025 0

ZACROS Corporation experiences data breach: personal information of over 157,000 individuals compromised.

RedDelta Leverages PlugX Backdoor in State-Sponsored Espionage Campaigns Kali365 phishing platform EmEditor Supply Chain Attack, WALSHAM INVESTMENTS LIMITED EggStreme, fileless malware North Korea Cybercrime, Remote IT Job Fraud RedDelta APT
  • Cyber Security
  • Malware

RedDelta Leverages PlugX Backdoor in State-Sponsored Espionage Campaigns

Do Son January 12, 2025 0

Uncover the details of RedDelta: A sophisticated cyber-espionage group targeting political and government entities in Asia.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-119446CVSS 9.4
    Session Fixation vulnerability in the CLI login flow in nerves-hub nerves_hub_web allows an unauthenticated attacker to obtain an...
    📅 Updated: Nov 10, 2026
  • CVE-2026-61949CVSS 9.3
    Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in Bookly Bookly bookly-responsive-appointment-booking-tool allows...
    📅 Updated: Nov 10, 2026
  • CVE-2026-13312CVSS 9.9
    A vulnerability that could allow an attacker to compromise a system.
    📅 Updated: Nov 10, 2026
  • CVE-2026-72868CVSS 9.9
    Dokploy is a free, self-hostable Platform as a Service (PaaS). Prior to 0.29.13, apps/dokploy/server/api/routers/destination.ts interpolates the accessKey, secretAccessKey,...
    📅 Updated: Nov 10, 2026
  • CVE-2026-6715CVSS 9.8
    IBM Concert 1.0 through 3.0.1.1 allows an attacker can supply crafted input that is incorporated into an operating...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17403CVSS 9.0
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to gain full...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17402CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.