Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
HiatusRAT Campaign Targets Web Cameras and DVRs: FBI Warns of Rising IoT Exploits BlueNoroff macOS Attack GhostCall Campaign Carding Underground Bulletproof Hosting DPRK Contagious Interview, npm Flood Stonefly group -HiatusRAT Actors
  • Cyber Security
  • Malware
  • Vulnerability

HiatusRAT Campaign Targets Web Cameras and DVRs: FBI Warns of Rising IoT Exploits

Do Son December 17, 2024 0

Stay informed about the latest threat to organizations worldwide: the HiatusRAT malware campaign targeting IoT devices.
Xloader Malware Delivered via Sophisticated SharePoint Attack Xloader malware - Formbook
  • Malware

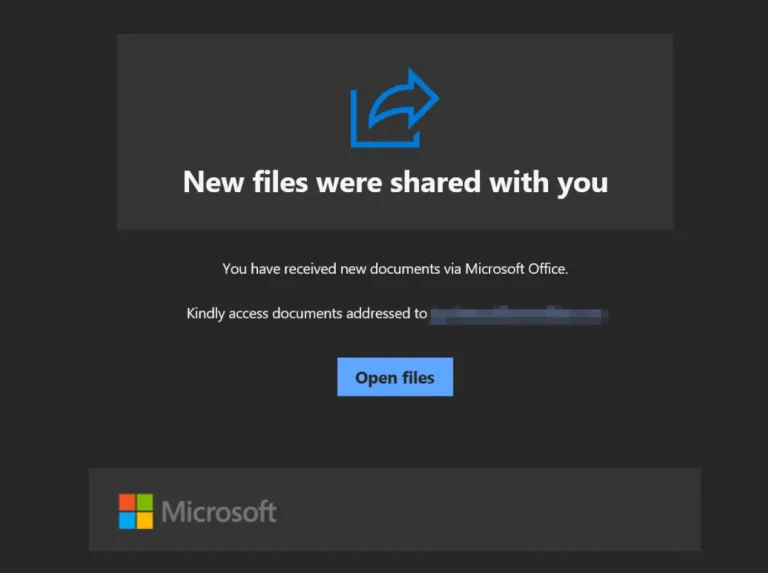
Xloader Malware Delivered via Sophisticated SharePoint Attack

Do Son December 17, 2024 0

Unveiling a new malicious SharePoint impersonation campaign delivering Xloader malware. Learn how this sophisticated attack takes advantage of brand impersonation and advanced process injection.

Spring Boot Actuator Misconfigurations: The Hidden Security Risks in Cloud Environments Spring Boot Actuator Misconfigurations
  • Vulnerability

Spring Boot Actuator Misconfigurations: The Hidden Security Risks in Cloud Environments

Do Son December 17, 2024 0

Learn how misconfigurations in Spring Boot Actuator can expose sensitive data and create opportunities for remote code execution in cloud environments.

CoinLurker Malware Targets Crypto Users via Fake Browser Updates Citrix NetScaler attack
  • Malware

CoinLurker Malware Targets Crypto Users via Fake Browser Updates

Do Son December 17, 2024 0

Beware of CoinLurker, a sophisticated data-stealing malware targeting cryptocurrency users and businesses through fake browser update campaigns.

Multiple Vulnerabilities in SHARP Routers Demand Urgent Firmware Updates CVE-2024-46873 and CVE-2024-45721
  • Vulnerability

Multiple Vulnerabilities in SHARP Routers Demand Urgent Firmware Updates

Do Son December 17, 2024 0

Critical vulnerabilities in SHARP routers pose significant risks for arbitrary command execution, data theft, and service disruptions.

Massive Ransomware Campaign Targets DrayTek Routers Osiris Ransomware Inc Ransomware Connection CountLoader Massive Ransomware Campaign CVE-2025-0289
  • Malware
  • Vulnerability

Massive Ransomware Campaign Targets DrayTek Routers

Do Son December 17, 2024 0

Explore the sophisticated ransomware campaign targeting DrayTek Vigor routers. Discover the tactics used by cybercriminals and steps to secure your devices.

From Taiwan to Korea: TIDRONE Threat Actor Targets ERP Software CLNTEND backdoor - threat actor
  • Cyber Security
  • Malware

From Taiwan to Korea: TIDRONE Threat Actor Targets ERP Software

Do Son December 17, 2024 0

Explore the TIDRONE threat actor and their cyberattacks on Korean companies. Find out how they exploit ERP software and deploy malware.
Russian State Actors Target UK Critical Infrastructure in New Cyber Campaign PHP RCE vulnerability
  • Cyber Security

Russian State Actors Target UK Critical Infrastructure in New Cyber Campaign

Do Son December 17, 2024 0

Alarming rise of cyber threats targeting the UK by Russian threat actors. Learn about the dangerous shift in geopolitical tensions and their impact on critical infrastructure.

DLL Side-Loading Strikes Again: Yokai Backdoor Bypasses Security exfiltrating AWS credentials - fabrice package
  • Cyber Security
  • Malware

DLL Side-Loading Strikes Again: Yokai Backdoor Bypasses Security

Do Son December 17, 2024 0

Discover the techniques used by Yokai Backdoor to bypass detection and exploit trusted executables. Stay informed about the latest cybersecurity threats.

Why Merchant Management Software is a Must-Have for Modern Banks and Payment Service Providers real_927d7428-06a7-415b-9e9c-4ad8c5f9f537
  • Technique

Why Merchant Management Software is a Must-Have for Modern Banks and Payment Service Providers

Do Son December 17, 2024 0
In today’s rapidly evolving financial ecosystem, banks and payment service providers (PSPs) face increasing demands for efficiency,...
Read More Read more about Why Merchant Management Software is a Must-Have for Modern Banks and Payment Service Providers
CVE-2024-49112 (CVSS 9.8): Critical Windows LDAP Flaw Puts Networks at Risk of Remote Takeover PlayReady Leak, DRM Certificates Windows Server 2022 update Hyper-V confidential VM fix CVE-2024-49112 Microsoft Authenticator, password manager
  • Vulnerability

CVE-2024-49112 (CVSS 9.8): Critical Windows LDAP Flaw Puts Networks at Risk of Remote Takeover

Do Son December 16, 2024 0

Microsoft discloses critical CVE-2024-49112 vulnerability in LDAP service. Learn about the severe risk it poses to enterprise networks and how to mitigate the threat.

Zero-Click HomeKit Exploit Used to Spy on Serbian Journalists HomeKit zero-click exploit
  • Malware
  • Vulnerability

Zero-Click HomeKit Exploit Used to Spy on Serbian Journalists

Do Son December 16, 2024 0

Learn about the alarming zero-click exploit in Apple's HomeKit feature used to compromise iPhones of Serbian journalists and activists.

Hackers exploit critical Apache Struts RCE flaw (CVE-2024-53677) after PoC exploit release CoinMarketCap Hack, Inferno Drainer CVE-2024-53677 PoC Exploit
  • Vulnerability

Hackers exploit critical Apache Struts RCE flaw (CVE-2024-53677) after PoC exploit release

Do Son December 16, 2024 0

Hackers are actively exploiting a recently fixed flaw CVE-2024-53677 in the Apache Struts after a PoC exploit was made public

CVE-2024-55661: RCE Vulnerability Discovered in Laravel Pulse Monitoring Tool Laravel Pulse - CVE-2024-55661
  • Vulnerability

CVE-2024-55661: RCE Vulnerability Discovered in Laravel Pulse Monitoring Tool

Do Son December 16, 2024 0

Attention Laravel developers: Learn about the CVE-2024-55661 security flaw in Laravel Pulse and how it can be exploited to execute arbitrary code.

Threat Actors Exploit Fake Brand Collaborations to Target YouTube Channels YouTube deepfake YouTube AI YouTube Premium YouTube Ad Blockers, Fake Buffering Google Lens, YouTube Shorts
  • Cyber Security

Threat Actors Exploit Fake Brand Collaborations to Target YouTube Channels

Do Son December 16, 2024 0

Protect your YouTube channel from phishing attacks posing as brand collaboration offers. Stay one step ahead of cybercriminals with these security tips.

Easy Money Online? FTC Warns of Exploding “Task Scam” Threat task scam report
  • Cyber Security

Easy Money Online? FTC Warns of Exploding “Task Scam” Threat

Do Son December 16, 2024 0

Beware of task scams: A new FTC report exposes the surge in online job scams promising easy earnings for completing simple tasks.

Critical Windows and Adobe ColdFusion Vulnerabilities Actively Exploited in the Wild, PoC Exploit Published Adobe ColdFusion Vulnerabilities
  • Vulnerability

Critical Windows and Adobe ColdFusion Vulnerabilities Actively Exploited in the Wild, PoC Exploit Published

Do Son December 16, 2024 0

Urgent warning: Critical Adobe ColdFusion and Windows vulnerabilities being actively exploited by malicious actors. Take action now to protect your system.
HeartCrypt: A Packer-as-a-Service Fueling Malware Campaigns Operation IconCat, UNG0801 AFP cyberattack -NetWalker Ransomware VShell RAT
  • Malware

HeartCrypt: A Packer-as-a-Service Fueling Malware Campaigns

Do Son December 16, 2024 0

Discover HeartCrypt, the powerful Packer-as-a-Service used by cybercriminals to protect malware from detection.

CVE-2024-55875 (CVSS 9.8): Critical XXE Vulnerability Found in http4k Toolkit CVE-2024-55875
  • Vulnerability

CVE-2024-55875 (CVSS 9.8): Critical XXE Vulnerability Found in http4k Toolkit

Do Son December 16, 2024 0

Understanding the CVE-2024-55875 vulnerability in the http4k toolkit: risks, impacts, and ways to mitigate this critical XXE Injection vulnerability.

SADBRIDGE Loader Unveils GOSAR Backdoor in Cyber Attacks XZ backdoor, Docker Hub MIFARE classic backdoor C++/CLI IIS Backdoor
  • Malware

SADBRIDGE Loader Unveils GOSAR Backdoor in Cyber Attacks

Do Son December 16, 2024 0

Discover GOSAR backdoor, a new Golang-based malware variant that rewrites the QUASAR RAT. Learn about its cross-platform capabilities and reduced detection rates

NodeLoader: A New Malware Family Exploits Node.js for Stealthy Attacks Screenshot 2024-12-15 150821
  • Malware

NodeLoader: A New Malware Family Exploits Node.js for Stealthy Attacks

Do Son December 16, 2024 0

Discover how NodeLoader malware uses Node.js applications for Windows to deliver second-stage payloads, including XMRig, Lumma, and Phemedrone Stealer.

Voice Phishing on Microsoft Teams Facilitates DarkGate Malware Attack voice phishing
  • Cyber Security
  • Malware

Voice Phishing on Microsoft Teams Facilitates DarkGate Malware Attack

Do Son December 16, 2024 0

Discover the new threat of voice phishing (vishing) via Microsoft Teams. Learn how cybercriminals are leveraging this tactic to distribute dangerous malware.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-91341CVSS 9.1
    Vulnerability in the Oracle Outside In Technology product of Oracle Fusion Middleware (component: Outside In Clean Content SDK)....
    📅 Updated: Nov 10, 2026
  • CVE-2026-63017CVSS 9.4
    Incorrect authorization in PowerSYSTEM Center allows a low-privileged, authenticated user to access resources normally limited to administrators.
    📅 Updated: Nov 10, 2026
  • CVE-2026-63774CVSS 9.4
    Insufficient input validation in the PowerSYSTEM Center report designer allows an authenticated user to execute unauthorized SQL commands.
    📅 Updated: Nov 10, 2026
  • CVE-2026-123025CVSS 9.4
    An OS Command Injection vulnerability was discovered in the Google Cloud DNS validation module of the OPNsense os-acme-client...
    📅 Updated: Nov 10, 2026
  • CVE-2026-123218CVSS 9.8
    IBM Aspera Faspex 5.0.0 through 5.0.19 could allow an authorized user to craft a specific message to bypass...
    CISA KEV📅 Added to KEV: Nov 9, 2026📅 Updated: Nov 10, 2026
  • CVE-2026-82509CVSS 9.1
    V programming language standard library net.http through version 0.5.2 prior to commit 4077484 contains a TLS certificate validation...
    📅 Updated: Nov 10, 2026
  • CVE-2026-8376CVSS 9.8
    Perl versions before 5.40.5-RC1, from 5.41.0 before 5.42.3-RC1, from 5.43.0 before 5.43.11 have a heap buffer overflow when...
    📅 Updated: Nov 10, 2026
  • CVE-2026-57433CVSS 9.8
    Storable versions before 3.41 for Perl have a signed integer overflow when deserializing a crafted SX_HOOK record. retrieve_hook_common...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.