
 Do Son
Stay ahead of SAP security vulnerabilities. Learn about the critical flaws disclosed in SAP's latest Security Patch Day, including CVE-2024-47578.

Critical vulnerability (CVE-2024-50623) in Cleo's software exposes organizations to threat actors. Learn about the implications for industries and the urgent need for patching.

Method Quick Overview Restart Your Router Gets you a new IP address from your ISP Use a...

OpenWrt discloses critical vulnerability CVE-2024-54143 that allows attackers to compromise firmware updates. Learn more about this security flaw.

Learn about the transition from OCSP to Certificate Revocation Lists (CRLs) by Let's Encrypt. Enhance privacy and operational efficiency in the world of internet security.

Stay informed about the recent dismantling of a phone phishing operation by Belgian and Dutch law enforcement agencies, targeting vulnerable individuals.

Unveiling the role of bulletproof hosting services in cybercriminal activities. Discover how these hidden infrastructures facilitate illegal operations.

Discover the risks posed by the CVE-2024-11205 vulnerability in WPForms. Find out how to safeguard your WordPress site and prevent financial loss.
FCC takes action to strengthen telecom cybersecurity after Salt Typhoon cyberattack. Discover the measures being implemented to ensure the safety and security of U.S. networks.

Explore Meta's Third Quarter Adversarial Threat Report and uncover key findings on global influence operations and coordinated inauthentic behavior.

Discover the detailed analysis of the Radiant Capital cyberattack, revealing a complex attack chain and vulnerability exploitation.

Learn about the high-severity vulnerability (CVE-2024-12254) in CPython that could lead to memory exhaustion in Python applications.

Learn about the upcoming enhancement to EFI Zboot in the Linux kernel. See how the optimization of compression algorithms improves efficiency.

Discover the threats posed by SpyNote Remote Administration Tool (RAT) and how it infiltrated targeted systems using disguised Android payloads.

Uncover the highly sophisticated Meeten malware campaign targeting professionals in the Web3 space. Learn how this cross-platform information stealer compromises macOS and Windows devices.

Learn about the vulnerabilities in Qlik Sense Enterprise for Windows: CVE-2024-55579 and CVE-2024-55580. Find out how unprivileged users could compromise the server and gain control.

Find out about the security risk CVE-2024-55563 in the Bitcoin network and its implications for the stability of the Lightning Network.

Learn about Activation Context Hijack and how Eclipse, a proof-of-concept tool, allows attackers to load and execute arbitrary DLLs within a target process.
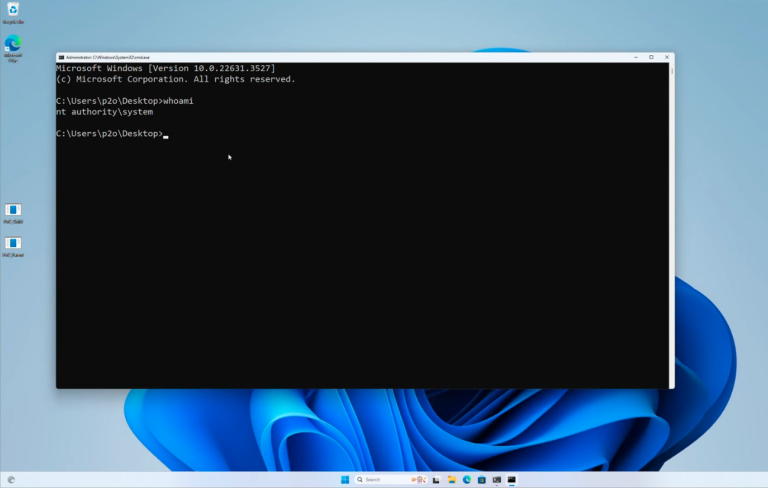
Explore the in-depth analysis of CVE-2024-38193, a critical use-after-free vulnerability in the afd.sys Windows driver. Understand the exploitation process and potential impact.

Stay informed about the latest cyber threat: Mauri ransomware exploiting a critical vulnerability (CVE-2023-46604) in Apache ActiveMQ.

Discover the latest QNAP QTS vulnerability advisory. Learn about the security vulnerabilities affecting License Center and QTS/QuTS hero operating systems.

Stay protected with Google's December 2024 security update for Pixel devices. Learn about the critical remote code execution flaws and other vulnerabilities