Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Privacy and Financial Security at Risk: McAfee Labs Warns of SpyLoan Applications SpyLoan
  • Android
  • Data Leak
  • Malware

Privacy and Financial Security at Risk: McAfee Labs Warns of SpyLoan Applications

Do Son November 26, 2024 0

Protect your privacy and financial security from SpyLoan apps. McAfee Labs reveals the risks of these predatory loan apps exploiting social engineering tactics.

VMware Aria Operations Hit By Multiple Vulnerabilities CVE-2022-31702 - VMware Aria Operations
  • Vulnerability

VMware Aria Operations Hit By Multiple Vulnerabilities

Do Son November 26, 2024 0

Discover the important security updates for VMware Aria Operations. Patch your system to address vulnerabilities, including local privilege escalation and stored cross-site scripting (XSS).

CVE-2024-21887 and More: How Earth Estries APT Group Exploits VPNs & Servers Earth Estries APT group
  • Cyber Security
  • Malware
  • Vulnerability

CVE-2024-21887 and More: How Earth Estries APT Group Exploits VPNs & Servers

Do Son November 26, 2024 0

Learn about the Earth Estries APT group, a significant cyber espionage actor targeting critical sectors and industries worldwide.

CyberVolk: The Hacktivist Collective Blurring Lines Between Activism, Ransomware, and Geopolitics CyberVolk Stealer
  • Cyber Security
  • Malware

CyberVolk: The Hacktivist Collective Blurring Lines Between Activism, Ransomware, and Geopolitics

Do Son November 26, 2024 0

Uncover the activities and alliances of CyberVolk, the pro-Russian hacktivist collective posing a significant threat in the cybercrime world.

CVE-2024-41779 (CVSS 9.8): IBM Rhapsody Model Manager Vulnerability Puts Systems at Risk CVE-2024-41779 - CVE-2025-0159 IBM HashiCorp Acquisition
  • Vulnerability

CVE-2024-41779 (CVSS 9.8): IBM Rhapsody Model Manager Vulnerability Puts Systems at Risk

Do Son November 26, 2024 0

Stay informed about the critical vulnerability CVE-2024-41779 in IBM Engineering Systems Design Rhapsody - Model Manager (RMM) and learn how to protect your systems.
Cybersecurity Alert: MUT-8694 Supply Chain Attack Targets npm and PyPI Ecosystems MUT-8694 threat actor
  • Cyber Security
  • Malware

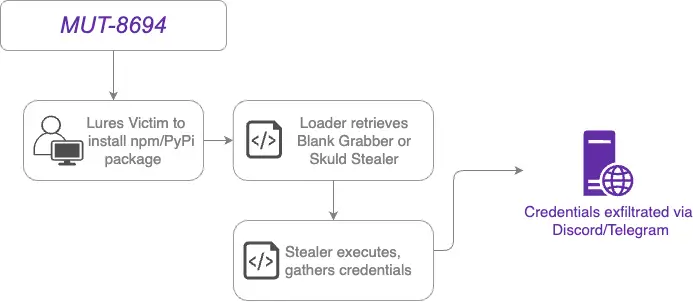
Cybersecurity Alert: MUT-8694 Supply Chain Attack Targets npm and PyPI Ecosystems

Do Son November 26, 2024 0

Uncover the supply chain attack by MUT-8694. Learn how this enigmatic threat actor targeted Windows users using malicious npm and PyPI packages.

Keycloak Patches Multiple Vulnerabilities in Latest Update Keycloak vulnerabilities Keycloak Security MFA Bypass
  • Vulnerability

Keycloak Patches Multiple Vulnerabilities in Latest Update

Do Son November 26, 2024 0

Stay informed about the latest Keycloak vulnerabilities and security updates. Learn about the risks and critical issues affecting the open-source IAM platform.

Kansas City Man Indicted for Hacking into Nonprofit and Health Club NATS-as-C2 Sysdig CVE-2026-33017 Langflow RCE Microsoft Phone Link Hijack CloudZ Pheno Plugin Insider Threat BlackCat (ALPHV) OFAC Sanctions DPRK IT Workers Transparent Tribe APT36 React2Shell, EtherRAT SideWinder Espionage, Netlify Phishing DDNS Abuse, C2 Infrastructure Hacking Health Club
  • Cyber Security

Kansas City Man Indicted for Hacking into Nonprofit and Health Club

Do Son November 26, 2024 0

Learn about the indictment of Nicholas Michael Kloster for hacking into a nonprofit organization and a health club's computer systems.

Palo Alto Networks Warns of GlobalProtect App Flaw with Public Exploit Code (CVE-2024-5921) CVE-2024-5921 - CVE-2025-0103 CVE-2025-0110 PoC
  • Vulnerability

Palo Alto Networks Warns of GlobalProtect App Flaw with Public Exploit Code (CVE-2024-5921)

Do Son November 25, 2024 0

Stay protected from CVE-2024-5921 vulnerability in Palo Alto Networks' GlobalProtect app. Learn how attackers can exploit this issue and how to prevent it.

PHP Patches Multi Flaws, Including CVE-2024-8932 (CVSS 9.8), Urges Immediate Update PHP Vulnerabilities, SQLi DoS CVE-2024-8932 & CVE-2024-8929
  • Vulnerability

PHP Patches Multi Flaws, Including CVE-2024-8932 (CVSS 9.8), Urges Immediate Update

Do Son November 25, 2024 0

Learn about the critical vulnerabilities in PHP versions prior to 8.1.31, 8.2.26, and 8.3.14. CVE-2024-8932 enables attackers to execute arbitrary code.

Critical Vulnerabilities in QNAP Notes Station 3: Update Now to Protect Your Data CVE-2024-38643 - CVE-2024-38645 & Notes Station 3
  • Vulnerability

Critical Vulnerabilities in QNAP Notes Station 3: Update Now to Protect Your Data

Do Son November 25, 2024 0

Stay secure with QNAP's security advisory on critical vulnerabilities in Notes Station 3. Learn about the risks and how to protect your data.

CVE-2024-10542 & CVE-2024-10781: Critical WordPress Plugin Flaw Exposes 200,000 Sites CVE-2024-10542 and CVE-2024-10781
  • Vulnerability

CVE-2024-10542 & CVE-2024-10781: Critical WordPress Plugin Flaw Exposes 200,000 Sites

Do Son November 25, 2024 0

CVE-2024-10542 and CVE-2024-10781 could allow unauthenticated attackers to compromise websites by installing malicious plugins & executing arbitrary code

Infostealers VietCredCare and DuckTail Fuel Facebook Business Account Exploitation VietCredCare
  • Cyber Security

Infostealers VietCredCare and DuckTail Fuel Facebook Business Account Exploitation

Do Son November 25, 2024 0

Stay informed about the Vietnam-based malware threats targeting Facebook Business accounts. Find out how VietCredCare and DuckTail compromise data and fuel an underground market.

North Korean and Chinese Threat Actors Target Crypto, Aerospace, and Government Agencies Storm-2077
  • Cyber Security

North Korean and Chinese Threat Actors Target Crypto, Aerospace, and Government Agencies

Do Son November 25, 2024 0

Unveiling the tactics and motivations of major nation-state cyber actors. Learn about North Korea and China's sophisticated operations in cyberspace.

CVE-2023-28461 (CVSS 9.8): Critical Array Networks Vulnerability Added to KEV Catalog CVE-2023-28461
  • Vulnerability

CVE-2023-28461 (CVSS 9.8): Critical Array Networks Vulnerability Added to KEV Catalog

Do Son November 25, 2024 0

Discover the urgent threat posed by CVE-2023-28461, a critical security flaw in Array Networks AG and vxAG ArrayOS. Find out how to secure your devices now.

Lazarus Group Exploits xattr with “RustyAttr” to Evade Detection RustyAttr
  • Malware

Lazarus Group Exploits xattr with “RustyAttr” to Evade Detection

Do Son November 25, 2024 0

Discover the stealthy technique used by the Lazarus Group: RustyAttr. Learn how this method leverages macOS metadata to conceal malicious payloads.

7 Android & Pixel Vulnerabilities Exposed: Researcher Publishes PoC Exploits Made by Google, Pixel 10 Pixel 10, Qi2 Baseband Security - CVE-2024-39343 Google Tensor TSMC Pixel 10 processor
  • Vulnerability

7 Android & Pixel Vulnerabilities Exposed: Researcher Publishes PoC Exploits

Do Son November 25, 2024 0

Protect your privacy and security: Discover the vulnerabilities affecting Google Pixel devices and Android, and take steps to safeguard your data.

Malicious npm Packages Exploiting Typosquatting to Inject SSH Backdoors Inject SSH Backdoor
  • Malware

Malicious npm Packages Exploiting Typosquatting to Inject SSH Backdoors

Do Son November 25, 2024 0

Beware of malicious npm packages disguising themselves as popular libraries. Learn how these packages inject SSH backdoors into developer systems.

Unveiling the “Nearest Neighbor Attack”: A Russian APT’s Covert Tactic to Weaponize Wi-Fi GruesomeLarch - Nearest Neighbor Attack
  • Cyber Security

Unveiling the “Nearest Neighbor Attack”: A Russian APT’s Covert Tactic to Weaponize Wi-Fi

Do Son November 25, 2024 0

Discover the Nearest Neighbor Attack, a novel cybersecurity technique used by the Russian APT group GruesomeLarch. Learn how Wi-Fi networks can be compromised without direct physical proximity.

CVE-2024-48860 (CVSS 9.5): Critical Flaw in QNAP QuRouter, Immediate Update Recommended QNAP QVR Pro Vulnerability CVE-2026-22898 CVE-2022-27595 - CVE-2024-48860 & CVE-2024-48861
  • Vulnerability

CVE-2024-48860 (CVSS 9.5): Critical Flaw in QNAP QuRouter, Immediate Update Recommended

Do Son November 25, 2024 0

Urgent security advisory: Update your QNAP QuRouter network appliance now to address critical CVE-2024-48860 & CVE-2024-48861 vulnerabilities

CVE-2024-11477: 7-Zip Vulnerability Allows Remote Code Execution, Update Now! CVE-2024-11477
  • Vulnerability

CVE-2024-11477: 7-Zip Vulnerability Allows Remote Code Execution, Update Now!

Do Son November 24, 2024 0

7-Zip vulnerability (CVE-2024-11477): understand the risks and learn how to safeguard your systems from potential code execution attacks.

Google Docs and Weebly Weaponized in New Phishing Scheme Motivated Threat Actors
  • Cyber Security

Google Docs and Weebly Weaponized in New Phishing Scheme

Do Son November 24, 2024 0

Uncover the lengths financially motivated threat actors will go to exploit trusted platforms and infrastructure in a recent phishing campaign.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-76954CVSS 9.8
    An improper neutralization of special elements used in an SQL command vulnerability in the Auth API in Synology...
    📅 Updated: Nov 10, 2026
  • CVE-2026-91241CVSS 9.1
    Vulnerability in the Oracle Business Intelligence Enterprise Edition product of Oracle Analytics (component: Analytics Web Administration). Supported versions...
    📅 Updated: Nov 10, 2026
  • CVE-2026-121683CVSS 9.4
    Missing authentication in Ivanti Cloud Services Application version 5.0.8 allows a remote unauthenticated attacker to add and delete...
    📅 Updated: Nov 10, 2026
  • CVE-2026-83283CVSS 9.8
    Vulnerability in the Oracle Business Intelligence Enterprise Edition product of Oracle Analytics (component: Platform Security). The supported version...
    📅 Updated: Nov 10, 2026
  • CVE-2026-108186CVSS 9.6
    Improper Input Validation in Zoom Workplace for Windows may allow an unauthenticated user to conduct an escalation of...
    📅 Updated: Nov 10, 2026
  • CVE-2026-121653CVSS 9.8
    SQL injection in the Core of Ivanti Endpoint Manager before version 2024 SU8 allows a remote unauthenticated attacker...
    📅 Updated: Nov 10, 2026
  • CVE-2026-125758CVSS 9.1
    Aptabase before commit 61d4c01 contains an authentication bypass vulnerability that allows unauthenticated attackers to forge sign-in links by...
    📅 Updated: Nov 10, 2026
  • CVE-2026-125757CVSS 9.4
    mailcow: dockerized before 2026-11 contains a server-side template injection vulnerability that allows domain administrators to execute commands in...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.