Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
WolfsBane: Gelsemium APT Group’s Linux Backdoor Debut Gelsemium APT group - WolfsBane
  • Cyber Security
  • Malware

WolfsBane: Gelsemium APT Group’s Linux Backdoor Debut

Do Son November 24, 2024 0

Unveiling WolfsBane: The Linux counterpart to Gelsevirine backdoor revealed by ESET researchers. Learn about the evolution of the Gelsemium APT group and their shift in strategy.

Asyncshell: The Evolution of APT-K-47’s Cyber Arsenal Asyncshell
  • Cyber Security
  • Malware

Asyncshell: The Evolution of APT-K-47’s Cyber Arsenal

Do Son November 24, 2024 0

Uncover the evolving threat from the APT-K-47 group and their sophisticated Asyncshell-v4 malware. Learn how this South Asia-based APT group is using malicious campaigns to infiltrate systems.
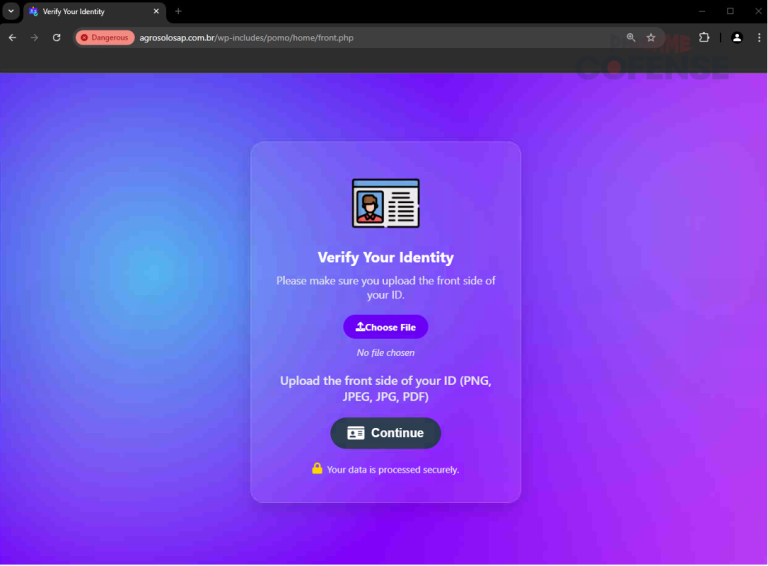
Government IDs and Facial Recognition: A New Phishing Threat Facial Recognition
  • Cyber Security
  • Data Leak

Government IDs and Facial Recognition: A New Phishing Threat

Do Son November 24, 2024 0

Beware of a new phishing scheme targeting government IDs and facial recognition. Learn how to protect yourself from this sophisticated attack.

PROSPERO & Proton66: Unmasking the Bulletproof Hosting Connection bulletproof networks - PROSPERO and Proton66
  • Cyber Security
  • Malware

PROSPERO & Proton66: Unmasking the Bulletproof Hosting Connection

Do Son November 24, 2024 0

Unveiling the operational similarities between PROSPERO and Proton66: a comprehensive report on bulletproof networks and their hosting of malicious software.

Fake Identities, Real Profits: Exposing North Korea’s IT Front Companies DPRK IT Workers
  • Cyber Security

Fake Identities, Real Profits: Exposing North Korea’s IT Front Companies

Do Son November 24, 2024 0

Unveiling the hidden network of DPRK IT workers. Explore how North Korea evades sanctions and generates revenue through front companies.

Fortune 1000’s Hidden Threat: 30,000 Exposed APIs and 100,000 API Vulnerabilities Unveiled API Vulnerabilities - API Exposure
  • Data Leak
  • Vulnerability

Fortune 1000’s Hidden Threat: 30,000 Exposed APIs and 100,000 API Vulnerabilities Unveiled

Do Son November 24, 2024 0

Discover the shocking number of exposed and vulnerable APIs in Fortune 1000 companies. Learn about the implications and security challenges.

Kling AI Announces Black Friday Mega Deals with Upgraded Features for Content Creators AI
  • Technique

Kling AI Announces Black Friday Mega Deals with Upgraded Features for Content Creators

Do Son November 24, 2024 0
On November 11th, Kling AI, a trailblazer in AI-powered image and video generation, has announced sweeping upgrades...
Read More Read more about Kling AI Announces Black Friday Mega Deals with Upgraded Features for Content Creators
CVE-2024-9511 (CVSS 9.8): Critical Flaw in FluentSMTP Plugin Exposes Over 300,000 WordPress Sites to Potential Takeover CVE-2024-9511
  • Vulnerability

CVE-2024-9511 (CVSS 9.8): Critical Flaw in FluentSMTP Plugin Exposes Over 300,000 WordPress Sites to Potential Takeover

Do Son November 23, 2024 0

Learn about the CVE-2024-9511 vulnerability in FluentSMTP WordPress plugin, which could lead to remote code execution on vulnerable websites.

Python NodeStealer Evolution: Targeting Facebook Ads Manager and Credit Cards WordPress Backdoor
  • Malware

Python NodeStealer Evolution: Targeting Facebook Ads Manager and Credit Cards

Do Son November 23, 2024 0

Find out how the NodeStealer infostealer has evolved to target Facebook Ads Manager and collect crucial financial information using Facebook’s Graph API.

Malicious Update in Python Crypto Library Targets Private Keys via Telegram Everon OCPP Vulnerability CVE-2026-26288 ASUSTOR ADM Vulnerability CVE-2026-24936 PrismX MX100 Vulnerability Hard-Coded Credentials Advantech Vulnerability CVE-2025-52694 Eaton UPS Companion, CVE-2025-59887 ASUS Router, Authentication Bypass ASUSTOR DLL Hijacking, Privilege Escalation OpenShift AI, Privilege Escalation GoAnywhere vulnerability CVE-2025-10035 LangChainGo, template injection DeepDiff, class pollution ToolShell Sunshine, CSRF Vulnerability KACE SMA, Critical Vulnerabilities Oracle Zero-Days - PDQ Deploy vulnerability
  • Malware

Malicious Update in Python Crypto Library Targets Private Keys via Telegram

Do Son November 23, 2024 0

Uncover the alarming details of the PyPI crypto library attack. Find out how private keys were exfiltrated by a malicious update.

CVE-2024-8811: WinZip Flaw Allows Malicious Code Execution CVE-2024-8811 - CVE-2025-1240
  • Vulnerability

CVE-2024-8811: WinZip Flaw Allows Malicious Code Execution

Do Son November 22, 2024 0

Critical vulnerability in WinZip exposes users to potential code execution. Learn about CVE-2024-8811 and how to protect your system.

Ignoble Scorpius Strikes Again: The Rise of BlackSuit Ransomware Ignoble Scorpius
  • Cyber Security
  • Malware

Ignoble Scorpius Strikes Again: The Rise of BlackSuit Ransomware

Do Son November 22, 2024 0

Discover the cybercrime group Ignoble Scorpius and their sophisticated ransomware campaign, BlackSuit, targeting industries worldwide.

Wowza Streaming Engine Vulnerabilities Expose Thousands of Servers to Attack Wowza Streaming Engine - CVE-2024-52052
  • Vulnerability

Wowza Streaming Engine Vulnerabilities Expose Thousands of Servers to Attack

Do Son November 22, 2024 0

Learn about the critical vulnerability CVE-2024-52052 in Wowza Streaming Engine and how it could allow remote attackers to take control of affected systems.

Microsoft Takes Down “ONNX” Phishing-as-a-Service Operation Fraudulent ONNX Store Telegram Channels
  • Cyber Security

Microsoft Takes Down “ONNX” Phishing-as-a-Service Operation

Do Son November 22, 2024 0

Microsoft's Digital Crimes Unit strikes blow against cybercrime supply chain. Learn how they seized 240 fraudulent websites and disrupted a major player in the PhaaS industry.
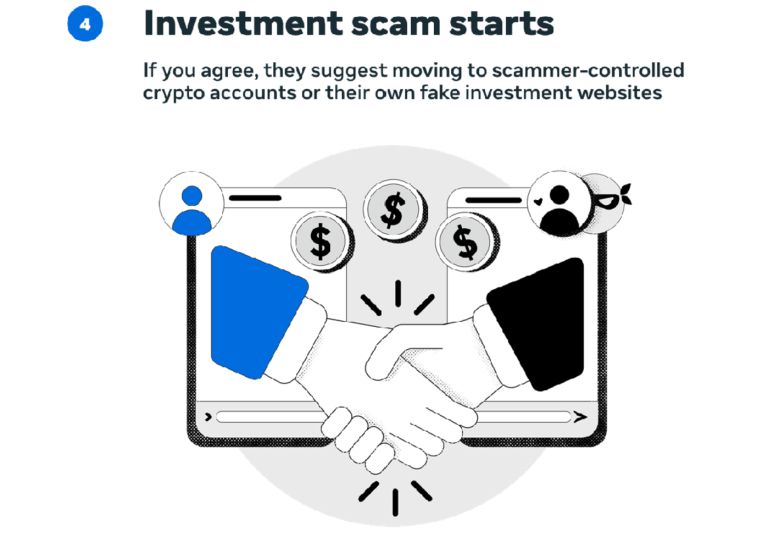
300,000 Forced to Scam: Meta’s Report Reveals Staggering Scale of “Pig Butchering” Pig Butchering
  • Cyber Security

300,000 Forced to Scam: Meta’s Report Reveals Staggering Scale of “Pig Butchering”

Do Son November 22, 2024 0
In a recent report, Meta detailed its efforts to combat the organized crime networks behind “pig butchering”...
Read More Read more about 300,000 Forced to Scam: Meta’s Report Reveals Staggering Scale of “Pig Butchering”
USDA Pioneers Phishing-Resistant MFA with Fast IDentity Online (FIDO) Fast IDentity Online
  • Cyber Security

USDA Pioneers Phishing-Resistant MFA with Fast IDentity Online (FIDO)

Do Son November 22, 2024 0

Discover how the USDA implemented phishing-resistant multi-factor authentication using Fast IDentity Online (FIDO) technology.

CISA Sounds the Alarm on Actively Exploited Apple and Oracle Zero-Days Everon OCPP Vulnerability CVE-2026-26288 ASUSTOR ADM Vulnerability CVE-2026-24936 PrismX MX100 Vulnerability Hard-Coded Credentials Advantech Vulnerability CVE-2025-52694 Eaton UPS Companion, CVE-2025-59887 ASUS Router, Authentication Bypass ASUSTOR DLL Hijacking, Privilege Escalation OpenShift AI, Privilege Escalation GoAnywhere vulnerability CVE-2025-10035 LangChainGo, template injection DeepDiff, class pollution ToolShell Sunshine, CSRF Vulnerability KACE SMA, Critical Vulnerabilities Oracle Zero-Days - PDQ Deploy vulnerability
  • Vulnerability

CISA Sounds the Alarm on Actively Exploited Apple and Oracle Zero-Days

Do Son November 22, 2024 0

Urgent alert: Apple and Oracle products vulnerable to actively exploited flaws. Update your software now to stay protected.
“PopeyeTools” Dismantled: Justice Department Seizes Cybercrime Marketplace and Charges Administrators PopeyeTools
  • Cyber Security

“PopeyeTools” Dismantled: Justice Department Seizes Cybercrime Marketplace and Charges Administrators

Do Son November 22, 2024 0

The U.S. Department of Justice seizes PopeyeTools, an illicit online marketplace for stolen credit cards and cybercrime tools. Three individuals charged.

Why Should Businesses Use Residential Proxies? CVE-2023-49606
  • Technique

Why Should Businesses Use Residential Proxies?

Do Son November 22, 2024 0
If you run a business, you should know the importance of accessing a wide range of data....
Read More Read more about Why Should Businesses Use Residential Proxies?
Red Hat Enterprise Linux Lands on Windows Subsystem for Linux Red Hat Enterprise Linux WSL WSL open source, Windows Linux
  • Linux
  • Technology
  • Windows

Red Hat Enterprise Linux Lands on Windows Subsystem for Linux

Do Son November 21, 2024 0

Discover the power of Red Hat Enterprise Linux on Windows with WSL. Streamline hybrid cloud development and enhance developer flexibility.

DOJ’s Radical Proposal: Could Google Be Forced to Sell Chrome and Android? Chrome Vulnerability CVE-2024-4761 - Google Sell Chrome CVE-2025-1920 Chrome Crash, Browser Issue
  • Technology

DOJ’s Radical Proposal: Could Google Be Forced to Sell Chrome and Android?

Do Son November 21, 2024 0

Get the latest on the DOJ's antitrust lawsuit against Google. Could Google be forced to sell Chrome and Android? Find out more.

Qualities of the Best Security Guard Company: Ensuring Safety and Peace of Mind cybersecurity Advertise
  • Technique

Qualities of the Best Security Guard Company: Ensuring Safety and Peace of Mind

Do Son November 21, 2024 0
In today’s world, the importance of security cannot be overstated. Whether you’re a business owner looking to...
Read More Read more about Qualities of the Best Security Guard Company: Ensuring Safety and Peace of Mind
❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-91241CVSS 9.1
    Vulnerability in the Oracle Business Intelligence Enterprise Edition product of Oracle Analytics (component: Analytics Web Administration). Supported versions...
    📅 Updated: Nov 10, 2026
  • CVE-2026-121683CVSS 9.4
    Missing authentication in Ivanti Cloud Services Application version 5.0.8 allows a remote unauthenticated attacker to add and delete...
    📅 Updated: Nov 10, 2026
  • CVE-2026-83283CVSS 9.8
    Vulnerability in the Oracle Business Intelligence Enterprise Edition product of Oracle Analytics (component: Platform Security). The supported version...
    📅 Updated: Nov 10, 2026
  • CVE-2026-108186CVSS 9.6
    Improper Input Validation in Zoom Workplace for Windows may allow an unauthenticated user to conduct an escalation of...
    📅 Updated: Nov 10, 2026
  • CVE-2026-121653CVSS 9.8
    SQL injection in the Core of Ivanti Endpoint Manager before version 2024 SU8 allows a remote unauthenticated attacker...
    📅 Updated: Nov 10, 2026
  • CVE-2026-125758CVSS 9.1
    Aptabase before commit 61d4c01 contains an authentication bypass vulnerability that allows unauthenticated attackers to forge sign-in links by...
    📅 Updated: Nov 10, 2026
  • CVE-2026-125757CVSS 9.4
    mailcow: dockerized before 2026-11 contains a server-side template injection vulnerability that allows domain administrators to execute commands in...
    📅 Updated: Nov 10, 2026
  • CVE-2026-124917CVSS 9.6
    Sandbox escape due to use-after-free in the Widget: Gtk component. This vulnerability was fixed in Firefox 160 and...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.