 Do Son
Learn about FrostyGoop, an alarming ICS-centric malware that exploits vulnerabilities in internet-exposed devices.

Learn about LIMINAL PANDA, a new China-nexus state-sponsored adversary targeting telecommunications providers and posing a cyber threat to critical infrastructure.

Stay informed about the critical remote code execution vulnerability affecting Veritas Enterprise Vault servers and learn how to protect your organization.

Discover the alarming rise of misconfigured JupyterLab servers and how threat actors exploit them for illegal live sports streaming.

Stay secure with Ruckus APs. Discover the critical vulnerability that allows unauthenticated remote code execution attacks and how to protect your network.

Discover the scale and sophistication of the NSOCKS botnet: a criminal proxy network aiding in DDoS attacks, phishing, and malware obfuscation.

Learn about the D-Link vulnerability affecting several router models and the potential risks of unauthenticated users executing remote code.

Discover the new Ghost Tap tactic in financial cybercrime. Criminals exploit mobile payment services to anonymously cash out stolen credit cards.
Stay safe while shopping on Black Friday. Learn about the cybercriminal tactics used to exploit consumers and businesses during peak shopping seasons.

Discover the severity of CVE-2024-48990 and other critical vulnerabilities in the needrestart utility. Explore how unprivileged users can exploit these flaws to gain root access.
Discover the details of the CVE-2024-51503 vulnerability in Trend Micro Deep Security and the potential impact on affected systems.

The cybersecurity employment market is at a record-high level, and it is only going to get bigger...

Security researcher Valentin Lobstein has developed and released PoC exploit code for CVE-2024-0012 & CVE-2024-9474, enabling effortless exploitation

Critical security vulnerability in Atlassian Sourcetree software (CVE-2024-21697). Learn how an unauthenticated attacker can execute arbitrary code.
Protect your system from security risks with the new Chrome browser update. Learn about the high-severity CVE-2024-11395 vulnerability and its potential impact.
Urgent security alert: Oracle Agile PLM software vulnerability (CVE-2024-21287) exposes critical business information. Take action now!

Discover the Gabagool phishing kit that targets corporate and government employees. Learn how it leverages Cloudflare's R2 storage service to bypass security measures.

CVE-2024-47533 exposes Cobbler servers to unauthorized access and control, enabling attackers to manipulate system configurations.

Explore the rising threat of the Helldown ransomware targeting Linux machines. Find out how Sekoia's TDR team uncovered this new variant.

Stay vigilant! A malvertising campaign is spreading malware disguised as a Bitwarden security update. Read to learn how to avoid falling victim.

Discover the CVE-2024-10524 vulnerability in Wget and learn how attackers can exploit it to launch server-side request forgery attacks.
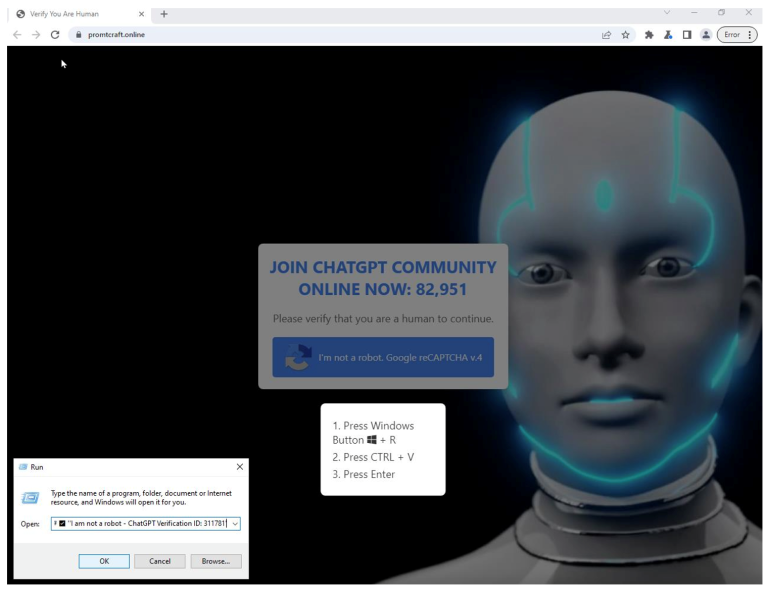
Discover the alarming rise of ClickFix, a unique social engineering method used to spread malware. Learn how it exploits human behavior and how to protect yourself.