Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Grafana Vulnerability CVE-2024-9264: PoC Exploit Released for 9.9-Rated Critical Flaw CVE-2024-9264 exploit
  • Vulnerability

Grafana Vulnerability CVE-2024-9264: PoC Exploit Released for 9.9-Rated Critical Flaw

Do Son October 28, 2024 0

Explore the technical details of CVE-2024-9264, a critical vulnerability in Grafana that allows attackers to exploit SQL expressions feature.

Four REvil Hackers Sentenced: St. Petersburg Court Imposes Years in Penal Colony REvil hacker
  • Cyber Security

Four REvil Hackers Sentenced: St. Petersburg Court Imposes Years in Penal Colony

Do Son October 27, 2024 0

Unmasking the REvil hacker group: delve into their ransomware exploits, identification of key members, and the impacts of their activities.

Synology Fixes Critical Vulnerabilities in Synology Photos and BeePhotos After Pwn2Own Exposure Synology Photos
  • Vulnerability

Synology Fixes Critical Vulnerabilities in Synology Photos and BeePhotos After Pwn2Own Exposure

Do Son October 27, 2024 0

Stay protected with Synology Photos and BeePhotos: Learn about the critical vulnerabilities addressed in the latest security updates.

CVE-2022-45157 (CVSS 9.1): Critical Security Flaw in Rancher Exposes vSphere Credentials in Plaintext Rancher - CVE-2022-45157
  • Vulnerability

CVE-2022-45157 (CVSS 9.1): Critical Security Flaw in Rancher Exposes vSphere Credentials in Plaintext

Do Son October 27, 2024 0

Protect your Rancher deployments from CVE-2022-45157. Discover the critical flaw in Rancher's handling of vSphere CPI and CSI credentials.

Researcher Details CVE-2024-38812 (CVSS 9.8): Critical RCE Flaw in VMware vCenter Screenshot 2024-10-25 005350
  • Vulnerability

Researcher Details CVE-2024-38812 (CVSS 9.8): Critical RCE Flaw in VMware vCenter

Do Son October 27, 2024 0

Understand the impact of CVE-2024-38812, a high-risk exploit, and how to secure your VMware vCenter Server with the necessary updates.

Intrinsec Report: China’s Strategic Exploitation of Cybersecurity Vulnerabilities China cybersecurity
  • Cyber Security
  • Vulnerability

Intrinsec Report: China’s Strategic Exploitation of Cybersecurity Vulnerabilities

Do Son October 27, 2024 0

Discover how China's Regulation on the Management of Network Product Security Vulnerabilities shapes its cybersecurity landscape.
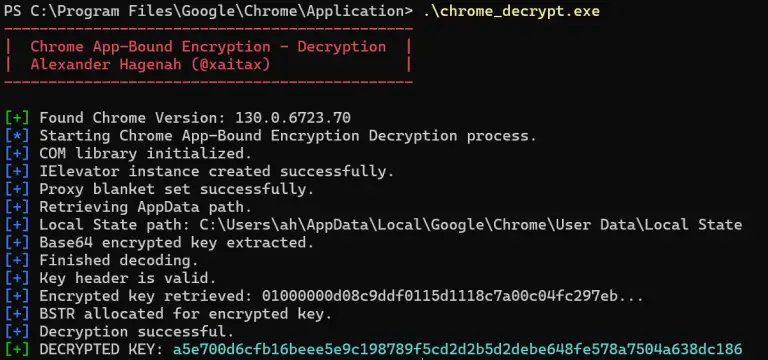
Chrome’s App-Bound Encryption Cracked: Open-Source Tool Bypasses Security Measure Chrome App-Bound Encryption
  • Open Source Tool

Chrome’s App-Bound Encryption Cracked: Open-Source Tool Bypasses Security Measure

Do Son October 27, 2024 0

Learn about the concerns surrounding Chrome's App-Bound Encryption and the decryption of protected keys by a newly released open-source tool.

WhatsUp Gold Users Beware: Critical Authentication Bypass Flaw Exposed – CVE-2024-7763 (CVSS 9.8) Sitefinity critical vulnerabilities Sitefinity security update CVE-2024-7763 - CVE-2024-8785 exploit CVE-2025-1758
  • Vulnerability

WhatsUp Gold Users Beware: Critical Authentication Bypass Flaw Exposed – CVE-2024-7763 (CVSS 9.8)

Do Son October 27, 2024 0

Discover the critical flaw in WhatsUp Gold: CVE-2024-7763. Take action to safeguard your network from unauthorized access and potential cyberattacks

Shahid Hemmat Hackers: $10M Reward Offered by US Shahid Hemmat
  • Cyber Security

Shahid Hemmat Hackers: $10M Reward Offered by US

Do Son October 27, 2024 0

Furthermore, it has been determined that the Shahid Hemmat group collaborates with other individuals and entities affiliated with the IRGC
$20 Million Drained and Returned: Government Wallet Under Scrutiny Tapioca attack
  • Cyber Security

$20 Million Drained and Returned: Government Wallet Under Scrutiny

Do Son October 27, 2024 0

Discover the details of the recent attack on a US government cryptocurrency wallet and the recovery of the stolen funds.

Black Basta Ransomware Group Elevates Social Engineering with Microsoft Teams and Malicious QR Codes Black Basta ransomware group
  • Cyber Security
  • Malware

Black Basta Ransomware Group Elevates Social Engineering with Microsoft Teams and Malicious QR Codes

Do Son October 27, 2024 0

Uncover the latest tactics of the Black Basta ransomware group targeting diverse sectors and geographies. Stay informed about the intensified social engineering campaign.

Healthcare Under Fire: HeptaX Campaign Steals and Manipulates Sensitive Data HeptaX campaign
  • Cyber Security

Healthcare Under Fire: HeptaX Campaign Steals and Manipulates Sensitive Data

Do Son October 27, 2024 0

Learn about the HeptaX cyberespionage campaign and how it exploits RDP settings to infiltrate and manipulate data across industries.

Cyber-Espionage Campaign Unveiled: Operation Cobalt Whisper Hits Sensitive Industries Operation Cobalt Whisper
  • Cyber Security

Cyber-Espionage Campaign Unveiled: Operation Cobalt Whisper Hits Sensitive Industries

Do Son October 27, 2024 0

Get insights into Operation Cobalt Whisper, a cyber-espionage campaign targeting defense, research, and technical sectors in South Asia.

DTLS “ClientHello” Race Condition: A New Threat to WebRTC Security DTLS “ClientHello” Race Condition
  • Vulnerability

DTLS “ClientHello” Race Condition: A New Threat to WebRTC Security

Do Son October 27, 2024 0

Find out about the DTLS “ClientHello” Race Condition flaw in WebRTC and its implications for user experience and service availability.

CVE-2024-9488 (CVSS 9.8): Authentication Bypass Flaw in wpDiscuz Plugin, Over 80,000 Sites at Risk CVE-2024-9488
  • Vulnerability

CVE-2024-9488 (CVSS 9.8): Authentication Bypass Flaw in wpDiscuz Plugin, Over 80,000 Sites at Risk

Do Son October 26, 2024 0

Critical vulnerability in wpDiscuz plugin (CVE-2024-9488). Learn how unauthenticated attackers can hijack user accounts in WordPress.

SolarSys: New Trojan Framework Threatens Brazilian Banking Customers SolarSys Trojan
  • Malware

SolarSys: New Trojan Framework Threatens Brazilian Banking Customers

Do Son October 26, 2024 0

Discover SolarSys, a dangerous Trojan framework that poses a serious threat to Brazilian banking customers. Stay informed and protect your online security.

CVE-2024-10327: Okta Verify for iOS Vulnerability Could Allow Unauthorized Access CVE-2024-10327 - Okta Verify Desktop
  • Vulnerability

CVE-2024-10327: Okta Verify for iOS Vulnerability Could Allow Unauthorized Access

Do Son October 25, 2024 0

Understand the impact of the CVE-2024-10327 vulnerability in Okta Verify for iOS and how it can grant attackers access to user accounts.

Rekoobe Backdoor and Typosquatting Domains: A Potential Threat to TradingView Users Rekoobe backdoor
  • Malware

Rekoobe Backdoor and Typosquatting Domains: A Potential Threat to TradingView Users

Do Son October 25, 2024 0

Discover the Rekoobe backdoor: a new cybersecurity threat with ties to APT31. Learn how it uses encrypted files and customized protocols to avoid detection in open directories.
CVE-2024-47901 (CVSS 10): Critical Security Flaw in Siemens InterMesh Siemens SIMATIC Vulnerability CVE-2025-40943 CVE-2024-47901 - Siemens InterMesh system CVE-2025-40804 Siemens SIVaaS
  • Vulnerability

CVE-2024-47901 (CVSS 10): Critical Security Flaw in Siemens InterMesh

Do Son October 24, 2024 0

Uncover the severe vulnerability CVE-2024-47901 in Siemens' InterMesh system. Learn about the potential impact and the steps to mitigate this critical security issue.

North Korean Cyber Espionage Group Tenacious Pungsan Compromises Open-Source Repositories with Backdoored npm Packages Mercenary Akula European Financial Targeting AI-Generated Malware React2Shell Exploit UAT-8837 Critical Infrastructure Attack APT36, BOSS Linux BRICKSTORM Malware, China Espionage Curly COMrades, MucorAgent Chinese APT - HTTP Client Tools Shuckworm Cyber Espionage
  • Cyber Security
  • Malware

North Korean Cyber Espionage Group Tenacious Pungsan Compromises Open-Source Repositories with Backdoored npm Packages

Do Son October 24, 2024 0

Uncover the malicious activities of the Tenacious Pungsan group. Learn how they target developers through name-squatting attacks on popular npm packages.

CISA Sounds Alarm on Actively Exploited Cisco and Roundcube Vulnerabilities CISA active exploit catalog critical gateway flaws CVE-2023-27532 & CVE-2024-37383
  • Vulnerability

CISA Sounds Alarm on Actively Exploited Cisco and Roundcube Vulnerabilities

Do Son October 24, 2024 0

Don't overlook the risks! Learn about actively exploited flaws in Cisco devices & Roundcube webmail software: CVE-2024-37383 & CVE-2024-20481

UNC5267: Exposing North Korea’s State-Sponsored IT Worker Infiltration UNC5267
  • Cyber Security

UNC5267: Exposing North Korea’s State-Sponsored IT Worker Infiltration

Do Son October 24, 2024 0

Explore the operations of UNC5267, a sophisticated North Korean cyber group that targets Western companies. Discover their tactics and the ongoing threat they pose.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-76954CVSS 9.8
    An improper neutralization of special elements used in an SQL command vulnerability in the Auth API in Synology...
    📅 Updated: Nov 10, 2026
  • CVE-2026-91241CVSS 9.1
    Vulnerability in the Oracle Business Intelligence Enterprise Edition product of Oracle Analytics (component: Analytics Web Administration). Supported versions...
    📅 Updated: Nov 10, 2026
  • CVE-2026-121683CVSS 9.4
    Missing authentication in Ivanti Cloud Services Application version 5.0.8 allows a remote unauthenticated attacker to add and delete...
    📅 Updated: Nov 10, 2026
  • CVE-2026-83283CVSS 9.8
    Vulnerability in the Oracle Business Intelligence Enterprise Edition product of Oracle Analytics (component: Platform Security). The supported version...
    📅 Updated: Nov 10, 2026
  • CVE-2026-108186CVSS 9.6
    Improper Input Validation in Zoom Workplace for Windows may allow an unauthenticated user to conduct an escalation of...
    📅 Updated: Nov 10, 2026
  • CVE-2026-121653CVSS 9.8
    SQL injection in the Core of Ivanti Endpoint Manager before version 2024 SU8 allows a remote unauthenticated attacker...
    📅 Updated: Nov 10, 2026
  • CVE-2026-125758CVSS 9.1
    Aptabase before commit 61d4c01 contains an authentication bypass vulnerability that allows unauthenticated attackers to forge sign-in links by...
    📅 Updated: Nov 10, 2026
  • CVE-2026-125757CVSS 9.4
    mailcow: dockerized before 2026-11 contains a server-side template injection vulnerability that allows domain administrators to execute commands in...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.