Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Red Hat Warns of Privilege Escalation Flaw CVE-2024-9050 in NetworkManager-libreswan CVE-2024-9050
  • Linux
  • Vulnerability

Red Hat Warns of Privilege Escalation Flaw CVE-2024-9050 in NetworkManager-libreswan

Do Son October 22, 2024 0

Discover the newly discovered flaw (CVE-2024-9050) in NetworkManager-libreswan and the risks it poses to Red Hat Enterprise Linux 9 systems.

1,700 Banks, 45 Countries: Grandoreiro Trojan Expands its Reach online-banking-3559760_640
  • Malware

1,700 Banks, 45 Countries: Grandoreiro Trojan Expands its Reach

Do Son October 22, 2024 0

Get insights into the global reach of Grandoreiro banking trojan. Discover how this potent malware is targeting 1,700 banks and 276 cryptocurrency wallets, posing a threat to financial institutions worldwide.

Urgent Security Update: Guix System Patches Critical Vulnerability GNU Guix, privilege escalation guix-daemon vulnerability
  • Linux
  • Vulnerability

Urgent Security Update: Guix System Patches Critical Vulnerability

Do Son October 22, 2024 0

Learn about the critical security vulnerability in the Guix system's guix-daemon and how it can be exploited to escalate privileges.

Virtual Hard Drives: The New Bypass for Secure Email Gateways and Antivirus Scanners XWorm RAT
  • Malware

Virtual Hard Drives: The New Bypass for Secure Email Gateways and Antivirus Scanners

Do Son October 22, 2024 0

Learn about a critical vulnerability in Secure Email Gateways and Antivirus scanners. Find out how to protect your organization from malicious VHD files.
Hardcoded Cloud Credentials Found in Popular Mobile Apps: A Major Security Flaw Booking.com Data Breach Claude Code Leak Anthropic Source Code YggTorrent data breach PS5 BootROM key leak 2026, PlayStation 5 unpatchable jailbreak Great Firewall data leak Dating App Breach, Tea App Leak 23andMe Data Leak
  • Data Leak

Hardcoded Cloud Credentials Found in Popular Mobile Apps: A Major Security Flaw

Do Son October 22, 2024 0

New security issue puts mobile app users at risk. Learn about hardcoded cloud credentials in popular apps and how it exposes sensitive data.

Dark Web Anti-Bot Services Enable Phishing Pages to Bypass Google’s “Red Page” bypass Google Red Page
  • Cyber Security

Dark Web Anti-Bot Services Enable Phishing Pages to Bypass Google’s “Red Page”

Do Son October 22, 2024 0

Discover how cybercriminals are bypassing Google's 'Red Page' warnings and putting users at risk. Learn about the rise of anti-bot services on the dark web.

Meta Combats Scams and Account Takeovers with Facial Recognition tackle celeb-bait scams
  • Technology

Meta Combats Scams and Account Takeovers with Facial Recognition

Do Son October 22, 2024 0

Discover how Meta is combatting celeb-bait scams on Facebook and Instagram with facial recognition technology.

Cryptojacking Alert: Hackers Exploit gRPC and HTTP/2 to Deploy Miners SRBMiner
  • Malware

Cryptojacking Alert: Hackers Exploit gRPC and HTTP/2 to Deploy Miners

Do Son October 22, 2024 0

Discover how cybercriminals use gRPC over h2c to deploy SRBMiner on Docker servers and mine XRP cryptocurrency.

Inside China’s State-Sponsored Hacking Competitions: Talent Spotting and Global Outreach Zhujian Cup
  • Cyber Security

Inside China’s State-Sponsored Hacking Competitions: Talent Spotting and Global Outreach

Do Son October 22, 2024 0

Explore China's impressive Capture the Flag (CTF) competition ecosystem and its role in shaping the country's cybersecurity strategy.
Tapioca Foundation Offers $1M Bounty After $4.7M DeFi Heist Tapioca attack
  • Cyber Security

Tapioca Foundation Offers $1M Bounty After $4.7M DeFi Heist

Do Son October 22, 2024 0

Discover the details of the Tapioca Foundation attack: learn how a social engineering scheme led to the theft of $4.7 million in cryptocurrency.

Exposed Docker APIs Under Attack: New Malware Campaign Deploys “perfctl” Docker Remote API - perfctl malware
  • Malware

Exposed Docker APIs Under Attack: New Malware Campaign Deploys “perfctl”

Do Son October 22, 2024 0

Discover the cyberattack campaign targeting Docker Remote API servers and the deployment of the perfctl malware.

OneDev DevOps Platform Patches Critical Security Flaw Exposing Sensitive Data – (CVE-2024-45309) CVE-2024-45309
  • Vulnerability

OneDev DevOps Platform Patches Critical Security Flaw Exposing Sensitive Data – (CVE-2024-45309)

Do Son October 22, 2024 0

Learn about the critical security vulnerability (CVE-2024-45309) in the popular open-source DevOps platform, OneDev. Discover the potential risks and how to mitigate them.

Critical EoP Flaw in Microsoft’s Remote Registry: Researcher Publishes PoC for CVE-2024-43532 HTTP.sys RCE vulnerability, Windows HTTP stack exploit, CVE-2026-47291 Netlogon RCE vulnerability Exploited in the wild Secure Boot certificate renewal 2026, Windows 11 UEFI update Community-First AI Infrastructure, Microsoft self-funding energy mandate aka.ms/aoh online portal CVE-2025-55681, Windows DWM Elevation Windows Administrator Protection, CVE-2025-60718 Microsoft AI Compute, IREN Infrastructure Microsoft Japan PPA, Renewable Energy Microsoft AI Investment, Cloud Expansion Microsoft Azure, Startup Credits Infinite Workday, AI in Work Microsoft Russia, Bankruptcy AI code generation, Microsoft AI Microsoft Layoffs, Restructuring
  • Vulnerability

Critical EoP Flaw in Microsoft’s Remote Registry: Researcher Publishes PoC for CVE-2024-43532

Do Son October 21, 2024 0

Get insights into the technical details and proof-of-concept exploit code for CVE-2024-43532, a critical Remote Registry Service EoP flaw
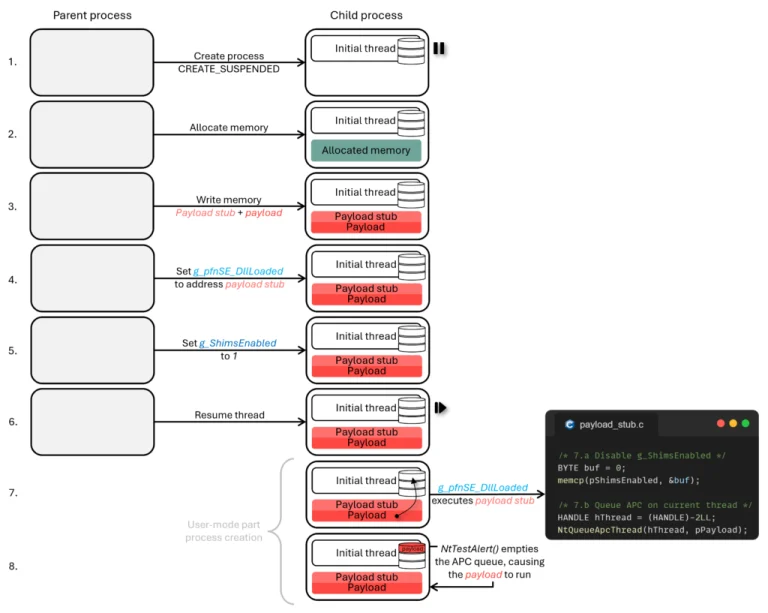
Early Cascade Injection: A Novel Evasion Technique Flow Early Cascade Injection
  • Vulnerability

Early Cascade Injection: A Novel Evasion Technique

Do Son October 21, 2024 0

Discover the groundbreaking Early Cascade Injection method for evading modern Endpoint Detection and Response (EDR) systems.

BattlEye Vulnerability: “BannleEye” Exploit Allows Arbitrary Banning Users BannleEye vulnerability
  • Vulnerability

BattlEye Vulnerability: “BannleEye” Exploit Allows Arbitrary Banning Users

Do Son October 21, 2024 0

Discover the BannleEye vulnerability in BattlEye, a widely used anti-cheat system, and how it can jeopardize user accounts in online games.
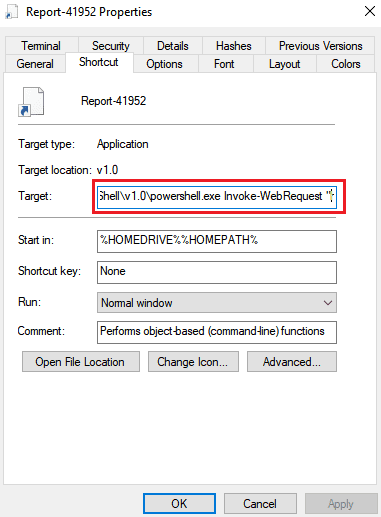
Bumblebee Loader Resurfaces with New Infection Chain Bumblebee-Loader
  • Malware

Bumblebee Loader Resurfaces with New Infection Chain

Do Son October 21, 2024 0

Explore the Bumblebee loader and its role in cybercrime. Learn about its new infection chain and the risks it poses to organizations.
BianLian Ransomware Gang Claims Attack on Boston Children’s Health Physicians, Compromising Thousands of Patient Records MedusaLocker ransomware - BabyLockerKZ
  • Cyber Security

BianLian Ransomware Gang Claims Attack on Boston Children’s Health Physicians, Compromising Thousands of Patient Records

Do Son October 21, 2024 0

Discover the details of the BCHP data breach and the actions taken by the organization to protect affected patients. Stay informed about the incident and its consequences.

Akira Ransomware Exploit CVE-2024-40766 in SonicWall SonicOS Akira ransomware tactics
  • Malware
  • Vulnerability

Akira Ransomware Exploit CVE-2024-40766 in SonicWall SonicOS

Do Son October 21, 2024 0

Discover the latest tactics of the Akira ransomware group and how they have evolved to target both Windows and Linux hosts.
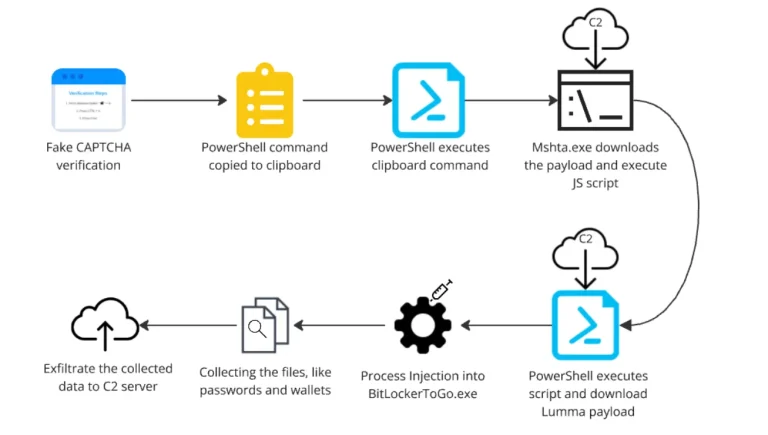
MaaS in Action: How Lumma Stealer Employs Advanced Delivery Techniques Lumma Stealer Tactics
  • Malware

MaaS in Action: How Lumma Stealer Employs Advanced Delivery Techniques

Do Son October 21, 2024 0

Explore the advanced delivery techniques and deceptive tactics employed by Lumma Stealer, an insidious information-stealing malware.
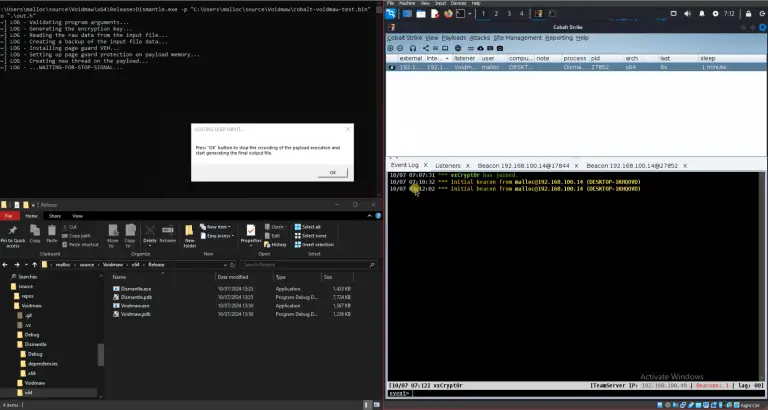
VOIDMAW: A New Bypass Technique for Memory Scanners Bypass Memory Scanners
  • Open Source Tool

VOIDMAW: A New Bypass Technique for Memory Scanners

Do Son October 21, 2024 0

Discover VOIDMAW, an innovative technique to bypass memory scanners and hide problematic code from antivirus software.

CVE-2024-9537 (CVSS 9.8): Critical Zero-Day in ScienceLogic EM7 Leads to Rackspace Security Incident CVE-2024-9537 - ScienceLogic EM7
  • Vulnerability

CVE-2024-9537 (CVSS 9.8): Critical Zero-Day in ScienceLogic EM7 Leads to Rackspace Security Incident
Do Son October 21, 2024 0

Discover the details of the security incident at Rackspace caused by the CVE-2024-9537 zero-day vulnerability in ScienceLogic EM7.
Cisco Investigates Potential Data Exposure, Confirms No Breach of Internal Systems CVE-2024-20404 and CVE-2024-20405
  • Data Leak

Cisco Investigates Potential Data Exposure, Confirms No Breach of Internal Systems

Do Son October 21, 2024 0

Cisco investigates alleged unauthorized data access in DevHub environment. Learn more about the incident and the steps taken to address it.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-76954CVSS 9.8
    An improper neutralization of special elements used in an SQL command vulnerability in the Auth API in Synology...
    📅 Updated: Nov 10, 2026
  • CVE-2026-91241CVSS 9.1
    Vulnerability in the Oracle Business Intelligence Enterprise Edition product of Oracle Analytics (component: Analytics Web Administration). Supported versions...
    📅 Updated: Nov 10, 2026
  • CVE-2026-121683CVSS 9.4
    Missing authentication in Ivanti Cloud Services Application version 5.0.8 allows a remote unauthenticated attacker to add and delete...
    📅 Updated: Nov 10, 2026
  • CVE-2026-83283CVSS 9.8
    Vulnerability in the Oracle Business Intelligence Enterprise Edition product of Oracle Analytics (component: Platform Security). The supported version...
    📅 Updated: Nov 10, 2026
  • CVE-2026-108186CVSS 9.6
    Improper Input Validation in Zoom Workplace for Windows may allow an unauthenticated user to conduct an escalation of...
    📅 Updated: Nov 10, 2026
  • CVE-2026-121653CVSS 9.8
    SQL injection in the Core of Ivanti Endpoint Manager before version 2024 SU8 allows a remote unauthenticated attacker...
    📅 Updated: Nov 10, 2026
  • CVE-2026-125758CVSS 9.1
    Aptabase before commit 61d4c01 contains an authentication bypass vulnerability that allows unauthenticated attackers to forge sign-in links by...
    📅 Updated: Nov 10, 2026
  • CVE-2026-125757CVSS 9.4
    mailcow: dockerized before 2026-11 contains a server-side template injection vulnerability that allows domain administrators to execute commands in...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.