Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
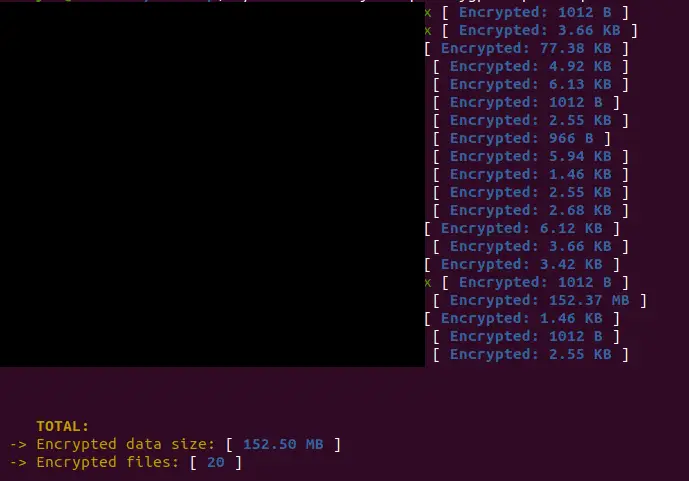
From Windows to Linux to ESXi: The Cicada3301 Ransomware Hits Them All Cicada3301 RaaS
  • Cyber Security
  • Malware

From Windows to Linux to ESXi: The Cicada3301 Ransomware Hits Them All

Do Son October 17, 2024 0

Explore the rise of Cicada3301, a notorious ransomware group targeting critical infrastructure. Discover their methods and impact on organizations.

Spring Framework Vulnerability CVE-2024-38819: Path Traversal Risk in Web Apps Spring Data vulnerabilities Spring Cloud Config CVE-2026-22739 Spring Gateway SpEL, STOMP WebSocket CSRF Spring Security, vulnerability CVE-2024-38819 CVE-2025-41243 Spring Cloud Gateway, vulnerability
  • Vulnerability

Spring Framework Vulnerability CVE-2024-38819: Path Traversal Risk in Web Apps

Do Son October 17, 2024 0

Discover the potential security risks posed by CVE-2024-38819, a path traversal vulnerability in Spring Framework, and what it means for web app security

North Korean IT Worker Schemes Evolve: From Salary Scams to Cyber Extortion NICKEL TAPESTRY
  • Cyber Security

North Korean IT Worker Schemes Evolve: From Salary Scams to Cyber Extortion

Do Son October 17, 2024 0

Discover the disturbing escalation of tactics used by North Korean government-linked actors in fraudulent IT jobs. Learn how they are targeting Western companies.

HORUS Protector: The New Undetectable Malware Crypter Threatening Cybersecurity HORUS Protector
  • Malware

HORUS Protector: The New Undetectable Malware Crypter Threatening Cybersecurity

Do Son October 17, 2024 0

Learn about the new malware crypter, HORUS Protector, and its potential impact on cybersecurity defenses. Stay informed and protect your systems.

Cisco ATA 190 Series Analog Telephone Adapter Firmware Flaws Exposed: Patch Now! Cisco CCX RCE and Java RMI Flaw CVE-2024-20458 - CVE-2025-20111 Cisco Smart Licensing Utility Flaw
  • Vulnerability

Cisco ATA 190 Series Analog Telephone Adapter Firmware Flaws Exposed: Patch Now!

Do Son October 17, 2024 0

Protect your Cisco ATA 190 Series Analog Telephone Adapter from high-severity vulnerabilities. Learn about CVE-2024-20458 and how to secure your device.

Pro-Russian Threat Actors Launch Coordinated DDoS Attacks Against Japanese Organizations NoName057(16)
  • Cyber Security

Pro-Russian Threat Actors Launch Coordinated DDoS Attacks Against Japanese Organizations

Do Son October 17, 2024 0

Uncover the latest cyber attacks targeting Japan's military cooperation with the US. Learn about the pro-Russian hacktivists behind the coordinated DDoS attack campaign.

How to Choose a Military Holster for Rapid Deployment camouflage-1541188_1280
  • Technique

How to Choose a Military Holster for Rapid Deployment

Do Son October 17, 2024 0
When it comes to military operations, every piece of gear plays a critical role in ensuring readiness,...
Read More Read more about How to Choose a Military Holster for Rapid Deployment
HM Surf (CVE-2024-44133): macOS Flaw Exposing Cameras and Microphones to Hackers, PoC Published CVE-2024-44133 - HM Surf
  • Vulnerability

HM Surf (CVE-2024-44133): macOS Flaw Exposing Cameras and Microphones to Hackers, PoC Published

Do Son October 17, 2024 0

Learn about CVE-2024-44133, a serious vulnerability in macOS that bypasses Apple's TCC technology, potentially exposing sensitive user data.

FBI, CISA, NSA Warn of Iranian Cyberattacks on Critical Infrastructure Iranian Cyberattacks
  • Cyber Security

FBI, CISA, NSA Warn of Iranian Cyberattacks on Critical Infrastructure

Do Son October 17, 2024 0

Stay informed about the alarming rise in Iranian cyberattacks targeting critical infrastructure. Learn about the techniques used and how to protect your organization.

CVE-2024-43240 & CVE-2024-43242 in Ultimate Membership Pro Plugin Put 40,000 Websites at Risk Ultimate Membership Pro - CVE-2024-43240 & CVE-2024-43242
  • Vulnerability

CVE-2024-43240 & CVE-2024-43242 in Ultimate Membership Pro Plugin Put 40,000 Websites at Risk

Do Son October 17, 2024 0

Discover the security flaws in the Ultimate Membership Pro plugin for WordPress. Learn about the vulnerabilities and how they can impact your membership subscriptions.

600 Million Daily Cyberattacks: Microsoft’s Alarming Report Cyber Threat
  • Cyber Security

600 Million Daily Cyberattacks: Microsoft’s Alarming Report

Do Son October 17, 2024 0

Stay informed about the rise of cyber threats in the digital age. Explore Microsoft's Digital Defense Report and discover the alarming trends of nation-state actors collaborating with cybercriminals.

X (formerly Twitter) to Use User Data for AI Development, No Compensation Offered X artificial intelligence
  • Technology

X (formerly Twitter) to Use User Data for AI Development, No Compensation Offered

Do Son October 17, 2024 0

Discover the revisions to X's Terms of Service and user blocking functionality. Get insights into the changes coming into effect on November 15, 2024.
Attackers Hijack 360 Total Security to Deliver SSLoad securityonline_cover
  • Cyber Security
  • Malware

Attackers Hijack 360 Total Security to Deliver SSLoad

Do Son October 17, 2024 0

Find out how cybercriminals are using a new loader called PhantomLoader to distribute the SSLoad malware undetected.

CVE-2024-45216: Critical Authentication Bypass Vulnerability Patched in Apache Solr CVE-2024-45216 & CVE-2024-45217
  • Vulnerability

CVE-2024-45216: Critical Authentication Bypass Vulnerability Patched in Apache Solr

Do Son October 16, 2024 0

Protect your organization from the risks of CVE-2024-45216 & CVE-2024-45217, a critical vulnerability in Apache Solr.

Broadcom Warns of High-Risk VMware HCX Vulnerability (CVE-2024-38814) VMware Fusion Privilege Escalation CVE-2026-41702 TOCTOU VMware Vulnerabilities, Broadcom Security CVE-2024-38814 - VMware HCX CVE-2025-22224, CVE-2025-22225, and CVE-2025-22226
  • Vulnerability

Broadcom Warns of High-Risk VMware HCX Vulnerability (CVE-2024-38814)

Do Son October 16, 2024 0

Learn about the serious security flaw (CVE-2024-38814) affecting VMware HCX and the high risk it poses to multi-cloud infrastructures.

LockBit Imposter: New Ransomware Leverages AWS for Attacks AWS S3
  • Malware

LockBit Imposter: New Ransomware Leverages AWS for Attacks

Do Son October 16, 2024 0

Discover the hidden threats of ransomware abusing AWS S3 infrastructure. Explore the tactics used by this sophisticated operation to steal sensitive data.
CVE-2024-48904 (CVSS 9.8): Critical Command Injection Vulnerability in Trend Micro Cloud Edge Trend Micro Apex One CVE-2025-71210 AI Security Trend Micro Deep Security - CVE-2024-48904 & CVE-2024-51503
  • Vulnerability

CVE-2024-48904 (CVSS 9.8): Critical Command Injection Vulnerability in Trend Micro Cloud Edge

Do Son October 16, 2024 0

Urgent security bulletin: Trend Micro warns of critical command injection vulnerability in Cloud Edge appliance (CVE-2024-48904).

ShadowLogic: The Codeless Backdoor Threatening AI Supply Chains ShadowLogic backdoors
  • Malware

ShadowLogic: The Codeless Backdoor Threatening AI Supply Chains

Do Son October 16, 2024 0

Discover the groundbreaking cybersecurity development known as ShadowLogic, a method for embedding undetectable backdoors in AI models.

Ragic Enterprise Cloud Database Patches Multi Flaws, Including CVE-2024-9984 (CVSS 9.8) Ragic Enterprise Cloud Database - CVE-2024-9983 - CVE-2024-9984 - CVE-2024-9985
  • Vulnerability

Ragic Enterprise Cloud Database Patches Multi Flaws, Including CVE-2024-9984 (CVSS 9.8)

Do Son October 16, 2024 0

Beware of CVE-2024-9984: a critical vulnerability in Ragic Enterprise Cloud Database. Learn how attackers can exploit missing authentication and gain unauthorized access to sensitive data.

U.S. DOJ Charges Operators of Anonymous Sudan for DDoS Attacks on Critical Infrastructure Anonymous Sudan Cyberattacks
  • Cyber Security

U.S. DOJ Charges Operators of Anonymous Sudan for DDoS Attacks on Critical Infrastructure

Do Son October 16, 2024 0

Discover the activities of Anonymous Sudan, a notorious cybercriminal group involved in thousands of DDoS attacks worldwide.

Matrix Discloses High-Severity Vulnerabilities in Encryption Key Sharing CVE-2024-47080 & CVE-2024-47824
  • Vulnerability

Matrix Discloses High-Severity Vulnerabilities in Encryption Key Sharing

Do Son October 16, 2024 0

Find out how matrix-js-sdk and matrix-react-sdk vulnerabilities CVE-2024-47080 and CVE-2024-47824 pose a risk to encrypted message history.

Apache CloudStack Patches Critical Security Flaws in Latest Release CVE-2024-45219 - CVE-2024-45693
  • Vulnerability

Apache CloudStack Patches Critical Security Flaws in Latest Release

Do Son October 16, 2024 0

Learn about the latest security releases from Apache CloudStack. Find out how CVE-2024-45219 could compromise KVM-based infrastructure.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-76954CVSS 9.8
    An improper neutralization of special elements used in an SQL command vulnerability in the Auth API in Synology...
    📅 Updated: Nov 10, 2026
  • CVE-2026-91241CVSS 9.1
    Vulnerability in the Oracle Business Intelligence Enterprise Edition product of Oracle Analytics (component: Analytics Web Administration). Supported versions...
    📅 Updated: Nov 10, 2026
  • CVE-2026-121683CVSS 9.4
    Missing authentication in Ivanti Cloud Services Application version 5.0.8 allows a remote unauthenticated attacker to add and delete...
    📅 Updated: Nov 10, 2026
  • CVE-2026-83283CVSS 9.8
    Vulnerability in the Oracle Business Intelligence Enterprise Edition product of Oracle Analytics (component: Platform Security). The supported version...
    📅 Updated: Nov 10, 2026
  • CVE-2026-108186CVSS 9.6
    Improper Input Validation in Zoom Workplace for Windows may allow an unauthenticated user to conduct an escalation of...
    📅 Updated: Nov 10, 2026
  • CVE-2026-121653CVSS 9.8
    SQL injection in the Core of Ivanti Endpoint Manager before version 2024 SU8 allows a remote unauthenticated attacker...
    📅 Updated: Nov 10, 2026
  • CVE-2026-125758CVSS 9.1
    Aptabase before commit 61d4c01 contains an authentication bypass vulnerability that allows unauthenticated attackers to forge sign-in links by...
    📅 Updated: Nov 10, 2026
  • CVE-2026-125757CVSS 9.4
    mailcow: dockerized before 2026-11 contains a server-side template injection vulnerability that allows domain administrators to execute commands in...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.