Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
NSA, FBI, and Allies Expose Ongoing Russian Cyber Espionage Operations Cyber Operations Messaging App Security State-Sponsored Hijacking
  • Cyber Security
  • Vulnerability

NSA, FBI, and Allies Expose Ongoing Russian Cyber Espionage Operations

Do Son October 11, 2024 0

Stay informed and protected from Russian cyber operations with this Joint Cybersecurity Advisory released by the NSA, FBI, CNMF, and NCSC.

Lynx Ransomware: The Evolution of INC Ransomware into a Potent Cyber Threat INC ransomware
  • Malware

Lynx Ransomware: The Evolution of INC Ransomware into a Potent Cyber Threat

Do Son October 11, 2024 0

Learn about the dangerous Lynx ransomware, a rebranding of INC ransomware. Find out how it threatens businesses and employs double extortion tactics.

DOJ Charges 18 in Cryptocurrency Fraud Case, Seizes Over $25 Million Cryptocurrency Fraud Case
  • Cyber Security

DOJ Charges 18 in Cryptocurrency Fraud Case, Seizes Over $25 Million

Do Son October 11, 2024 0

Uncover the details of a groundbreaking cryptocurrency fraud case involving market manipulation, wash trades, and seizures of over $25 million worth of cryptocurrency.
CISA Warns of F5 BIG-IP Cookie Exploitation F5 BIG-IP Hunt Electronic DVR, Critical Vulnerability
  • Vulnerability

CISA Warns of F5 BIG-IP Cookie Exploitation

Do Son October 11, 2024 0

CISA warns of vulnerability in F5 BIG-IP affecting network security. Learn how unencrypted cookies can be exploited by cyber threat actors.

Fog & Akira Ransomware Exploit Critical Veeam RCE Flaw CVE-2024-40711 After PoC Release Veeam RCE
  • Malware
  • Vulnerability

Fog & Akira Ransomware Exploit Critical Veeam RCE Flaw CVE-2024-40711 After PoC Release

Do Son October 10, 2024 0

Protect your enterprise from ransomware attacks exploiting Veeam Backup & Replication vulnerability. Patch and fortify your systems now!

Multiple Vulnerabilities Found in SonicWall SSL-VPN SMA1000 and Connect Tunnel Windows Client SonicWall SSL-VPN SMA1000 - CVE-2024-45316
  • Vulnerability

Multiple Vulnerabilities Found in SonicWall SSL-VPN SMA1000 and Connect Tunnel Windows Client

Do Son October 10, 2024 0

Discover the recent security updates for SonicWall's SMA 1000 series SSL-VPN appliances. Learn how to address potential vulnerabilities and protect your system from attacks.

CVE-2024-9465 (CVSS 9.2) SQLi Flaw in Palo Alto Expedition Revealed: Full Exploit & PoC Published CVE-2024-9465 PoC exploit
  • Vulnerability

CVE-2024-9465 (CVSS 9.2) SQLi Flaw in Palo Alto Expedition Revealed: Full Exploit & PoC Published

Do Son October 10, 2024 0

The researcher published a proof of concept to exploit CVE-2024-9465 (CVSS 9.2) on vulnerable Palo Alto Networks’ Expedition devices.

Zyxel Devices Targeted by Malicious Actors: Urgent Firmware Update Required Zyxel security - Mitel MiCollab Vulnerability
  • Vulnerability

Zyxel Devices Targeted by Malicious Actors: Urgent Firmware Update Required

Do Son October 10, 2024 0

Protect your Zyxel security appliances from malicious activity. Stay up-to-date with firmware updates and secure your network against unauthorized access.

CVE-2024-41713 (CVSS 9.8): Unpatched MiCollab Vulnerability Allows Unauthorized Access Mitel MiCollab SQL Injection MiCollab software - CVE-2024-47223 & CVE-2024-41713
  • Vulnerability

CVE-2024-41713 (CVSS 9.8): Unpatched MiCollab Vulnerability Allows Unauthorized Access

Do Son October 10, 2024 0

Mitel's MiCollab platform at risk: Understand the severity of the CVE-2024-41713 vulnerability and the unauthorized access it can enable.

Progress Patches Critical Security Flaw CVE-2024-8015 (CVSS 9.1) in Telerik Report Server CVE-2023-42659 & CVE-2024-8015 MOVEit AS2 DoS, Uncontrolled Resource Consumption
  • Vulnerability

Progress Patches Critical Security Flaw CVE-2024-8015 (CVSS 9.1) in Telerik Report Server

Do Son October 10, 2024 0

Protect your organization from risks: Check out the important security advisory on Telerik Report Server's flaws, including CVE-2024-8015.

AsyncRAT Malware Campaign Exploits Bitbucket to Deliver Multi-Stage Attack AsyncRAT analysis
  • Malware

AsyncRAT Malware Campaign Exploits Bitbucket to Deliver Multi-Stage Attack

Do Son October 10, 2024 0

Uncover the details of a sophisticated AsyncRAT campaign utilizing Bitbucket. Learn how attackers distributed malicious payloads and evaded detection.

Keycloak Patches CVE-2024-3656 Granting Low-Privilege Users Administrative Access CVE-2024-3656
  • Vulnerability

Keycloak Patches CVE-2024-3656 Granting Low-Privilege Users Administrative Access

Do Son October 10, 2024 0

Learn about the high-severity vulnerability in Keycloak (CVE-2024-3656) that allows unauthorized access to administrative functions.

OpenAI Disrupts 20+ Malicious Operations, Including Election Interference and Malware Development SweetSpecter
  • Cyber Security

OpenAI Disrupts 20+ Malicious Operations, Including Election Interference and Malware Development

Do Son October 10, 2024 0

Uncover the tactics used by threat actors in cyberattacks and disinformation campaigns. Read OpenAI's report on combating AI misuse.

CVE-2024-38365: Btcd Bug Could Have Led to Bitcoin Network Fork CVE-2024-38365
  • Vulnerability

CVE-2024-38365: Btcd Bug Could Have Led to Bitcoin Network Fork

Do Son October 10, 2024 0

Discover the critical vulnerability CVE-2024-38365 in btcd, an alternative Bitcoin implementation, that could have led to a hard fork of the blockchain.

Telekopye Expands to Target Tourists via Hotel Booking Scam Telekopye scam toolkit
  • Cyber Security

Telekopye Expands to Target Tourists via Hotel Booking Scam

Do Son October 10, 2024 0

Discover the evolution of the Telekopye scam toolkit: from targeting online marketplace users to exploiting tourists via accommodation booking platforms.

The Future of Cloud Security: Automation Strategies and Techniques Cloud Security
  • Technique

The Future of Cloud Security: Automation Strategies and Techniques

Do Son October 10, 2024 0

Stay ahead of the game with cloud security automation. Explore the benefits of using automation tools to detect and respond to threats in real time.

CVE-2024-9466 Flaw in Palo Alto Networks’ Expedition Exposes Sensitive Credentials to Attackers, PoC Published CVE-2024-9466
  • Vulnerability

CVE-2024-9466 Flaw in Palo Alto Networks’ Expedition Exposes Sensitive Credentials to Attackers, PoC Published

Do Son October 10, 2024 0

Critical vulnerability in Palo Alto Networks' Expedition tool (CVE-2024-9466) could expose sensitive credentials to authenticated attackers.

CVE-2024-47223 (CVSS 9.4): SQLi Flaw in Mitel MiCollab Poses Severe Risk to Enterprises Mitel MiCollab SQL Injection MiCollab software - CVE-2024-47223 & CVE-2024-41713
  • Vulnerability

CVE-2024-47223 (CVSS 9.4): SQLi Flaw in Mitel MiCollab Poses Severe Risk to Enterprises

Do Son October 10, 2024 0

Mitel warns of high-severity SQL injection vulnerability (CVE-2024-47223) in MiCollab software. Find out about the potential impacts it could have on system security and corporate collaboration.

Internet Archive Under Siege: DDoS Attacks and a Mysterious Data Breach Internet Archive Data Breach
  • Cyber Security
  • Data Leak

Internet Archive Under Siege: DDoS Attacks and a Mysterious Data Breach

Do Son October 9, 2024 0

Discover the shocking details of the Internet Archive data breach: 31 million user records compromised and dumped online.

CVE-2024-9164 (CVSS 9.6): GitLab Users Urged to Update Now CVE-2024-9164 - CVE-2025-0376 GitLab Wiki XSS, Session Hijack Flaw
  • Vulnerability

CVE-2024-9164 (CVSS 9.6): GitLab Users Urged to Update Now

Do Son October 9, 2024 0

Stay secure with GitLab's latest security updates. Learn about crucial patches that address flaws, including the critical CVE-2024-9164.
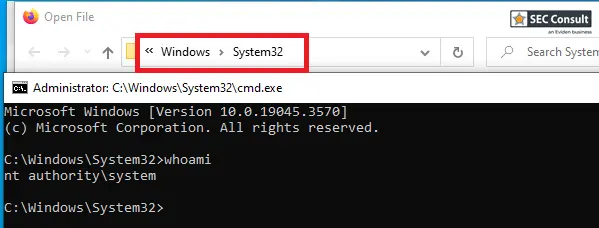
Researcher Details Privilege Escalation in Palo Alto Networks’ GlobalProtect MSI Installer (CVE-2024-9473) CVE-2024-9473
  • Vulnerability

Researcher Details Privilege Escalation in Palo Alto Networks’ GlobalProtect MSI Installer (CVE-2024-9473)

Do Son October 9, 2024 0

Learn about the recently discovered local privilege escalation vulnerability (CVE-2024-9473) affecting Palo Alto Networks' GlobalProtect software.

OpenBAS: A Powerful Open-Source Platform for Cyber Adversary Simulations Cyber Adversary Simulations
  • Open Source Tool

OpenBAS: A Powerful Open-Source Platform for Cyber Adversary Simulations

Do Son October 9, 2024 0

OpenBAS is an open-source platform aimed at providing organizations with the ability to plan and execute detailed cyber adversary simulations

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-76954CVSS 9.8
    An improper neutralization of special elements used in an SQL command vulnerability in the Auth API in Synology...
    📅 Updated: Nov 10, 2026
  • CVE-2026-91241CVSS 9.1
    Vulnerability in the Oracle Business Intelligence Enterprise Edition product of Oracle Analytics (component: Analytics Web Administration). Supported versions...
    📅 Updated: Nov 10, 2026
  • CVE-2026-121683CVSS 9.4
    Missing authentication in Ivanti Cloud Services Application version 5.0.8 allows a remote unauthenticated attacker to add and delete...
    📅 Updated: Nov 10, 2026
  • CVE-2026-83283CVSS 9.8
    Vulnerability in the Oracle Business Intelligence Enterprise Edition product of Oracle Analytics (component: Platform Security). The supported version...
    📅 Updated: Nov 10, 2026
  • CVE-2026-108186CVSS 9.6
    Improper Input Validation in Zoom Workplace for Windows may allow an unauthenticated user to conduct an escalation of...
    📅 Updated: Nov 10, 2026
  • CVE-2026-121653CVSS 9.8
    SQL injection in the Core of Ivanti Endpoint Manager before version 2024 SU8 allows a remote unauthenticated attacker...
    📅 Updated: Nov 10, 2026
  • CVE-2026-125758CVSS 9.1
    Aptabase before commit 61d4c01 contains an authentication bypass vulnerability that allows unauthenticated attackers to forge sign-in links by...
    📅 Updated: Nov 10, 2026
  • CVE-2026-125757CVSS 9.4
    mailcow: dockerized before 2026-11 contains a server-side template injection vulnerability that allows domain administrators to execute commands in...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.