2024 US Election Faces Escalating Iranian Cyber Influence, MTAC Warns Cyber Security 2024 US Election Faces Escalating Iranian Cyber Influence, MTAC Warns Do Son August 10, 2024 0 Read More Read more about 2024 US Election Faces Escalating Iranian Cyber Influence, MTAC Warns
Nexera Hacked: $1.8 Million Stolen from Tokenization Giant Cyber Security Nexera Hacked: $1.8 Million Stolen from Tokenization Giant Do Son August 9, 2024 0 Read More Read more about Nexera Hacked: $1.8 Million Stolen from Tokenization Giant
Wazuh: A Comprehensive Open-Source Platform for Threat Detection and Response Open Source Tool Wazuh: A Comprehensive Open-Source Platform for Threat Detection and Response Do Son August 9, 2024 0 Read More Read more about Wazuh: A Comprehensive Open-Source Platform for Threat Detection and Response
Django Releases Security Updates to Address Critical Flaw (CVE-2024-42005, CVSS 9.8) Vulnerability Django Releases Security Updates to Address Critical Flaw (CVE-2024-42005, CVSS 9.8) Do Son August 9, 2024 0 Read More Read more about Django Releases Security Updates to Address Critical Flaw (CVE-2024-42005, CVSS 9.8)
GoGra: New Go-Based Backdoor Targets South Asian Media Cyber Security Malware GoGra: New Go-Based Backdoor Targets South Asian Media Do Son August 9, 2024 0 Read More Read more about GoGra: New Go-Based Backdoor Targets South Asian Media
Team82 Unveils Research on Unitronics PLC/HMI Attacks Targeting Critical Infrastructure Vulnerability Team82 Unveils Research on Unitronics PLC/HMI Attacks Targeting Critical Infrastructure Do Son August 9, 2024 0 Read More Read more about Team82 Unveils Research on Unitronics PLC/HMI Attacks Targeting Critical Infrastructure
Windows Smart App Control, SmartScreen Vulnerable to Exploits Vulnerability Windows Smart App Control, SmartScreen Vulnerable to Exploits Do Son August 9, 2024 0 Read More Read more about Windows Smart App Control, SmartScreen Vulnerable to Exploits
Department of Justice Disrupts North Korean IT Worker Fraud Scheme with Arrest of Nashville Resident Cyber Security Department of Justice Disrupts North Korean IT Worker Fraud Scheme with Arrest of Nashville Resident Do Son August 9, 2024 0 Read More Read more about Department of Justice Disrupts North Korean IT Worker Fraud Scheme with Arrest of Nashville Resident
SSHamble: runZero’s Open Source Tool to Secure Your SSH Implementations Vulnerability SSHamble: runZero’s Open Source Tool to Secure Your SSH Implementations Do Son August 9, 2024 0 Read More Read more about SSHamble: runZero’s Open Source Tool to Secure Your SSH Implementations
Beware: Hackers Use Google Drawings & WhatsApp Links to Steal Data Cyber Security Beware: Hackers Use Google Drawings & WhatsApp Links to Steal Data Do Son August 9, 2024 0 Read More Read more about Beware: Hackers Use Google Drawings & WhatsApp Links to Steal Data
Exploitable PoC Released for CVE-2024-38077: 0-Click RCE Threatens All Windows Servers Vulnerability Exploitable PoC Released for CVE-2024-38077: 0-Click RCE Threatens All Windows Servers Do Son August 8, 2024 0 Read More Read more about Exploitable PoC Released for CVE-2024-38077: 0-Click RCE Threatens All Windows Servers
CVE-2024-5290: Wi-Fi Flaw Leaves Millions Vulnerable to Root Takeover Vulnerability CVE-2024-5290: Wi-Fi Flaw Leaves Millions Vulnerable to Root Takeover Do Son August 8, 2024 0 Read More Read more about CVE-2024-5290: Wi-Fi Flaw Leaves Millions Vulnerable to Root Takeover
MongoDB Patches High-Severity Windows Vulnerability (CVE-2024-7553) in Multiple Products Vulnerability MongoDB Patches High-Severity Windows Vulnerability (CVE-2024-7553) in Multiple Products Do Son August 8, 2024 0 Read More Read more about MongoDB Patches High-Severity Windows Vulnerability (CVE-2024-7553) in Multiple Products
1Password Updates macOS App to Fix Vulnerabilities CVE-2024-42218 and CVE-2024-42219 Vulnerability 1Password Updates macOS App to Fix Vulnerabilities CVE-2024-42218 and CVE-2024-42219 Do Son August 8, 2024 0 Read More Read more about 1Password Updates macOS App to Fix Vulnerabilities CVE-2024-42218 and CVE-2024-42219
ATLAS LION Cybercriminal Group Persists in Targeting Gift Card Issuing Systems Cyber Security ATLAS LION Cybercriminal Group Persists in Targeting Gift Card Issuing Systems Do Son August 8, 2024 0 Read More Read more about ATLAS LION Cybercriminal Group Persists in Targeting Gift Card Issuing Systems
Trojan Malware Infiltrates Browser Extensions, Impacts 300,000 Users Malware Trojan Malware Infiltrates Browser Extensions, Impacts 300,000 Users Do Son August 8, 2024 0 Read More Read more about Trojan Malware Infiltrates Browser Extensions, Impacts 300,000 Users
CVE-2024-42458 (CVSS 9.8) – New Security Vulnerability in Neat VNC: Urgent Patch Released Vulnerability CVE-2024-42458 (CVSS 9.8) – New Security Vulnerability in Neat VNC: Urgent Patch Released Do Son August 8, 2024 0 Read More Read more about CVE-2024-42458 (CVSS 9.8) – New Security Vulnerability in Neat VNC: Urgent Patch Released
South Korea Reports: 8,400 North Koreans in Cyber Warfare Operations Cyber Security South Korea Reports: 8,400 North Koreans in Cyber Warfare Operations Do Son August 8, 2024 0 Read More Read more about South Korea Reports: 8,400 North Koreans in Cyber Warfare Operations
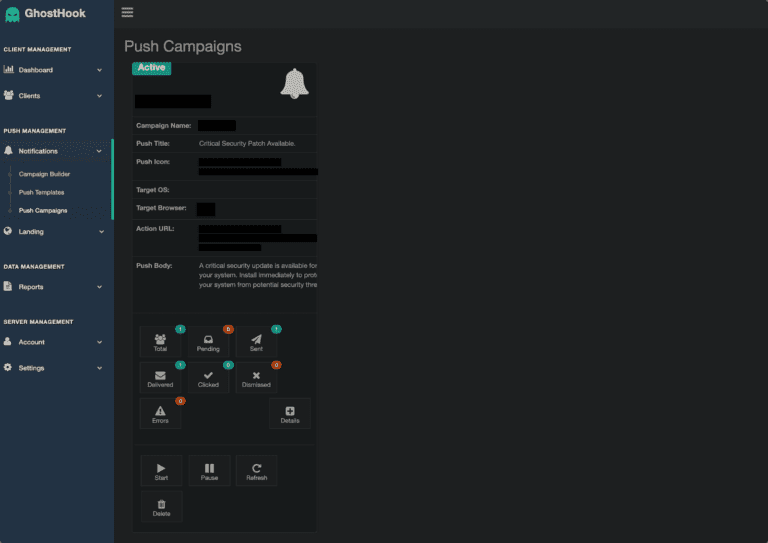
GhostHook Framework: A New Fileless Malware Threatens Android Devices Malware GhostHook Framework: A New Fileless Malware Threatens Android Devices Do Son August 8, 2024 0 Read More Read more about GhostHook Framework: A New Fileless Malware Threatens Android Devices
Cisco Warns of Public PoC Exploit Code of Critical CVE-2024-20419 (CVSS 10) Flaw Vulnerability Cisco Warns of Public PoC Exploit Code of Critical CVE-2024-20419 (CVSS 10) Flaw Do Son August 8, 2024 0 Read More Read more about Cisco Warns of Public PoC Exploit Code of Critical CVE-2024-20419 (CVSS 10) Flaw
HPE Aruba Networking Addresses Severe Vulnerabilities in Access Points Vulnerability HPE Aruba Networking Addresses Severe Vulnerabilities in Access Points Do Son August 8, 2024 0 Read More Read more about HPE Aruba Networking Addresses Severe Vulnerabilities in Access Points
CrowdStrike Identifies Root Cause of Massive Windows Outage Technology CrowdStrike Identifies Root Cause of Massive Windows Outage Do Son August 8, 2024 0 Read More Read more about CrowdStrike Identifies Root Cause of Massive Windows Outage

 Do Son