Skip to content
November 11, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Evil Corp Cybercriminals Exposed: UK Sanctions 16 Individuals Linked to Russian State and LockBit Evil Corp
  • Cyber Security
  • Malware

Evil Corp Cybercriminals Exposed: UK Sanctions 16 Individuals Linked to Russian State and LockBit

Do Son October 2, 2024 0

Learn how the United Kingdom is taking action against Evil Corp, a notorious cybercrime group linked to the Russian state and other ransomware groups.
Cybersecurity Threats Skyrocket in Hong Kong: Fraud, Phishing, and Malware Take Center Stage BiDi Swap, phishing attacks Cybersecurity Threats
  • Cyber Security

Cybersecurity Threats Skyrocket in Hong Kong: Fraud, Phishing, and Malware Take Center Stage

Do Son October 2, 2024 0

Discover the alarming rise of cyber threats in Hong Kong. Find out about the most common types of attacks and how to safeguard your online security.

Microsoft Defender Introduces VPN to Secure Public Wi-Fi Connections Defender VPN
  • Windows

Microsoft Defender Introduces VPN to Secure Public Wi-Fi Connections

Do Son October 1, 2024 0

Protect your data on public Wi-Fi networks with Defender VPN. Learn how Microsoft's updated Defender features keep you safe while connected on the go.

PoC Exploit Releases for Zimbra RCE Flaw CVE-2024-45519: Mass Exploitation Detected CVE-2024-45519 PoC exploit
  • Vulnerability

PoC Exploit Releases for Zimbra RCE Flaw CVE-2024-45519: Mass Exploitation Detected

Do Son October 1, 2024 0

Security researcher Kalana Damsas has published a Python script on GitHub that simplifies the process of exploiting the CVE-2024-45519 flaw

Microarchitectural Control-flow Integrity (μCFI): Thwarting Timing & Hijacking Attacks Microarchitectural Control-flow Integrity - μCFI
  • Vulnerability

Microarchitectural Control-flow Integrity (μCFI): Thwarting Timing & Hijacking Attacks

Do Son October 1, 2024 0

Discover how Microarchitectural Control-flow Integrity (μCFI) can protect CPU control flows from timing-based and hijacking attacks.

CVE-2024-8940 (CVSS 10): Critical Flaw in Scriptcase Low-Code Platform Leaves Developers at Risk CVE-2024-8940 - Scriptcase
  • Vulnerability

CVE-2024-8940 (CVSS 10): Critical Flaw in Scriptcase Low-Code Platform Leaves Developers at Risk

Do Son October 1, 2024 0

Critical security vulnerabilities discovered in Scriptcase! Update now to protect your applications from potential remote code execution.

Stealthy Cyberattack Turns Visual Studio Code into a Remote Access Tool Visual Studio Code
  • Malware

Stealthy Cyberattack Turns Visual Studio Code into a Remote Access Tool

Do Son October 1, 2024 0

Uncover the advanced cyberattack that exploits Visual Studio Code for unauthorized remote access. Stay informed and safeguard your systems.

CVE-2024-9194: SQLi Flaw Discovered in Octopus Server, Urgent Patch Recommended Octopus Deploy - CVE-2024-9194
  • Vulnerability

CVE-2024-9194: SQLi Flaw Discovered in Octopus Server, Urgent Patch Recommended

Do Son October 1, 2024 0

Critical security update for Octopus Deploy: Learn about the severe flaw (CVE-2024-9194) and how to address it to protect your project data.

Roblox Cheaters Targeted: Skuld Stealer and Blank Grabber Malware Lurks in PyPI Packages Skuld Stealer & Blank Grabber
  • Malware

Roblox Cheaters Targeted: Skuld Stealer and Blank Grabber Malware Lurks in PyPI Packages

Do Son October 1, 2024 0

Protect yourself from Skuld Stealer & Blank Grabber: two dangerous malware that exploits Roblox players using cheats and mods for an unfair advantage

CVE-2024-47070: Critical Flaw in authentik Identity Provider Allows Authentication Bypass authentik CVE-2024-47070
  • Vulnerability

CVE-2024-47070: Critical Flaw in authentik Identity Provider Allows Authentication Bypass

Do Son October 1, 2024 0

Get insights into the security flaw in authentik. Explore the details of CVE-2024-47070 and understand the impact on identity management and authentication solutions.

XWorm Unveils Stealthier Techniques in Latest Malware Evolution XWorm RAT
  • Malware

XWorm Unveils Stealthier Techniques in Latest Malware Evolution

Do Son October 1, 2024 0

Discover the latest evasive techniques and capabilities of XWorm, a sophisticated and multifaceted malware identified in 2022.
AFP Under Cyberattack: News Delivery Disrupted, Investigation Underway Operation IconCat, UNG0801 AFP cyberattack -NetWalker Ransomware VShell RAT
  • Cyber Security

AFP Under Cyberattack: News Delivery Disrupted, Investigation Underway

Do Son September 30, 2024 0

Learn about the recent cyberattack on AFP. Find out how the agency is handling the breach and ensuring the security of its operations.

Researcher Details RCE Flaw (CVE-2024-36435) in Supermicro BMC IPMI Firmware Supermicro
  • Vulnerability

Researcher Details RCE Flaw (CVE-2024-36435) in Supermicro BMC IPMI Firmware

Do Son September 30, 2024 0

Discover the critical vulnerability in Supermicro enterprise products: CVE-2024-36435 exposes organizations to security risks and allows remote code execution.

CISA Adds Four Actively Exploited Vulnerabilities to KEV Catalog CVE-2023-25280
  • Vulnerability

CISA Adds Four Actively Exploited Vulnerabilities to KEV Catalog

Do Son September 30, 2024 0

Stay protected from cyber threats with patching and mitigation efforts. Learn about the critical vulnerability CVE-2023-25280 in D-Link routers.
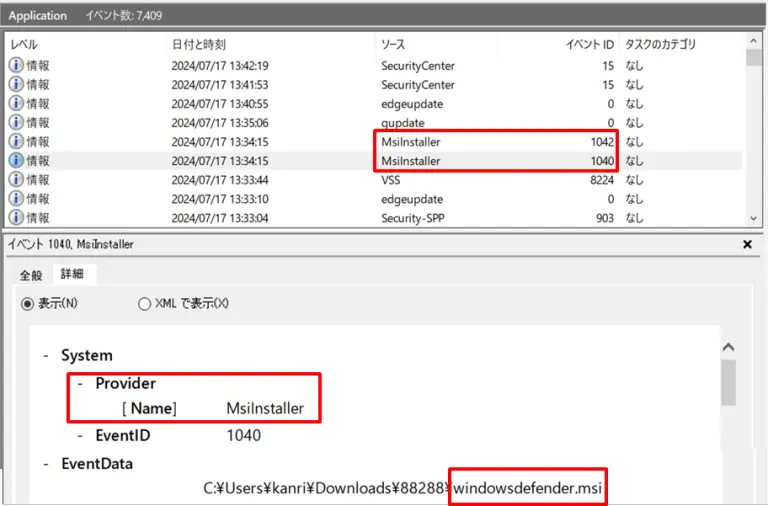
Windows Event Logs: A Key to Unmasking Human-Operated Ransomware Windows Event Logs
  • Malware

Windows Event Logs: A Key to Unmasking Human-Operated Ransomware

Do Son September 30, 2024 0

Discover how Windows Event Logs can be a powerful tool in the fight against human-operated ransomware. Learn how to detect and mitigate these evolving threats.
KartLANPwn (CVE-2024-45200) Exploits Mario Kart 8 Deluxe LAN Play Feature for RCE KartLANPwn (CVE-2024-45200) - Mario Kart 8 Deluxe
  • Vulnerability

KartLANPwn (CVE-2024-45200) Exploits Mario Kart 8 Deluxe LAN Play Feature for RCE

Do Son September 30, 2024 0

A recently discovered vulnerability, dubbed "KartLANPwn" (CVE-2024-45200), has put Mario Kart 8 Deluxe players at risk of RCE

Hadooken & K4Spreader Malware: 8220 Gang’s Latest Cloud Hijacking Tools K4Spreader malware
  • Cyber Security
  • Malware

Hadooken & K4Spreader Malware: 8220 Gang’s Latest Cloud Hijacking Tools

Do Son September 30, 2024 0

Stay informed about the evolving tactics of the 8220 Gang. Read about the new K4Spreader & Hadooken malware that targets cloud environments for cryptomining.

PLANET Technology Switches Face CVE-2024-8456 (CVSS 9.8), Urgent Firmware Updates Advised CVE-2025-9971 CVE-2025-9972 PLANET Technology - CVE-2024-8456
  • Vulnerability

PLANET Technology Switches Face CVE-2024-8456 (CVSS 9.8), Urgent Firmware Updates Advised

Do Son September 30, 2024 0

Stay informed about critical vulnerabilities affecting PLANET Technology switch models. Learn about the risks and potential impacts.
Transparent Tribe APT Group’s New Arsenal: Mythic Poseidon, Linux, and C2 Takedown Transparent Tribe APT
  • Cyber Security

Transparent Tribe APT Group’s New Arsenal: Mythic Poseidon, Linux, and C2 Takedown

Do Son September 30, 2024 0

Uncover the activities of Transparent Tribe APT group and their new tactics of espionage. Learn how they target Indian government officials and defense sectors.

CVE-2024-22170 (CVSS 9.2): Western Digital Addresses Critical Flaw in My Cloud Devices My Cloud OS 5 - CVE-2024-22170
  • Vulnerability

CVE-2024-22170 (CVSS 9.2): Western Digital Addresses Critical Flaw in My Cloud Devices

Do Son September 30, 2024 0

Ensure the security of your Western Digital My Cloud devices. Learn about CVE-2024-22170 which could lead to unauthorized access and data breaches.

Rhadamanthys Evolves: AI-Powered Crypto Theft with Version 0.7.0 Rhadamanthys version 0.7.0
  • Malware

Rhadamanthys Evolves: AI-Powered Crypto Theft with Version 0.7.0

Do Son September 30, 2024 0

Discover the powerful new features of Rhadamanthys Stealer version 0.7.0: weaponized AI and OCR technology for advanced data theft.

Can Telecoms Fraud Be Eliminated? pbx
  • Technique

Can Telecoms Fraud Be Eliminated?

Do Son September 30, 2024 0

Telecoms fraud features prominently on Interpol’s crime lists and is a worldwide, recognised cybercrime. But can fraud be eliminated?

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-20320CVSS 7.5
    A vulnerability in the Open Client Interface (OCI) XML Parser of Cisco BroadWorks could allow an unauthenticated, remote...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111560CVSS 8.6
    Improper neutralization of shell metacharacters in the timezone configuration field in certain Barracuda appliance products using common Barracuda...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-124194CVSS 6.5
    Product ui does not warn user of unsafe actions in Microsoft Office Outlook allows an unauthorized attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-126259CVSS 9.0
    Missing authentication for critical function in FortiOS
    📅 Updated: Nov 10, 2026
  • CVE-2026-126262CVSS 9.3
    Improper neutralization of special elements used in an SQL command in FortiManager
    📅 Updated: Nov 10, 2026
  • CVE-2026-126260CVSS 9.0
    Server side request forgery vulnerability in FortiAnalyzer, FortiManager with FortiAnalyzer features & FortiAnalyzer-BigData
    📅 Updated: Nov 10, 2026
  • CVE-2026-126170CVSS 9.8
    Unauthenticated RCE in multiple products
    📅 Updated: Nov 10, 2026
  • CVE-2026-126261CVSS 9.0
    Improper authorizatin vulnerability in FortiManager
    📅 Updated: Nov 10, 2026
  • CVE-2026-126187CVSS 9.5
    React is a JavaScript library for building user interfaces. From 19.0.0 until 19.0.9, 19.1.10, 19.2.9, and 19.3.1, the...
    📅 Updated: Nov 10, 2026
  • CVE-2026-126229CVSS 9.1
    Authorization Bypass in FortiManager, FortiAnalyzer, FortiManager Cloud and FortiAnalyzer Cloud
    📅 Updated: Nov 10, 2026
  • CVE-2026-126253CVSS 9.3
    OSPF Authentication Bypass in multiple product
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.