
Skip to content
November 11, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Compromised Credentials: New Cyberattack Exploits Industry Email Accounts LokiBot Steganography, .NET Loader PlugX malware YiBackdoor, ransomware
  • Malware

Compromised Credentials: New Cyberattack Exploits Industry Email Accounts

Do Son September 24, 2024 0

Transport and logistics companies in North America targeted in a sophisticated cyberattack. Learn about the tactics used and how to protect your business.

RansomHub’s EDR-Killer: How Zerologon and EDRKillShifter Exploit Networks Without Detection RansomHub EDRKillShifter
  • Malware

RansomHub’s EDR-Killer: How Zerologon and EDRKillShifter Exploit Networks Without Detection

Do Son September 24, 2024 0

Explore the sophisticated tactics of RansomHub ransomware and their use of EDRKillShifter. Discover how this tool enables them to evade detection and disable antivirus solutions.

CISA Warns of Actively Exploited Ivanti vTM Flaw CVE-2024-7593 (CVSS 9.8), PoC Published Ivanti vTM
  • Vulnerability

CISA Warns of Actively Exploited Ivanti vTM Flaw CVE-2024-7593 (CVSS 9.8), PoC Published

Do Son September 24, 2024 0

Actively exploited vulnerability in Ivanti vTM puts organizations at risk. Take immediate action to secure your systems.

Revolutionising AdTech: 0→1 Product Innovation at Evido Ragic Enterprise Cloud Database - CVE-2024-9983 - CVE-2024-9984 - CVE-2024-9985
  • Technique

Revolutionising AdTech: 0→1 Product Innovation at Evido

Dan Agbo September 24, 2024
Evido’s Emergence in CIS Digital Advertising September 2024 – Evido has rapidly positioned itself as a noteworthy...
Read More Read more about Revolutionising AdTech: 0→1 Product Innovation at Evido
Severe Unauthenticated RCE Flaw (CVSS 9.9) in GNU/Linux Systems Awaiting Full Disclosure Linux Vulnerability
  • Linux
  • Vulnerability

Severe Unauthenticated RCE Flaw (CVSS 9.9) in GNU/Linux Systems Awaiting Full Disclosure

Do Son September 23, 2024 0

Stay up to date with the latest news on a critical Linux vulnerability. Learn about its severity, impact, and ongoing efforts to find a fix.
Researcher Details CVE-2024-20439 (CVSS 9.8) Flaw in Cisco Smart Licensing Utility Smart Licensing Utility
  • Vulnerability

Researcher Details CVE-2024-20439 (CVSS 9.8) Flaw in Cisco Smart Licensing Utility

Do Son September 23, 2024 0

Unveiling the details of CVE-2024-20439: a severe vulnerability affecting Cisco's Smart Licensing Utility (CSLU).

CVE-2024-9043 (CVSS 9.8): Cellopoint Secure Email Gateway Flaw Puts Sensitive Data at Risk Fortra BoKS vulnerability OS command injection, CVE-2026-9862 Altium Enterprise Server Vulnerability CVE-2026-9129 Path Traversal Patreon OAuth Vulnerability Identity Collision DRC INSIGHT Vulnerability Exam Data Hijacking Horner Automation PLC Industrial Brute Force Honeywell IQ4x Vulnerability CVE-2026-3611 DJI Romo vacuum security flaw Python Cryptography Vulnerability CVE-2026-26007 Open5GS Vulnerability CVE-2026-0622 Vivotek IP7137 Vulnerabilities CVE-2025-66049 Forcepoint DLP Vulnerability CVE-2025-14026 Cellopoint Secure Email Gateway - CVE-2024-9043
  • Vulnerability

CVE-2024-9043 (CVSS 9.8): Cellopoint Secure Email Gateway Flaw Puts Sensitive Data at Risk

Do Son September 23, 2024 0

Discover the severity and potential impact of the recently disclosed vulnerability (CVE-2024-9043) in Cellopoint's Secure Email Gateway

CVE-2024-38286: Denial-of-Service Vulnerability Discovered in Apache Tomcat Apache Tomcat, Brute-Force Attacks CVE-2024-38286 - Apache Tomcat 11
  • Vulnerability

CVE-2024-38286: Denial-of-Service Vulnerability Discovered in Apache Tomcat

Do Son September 23, 2024 0

Learn about the newly discovered vulnerability in Apache Tomcat (CVE-2024-38286) and how it can lead to denial-of-service attacks.
CVE-2024-47062 (CVSS 9.4): Flaws Discovered in Navidrome Music Server Expose Sensitive Data Navidrome - CVE-2024-47062
  • Vulnerability

CVE-2024-47062 (CVSS 9.4): Flaws Discovered in Navidrome Music Server Expose Sensitive Data

Do Son September 23, 2024 0

CVE-2024-47062 was discovered in Navidrome, a popular open-source music streaming server. Learn about the risks and potential exploits.

Information Stealer Alert: Lumma Strikes Again with Go-Based Injector Go Injector
  • Malware

Information Stealer Alert: Lumma Strikes Again with Go-Based Injector

Do Son September 23, 2024 0

Uncover the tactics of cybercriminals using a Go-based Injector and Lumma Stealer. Learn how they exploit vulnerabilities to access and exfiltrate valuable data.

ENISA Calls for Urgent Action as EU Cyberattacks Reach Record High Apple Google EU alliance DMA European Commission Breach Trivy Supply Chain Attack Europa.eu Breach EU Cloud Infrastructure EU Cyber Sanctions State-Sponsored Hacking EU 2040 Emissions Target, Europe Climate Leadership AWS Azure DMA Cloud Gatekeeper DSA violation, illegal content Apple DMA Delay, iPhone Mirroring EU EU Age Verification, Google Play Integrity Corning Antitrust, EU Competition Apple EU Digital Markets Act App Store commission European Union cyberattacks - InvestAI EU Targets Musk’s X Digital Markets Act, EU fines
  • Cyber Security
  • Malware
  • Vulnerability

ENISA Calls for Urgent Action as EU Cyberattacks Reach Record High

Do Son September 23, 2024 0

Uncover the latest cyber threats targeting the European Union. From DDoS attacks to ransomware, gain insights into the challenges faced by the EU.

CVE-2024-8956 (CVSS 9.1): PTZOptics Cameras Vulnerable to Remote Attacks KMW CCTV vulnerability unauthenticated password reset Xiongmai IP Camera Vulnerability CVE-2025-65856 CVE-2024-8956 (CVSS 9.1): PTZOptics Cameras
  • Vulnerability

CVE-2024-8956 (CVSS 9.1): PTZOptics Cameras Vulnerable to Remote Attacks

Do Son September 23, 2024 0

Discover the severity of the CVE-2024-8956 security flaw in PTZOptics Cameras. Find out how it exposes sensitive data and allows unauthorized access.
New Necro Trojan Targets Over 11 Million Android Devices Through Google Play and Unofficial Apps Necro Trojan
  • Malware

New Necro Trojan Targets Over 11 Million Android Devices Through Google Play and Unofficial Apps

Do Son September 23, 2024 0

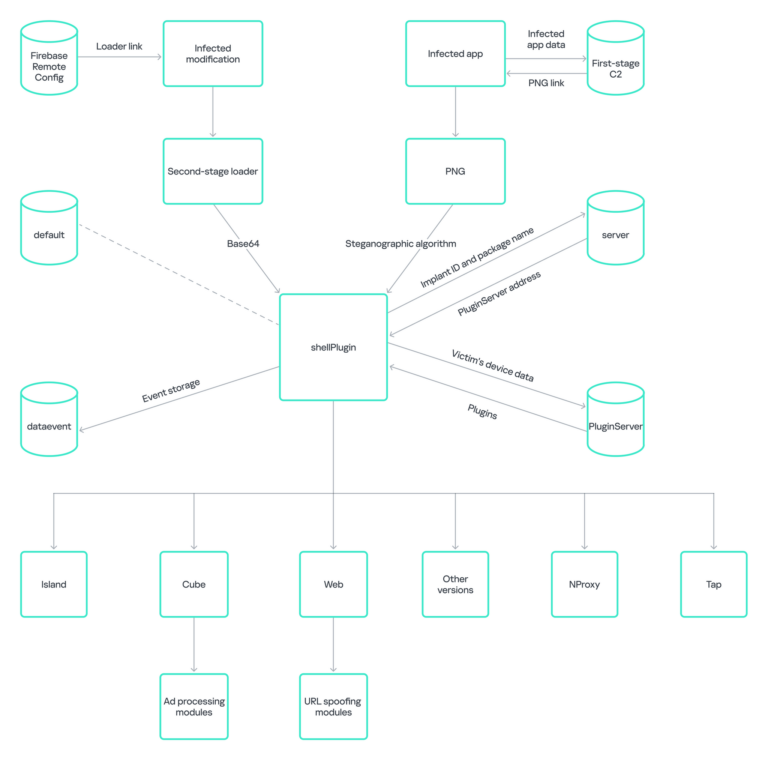
Stay informed about the latest Android threat: the Necro Trojan. Discover how this multi-stage malware is infecting millions of devices worldwide.

What is Cybersecurity Risk? BlackByte Ransomware Group
  • Technique

What is Cybersecurity Risk?

Do Son September 23, 2024 0

Understand the nature and implications of cybersecurity risk for businesses. Learn effective strategies for managing and mitigating cyber threats.

BingX Suffers $44 Million Cyberattack, Highlighting Web3 Security Concerns BingX cyberattack FortiGate SSO Attacks Firewall Config Theft
  • Cyber Security

BingX Suffers $44 Million Cyberattack, Highlighting Web3 Security Concerns

Do Son September 23, 2024 0

BingX, a Singapore-based cryptocurrency exchange, suffers $44 million security breach. Learn about the incident and its impact on the DeFi industry.
WordPress Theme ‘Houzez’ and Associated Plugin Vulnerabilities Expose Thousands of Sites Houzez theme - CVE-2024-22303 and CVE-2024-21743
  • Vulnerability

WordPress Theme ‘Houzez’ and Associated Plugin Vulnerabilities Expose Thousands of Sites

Do Son September 23, 2024 0

Critical vulnerabilities discovered in the widely-used WordPress theme Houzez and its companion plugin. Take action to secure your website now.
Qualcomm’s Bold Move: Intel Acquisition Bid Faces Antitrust Hurdle Qualcomm acquisition Intel
  • Technology

Qualcomm’s Bold Move: Intel Acquisition Bid Faces Antitrust Hurdle

Do Son September 22, 2024 0

Rumors swirl around Qualcomm's potential acquisition of Intel's chip design division. Learn about the latest developments and potential implications.

Windows Server Update Services Deprecation: What It Means for Your Update Strategy Windows Server Update Services
  • Windows

Windows Server Update Services Deprecation: What It Means for Your Update Strategy

Do Son September 22, 2024 0

Discover the future of Windows Server Update Services (WSUS) and its deprecation by Microsoft. Stay informed on the latest developments.

FreeBSD Issues Critical Security Advisory for CVE-2024-41721 (CVSS 9.8) CVE-2024-41721 - FreeBSD FreeBSD RCE, IPv6 Router Advertisement
  • Vulnerability

FreeBSD Issues Critical Security Advisory for CVE-2024-41721 (CVSS 9.8)

Do Son September 22, 2024 0

Learn about the high severity vulnerability CVE-2024-41721 in FreeBSD's bhyve hypervisor and how it can be exploited.

CVE-2024-7490: Urgent Warning for IoT Devices Using Microchip ASF, No Patch Available tinydhcp server - CVE-2024-7490
  • Vulnerability

CVE-2024-7490: Urgent Warning for IoT Devices Using Microchip ASF, No Patch Available

Do Son September 22, 2024 0

Discover the critical security flaw in the Microchip ASF's tinydhcp server. Uncover the risks it poses to IoT devices and the lack of available patch.
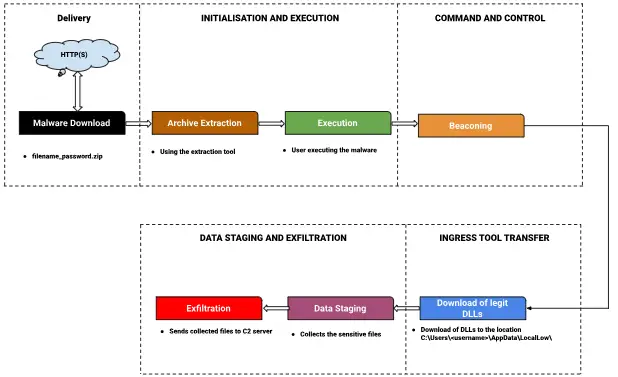
RecordStealer: A Case Study in the Persistent Threat of Info-Stealing Malware RECORDSTEALER
  • Malware

RecordStealer: A Case Study in the Persistent Threat of Info-Stealing Malware

Do Son September 22, 2024 0

Learn about the dangerous RECORDSTEALER malware and its impact on user data. Stay informed and protect your sensitive information.

Critical Dragonfly2 Flaw CVE-2023-27584: Hardcoded Key Threatens Admin Access Dragonfly2
  • Vulnerability

Critical Dragonfly2 Flaw CVE-2023-27584: Hardcoded Key Threatens Admin Access

Do Son September 22, 2024 0

Discover the critical security flaw in Dragonfly2, an open-source file distribution system. Learn how CVE-2023-27584 can lead to unauthorized access and devastating attacks.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-20320CVSS 7.5
    A vulnerability in the Open Client Interface (OCI) XML Parser of Cisco BroadWorks could allow an unauthenticated, remote...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111560CVSS 8.6
    Improper neutralization of shell metacharacters in the timezone configuration field in certain Barracuda appliance products using common Barracuda...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-124194CVSS 6.5
    Product ui does not warn user of unsafe actions in Microsoft Office Outlook allows an unauthorized attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-126259CVSS 9.0
    Missing authentication for critical function in FortiOS
    📅 Updated: Nov 10, 2026
  • CVE-2026-126262CVSS 9.3
    Improper neutralization of special elements used in an SQL command in FortiManager
    📅 Updated: Nov 10, 2026
  • CVE-2026-126260CVSS 9.0
    Server side request forgery vulnerability in FortiAnalyzer, FortiManager with FortiAnalyzer features & FortiAnalyzer-BigData
    📅 Updated: Nov 10, 2026
  • CVE-2026-126170CVSS 9.8
    Unauthenticated RCE in multiple products
    📅 Updated: Nov 10, 2026
  • CVE-2026-126261CVSS 9.0
    Improper authorizatin vulnerability in FortiManager
    📅 Updated: Nov 10, 2026
  • CVE-2026-126187CVSS 9.5
    React is a JavaScript library for building user interfaces. From 19.0.0 until 19.0.9, 19.1.10, 19.2.9, and 19.3.1, the...
    📅 Updated: Nov 10, 2026
  • CVE-2026-126229CVSS 9.1
    Authorization Bypass in FortiManager, FortiAnalyzer, FortiManager Cloud and FortiAnalyzer Cloud
    📅 Updated: Nov 10, 2026
  • CVE-2026-126253CVSS 9.3
    OSPF Authentication Bypass in multiple product
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.