Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Critical SonicWall NSM Vulnerabilities Patched Critical SonicWall NSM vulnerabilities security update overview
  • Vulnerability Report

Critical SonicWall NSM Vulnerabilities Patched

Do Son September 3, 2026 0

SonicWall patched critical SonicWall NSM vulnerabilities in on-prem software. Update now to protect your network against remote code execution.
CVE-2026-85046: Chrome Zero-Day Vulnerability Exploited in the Wild Chrome zero-day vulnerability and V8 type confusion flaw
  • Vulnerability Report

CVE-2026-85046: Chrome Zero-Day Vulnerability Exploited in the Wild

Do Son September 3, 2026 0

Google patched a Chrome zero-day vulnerability currently exploited in the wild. The update resolves a severe V8 type confusion flaw (CVE-2026-85046).
Fewer attacks, more force: Link11’s European Cyber Report finds new DDoS records for the first half of 2026 05_Link11_ECR_Mid26_1_17883652968VDMcpNlac
  • Press Release

Fewer attacks, more force: Link11’s European Cyber Report finds new DDoS records for the first half of 2026

cybernewswire September 3, 2026 0
Frankfurt am Main, Deutschland, 3rd September 2026, CyberNewswire
Read More Read more about Fewer attacks, more force: Link11’s European Cyber Report finds new DDoS records for the first half of 2026
Cisco Secure Email S/MIME Flaws Publicly Disclosed Cisco Secure Email vulnerability S/MIME ciphertext decryption flaws publicly disclosed plus Cisco phone SIP denial of service diagram
  • Vulnerability Report

Cisco Secure Email S/MIME Flaws Publicly Disclosed

Do Son September 3, 2026 0

A public announcement exists for the Cisco Secure Email vulnerability pair in S/MIME decryption, plus a Cisco phone SIP denial-of-service flaw.
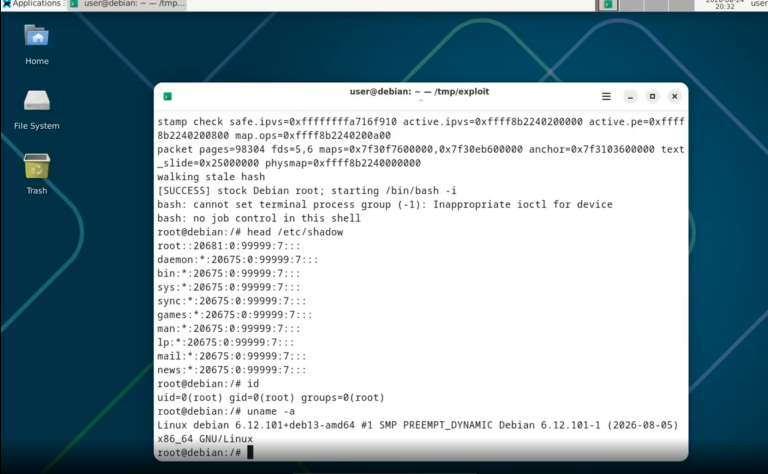
CVE-2026-80714 (CVSS 9.8): Linux Root Escalation PoC Out Linux kernel vulnerability CVE-2026-80714 IPVS netfilter use-after-free root privilege escalation PoC
  • Vulnerability Report

CVE-2026-80714 (CVSS 9.8): Linux Root Escalation PoC Out

Do Son September 3, 2026 0

CVE-2026-80714 (CVSS 9.8) is a Linux kernel IPVS use-after-free with public PoC code enabling root privilege escalation on Debian. Patch now.
CVE-2026-59346 (CVSS 9.3): VMware Flaw Allows Runnin Code on the Host VMware Workstation vulnerability CVE-2026-59346 VMXNET3 integer overflow execute code on the host advisory diagram
  • Vulnerability Report

CVE-2026-59346 (CVSS 9.3): VMware Flaw Allows Runnin Code on the Host

Do Son September 3, 2026 0

CVE-2026-59346, a critical VMware Workstation vulnerability, lets an attacker escape a guest VM and execute code on the host. Broadcom rates it 9.3 CVSS.
Cisco Fixes Critical Cisco IOS XR Vulnerabilities Engineers patching critical Cisco IOS XR vulnerabilities across carrier networks
  • Vulnerability Report

Cisco Fixes Critical Cisco IOS XR Vulnerabilities

Do Son September 3, 2026 0

Cisco fixed critical Cisco IOS XR vulnerabilities discovered by AI models. Update systems to patch Cisco IOS XR vulnerabilities.
Microsoft to Require Windows Driver SBOM and VEX Statements from March 2027 Windows driver SBOM and VEX requirement for WHCP certification 2027
  • Windows

Microsoft to Require Windows Driver SBOM and VEX Statements from March 2027

Do Son September 3, 2026 0

Microsoft will require a Windows driver SBOM and VEX statement for signing from March 2027, aligning WHCP with the EU CRA.

Microsoft Warns of TerminalFix Campaign Deploying Reverse Tunnels Half-click exploits chain showing webmail zero-days used by TA488 and TA458 against Zimbra, SOGo and Roundcube mailservers
  • Malware

Microsoft Warns of TerminalFix Campaign Deploying Reverse Tunnels

Do Son September 3, 2026 0

A new TerminalFix campaign uses fake CAPTCHAs to breach systems. Explore the TerminalFix attack chain and its covert reverse tunnel.
Court Upholds Edge Gatekeeper Exemption EU exempts Microsoft Edge browser from Digital Markets Act gatekeeper status
  • Technology

Court Upholds Edge Gatekeeper Exemption

Do Son September 3, 2026 0

The General Court dismisses the Opera lawsuit. The EU exempts Microsoft Edge from strict Digital Markets Act gatekeeper rules based on low user engagement.
Gryxa Toolkit: AI-Built Malware Watches Defenders Gryxa toolkit AI-built malware diagram showing RMM abuse and crypto credential theft across 324 hosts
  • Cybercriminals

Gryxa Toolkit: AI-Built Malware Watches Defenders

Do Son September 3, 2026 0

ReliaQuest found the Gryxa toolkit, AI-built malware that steals crypto credentials and spies on how defenders try to remove it across 324 hosts.
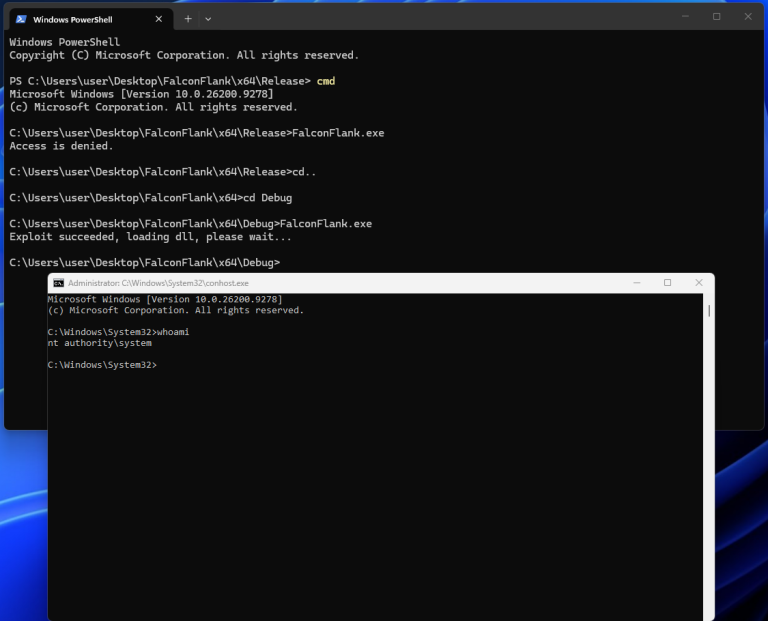
Researcher Claims CrowdStrike Falcon 0day, Posts PoC CrowdStrike Falcon vulnerability FalconFlank claimed 0day privilege escalation proof-of-concept publicly disclosed on GitHub diagram
  • Vulnerability Report

Researcher Claims CrowdStrike Falcon 0day, Posts PoC

Do Son September 3, 2026 0

A researcher claims a CrowdStrike Falcon vulnerability enabling privilege escalation and published a PoC. CrowdStrike has not confirmed it; no CVE exists.
Microsoft Defender Intercepts Legitimate Links Microsoft Defender falsely flags Google search links as malicious malware alerts
  • Technology

Microsoft Defender Intercepts Legitimate Links

Do Son September 3, 2026 0

Microsoft Defender for Office 365 incorrectly flags Google search links as malicious, causing false alarms. Microsoft is fixing the classification error.
CISA Adds Seven Critical Vulnerabilities to its KEV Security alert showing critical CISA KEV vulnerabilities added to the catalog
  • Vulnerability Report

CISA Adds Seven Critical Vulnerabilities to its KEV

Do Son September 3, 2026 0

CISA added critical CISA KEV vulnerabilities to its list. Patch these CISA KEV vulnerabilities now to block ongoing cyberattacks.
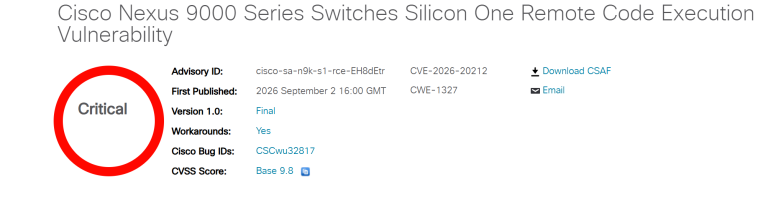
CVE-2026-20212 (CVSS 9.8): Cisco Nexus 9000 Root RCE Flaw Cisco Nexus 9000 vulnerability CVE-2026-20212 unauthenticated remote code execution root privileges Silicon One diagram
  • Vulnerability Report

CVE-2026-20212 (CVSS 9.8): Cisco Nexus 9000 Root RCE Flaw

Do Son September 3, 2026 0

CVE-2026-20212, a critical Cisco Nexus 9000 vulnerability, lets an unauthenticated attacker gain remote code execution with root privileges. CVSS 9.8.
Firefox for iOS Adds Native Ad Blocker A visual representation of the Firefox for iOS native ad blocker filtering internet content on an Apple device
  • Technology

Firefox for iOS Adds Native Ad Blocker

Do Son September 3, 2026 0

Mozilla integrates a native ad blocker into Firefox for iOS. Discover how this new feature utilizes the WebKit engine to filter intrusive advertisements.
Russian National Indicted in Freelance Malware Scheme A Russian national indicted for malware targeting freelance workers
  • Cybercriminals

Russian National Indicted in Freelance Malware Scheme

Do Son September 3, 2026 0

A Russian national indicted for malware faces trial. This Russian national indicted targeted 80,000 freelancers with malicious Excel attachments.
CVE-2026-43748 (CVSS 9.8): Apple ANE Kernel Bug, PoC Out Apple ANE kernel vulnerability CVE-2026-43748 out-of-bounds write heap corruption PoC on iOS and macOS
  • Vulnerability Report

CVE-2026-43748 (CVSS 9.8): Apple ANE Kernel Bug, PoC Out

Do Son September 3, 2026 0

CVE-2026-43748 (CVSS 9.8) is an Apple ANE kernel out-of-bounds write reachable from a sandbox. Details and macOS/iOS PoC code are public. Update now.
AI Solves 370-Year-Old Cryptogram An illustration of Claude AI deciphering an ancient 17th-century manuscript cryptogram
  • Technology

AI Solves 370-Year-Old Cryptogram

Do Son September 3, 2026 0

Vals AI used the newly released Claude Fable 5.1 model to successfully decrypt Thomas Urquhart's 370-year-old Cyphral Distich.
CVE-2026-73749: Unauth RCE in HPE Networking AOS-CX Scores 9.8 HPE AOS-CX vulnerability CVE-2026-73749 unauthenticated remote code execution CVSS 9.8 switch advisory diagram
  • Vulnerability Report

CVE-2026-73749: Unauth RCE in HPE Networking AOS-CX Scores 9.8

Do Son September 3, 2026 0

CVE-2026-73749, a critical HPE AOS-CX vulnerability, enables unauthenticated remote code execution at CVSS 9.8. HPE patched 31 flaws across its switches.
Jenkins Patches RCE Flaw and 30+ Vulnerabilities Jenkins vulnerability deserialization remote code execution security advisory core and plugins patch diagram
  • Vulnerability Report

Jenkins Patches RCE Flaw and 30+ Vulnerabilities

Do Son September 3, 2026 0

Jenkins fixed a deserialization flaw leading to remote code execution, plus over 30 more CVEs across core and popular plugins. Update now.
Broadcom TrueSource Project Secures Open-Source Builds Broadcom TrueSource project AI vulnerability scanning and enterprise software supply chain security
  • Technology

Broadcom TrueSource Project Secures Open-Source Builds

Do Son September 2, 2026 0

The Broadcom TrueSource project provides verified, secure, and commercially supported open-source software builds to combat supply chain attacks.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59360CVSS 9.8
    The killProcesses mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59361CVSS 9.8
    The cleanIptables mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2026-119923CVSS 9.3
    A heap-based buffer overflow in the TDS prelogin parser in the Babelfish for PostgreSQL extension versions 1.0-1.5, 2.1-2.15,...
    📅 Updated: Nov 7, 2026
  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121379CVSS 9.6
    The Tournamatch WordPress plugin before 4.7.1 does not validate or restrict the path of a previously stored profile...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.