Skip to content
November 11, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Hackers Exploit Foundation Software, Exposing Sensitive Contractor Data Foundation Software
  • Cyber Security

Hackers Exploit Foundation Software, Exposing Sensitive Contractor Data

Do Son September 18, 2024 0

Protecting your construction business from cyberattacks. Learn about the recent wave targeting the widely-used Foundation Software.

Cyberattack on Delta Prime: Losses Soar to $6M Delta Prime cyberattack
  • Cyber Security

Cyberattack on Delta Prime: Losses Soar to $6M

Do Son September 18, 2024 0

Learn about the recent cyberattack on the Delta Prime platform and the theft of $6 million worth of cryptocurrency.

Chinese Engineer Indicted for Alleged Cyber Espionage Campaign Against US Aerospace Industry CVE-2024-3817
  • Cyber Security

Chinese Engineer Indicted for Alleged Cyber Espionage Campaign Against US Aerospace Industry

Do Son September 18, 2024 0

Discover the details of the indictment against Song Wu, a Chinese engineer accused of spear phishing to obtain sensitive aerospace software.

LibreOffice Vulnerability (CVE-2024-7788): Exploit of “Repair Mode” Signatures Raises Security Concerns CVE-2024-7788 LibreOffice CVE-2025-1080
  • Vulnerability

LibreOffice Vulnerability (CVE-2024-7788): Exploit of “Repair Mode” Signatures Raises Security Concerns

Do Son September 18, 2024 0

Discover the newly disclosed CVE-2024-7788 security vulnerability in LibreOffice's document recovery mechanism, and learn how to protect your system.

Apple Hits Pause on iPadOS 18 for M4 iPad Pro Amid ‘Bricking’ Fears iPad Pro Camera, M5 Chip iPadOS 18 iPad Repair, Self-Service
  • Technology

Apple Hits Pause on iPadOS 18 for M4 iPad Pro Amid ‘Bricking’ Fears

Do Son September 17, 2024 0

Apple pulls the plug on iPadOS 18 update for M4 iPad Pro models after reports of devices becoming unusable. Learn more about the issue and its impact.
Microsoft Confirms CVE-2024-37985 as Zero-Day Bug in Windows CVE-2024-37985
  • Vulnerability

Microsoft Confirms CVE-2024-37985 as Zero-Day Bug in Windows

Do Son September 17, 2024 0

Stay informed about the latest security update from Microsoft: CVE-2024-37985, a zero-day vulnerability in the Windows kernel.

CISA Warns of Actively Exploited Adobe Flash Player Vulnerabilities
  • Vulnerability

CISA Warns of Actively Exploited Adobe Flash Player Vulnerabilities

Do Son September 17, 2024 0

Stay informed about the latest Adobe Flash Player vulnerability. Learn about the critical flaws actively exploited in the wild.

GitLab Releases Critical Security Patch for CVE-2024-45409 (CVSS 10) Vulnerability GitLab Security Update Account Impersonation GitLab Security Update CVE-2026-1090 GitLab vulnerability GitLab vulnerability, GitLab patches
  • Vulnerability

GitLab Releases Critical Security Patch for CVE-2024-45409 (CVSS 10) Vulnerability

Do Son September 17, 2024 0

Stay informed about the urgent GitLab vulnerability update. Learn how to address the critical CVE-2024-45409 flaw that exposes instances to potential security breaches.
Critical Flaws in Red Hat OpenShift: CVE-2024-45496 (CVSS 9.9) & CVE-2024-7387 (CVSS 9.1) CVE-2024-45496 & CVE-2024-7387 - OpenShift
  • Vulnerability

Critical Flaws in Red Hat OpenShift: CVE-2024-45496 (CVSS 9.9) & CVE-2024-7387 (CVSS 9.1)

Do Son September 17, 2024 0

Discover the critical vulnerabilities impacting Red Hat OpenShift's security posture. Learn about CVE-2024-45496 and CVE-2024-7387 and their potential impact on the platform.

Cybercriminals Exploit CAPTCHA to Deliver Malware: Experts Issue Warning CAPTCHA
  • Malware

Cybercriminals Exploit CAPTCHA to Deliver Malware: Experts Issue Warning

Do Son September 17, 2024 0

Beware of counterfeit CAPTCHA tests! Learn how cybercriminals are using fake CAPTCHA challenges to distribute malware on Windows devices.

PoC Exploit Releases for Unauthenticated RCE CVE-2024-40711 in Veeam Backup & Replication CVE-2024-40711 exploit
  • Vulnerability

PoC Exploit Releases for Unauthenticated RCE CVE-2024-40711 in Veeam Backup & Replication

Do Son September 17, 2024 0

To complicate matters further, a proof-of-concept (PoC) exploit for CVE-2024-40711 has been made publicly available on GitHub.

UNC2970’s Backdoor Deployed via Trojanized PDF Reader Targets Critical Infrastructure UNC2970 - MISTPEN backdoor
  • Cyber Security
  • Malware

UNC2970’s Backdoor Deployed via Trojanized PDF Reader Targets Critical Infrastructure

Do Son September 17, 2024 0

Uncover the cyber-espionage tactics of UNC2970 and their custom backdoor, MISTPEN, targeting senior-level employees in critical industries.

WooCommerce Skimmer Employs Stealthy Tactics to Pilfer Card Data Magento Credit Card Stealer npm package reverse shell
  • Malware

WooCommerce Skimmer Employs Stealthy Tactics to Pilfer Card Data

Do Son September 17, 2024 0

Uncover the latest credit card skimming technique targeting WooCommerce stores. Learn how malicious code disguised as an image file can steal customer data.

CVE-2024-38812: VMware’s 9.8 Severity Security Nightmare CVE-2024-38812 Broadcom VMware, EU Antitrust Lawsuit
  • Vulnerability

CVE-2024-38812: VMware’s 9.8 Severity Security Nightmare

Do Son September 17, 2024 0

Discover the details of CVE-2024-38812, a critical vulnerability in VMware vCenter Server that allows remote code execution.
Cybercriminals Target US-Taiwan Defense Industry Conference with Stealthy Fileless Malware Stealthy Fileless Malware
  • Cyber Security
  • Malware

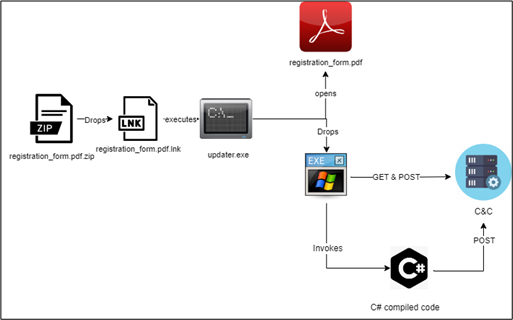
Cybercriminals Target US-Taiwan Defense Industry Conference with Stealthy Fileless Malware

Do Son September 17, 2024 0

Unveiling a sophisticated cyberattack: Learn about the stealthy fileless malware targeting individuals associated with the US-Taiwan Defense Industry Conference.
PoC Exploit Released for Windows Hyper-V Zero-Day Vulnerability CVE-2024-38080 CVE-2024-38080 PoC exploit Github
  • Vulnerability

PoC Exploit Released for Windows Hyper-V Zero-Day Vulnerability CVE-2024-38080

Do Son September 16, 2024 0

Explore the analysis and PoC exploit for the CVE-2024-38080 vulnerability in Windows Hyper-V, a serious threat to virtualized environments.
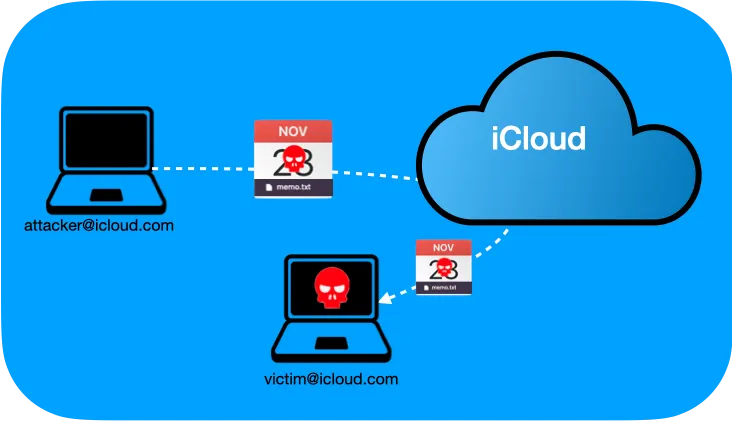
Zero-Click Calendar Invite: Critical macOS Vulnerability Chain Uncovered zero-click macOS vulnerability
  • Vulnerability

Zero-Click Calendar Invite: Critical macOS Vulnerability Chain Uncovered

Do Son September 16, 2024 0

Discover the Zero-Click Calendar Invite vulnerability in macOS, exposing millions of users to potential remote code execution.

166k+ Projects at Risk: AutoGPT’s Critical Vulnerability Explained – CVE-2024-6091 (CVSS 9.8) CVE-2024-6091 - AutoGPT
  • Vulnerability

166k+ Projects at Risk: AutoGPT’s Critical Vulnerability Explained – CVE-2024-6091 (CVSS 9.8)

Do Son September 16, 2024 0

Learn about the recent security vulnerability in AutoGPT, CVE-2024-6091. Understand the risks it poses and how to protect your systems from potential exploitation.

Faraday: Open Source Vulnerability Management Platform Vulnerability Management Platform
  • Open Source Tool

Faraday: Open Source Vulnerability Management Platform

Do Son September 16, 2024 0

Discover how Faraday's Vulnerability Management Platform helps security teams streamline vulnerability discovery and remediation efforts.
CISA Flags Two Actively Exploited Vulnerabilities: Critical Threats to Windows and WhatsUp Gold State-Sponsored Exploitation CISA KEV Catalog F5 BIG-IP RCE CISA KEV Catalog SolarWinds WHD Exploit CVE-2025-40551 Zimbra XSS Zero-Day CVE-2025-27915 Exploited Windows Security Vulnerabilities
  • Cyber Security
  • Malware
  • Vulnerability

CISA Flags Two Actively Exploited Vulnerabilities: Critical Threats to Windows and WhatsUp Gold

Do Son September 16, 2024 0

Take immediate action to protect your Windows system. Learn about the new actively exploited vulnerabilities and how to safeguard your data.

Kiosk Mode Attack: New Cyber Threat Steals Browser Credentials StealC malware
  • Malware

Kiosk Mode Attack: New Cyber Threat Steals Browser Credentials

Do Son September 16, 2024 0

Discover the new attack method used by cybercriminals: StealC malware. Learn how this malicious software steals user credentials through web browsers.

Tenable Exposes Critical “CloudImposer” Vulnerability in Google Cloud Platform Composer CloudImposer - dependency confusion
  • Vulnerability

Tenable Exposes Critical “CloudImposer” Vulnerability in Google Cloud Platform Composer

Do Son September 16, 2024 0

Discover the critical vulnerability in Google Cloud Platform (GCP) Composer known as CloudImposer and the risks it poses to cloud environments.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-20320CVSS 7.5
    A vulnerability in the Open Client Interface (OCI) XML Parser of Cisco BroadWorks could allow an unauthenticated, remote...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111560CVSS 8.6
    Improper neutralization of shell metacharacters in the timezone configuration field in certain Barracuda appliance products using common Barracuda...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-124194CVSS 6.5
    Product ui does not warn user of unsafe actions in Microsoft Office Outlook allows an unauthorized attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-126542CVSS 9.3
    WWBN AVideo 6.5 through 29.7.1 contains an authentication bypass vulnerability that allows unauthenticated attackers to log in as...
    📅 Updated: Nov 11, 2026
  • CVE-2026-126539CVSS 9.2
    Directus before 12.1.0 contains an authorization bypass vulnerability that allows unauthenticated attackers to skip permission checks by sending...
    📅 Updated: Nov 11, 2026
  • CVE-2026-114160CVSS 9.8
    Server-side request forgery (ssrf) in Azure Managed Grafana allows an unauthorized attacker to elevate privileges over a network.
    📅 Updated: Nov 11, 2026
  • CVE-2026-126259CVSS 9.0
    Missing authentication for critical function in FortiOS
    📅 Updated: Nov 10, 2026
  • CVE-2026-126262CVSS 9.3
    Improper neutralization of special elements used in an SQL command in FortiManager
    📅 Updated: Nov 10, 2026
  • CVE-2026-126260CVSS 9.0
    Server side request forgery vulnerability in FortiAnalyzer, FortiManager with FortiAnalyzer features & FortiAnalyzer-BigData
    📅 Updated: Nov 10, 2026
  • CVE-2026-126170CVSS 9.8
    Unauthenticated RCE in multiple products
    📅 Updated: Nov 10, 2026
  • CVE-2026-126261CVSS 9.0
    Improper authorizatin vulnerability in FortiManager
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.