CatDDoS-Related Gangs Ramp Up Attacks Exploiting Over 80 Vulnerabilities Cyber Security Malware CatDDoS-Related Gangs Ramp Up Attacks Exploiting Over 80 Vulnerabilities Do Son May 26, 2024 0 Read More Read more about CatDDoS-Related Gangs Ramp Up Attacks Exploiting Over 80 Vulnerabilities
Unfading Sea Haze: A New Cyber Espionage Threat in the South China Sea Cyber Security Unfading Sea Haze: A New Cyber Espionage Threat in the South China Sea Do Son May 26, 2024 0 Read More Read more about Unfading Sea Haze: A New Cyber Espionage Threat in the South China Sea
CLOUD#REVERSER: Threat Actors Exploit Legitimate Cloud Services for Stealthy Attacks Cyber Security CLOUD#REVERSER: Threat Actors Exploit Legitimate Cloud Services for Stealthy Attacks Do Son May 26, 2024 0 Read More Read more about CLOUD#REVERSER: Threat Actors Exploit Legitimate Cloud Services for Stealthy Attacks
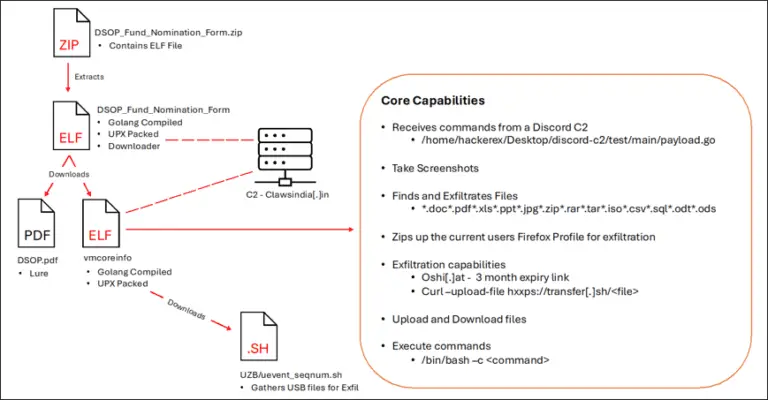
Transparent Tribe Targets Indian Government and Defense Sectors with Evolving Cyber Espionage Tactics Cyber Security Malware Transparent Tribe Targets Indian Government and Defense Sectors with Evolving Cyber Espionage Tactics Do Son May 26, 2024 0 Read More Read more about Transparent Tribe Targets Indian Government and Defense Sectors with Evolving Cyber Espionage Tactics
How Data Governance Automation Reduces Enterprise Security Vulnerabilities Technique How Data Governance Automation Reduces Enterprise Security Vulnerabilities Do Son May 26, 2024 0 Read More Read more about How Data Governance Automation Reduces Enterprise Security Vulnerabilities
CVE-2024-5148: GNOME Remote Desktop Vulnerability Exposes Sensitive Information Vulnerability CVE-2024-5148: GNOME Remote Desktop Vulnerability Exposes Sensitive Information Do Son May 24, 2024 0 Read More Read more about CVE-2024-5148: GNOME Remote Desktop Vulnerability Exposes Sensitive Information
Researchers Detail Critical Vulnerability in AI-as-a-Service Provider Replicate Vulnerability Researchers Detail Critical Vulnerability in AI-as-a-Service Provider Replicate Do Son May 24, 2024 0 Read More Read more about Researchers Detail Critical Vulnerability in AI-as-a-Service Provider Replicate
Attackers Exploit Obscure WordPress Plugin to Steal Credit Card Data Malware Attackers Exploit Obscure WordPress Plugin to Steal Credit Card Data Do Son May 24, 2024 0 Read More Read more about Attackers Exploit Obscure WordPress Plugin to Steal Credit Card Data
DNSBomb: New DDoS Attack Explodes DNS Traffic, Threatening Critical Internet Infrastructure Vulnerability DNSBomb: New DDoS Attack Explodes DNS Traffic, Threatening Critical Internet Infrastructure Do Son May 23, 2024 0 Read More Read more about DNSBomb: New DDoS Attack Explodes DNS Traffic, Threatening Critical Internet Infrastructure
CVE-2024-36077: Remote Code Execution Threatens Qlik Sense Users Vulnerability CVE-2024-36077: Remote Code Execution Threatens Qlik Sense Users Do Son May 23, 2024 0 Read More Read more about CVE-2024-36077: Remote Code Execution Threatens Qlik Sense Users
The Hidden Threat in Man Pages: Kinsing Malware Targets Apache Tomcat Servers Cyber Security Malware The Hidden Threat in Man Pages: Kinsing Malware Targets Apache Tomcat Servers Do Son May 23, 2024 0 Read More Read more about The Hidden Threat in Man Pages: Kinsing Malware Targets Apache Tomcat Servers
CVE-2024-34710: Wiki.js Vulnerability Exposes Users to Potential Account Takeover Vulnerability CVE-2024-34710: Wiki.js Vulnerability Exposes Users to Potential Account Takeover Do Son May 23, 2024 0 Read More Read more about CVE-2024-34710: Wiki.js Vulnerability Exposes Users to Potential Account Takeover
CVE-2024-28064: Critical Flaw Discovered in Totemomail Email Encryption Software Vulnerability CVE-2024-28064: Critical Flaw Discovered in Totemomail Email Encryption Software Do Son May 23, 2024 0 Read More Read more about CVE-2024-28064: Critical Flaw Discovered in Totemomail Email Encryption Software
Ransomhub’s SCADA Hack: A Wake-Up Call for Industrial Cybersecurity Cyber Security Ransomhub’s SCADA Hack: A Wake-Up Call for Industrial Cybersecurity Do Son May 23, 2024 0 Read More Read more about Ransomhub’s SCADA Hack: A Wake-Up Call for Industrial Cybersecurity
CVE-2024-5274: Google Patches Zero-Day Vulnerability Actively Exploited in the Wild Vulnerability CVE-2024-5274: Google Patches Zero-Day Vulnerability Actively Exploited in the Wild Do Son May 23, 2024 0 Read More Read more about CVE-2024-5274: Google Patches Zero-Day Vulnerability Actively Exploited in the Wild
Researchers Reveals Ikaruz Red Team’s Rising Threat to Philippine Cybersecurity Cyber Security Researchers Reveals Ikaruz Red Team’s Rising Threat to Philippine Cybersecurity Do Son May 23, 2024 0 Read More Read more about Researchers Reveals Ikaruz Red Team’s Rising Threat to Philippine Cybersecurity
CISA Adds Apache Flink CVE-2020-17519 Vulnerability to KEV Catalog Vulnerability CISA Adds Apache Flink CVE-2020-17519 Vulnerability to KEV Catalog Do Son May 23, 2024 0 Read More Read more about CISA Adds Apache Flink CVE-2020-17519 Vulnerability to KEV Catalog
CVE-2024-4978: Backdoor Discovered in Justice AV Solutions Courtroom Software Malware Vulnerability CVE-2024-4978: Backdoor Discovered in Justice AV Solutions Courtroom Software Do Son May 23, 2024 0 Read More Read more about CVE-2024-4978: Backdoor Discovered in Justice AV Solutions Courtroom Software
CVE-2024-20360: Cisco FMC Vulnerability Grants Hackers Root Access Vulnerability CVE-2024-20360: Cisco FMC Vulnerability Grants Hackers Root Access Do Son May 23, 2024 0 Read More Read more about CVE-2024-20360: Cisco FMC Vulnerability Grants Hackers Root Access
Software Supply Chains Threatened: Nexus Repository CVE-2024-4956 Flaw Exposed Vulnerability Software Supply Chains Threatened: Nexus Repository CVE-2024-4956 Flaw Exposed Do Son May 23, 2024 0 Read More Read more about Software Supply Chains Threatened: Nexus Repository CVE-2024-4956 Flaw Exposed
Westermo EDW-100 Converter Vulnerable: Critical Flaws Discovered, Replacement Urged Vulnerability Westermo EDW-100 Converter Vulnerable: Critical Flaws Discovered, Replacement Urged Do Son May 22, 2024 0 Read More Read more about Westermo EDW-100 Converter Vulnerable: Critical Flaws Discovered, Replacement Urged
PoC Releases for Unauthorized RCE Flaw (CVE-2024-29269) Threatens 40K+ Telesquare Routers Vulnerability PoC Releases for Unauthorized RCE Flaw (CVE-2024-29269) Threatens 40K+ Telesquare Routers Do Son May 22, 2024 0 Read More Read more about PoC Releases for Unauthorized RCE Flaw (CVE-2024-29269) Threatens 40K+ Telesquare Routers

 Do Son