Google Rushes to Patch Chrome Zero-Day Exploit: CVE-2024-4671 Vulnerability Google Rushes to Patch Chrome Zero-Day Exploit: CVE-2024-4671 Do Son May 9, 2024 0 Read More Read more about Google Rushes to Patch Chrome Zero-Day Exploit: CVE-2024-4671
CVE-2024-34350 & CVE-2024-34351: Two Vulnerabilities Patched in Popular Next.js Framework Vulnerability CVE-2024-34350 & CVE-2024-34351: Two Vulnerabilities Patched in Popular Next.js Framework Do Son May 9, 2024 0 Read More Read more about CVE-2024-34350 & CVE-2024-34351: Two Vulnerabilities Patched in Popular Next.js Framework
CVE-2024-4701 (CVSS 9.9): Major RCE Risk in Netflix’s Genie Platform Vulnerability CVE-2024-4701 (CVSS 9.9): Major RCE Risk in Netflix’s Genie Platform Do Son May 9, 2024 0 Read More Read more about CVE-2024-4701 (CVSS 9.9): Major RCE Risk in Netflix’s Genie Platform
90k+ Users at Risk: Unauthenticated LFI Vulnerability Affects Porto Theme Vulnerability 90k+ Users at Risk: Unauthenticated LFI Vulnerability Affects Porto Theme Do Son May 9, 2024 0 Read More Read more about 90k+ Users at Risk: Unauthenticated LFI Vulnerability Affects Porto Theme
FIN7 Hackers Using Signed Malware and Fake Google Ads to Evade Defenses Cyber Security Malware FIN7 Hackers Using Signed Malware and Fake Google Ads to Evade Defenses Do Son May 9, 2024 0 Read More Read more about FIN7 Hackers Using Signed Malware and Fake Google Ads to Evade Defenses
Critical Spin Framework Flaw: Sandbox Escape Vulnerability Exposed (CVE-2024-32980) Vulnerability Critical Spin Framework Flaw: Sandbox Escape Vulnerability Exposed (CVE-2024-32980) Do Son May 9, 2024 0 Read More Read more about Critical Spin Framework Flaw: Sandbox Escape Vulnerability Exposed (CVE-2024-32980)
CVE-2024-33861: Patch Released for Qt Vulnerability Affecting Applications Vulnerability CVE-2024-33861: Patch Released for Qt Vulnerability Affecting Applications Do Son May 9, 2024 0 Read More Read more about CVE-2024-33861: Patch Released for Qt Vulnerability Affecting Applications
SocGholish Campaign Targets Business Networks via Fake Browser Updates Malware SocGholish Campaign Targets Business Networks via Fake Browser Updates Do Son May 8, 2024 0 Read More Read more about SocGholish Campaign Targets Business Networks via Fake Browser Updates
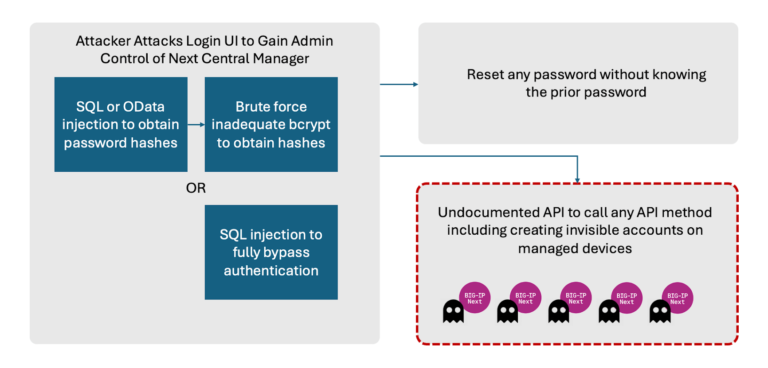
Next-Gen F5 BIG-IP Management System Hit by Serious Vulnerabilities Vulnerability Next-Gen F5 BIG-IP Management System Hit by Serious Vulnerabilities Do Son May 8, 2024 0 Read More Read more about Next-Gen F5 BIG-IP Management System Hit by Serious Vulnerabilities
CVE-2024-24787 (CVSS 9.8): Go Vulnerability Could Lead to Code Execution Vulnerability CVE-2024-24787 (CVSS 9.8): Go Vulnerability Could Lead to Code Execution Do Son May 8, 2024 0 Read More Read more about CVE-2024-24787 (CVSS 9.8): Go Vulnerability Could Lead to Code Execution
Critical Flaws in CyberPower Software Put Power Systems at Risk Vulnerability Critical Flaws in CyberPower Software Put Power Systems at Risk Do Son May 8, 2024 0 Read More Read more about Critical Flaws in CyberPower Software Put Power Systems at Risk
Beware! AsyncRAT Shapeshifts to Evade Defenses Malware Beware! AsyncRAT Shapeshifts to Evade Defenses Do Son May 8, 2024 0 Read More Read more about Beware! AsyncRAT Shapeshifts to Evade Defenses
CVE-2024-34346: Deno Vulnerability Allows Privilege Elevation Vulnerability CVE-2024-34346: Deno Vulnerability Allows Privilege Elevation Do Son May 8, 2024 0 Read More Read more about CVE-2024-34346: Deno Vulnerability Allows Privilege Elevation
CVE-2024-32849: Trend Micro Maximum Security Privilege Escalation Vulnerability Vulnerability CVE-2024-32849: Trend Micro Maximum Security Privilege Escalation Vulnerability Do Son May 8, 2024 0 Read More Read more about CVE-2024-32849: Trend Micro Maximum Security Privilege Escalation Vulnerability
CVE-2024-29212: Veeam RCE Vulnerability Exposes Data Protection Services to Risk Vulnerability CVE-2024-29212: Veeam RCE Vulnerability Exposes Data Protection Services to Risk Do Son May 7, 2024 0 Read More Read more about CVE-2024-29212: Veeam RCE Vulnerability Exposes Data Protection Services to Risk
Mirai Botnet Exploits Ivanti Vulnerabilities (CVE-2023-46805 & CVE-2024-21887) Malware Vulnerability Mirai Botnet Exploits Ivanti Vulnerabilities (CVE-2023-46805 & CVE-2024-21887) Do Son May 7, 2024 0 Read More Read more about Mirai Botnet Exploits Ivanti Vulnerabilities (CVE-2023-46805 & CVE-2024-21887)
Minecraft Mod Disguises Popular Password Stealer – zEus Stealer Malware Minecraft Mod Disguises Popular Password Stealer – zEus Stealer Do Son May 7, 2024 0 Read More Read more about Minecraft Mod Disguises Popular Password Stealer – zEus Stealer
CVE-2024-4367 & CVE-2024-34342: JavaScript Flaws Threaten Millions of PDF.js and React-PDF Users Vulnerability CVE-2024-4367 & CVE-2024-34342: JavaScript Flaws Threaten Millions of PDF.js and React-PDF Users Do Son May 7, 2024 0 Read More Read more about CVE-2024-4367 & CVE-2024-34342: JavaScript Flaws Threaten Millions of PDF.js and React-PDF Users
“Cuckoo” Malware Lands on Macs, Steals Data, and Spies on Users Malware “Cuckoo” Malware Lands on Macs, Steals Data, and Spies on Users Do Son May 7, 2024 0 Read More Read more about “Cuckoo” Malware Lands on Macs, Steals Data, and Spies on Users
China-Linked Hackers Target MITRE with ROOTROT Web Shell Cyber Security Malware Vulnerability China-Linked Hackers Target MITRE with ROOTROT Web Shell Do Son May 7, 2024 0 Read More Read more about China-Linked Hackers Target MITRE with ROOTROT Web Shell
What is URL Phishing and How to Avoid It Cyber Security What is URL Phishing and How to Avoid It Do Son May 7, 2024 0 Read More Read more about What is URL Phishing and How to Avoid It
PoC Releases for CVE-2024-21006: Hackers Can Take Over Oracle WebLogic Server Vulnerability PoC Releases for CVE-2024-21006: Hackers Can Take Over Oracle WebLogic Server Do Son May 6, 2024 0 Read More Read more about PoC Releases for CVE-2024-21006: Hackers Can Take Over Oracle WebLogic Server
 Do Son