
 Do Son
Researchers from Unit 42, the threat intelligence team at Palo Alto Networks, have discovered a previously unknown...
Latest news

Researchers at zLabs have uncovered a sophisticated Android Remote Access Trojan (RAT) known as Fantasy Hub, being...

A sophisticated supply-chain attack has been uncovered in the NuGet package registry, where nine packages published under...

A sophisticated, self-propagating malware campaign known as GlassWorm has re-emerged, infecting three new VS Code extensions and...

The LangGraph project, a powerful, low-level orchestration framework trusted by major tech companies for building stateful AI...

Researchers at Datadog Security Research have uncovered a major supply-chain compromise in the npm ecosystem involving 17...

Elastic has released security updates to address a serious flaw in Elastic Defend, its endpoint protection component...

A new investigation by the Broadcom Threat Hunter Team has uncovered a China-linked cyber espionage campaign that...

A new report from Zensec has exposed a critical vulnerability in the IT supply chain, detailing how...

The North Korean advanced persistent threat (APT) group Kimsuky has once again emerged with a new, JavaScript-driven...

CVE-2024-34359 allow attackers to execute arbitrary code on systems using the library, leading to data breaches and system compromise

A new report reveals a disturbing trend in cyber attacks: the increasing use of Microsoft OneNote files to deliver malicious payloads
CVE-2024-3368 enables attackers to inject malicious code into websites, potentially leading to unauthorized access, data theft

A new wave of cyberattacks targeting financial institutions has been uncovered, with the notorious Metamorfo banking Trojan at its center

A proof-of-concept (PoC) exploit code for a recently patched zero-day CVE-2024-4947 vulnerability in Google Chrome has surfaced

Cybersecurity researchers at Elastic Security Labs have issued a warning about the increasing prominence of LATRODECTUS, a malware loader
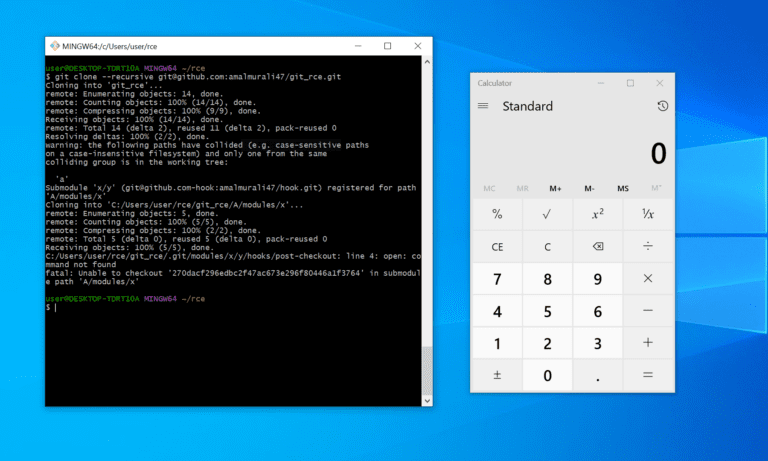
In addition to the technical details, Murali crafted a proof-of-concept (PoC) exploit for CVE-2024-32002 to demonstrate the RCE.

The North Korean state-sponsored group Springtail (also known as Kimsuky) has added a new Linux backdoor, dubbed Gomir, to its arsenal
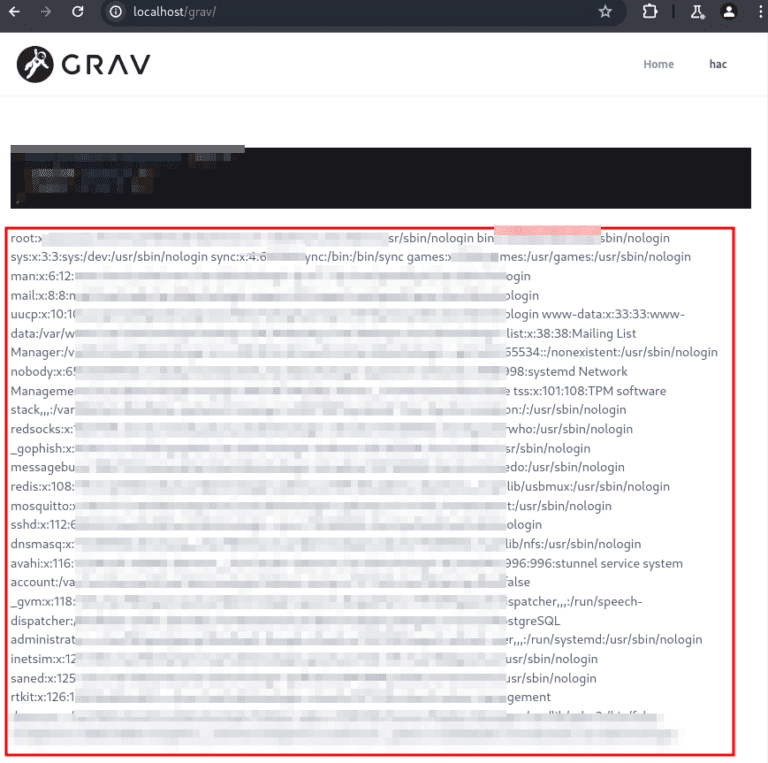
Tracked as CVE-2024-34082 (CVSS 8.5), the vulnerability stems from Grav's use of the Twig templating engine.

This novel use of Tesseract is part of a broader strategy by ViperSoftX to install additional malware strains, including Quasar RAT

A recent analysis by S-RM, a global cybersecurity consultancy, has shed light on the escalating sophistication of...

A series of critical vulnerabilities have been discovered in the XStore theme and its accompanying XStore Core plugin

Exploiting CVE-2024-22120 allows attackers to dump any values from the database, including sensitive information

Each tasked with managing activities and establishing communication with compromised IPs to facilitate the distribution of XMRig cryptominers

Bryan Smith shared the technical details and a proof-of-concept (PoC) for CVE-2024-22026 in Ivanti's Enterprise Mobility Management Platform

The flaw, tracked as CVE-2024-22476, could allow an unauthenticated attacker to “enable escalation of privilege via remote access”.

The campaign, dubbed UNK_SweetSpecter, utilizes a Remote Access Trojan (RAT) known as SugarGh0st to infiltrate systems and exfiltrate sensitive data

A critical SQL injection vulnerability (CVE-2024-32888) has been discovered in the Amazon JDBC Driver for Redshift
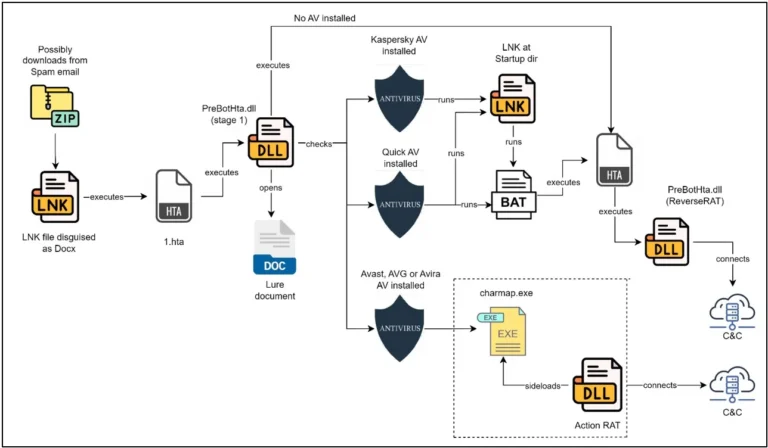
Upon further investigation, CRIL uncovered the use of malicious LNK files in the SideCopy malware campaign. These files, once executed

The PrestaShop project has recently issued a security advisory revealing two significant vulnerabilities (CVE-2024-34716 & CVE-2024-34717)

The campaign exploits GitHub, a legitimate platform for software development, to distribute various malware families

The campaign's success lies in its ability to bypass MFA, a security measure designed to protect accounts from unauthorized access