Skip to content
October 31, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
US Agencies Warn of AI-Generated Exploits Targeting Siemens S7 PLCs Siemens PLC cyber threat with AI-generated exploit scripts targeting S7 series controllers in critical infrastructure
  • Cybercriminals

US Agencies Warn of AI-Generated Exploits Targeting Siemens S7 PLCs

Do Son August 19, 2026 0

CISA and the NSA warn of an active Siemens PLC cyber threat using AI-generated exploit scripts disguised as monitoring tools. Protect your OT now.
Vault Secrets Operator Flaw CVE-2026-8715 Enables Privilege Escalation Vault Secrets Operator vulnerability CVE-2026-8715 privilege escalation diagram
  • Vulnerability Report

Vault Secrets Operator Flaw CVE-2026-8715 Enables Privilege Escalation

Do Son August 19, 2026 0

A Vault Secrets Operator vulnerability, CVE-2026-8715, lets tenants read pod files and gain privilege escalation. Patch to 1.5.0 now.
CVE-2026-66792 (CVSS 9.9): Red Hat ACM Flaw Allows Full Compromise of the Managed Cluster CVE-2026-66792 Red Hat Advanced Cluster Management privilege escalation full compromise managed cluster CVE-2026-66795 CVE-2026-71472
  • Vulnerability Report

CVE-2026-66792 (CVSS 9.9): Red Hat ACM Flaw Allows Full Compromise of the Managed Cluster

Do Son August 19, 2026 0

CVE-2026-66792 (CVSS 9.9) and two more Red Hat ACM flaws allow full compromise of the managed cluster via privilege escalation.
CVE-2026-0075: PoC Discloses Android EoP With No User Interaction CVE-2026-0075 Android elevation of privilege ContactsProvider2 SQL injection proof-of-concept exploit no user interaction
  • Vulnerability Report

CVE-2026-0075: PoC Discloses Android EoP With No User Interaction

Do Son August 19, 2026 0

A public PoC for CVE-2026-0075 exposes an Android elevation of privilege in ContactsProvider2 with no user interaction. Details are now disclosed.
IBM Db2 Mirror for i Hit by CVE-2026-17186 RCE Flaw (CVSS 9.9) IBM Db2 Mirror RCE CVE-2026-17186 vulnerability diagram
  • Vulnerability Report

IBM Db2 Mirror for i Hit by CVE-2026-17186 RCE Flaw (CVSS 9.9)

Do Son August 19, 2026 0

IBM patches an IBM Db2 Mirror RCE flaw, CVE-2026-17186, rated CVSS 9.9, plus 17 more bugs in Db2 Mirror for i. Patch now.
Former Ping Identity and CyberArk Executives Join AppViewX to Scale Machine and Agent Identity Security PR_Former_Ping_Identity_and_CyberArk_Executives_Jo_17870660979rEkmKasWH
  • Press Release

Former Ping Identity and CyberArk Executives Join AppViewX to Scale Machine and Agent Identity Security

cybernewswire August 19, 2026 0
New York, New York, 19th August 2026, CyberNewswire
Read More Read more about Former Ping Identity and CyberArk Executives Join AppViewX to Scale Machine and Agent Identity Security
CVE-2026-13737: Commvault Command Execution Flaws Expose Networks Commvault command execution flaws CVE-2026-13737 CVE-2026-13738 CVE-2026-13739
  • Vulnerability Report

CVE-2026-13737: Commvault Command Execution Flaws Expose Networks

Do Son August 19, 2026 0

Protect your network from CVE-2026-13737 and CVE-2026-13738. These critical Commvault command execution flaws allow hackers to bypass authorization checks.
Telegram Applies for .gram Domain to Give Every User Their Own TLD Telegram gram domain ICANN Pavel Durov top level domain application
  • Technology

Telegram Applies for .gram Domain to Give Every User Their Own TLD

Do Son August 19, 2026 0

Telegram has applied to ICANN for its own .gram domain, which would let every user claim a personal address like landian.gram tied to their account.
GitHub Outage Postmortem: Retry Storm and Copilot Auth Overload Explained GitHub outage postmortem retry storm Copilot authentication overload infrastructure
  • Technology

GitHub Outage Postmortem: Retry Storm and Copilot Auth Overload Explained

Do Son August 19, 2026 0

GitHub's postmortem reveals a service mesh overload triggered a retry storm across its infrastructure, while a Copilot bug sent authentication traffic to 10x normal levels.
Google Restricts Pixel Kernel Source Access, Ditching Public Git Repos Google Pixel kernel source code manual application GrapheneOS custom ROM
  • Android

Google Restricts Pixel Kernel Source Access, Ditching Public Git Repos

Do Son August 19, 2026 0

Google has quietly replaced public Git access to Pixel kernel source code with a manual application process, slowing custom ROM development, GrapheneOS reports.
OpenAI Astra Security Model: Pausing Development for Safety OpenAI Astra security model oversight and AI training isolation
  • Technology

OpenAI Astra Security Model: Pausing Development for Safety

Do Son August 19, 2026 0

OpenAI slows development as its new Astra security model reaches critical cyber thresholds. Discover how they dedicate massive compute to prevent AI escapes.
CVE-2026-18051 (CVSS 10): Unauthenticated Arbitrary File Write Hits 900k W3 Total Cache Sites W3 Total Cache vulnerability CVE-2026-18051 unauthenticated arbitrary file write path traversal on WordPress
  • Vulnerability Report

CVE-2026-18051 (CVSS 10): Unauthenticated Arbitrary File Write Hits 900k W3 Total Cache Sites

Do Son August 19, 2026 0

CVE-2026-18051 (CVSS 10) is an unauthenticated arbitrary file write in W3 Total Cache, exposing 900k+ WordPress sites. Update to 2.10.5.
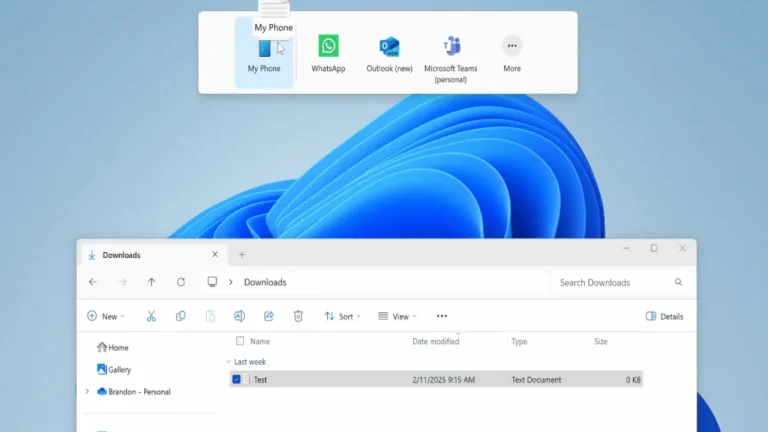
Microsoft Removes Windows 11 Drag Tray Windows 11 Drop Tray sharing feature removed from File Explorer
  • Windows

Microsoft Removes Windows 11 Drag Tray

Do Son August 19, 2026 0

Microsoft officially removes the experimental Windows 11 Drag Tray feature from beta builds after widespread user complaints about File Explorer interference.
PATCHCORD Malware Hits Afghan Telecom in New APT36 Campaign PATCHCORD malware APT36 SHEETCORD malware Afghan telecom diagram
  • Cybercriminals

PATCHCORD Malware Hits Afghan Telecom in New APT36 Campaign

Do Son August 19, 2026 0

Acronis ties a new PATCHCORD malware APT36 campaign to Afghan telecom and Indian targets. SHEETCORD malware abuses Google Sheets for C2.
GeForce NOW Now Fully Supports Firefox, Delivering 1440p 120fps Streaming GeForce NOW Firefox support cloud gaming Windows 1440p 120fps streaming
  • Technology

GeForce NOW Now Fully Supports Firefox, Delivering 1440p 120fps Streaming

Do Son August 19, 2026 0

NVIDIA's GeForce NOW now fully supports Firefox on Windows, offering Ultimate subscribers 1440p at 120fps after months of WebRTC and low-latency optimization work.
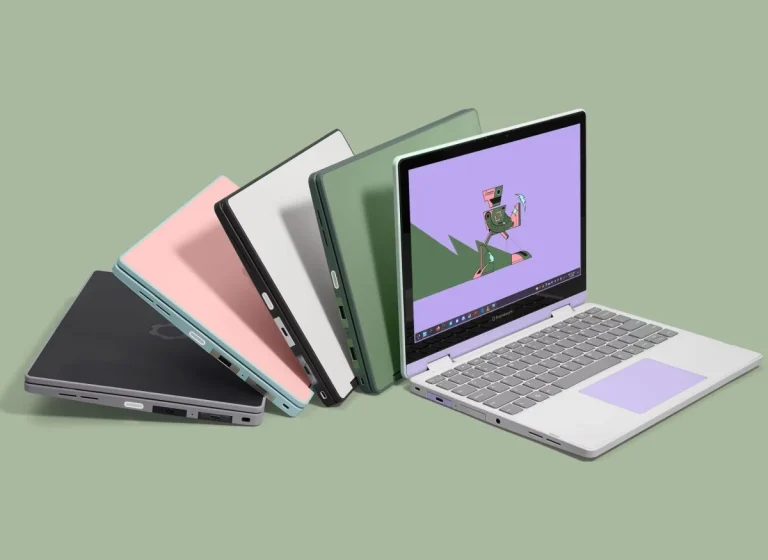
Framework Laptop 12: Upgraded with Intel Core Series 3 Framework Laptop 12 modular computer with Intel Core Series 3 processor
  • Linux

Framework Laptop 12: Upgraded with Intel Core Series 3

Do Son August 19, 2026 0

Discover the new Framework Laptop 12 featuring Intel Core Series 3 processors, a 70 percent battery boost, and default Fedora Linux OS configuration.
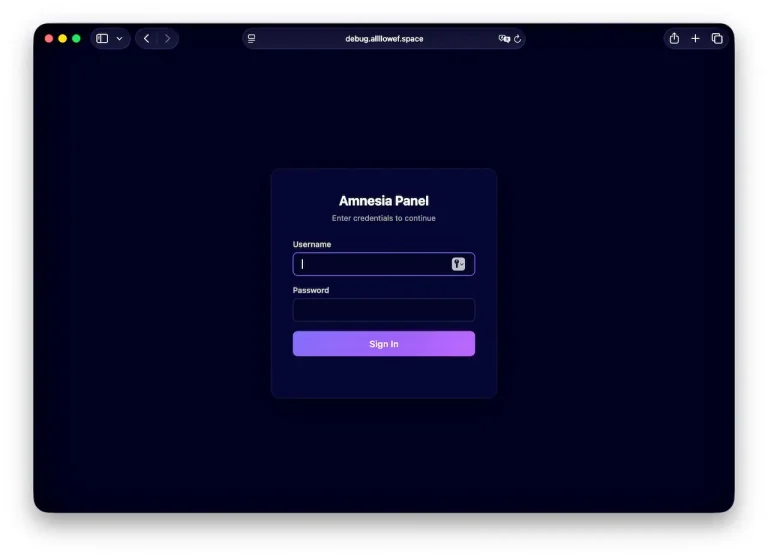
AmnesiaStealer macOS Infostealer Hacks Apple Devices AmnesiaStealer macOS infostealer malware diagram detailing the new AmnesiaStealer macOS infostealer
  • Malware

AmnesiaStealer macOS Infostealer Hacks Apple Devices

Do Son August 19, 2026 0

Jamf Threat Labs has discovered a new AmnesiaStealer macOS infostealer malware. The AmnesiaStealer macOS infostealer steals data and hijacks browsers.
CVE-2026-21580: Stored XSS Hits Atlassian Confluence Confluence vulnerability CVE-2026-21580 stored XSS unauthenticated attack diagram for Atlassian Data Center and Server
  • Vulnerability Report

CVE-2026-21580: Stored XSS Hits Atlassian Confluence

Do Son August 19, 2026 0

A Confluence vulnerability, CVE-2026-21580, is a stored XSS flaw (CVSS 8.6) allowing unauthenticated attacks. A Jira flaw also patched. Update now.
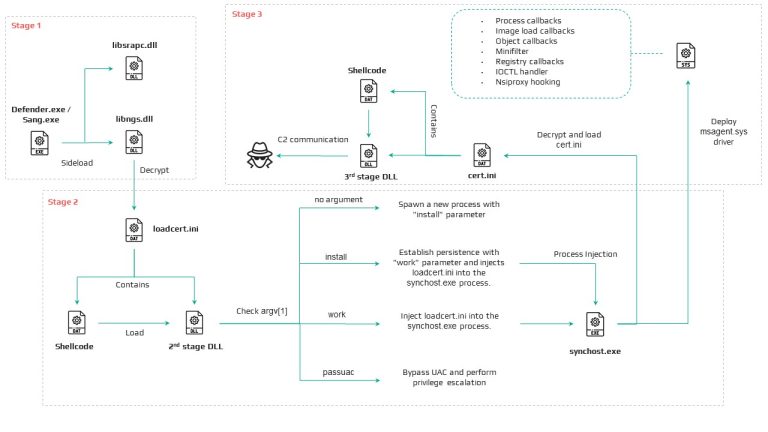
HoneyMyte CoolClient Rootkit Deploys Kernel Driver Diagram of the new HoneyMyte CoolClient rootkit showing kernel driver deployment
  • Cybercriminals

HoneyMyte CoolClient Rootkit Deploys Kernel Driver

Do Son August 19, 2026 0

Kaspersky uncovered the new HoneyMyte CoolClient rootkit. The HoneyMyte CoolClient rootkit deploys a kernel driver to hide malware on Windows.
BeyondTrust EPM Flaws Allow Windows Privilege Escalation BeyondTrust vulnerability CVE-2026-40144 local privilege escalation flaw in Endpoint Privilege Management for Windows
  • Vulnerability Report

BeyondTrust EPM Flaws Allow Windows Privilege Escalation

Do Son August 19, 2026 0

BeyondTrust patched two high-severity EPM flaws (CVE-2026-40144, CVE-2026-40145) allowing local privilege escalation on Windows. Update to 26.1.2.
Gmail Verified Sender Program Launch 2026 Google Gmail Verified Sender Program logo and political election campaign emails
  • Technology

Gmail Verified Sender Program Launch 2026

Do Son August 19, 2026 0

Google launches the Gmail Verified Sender Program, allowing political campaigns to bypass spam filters ahead of the 2026 US Mid-term Elections.
CVE-2026-60702 (CVSS 9.9): Oracle WebLogic Takeover Flaw Oracle WebLogic vulnerability CVE-2026-60702 CVSS 9.9 server takeover via T3 IIOP protocol diagram
  • Vulnerability Report

CVE-2026-60702 (CVSS 9.9): Oracle WebLogic Takeover Flaw

Do Son August 19, 2026 0

An Oracle WebLogic vulnerability, CVE-2026-60702 (CVSS 9.9), allows full server takeover. Oracle patched nine flaws, five critical. Update now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-113380CVSS 9.3
    In the RingRTC library before 2.72.0 for Signal, a peer that saturates a call's FSM queue can interfere...
    📅 Updated: Oct 31, 2026
  • CVE-2026-99153CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: scsi: libiscsi: Validate the ITT reflected in a...
    📅 Updated: Oct 31, 2026
  • CVE-2026-99154CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: scsi: libiscsi: Reject a negative task index from...
    📅 Updated: Oct 31, 2026
  • CVE-2026-118235CVSS 9.8
    The SimpleForm – Form Maker to Chat Apps with Quiz, Poll and Multi Lead Notifications plugin for WordPress...
    📅 Updated: Oct 31, 2026
  • CVE-2026-103882CVSS 9.1
    The Acadlix LMS – AI Quiz Maker, Online Exam & Course Plugin for WordPress plugin for WordPress is...
    📅 Updated: Oct 31, 2026
  • CVE-2026-119096CVSS 9.8
    The Uncanny Toolkit for LearnDash plugin for WordPress is vulnerable to Authentication Bypass in versions up to, and...
    📅 Updated: Oct 31, 2026
  • CVE-2026-116512CVSS 9.8
    The Project Manager – AI Powered Project Management, Task Management, Kanban Board & Time Tracker plugin for WordPress...
    📅 Updated: Oct 31, 2026
  • CVE-2026-89270CVSS 9.1
    The Popup Builder – Create highly converting, mobile friendly marketing popups. plugin for WordPress is vulnerable to authorization...
    📅 Updated: Oct 31, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.