Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
CISA Adds Six Exploited Vulnerabilities Including Citrix NetScaler Flaw CISA KEV Catalog warning showing six exploited vulnerabilities and Citrix NetScaler flaw CVE-2026-8452
  • Vulnerability Report

CISA Adds Six Exploited Vulnerabilities Including Citrix NetScaler Flaw

Do Son August 27, 2026 0

CISA adds six exploited vulnerabilities to its KEV Catalog, including a Citrix NetScaler flaw and CVE-2026-8452, with active exploitation confirmed.
Dell Cloud Disaster Recovery CVE-2026-70419 (CVSS 9.1) Allows Command Execution Dell Cloud Disaster Recovery vulnerability enabling command execution, CVE-2026-70419 CVSS 9.1 critical OS command injection flaw
  • Vulnerability Report

Dell Cloud Disaster Recovery CVE-2026-70419 (CVSS 9.1) Allows Command Execution

Do Son August 27, 2026 0

Dell patched 5 Cloud Disaster Recovery flaws. The top bug, CVE-2026-70419 (CVSS 9.1), allows command execution. Update to CDR 20.3 now.
High-Severity TP-Link Kasa Vulnerability Requires Immediate Patch Graphic showing the TP-Link Kasa vulnerability tracked as CVE-2026-76784
  • Vulnerability Report

High-Severity TP-Link Kasa Vulnerability Requires Immediate Patch

Do Son August 27, 2026 0

A high-severity TP-Link Kasa vulnerability (CVE-2026-76784) allows unauthorized smart home device control. Apply the latest firmware patch immediately.
CVE-2026-53361: PoC Exploit Enables AF_UNIX Container Escape CVE-2026-53361 AF_UNIX garbage collector container escape use-after-free race condition proof-of-concept
  • Vulnerability Report

CVE-2026-53361: PoC Exploit Enables AF_UNIX Container Escape

Do Son August 27, 2026 0

A public PoC for CVE-2026-53361 turns an AF_UNIX kernel race into a local container escape on Linux. Details and exploit code are now disclosed.
NVIDIA Releases Security Fixes for UFM Enterprise and DGX Spark Critical NVIDIA security updates patching CVE-2026-24170 in UFM Enterprise
  • Vulnerability Report

NVIDIA Releases Security Fixes for UFM Enterprise and DGX Spark

Do Son August 26, 2026 0

Critical NVIDIA security updates patch multiple flaws in UFM and DGX Spark systems, addressing CVE-2026-24170 and CVE-2026-24262.
GitLab Updates Fix Arbitrary Command Execution Vulnerability GitLab EE security patch addressing CVE-2026-18252
  • Vulnerability Report

GitLab Updates Fix Arbitrary Command Execution Vulnerability

Do Son August 26, 2026 0

A critical GitLab EE security patch addresses CVE-2026-18252, fixing a command execution flaw. Learn about affected versions, mechanisms, and mitigation.
FreeBSD Patches Eight Kernel Vulnerabilities FreeBSD security advisories patching eight kernel vulnerabilities including use-after-free local privilege escalation flaws CVE-2026-58090
  • Vulnerability Report

FreeBSD Patches Eight Kernel Vulnerabilities

Do Son August 26, 2026 0

FreeBSD patched 8 vulnerabilities on August 25, 2026, mostly local privilege escalation flaws plus a ppp code execution bug. Update now.
UniFi CVE-2026-77537 (CVSS 10.0): Command Injection Flaws Hit 22 Ubiquiti Products UniFi command injection vulnerabilities across Ubiquiti products, CVE-2026-77537 CVSS 10.0 critical flaw in UniFi Protect Application
  • Vulnerability Report

UniFi CVE-2026-77537 (CVSS 10.0): Command Injection Flaws Hit 22 Ubiquiti Products

Do Son August 26, 2026 0

Ubiquiti patched 22 UniFi flaws. Three hit CVSS 10.0, including command injection CVE-2026-77537. Update UniFi Protect, OS, and Talk now.
NVIDIA NemoClaw and OpenShell: CVE-2026-65093 (CVSS 9.9) Enables Code Execution NVIDIA NemoClaw and OpenShell vulnerabilities enabling code execution, CVE-2026-65093 CVSS 9.9 critical sandbox escape flaw
  • Vulnerability Report

NVIDIA NemoClaw and OpenShell: CVE-2026-65093 (CVSS 9.9) Enables Code Execution

Do Son August 26, 2026 0

NVIDIA patched 20 NemoClaw and OpenShell flaws. The worst, CVE-2026-65093 (CVSS 9.9), enables code execution via sandbox escape. Update now.
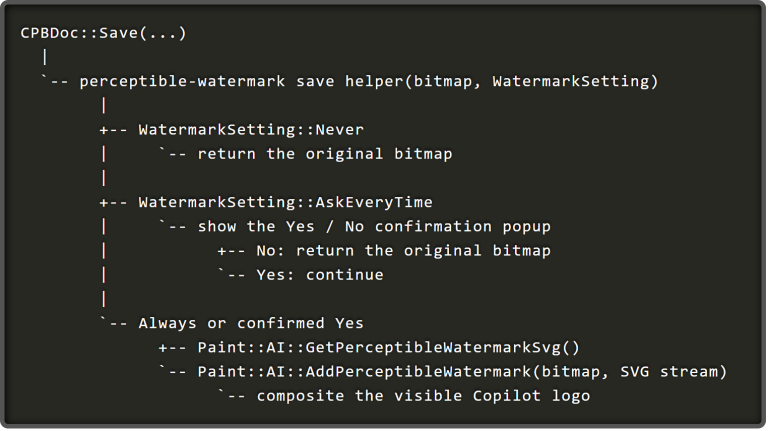
Reverse Engineering Reveals Microsoft’s Hidden InvisMark Watermark in Paint Microsoft InvisMark invisible watermark AI image Paint Photos reverse engineering
  • Technology

Reverse Engineering Reveals Microsoft’s Hidden InvisMark Watermark in Paint

Do Son August 26, 2026 0

Reverse engineering shows Microsoft's Paint app embeds an invisible, server-issued watermark into every AI-generated image, one users cannot fully disable.
Google Cloud Launches Gemini Enterprise for Finance and Law Google Cloud Gemini Enterprise platform empowering financial and legal professionals
  • Technology

Google Cloud Launches Gemini Enterprise for Finance and Law

Do Son August 26, 2026 0

Discover how Google Cloud Gemini Enterprise empowers the financial and legal sectors. Learn about its secure AI agents, data lineage, and MCP integration.
EA Anti-Cheat Secures Support for RTX SPARK NVIDIA RTX SPARK logo alongside EA Javelin Anticheat system integration graphics
  • Technology

EA Anti-Cheat Secures Support for RTX SPARK

Do Son August 26, 2026 0

NVIDIA confirms EA and Ubisoft are adapting anti-cheat software for the RTX SPARK platform, solving critical multiplayer gaming issues on Windows on Arm.
CVE-2026-65641 (CVSS 9.3): Veeam ONE Flaw Lets Unauthenticated Attacker Coerce SMB Authentication Veeam vulnerability allowing unauthenticated network attacker to coerce SMB authentication, CVE-2026-65641 CVSS 9.3 critical flaw
  • Vulnerability Report

CVE-2026-65641 (CVSS 9.3): Veeam ONE Flaw Lets Unauthenticated Attacker Coerce SMB Authentication

Do Son August 26, 2026 0

A critical Veeam ONE vulnerability (CVE-2026-65641, CVSS 9.3) lets an unauthenticated attacker coerce SMB authentication. Patch Veeam now.
77 Malicious Firefox Extensions Steal Crypto Wallet Secrets and Credentials Malicious Firefox extensions stealing crypto wallet secrets and credentials in the Offside Wallet Theft Factory campaign
  • Malware

77 Malicious Firefox Extensions Steal Crypto Wallet Secrets and Credentials

Do Son August 26, 2026 0

Socket tracked 77 malicious Firefox extensions that steal crypto wallet secrets and credentials. See how the Offside Wallet Theft Factory works.
Public Disclosure: Unpatched Log4j RCE Flaw in FilteredObjectInputStream, No CVE Assigned Log4j vulnerability enabling unauthenticated remote code execution via FilteredObjectInputStream deserialization, publicly disclosed on Apache issue tracker
  • Vulnerability Report

Public Disclosure: Unpatched Log4j RCE Flaw in FilteredObjectInputStream, No CVE Assigned

Do Son August 26, 2026 2

An unpatched Log4j RCE vulnerability was publicly disclosed on Apache's issue tracker. No CVE is assigned and no fix exists yet. Workaround inside.

Operation CameraSwarm: 14,500 Dahua Cameras Compromised Across Ukraine and Russia Diagram showing how prompt injection attacks and prompt injection techniques threaten AI security.
  • Cybercriminals

Operation CameraSwarm: 14,500 Dahua Cameras Compromised Across Ukraine and Russia

Do Son August 26, 2026 0

Operation CameraSwarm compromised 14,500+ Dahua cameras in 35 days. Hunt.io traced the camera hacking campaign to an exposed operator directory.
Apache Tomcat Patches 11 Vulnerabilities in 11.0.25 Update Apache Tomcat vulnerability patch in version 11.0.25 fixing authentication bypass and HTTP/2 denial of service flaws CVE-2026-68569
  • Vulnerability Report

Apache Tomcat Patches 11 Vulnerabilities in 11.0.25 Update

Do Son August 26, 2026 0

Apache Tomcat fixed 11 vulnerabilities on August 25, 2026, including auth bypass (CVE-2026-68569) and HTTP/2 DoS flaws. Update to 11.0.25 now.
Unpatched FURUNO FA-50 Vulnerabilities Impact Maritime Transponders Diagram of the maritime transponder exploiting FURUNO FA-50 vulnerabilities CVE-2026-59769 and CVE-2026-67578
  • Vulnerability Report

Unpatched FURUNO FA-50 Vulnerabilities Impact Maritime Transponders

Do Son August 26, 2026 0

Two unpatched FURUNO FA-50 vulnerabilities (CVE-2026-59769, CVE-2026-67578) let attackers alter maritime transponder settings. Learn the mitigation steps.

Grandoreiro Banking Trojan Returns With a DLL Sideloading Campaign TanStack Typosquatting npm Supply Chain Attack Axios Supply Chain Attack npm Poisoning eScan Supply Chain Attack Antivirus Compromise APT-36, NCERT WhatsApp Advisory FBI alert, Salesforce Salt Typhoon, APT group ConnectWise ScreenConnect hack Nation-state cyberattack FortiGate Leak - zkLend vulnerability - TRIPLESTRENGTH Threat Actor Group Dark Storm
  • Malware

Grandoreiro Banking Trojan Returns With a DLL Sideloading Campaign

Do Son August 26, 2026 0

Grandoreiro banking trojan resurfaces in a DLL sideloading campaign that abuses Duplicate Files Finder to hit Mexico and Latin America.
Adobe Campaign Classic CVE-2026-76197 (CVSS 10.0): Critical Flaws Allow Arbitrary Code Execution Adobe Campaign Classic vulnerability enabling arbitrary code execution, CVE-2026-76197 CVSS 10.0 critical OS command injection flaw
  • Vulnerability Report

Adobe Campaign Classic CVE-2026-76197 (CVSS 10.0): Critical Flaws Allow Arbitrary Code Execution

Do Son August 26, 2026 0

Three critical Adobe Campaign Classic flaws (CVE-2026-76197, CVSS 10.0) allow arbitrary code execution. Update to build 9401 now.
45M Weekly Downloads at Risk: Next.js CVE-2026-75604 (CVSS 9.0) Enables Unauthenticated Remote Code Execution Next.js vulnerability enabling unauthenticated remote code execution, CVE-2026-75604 CVSS 9.0 critical flaw affecting 45M weekly downloads
  • Vulnerability Report

45M Weekly Downloads at Risk: Next.js CVE-2026-75604 (CVSS 9.0) Enables Unauthenticated Remote Code Execution

Do Son August 26, 2026 0

Two critical Next.js vulnerabilities, including CVE-2026-75604 (CVSS 9.0), enable unauthenticated remote code execution. Patch to 15.5.24 or 16.3.3 now.
CVE-2026-57909: WatchGuard Agent Unauthenticated Remote Code Execution WatchGuard Agent vulnerability enabling unauthenticated remote code execution, CVE-2026-57909 path traversal critical flaw
  • Vulnerability Report

CVE-2026-57909: WatchGuard Agent Unauthenticated Remote Code Execution

Do Son August 26, 2026 0

Two critical WatchGuard Agent flaws (CVE-2026-57909, CVE-2026-57910) allow unauthenticated remote code execution. Update to 1.25.13.0000 now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59360CVSS 9.8
    The killProcesses mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59361CVSS 9.8
    The cleanIptables mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2026-119923CVSS 9.3
    A heap-based buffer overflow in the TDS prelogin parser in the Babelfish for PostgreSQL extension versions 1.0-1.5, 2.1-2.15,...
    📅 Updated: Nov 7, 2026
  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121379CVSS 9.6
    The Tournamatch WordPress plugin before 4.7.1 does not validate or restrict the path of a previously stored profile...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.