Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
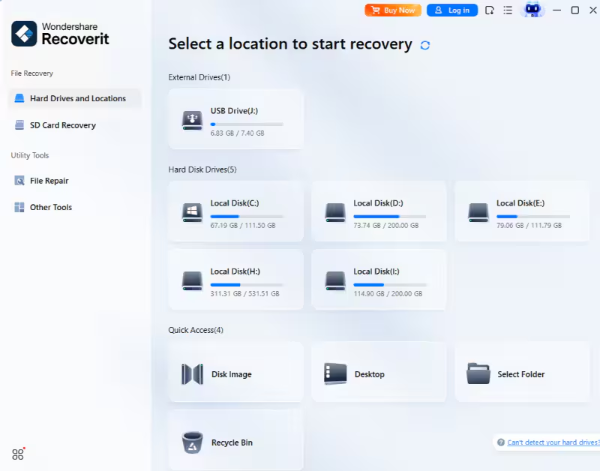
Data Recovery Basics: How to Restore Lost Files Without Causing More Damage Picture1
  • Technique

Data Recovery Basics: How to Restore Lost Files Without Causing More Damage

Do Son August 24, 2026 0

Learn the basics of data recovery, avoid common mistakes, and restore lost files safely with a simple step-by-step process.
CVE-2026-19478: GitLab Flaw Exploited in the Wild, PoC Public GitLab CVE-2026-19478 critical vulnerability warning showing unauthenticated attackers delete public projects exploited in the wild
  • Vulnerability Report

CVE-2026-19478: GitLab Flaw Exploited in the Wild, PoC Public

Do Son August 23, 2026 0

GitLab CVE-2026-19478 vulnerability lets unauthenticated attackers delete public projects. Exploited in the wild with public PoC. Patch now.
LinkedIn AI Slop Reduction: A Necessary Course Correction LinkedIn platform interface showing the new report AI slop button reducing artificial content views
  • Technology

LinkedIn AI Slop Reduction: A Necessary Course Correction

Do Son August 23, 2026 0

Discover how LinkedIn successfully reduced AI slop views by 40% using a new user reporting tool. Learn about the platform's shift in generative AI policies.
Take-Two Subpoenas Microsoft and Discord Over GTA VI “Cyberleek” Leaks Take-Two GTA VI leak subpoena Microsoft Discord Cyberleek Rockstar
  • Data Leak

Take-Two Subpoenas Microsoft and Discord Over GTA VI “Cyberleek” Leaks

Do Son August 23, 2026 0

Take-Two has subpoenaed Microsoft and Discord for account data, IPs, and device IDs tied to "Cyberleek," the source behind a wave of GTA VI gameplay leaks.
Apple Music AI Labels: Combating Algorithmically Generated Spam Apple Music AI labels interface displaying artificially generated track warnings
  • Technology

Apple Music AI Labels: Combating Algorithmically Generated Spam

Do Son August 23, 2026 0

Apple Music introduces mandatory AI labels to combat the flood of algorithmically generated spam songs, ensuring transparency and protecting creator royalties.
AliExpress Audio Fingerprinting Hijacks Your Bluetooth Diagram of hidden AliExpress audio fingerprinting scripts running a silent WebAudio browser fingerprint graph
  • Data Leak

AliExpress Audio Fingerprinting Hijacks Your Bluetooth

Do Son August 23, 2026 0

AliExpress audio fingerprinting uses hidden WebAudio scripts for browser fingerprinting, silently seizing your Bluetooth audio. Learn to block it.
ChatGPT iMessage Integration: A macOS Privacy Clash ChatGPT iMessage integration interface displaying privacy warnings and Mac access prompts
  • Data Leak

ChatGPT iMessage Integration: A macOS Privacy Clash

Do Son August 23, 2026 0

Discover how the new ChatGPT iMessage integration on macOS operates. Uncover the severe privacy concerns and Apple's potential security retaliation.

TikTok Secures $400 Million Privacy Settlement TikTok logo next to a gavel representing the massive $400 million US Department of Justice settlement
  • Technology

TikTok Secures $400 Million Privacy Settlement

Do Son August 23, 2026 0

TikTok and ByteDance finalize a massive $400 million settlement with the US Department of Justice, resolving severe violations of children's privacy laws.
EverShop CVE-2026-72843 Flaw Allows Unauthenticated Account Takeover Diagram showing the EverShop account takeover flow and eCommerce platform vulnerability mechanism.
  • Vulnerability Report

EverShop CVE-2026-72843 Flaw Allows Unauthenticated Account Takeover

Do Son August 23, 2026 0

A critical EverShop account takeover flaw, CVE-2026-72843, exposes systems to an eCommerce platform vulnerability. Update to version 2.2.1 immediately.
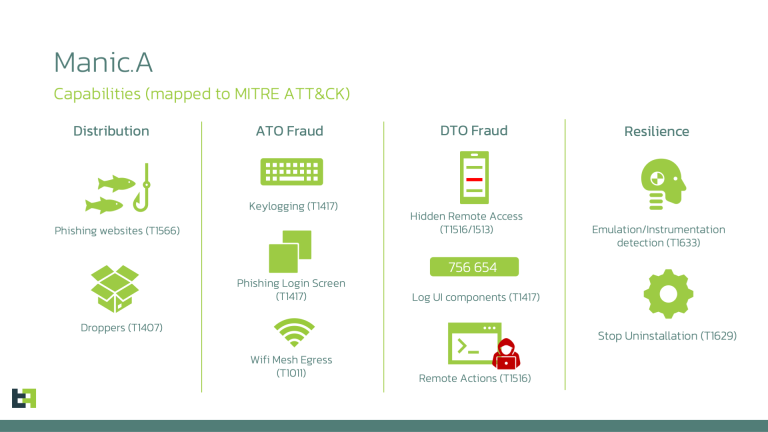
Manic Android Malware Steals Data Without Active Internet Manic Android malware utilizing offline mesh relay to steal data
  • Malware

Manic Android Malware Steals Data Without Active Internet

Do Son August 23, 2026 0

A new Manic Android malware campaign combines banking fraud and spyware, using a unique offline mesh relay to steal data even without internet access.
CVE-2026-77806: SPIP Unauthenticated RCE Exploited in the Wild as Public Exploit Lands SPIP CVE-2026-77806 unauthenticated remote code execution vulnerability exploited in the wild public exploit patch 4.4.21
  • Vulnerability Report

CVE-2026-77806: SPIP Unauthenticated RCE Exploited in the Wild as Public Exploit Lands

Do Son August 21, 2026 0

CVE-2026-77806 (CVSS 9.8) is a SPIP unauthenticated RCE exploited in the wild, with public exploit code now available. Update to SPIP 4.4.21 now.
Spring Data REST and Spring AI Vulnerabilities: Four High-Severity Flaws Patched Spring vulnerabilities advisory covering Spring Data REST and Spring AI four high severity flaws CVE-2026-47849
  • Vulnerability Report

Spring Data REST and Spring AI Vulnerabilities: Four High-Severity Flaws Patched

Do Son August 21, 2026 0

Four Spring vulnerabilities hit Spring Data REST and Spring AI, including CVE-2026-47849, a privilege escalation flaw. Patch to the fixed versions now.
CVE-2026-75501: Public PoC for Calix Router Flaw That Bypasses NAT and Firewall Protections Calix GS7 XGS router CVE-2026-75501 UPnP missing authentication flaw bypass NAT and firewall protections public PoC
  • Vulnerability Report

CVE-2026-75501: Public PoC for Calix Router Flaw That Bypasses NAT and Firewall Protections

Do Son August 21, 2026 0

CVE-2026-75501 exposes an unauthenticated UPnP service on Calix routers. Public PoC code shows how attackers bypass NAT and firewall protections.
CVE-2026-19598: Pods Plugin Flaw Enables Complete Site Takeover, Attacks Seen in the Wild Pods WordPress plugin CVE-2026-19598 privilege escalation vulnerability enabling complete site takeover attacks in the wild
  • Vulnerability Report

CVE-2026-19598: Pods Plugin Flaw Enables Complete Site Takeover, Attacks Seen in the Wild

Do Son August 21, 2026 0

CVE-2026-19598 (CVSS 9.8) in the Pods WordPress plugin enables complete site takeover. Wordfence is blocking attacks in the wild. Update now.
CVE-2026-50112: Apache CloudStack Flaw Allows Cross-Tenant Remote Code Execution on KVM Hosts Apache CloudStack CVE-2026-50112 remote code execution vulnerability on KVM hypervisor host security release advisory
  • Vulnerability Report

CVE-2026-50112: Apache CloudStack Flaw Allows Cross-Tenant Remote Code Execution on KVM Hosts

Do Son August 21, 2026 0

CVE-2026-50112 is a critical Apache CloudStack flaw enabling cross-tenant remote code execution as root on KVM hosts. Upgrade to 4.20.3.1 or 4.22.1.1.
IBM AIX Vulnerabilities: Remote Code Execution Flaws Hit CVSS 9.9 IBM AIX vulnerabilities remote code execution CVSS 9.9 security patch chart
  • Vulnerability Report

IBM AIX Vulnerabilities: Remote Code Execution Flaws Hit CVSS 9.9

Do Son August 21, 2026 0

IBM AIX vulnerabilities include remote code execution flaws rated up to CVSS 9.9. Patch AIX 7.2, 7.3, and PowerVM VIOS 4.1 now.
uutils coreutils stdbuf Flaw Lets Local Users Execute Arbitrary Code uutils coreutils vulnerability stdbuf LD_PRELOAD world-writable library flaw diagram
  • Vulnerability Report

uutils coreutils stdbuf Flaw Lets Local Users Execute Arbitrary Code

Do Son August 21, 2026 0

A uutils coreutils vulnerability in stdbuf uses a world-writable libstdbuf.so via LD_PRELOAD, letting local users execute arbitrary code.
RDK-B WebUI Vulnerabilities Let Attackers Bypass Login RDK-B WebUI vulnerabilities authentication bypass CVE-2026-19505 broadband gateway diagram
  • Vulnerability Report

RDK-B WebUI Vulnerabilities Let Attackers Bypass Login

Do Son August 21, 2026 0

Five RDK-B WebUI vulnerabilities let attackers bypass authentication and gain admin access on broadband gateways. No patch is available yet.
Leaked Corporate AWS Keys Expose Full Admin Rights leak
  • Data Leak

Leaked Corporate AWS Keys Expose Full Admin Rights

Do Son August 21, 2026 0

Truffle Security found leaked corporate AWS keys holding full control. See how leaked corporate AWS keys admin rights expose enterprise cloud accounts.
CVE-2026-18963: Unauthenticated Account Takeover Flaw Hits Keycloak Keycloak account takeover CVE-2026-18963 unauthenticated password reset flaw diagram
  • Vulnerability Report

CVE-2026-18963: Unauthenticated Account Takeover Flaw Hits Keycloak

Do Son August 21, 2026 0

A Keycloak account takeover flaw, CVE-2026-18963, lets attackers reset any user's password with no email verification. Update to 26.7.2 now.
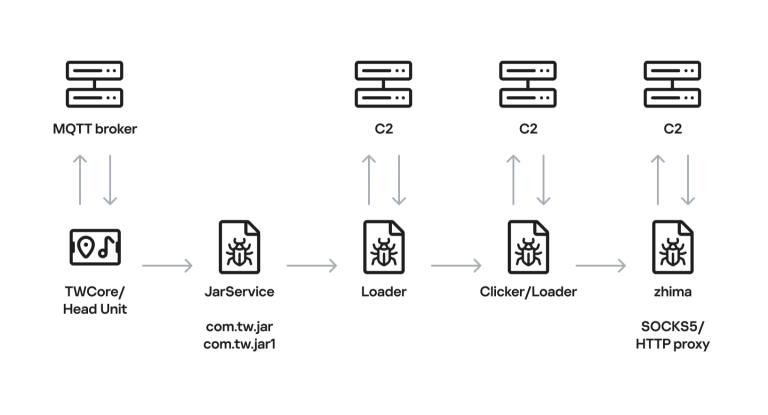
Android Head Unit Malware Recruits Vehicles into Botnet Diagram illustrating Android head unit malware and the Android head unit malware botnet infection chain
  • Malware

Android Head Unit Malware Recruits Vehicles into Botnet

Do Son August 21, 2026 0

Kaspersky exposed Android head unit malware turned into a botnet. Discover how this Android head unit malware botnet infects smart cars.
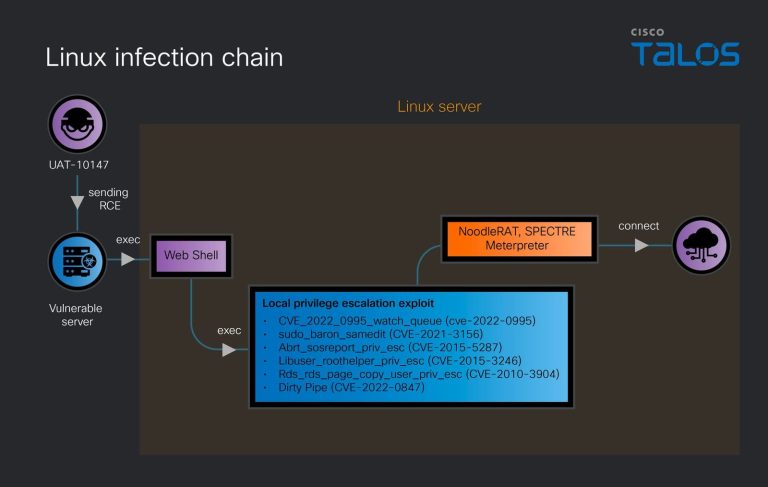
Cisco Talos Exposes UAT-10147 Agentic AI Attacks Diagram showing UAT-10147 agentic AI attacks and automated intrusion workflows
  • Cybercriminals

Cisco Talos Exposes UAT-10147 Agentic AI Attacks

Do Son August 21, 2026 0

Cisco Talos revealed how UAT-10147 agentic AI attacks target global servers. Learn how UAT-10147 agentic AI tools automate intrusions and data theft.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59360CVSS 9.8
    The killProcesses mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59361CVSS 9.8
    The cleanIptables mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2026-119923CVSS 9.3
    A heap-based buffer overflow in the TDS prelogin parser in the Babelfish for PostgreSQL extension versions 1.0-1.5, 2.1-2.15,...
    📅 Updated: Nov 7, 2026
  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121379CVSS 9.6
    The Tournamatch WordPress plugin before 4.7.1 does not validate or restrict the path of a previously stored profile...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.