Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
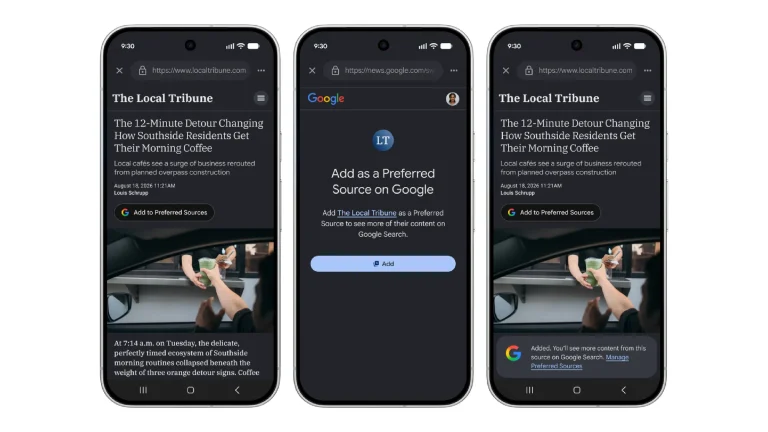
Google Preferred Sources: A New Era for News SEO Google Preferred Sources button and Gemini AI integration transforming Discover feed SEO strategies
  • Technology

Google Preferred Sources: A New Era for News SEO

Do Son August 21, 2026 0

Discover how the new Google Preferred Sources button empowers publishers, integrates Gemini into Discover, and transforms modern SEO strategies.
CVE-2026-67567 (CVSS 9.9): Red Hat Flaws Enable Privilege Escalation in ACM and FreeIPA Red Hat privilege escalation vulnerabilities CVE-2026-67567 ACM and FreeIPA CVE-2026-11861 CVE-2026-13097 advisory
  • Vulnerability Report

CVE-2026-67567 (CVSS 9.9): Red Hat Flaws Enable Privilege Escalation in ACM and FreeIPA

Do Son August 21, 2026 0

CVE-2026-67567 (CVSS 9.9) leads three Red Hat privilege escalation flaws in ACM and FreeIPA. Two FreeIPA bugs can reach full domain compromise.
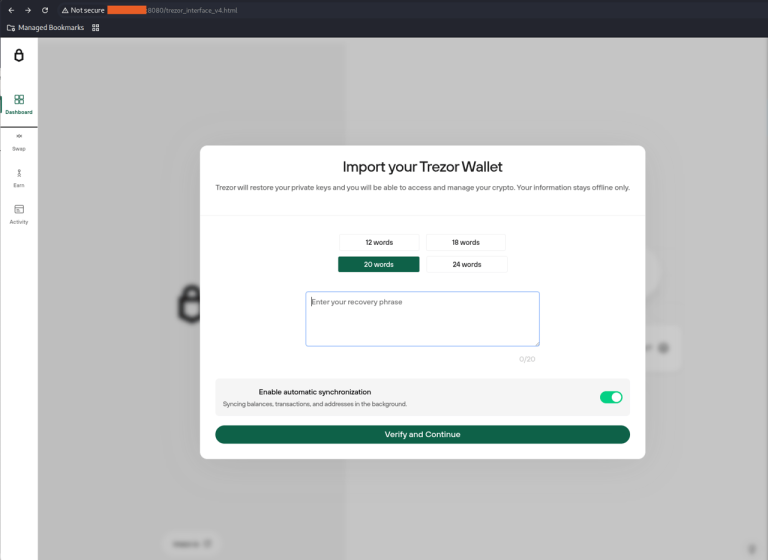
Operation ASTERIX: Crypto Scam Used AI and Fake Wallets Operation ASTERIX crypto fraud attack chain showing vishing calls and fake wallet apps stealing seed phrases
  • Cybercriminals

Operation ASTERIX: Crypto Scam Used AI and Fake Wallets

Do Son August 21, 2026 0

Rapid7 exposed Operation ASTERIX, a crypto fraud operation using AI, vishing, and fake wallet apps to steal seed phrases from validated holders.
CVE-2026-32475 (CVSS 9.8): Elementor Pro Flaw Risks Complete Site Compromise for 6 Million Sites Elementor Pro CVE-2026-32475 unauthenticated arbitrary file upload vulnerability risking complete site compromise on WordPress
  • Vulnerability Report

CVE-2026-32475 (CVSS 9.8): Elementor Pro Flaw Risks Complete Site Compromise for 6 Million Sites

Do Son August 21, 2026 0

CVE-2026-32475 (CVSS 9.8) is an Elementor Pro arbitrary file upload flaw risking complete site compromise across 6 million WordPress sites. Update to 4.2.2.
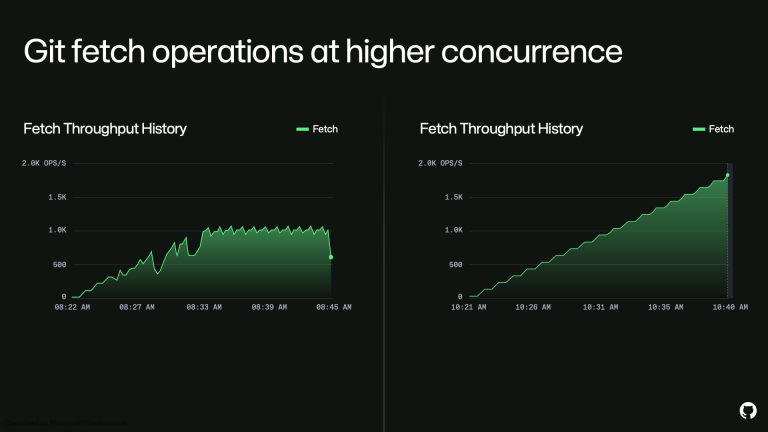
GitHub Infrastructure Outage: The True Cause GitHub infrastructure outage graph showing peak server loads and traffic spikes
  • Technology

GitHub Infrastructure Outage: The True Cause

Do Son August 21, 2026 0

Discover the real reasons behind the recent GitHub infrastructure outage. A massive surge to 2.9 billion monthly commits forced emergency Azure migrations.
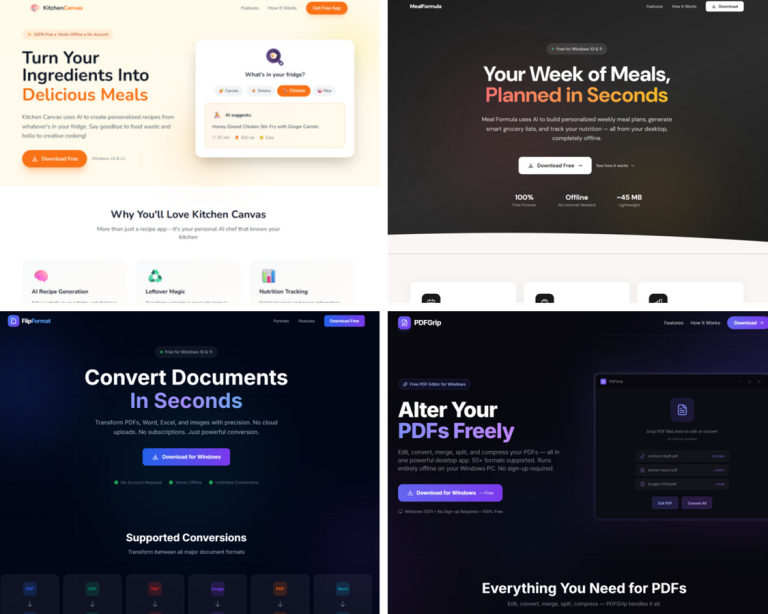
Projextor Malware Hides in Fake PDF and Recipe Apps Projextor Electron malware fake PDF converter and recipe apps diagram showing injected scripts and desktop capture
  • Malware

Projextor Malware Hides in Fake PDF and Recipe Apps

Do Son August 21, 2026 0

G DATA details Projextor, an Electron malware hidden in working PDF and recipe apps that runs injected scripts and captures the desktop.
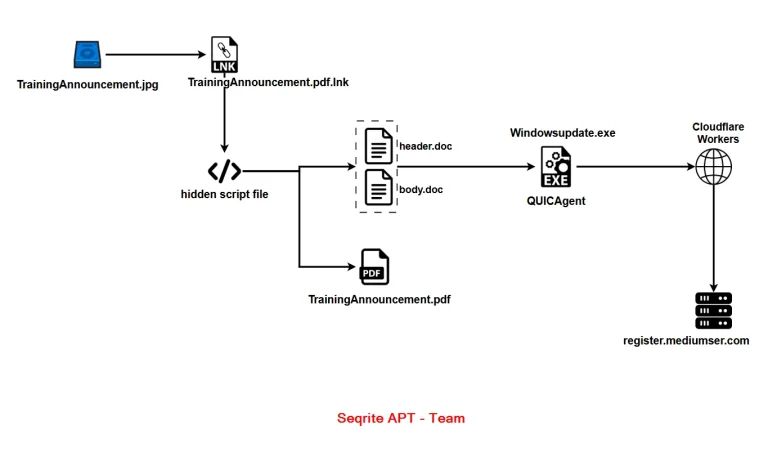
Operation QUICSILVER Targets Myanmar Government With Go Backdoor Operation QUICSILVER infection chain showing VHD lure delivering the QUICAgent Go backdoor to Myanmar government targets
  • Cybercriminals

Operation QUICSILVER Targets Myanmar Government With Go Backdoor

Do Son August 21, 2026 0

Seqrite links Operation QUICSILVER to a China-nexus actor deploying the QUICAgent Go backdoor against Myanmar government targets via a VHD lure.
Android 17 Memory Limits: Stricter App Constraints Android 17 memory limits diagram showing system terminating apps with severe memory leaks
  • Android

Android 17 Memory Limits: Stricter App Constraints

Do Son August 21, 2026 0

Discover how Android 17 memory limits will terminate apps with severe leaks. Learn about new tools to improve your app performance and stop memory leaks.
Windows 11 Gaming Issues Emerge After August Update Windows 11 gaming issues causing EXCEPTION_ACCESS_VIOLATION errors and system reboots
  • Windows

Windows 11 Gaming Issues Emerge After August Update

Do Son August 21, 2026 0

Microsoft investigates Windows 11 gaming issues causing crashes and stuttering in the 24H2 and 25H2 August updates. Learn how to fix these anomalies.
Sakura Internet Breach Exposes 1.36 Million Customer Accounts Sakura Internet data breach 1.36 million customer accounts Japan cloud provider
  • Data Leak

Sakura Internet Breach Exposes 1.36 Million Customer Accounts

Do Son August 21, 2026 0

Sakura Internet disclosed a breach of its customer management system affecting 1.36 million accounts, though passwords were hashed and salted and no ransom was demanded.
CVE-2026-77647 (CVSS 9.8): Unauthenticated SPIP RCE Exploited in the Wild SPIP CVE-2026-77647 unauthenticated remote code execution vulnerability exploited in the wild patch 4.4.20
  • Vulnerability Report

CVE-2026-77647 (CVSS 9.8): Unauthenticated SPIP RCE Exploited in the Wild

Do Son August 21, 2026 0

CVE-2026-77647 (CVSS 9.8) is an unauthenticated SPIP remote code execution flaw exploited in the wild. Update to SPIP 4.4.20 now.
CVE-2026-19586 (CVSS 9.3): Pre-Authentication OS Command Injection Hits Omada Gateways TP-Link Omada gateway CVE-2026-19586 pre-authentication OS command injection vulnerability advisory OpenVPN Server
  • Vulnerability Report

CVE-2026-19586 (CVSS 9.3): Pre-Authentication OS Command Injection Hits Omada Gateways

Do Son August 21, 2026 0

CVE-2026-19586 (CVSS 9.3) is a pre-authentication OS command injection in TP-Link Omada gateways running OpenVPN Server. Patch the firmware now.
CVE-2026-69836 (CVSS 10): Entra ID Remote Code Execution Flaw Microsoft Entra ID remote code execution vulnerability CVE-2026-69836 CVSS 10 exploited in the wild advisory
  • Vulnerability Report

CVE-2026-69836 (CVSS 10): Entra ID Remote Code Execution Flaw

Do Son August 21, 2026 0

CVE-2026-69836 is a CVSS 10 Entra ID remote code execution flaw exploited in the wild. Microsoft has fully mitigated it server-side.
CVE-2026-59270: Spring Security LDAP Flaw Lets Attackers Read or Modify Directory Entries Spring Security vulnerabilities advisory showing CVE-2026-59270 embedded LDAP flaw exposing in-memory directory entries
  • Vulnerability Report

CVE-2026-59270: Spring Security LDAP Flaw Lets Attackers Read or Modify Directory Entries

Do Son August 21, 2026 0

CVE-2026-59270 (CVSS 9.4) tops four Spring Security vulnerabilities. Its embedded LDAP flaw lets attackers read or modify in-memory directory entries.
CVE-2026-77176: Kata Containers Flaw Mounts Arbitrary Guest Rootfs Paths CVE-2026-77176 Kata Containers genpolicy vulnerability mounting arbitrary guest rootfs paths in Confidential Containers
  • Vulnerability Report

CVE-2026-77176: Kata Containers Flaw Mounts Arbitrary Guest Rootfs Paths

Do Son August 21, 2026 0

CVE-2026-77176 lets a malicious operator mount arbitrary guest rootfs paths in Kata Containers Confidential Containers. Upgrade to Kata 4.1.0.
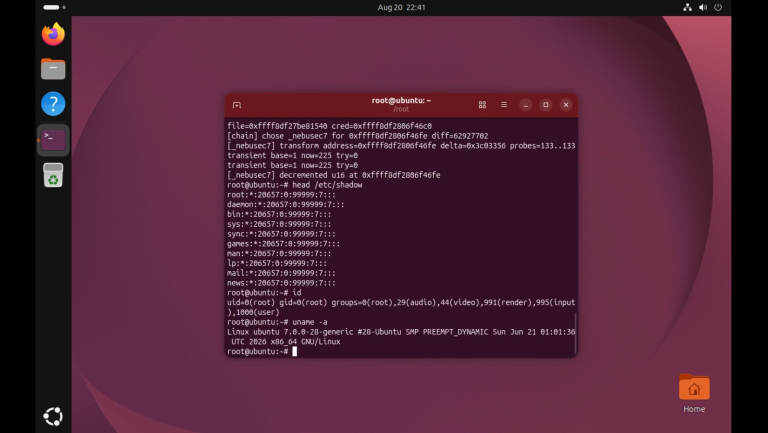
CVE-2026-52929: PoC Exploit Published for Linux SCTP Privilege Escalation Linux kernel CVE-2026-52929 SCTP privilege escalation proof-of-concept exploit code demonstration on Ubuntu
  • Vulnerability Report

CVE-2026-52929: PoC Exploit Published for Linux SCTP Privilege Escalation

Do Son August 21, 2026 0

Public PoC exploit code for CVE-2026-52929, a Linux kernel SCTP flaw, escalates to root. Full vulnerability details are now disclosed.
Spring GraphQL Vulnerabilities: Seven Flaws Patched, One Enables RCE Spring GraphQL vulnerabilities security advisory dashboard showing CVE-2026-59285 remote code execution
  • Vulnerability Report

Spring GraphQL Vulnerabilities: Seven Flaws Patched, One Enables RCE

Do Son August 20, 2026 0

Seven Spring GraphQL vulnerabilities were patched on August 20, including CVE-2026-59285, an unsafe deserialization flaw that can lead to remote code execution.
CVE-2026-72529 and CVE-2026-72530 Exploited in the Wild: TrueConf Server Under Attack TrueConf Server vulnerabilities CVE-2026-72529 CVE-2026-72530 exploited in the wild delivering PhantomCore malware advisory
  • Vulnerability Report

CVE-2026-72529 and CVE-2026-72530 Exploited in the Wild: TrueConf Server Under Attack

Do Son August 20, 2026 0

CISA confirms two TrueConf Server flaws, CVE-2026-72529 and CVE-2026-72530, are exploited in the wild to deliver PhantomCore malware. Patch now.
arrayref Rust Crate Hijacked in Supply Chain Attack With DPRK Infrastructure Overlap Rust supply chain attack on arrayref crate with proc-macro1 typosquat and DPRK infrastructure overlap
  • Cybercriminals

arrayref Rust Crate Hijacked in Supply Chain Attack With DPRK Infrastructure Overlap

Do Son August 20, 2026 0

A Rust supply chain attack poisoned arrayref and two other crates to run malware at build time. Wiz ties the infrastructure to DPRK campaigns.
CVE-2026-76017: Critical Use-After-Free in Chrome Headlines 7 Security Fixes Chrome use-after-free vulnerability CVE-2026-76017 critical Chromoting flaw among 7 security fixes advisory
  • Vulnerability Report

CVE-2026-76017: Critical Use-After-Free in Chrome Headlines 7 Security Fixes

Do Son August 20, 2026 0

Google patches CVE-2026-76017, a critical use-after-free in Chrome, among 7 security fixes. Update to 151.0.7922.173 or later now.

Spring Integration Vulnerabilities Demand Immediate Action Diagram illustrating Spring Integration vulnerabilities CVE-2026-59307 and CVE-2026-59324
  • Vulnerability Report

Spring Integration Vulnerabilities Demand Immediate Action

Do Son August 20, 2026 0

Two critical Spring Integration vulnerabilities, CVE-2026-59307 and CVE-2026-59324, expose systems to remote code execution and data leakage. Update now.

CVE-2026-14950 (CVSS 9.8): Frauscher FDS102 Flaw Enables Unauthorized Continued Access Frauscher FDS102 vulnerabilities CVE-2026-14950 unauthorized continued access railway diagram
  • Vulnerability Report

CVE-2026-14950 (CVSS 9.8): Frauscher FDS102 Flaw Enables Unauthorized Continued Access

Do Son August 20, 2026 0

Frauscher FDS102 vulnerabilities include CVE-2026-14950 (CVSS 9.8), a session flaw enabling unauthorized continued access. Update to v2.14.0.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59360CVSS 9.8
    The killProcesses mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59361CVSS 9.8
    The cleanIptables mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2026-119923CVSS 9.3
    A heap-based buffer overflow in the TDS prelogin parser in the Babelfish for PostgreSQL extension versions 1.0-1.5, 2.1-2.15,...
    📅 Updated: Nov 7, 2026
  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121379CVSS 9.6
    The Tournamatch WordPress plugin before 4.7.1 does not validate or restrict the path of a previously stored profile...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.