
 Do Son
Security researcher Crnkovic has disclosed three critical vulnerabilities — CVE-2025-9152, CVE-2025-10611, and CVE-2025-9804 — in WSO2 API...
Latest news

In a study titled “TEE.fail: Breaking Trusted Execution Environments via DDR5 Memory Bus Interposition,” researchers from Georgia...

The AhnLab Security Intelligence Center (ASEC) has published a new report revealing that the Trigona ransomware threat...

Researchers from the Internet Initiative Japan (IIJ) have analyzed a previously unknown malware loader that can simultaneously...

A new ransomware family called Midnight has emerged, borrowing heavily from the Babuk ransomware framework — but...

The HelixGuard Threat Intelligence Team has uncovered a widespread supply chain compromise affecting the Visual Studio Code...

Google has announced that starting with Chrome 154, releasing in October 2026, the browser will automatically enable...

Researchers from Exodus Intelligence, led by Michele Campa, have disclosed a privilege-escalation vulnerability in Microsoft’s Cloud Files...

Researchers at BitSight have uncovered a long-running spam campaign operated by a Brazilian threat group behind the...

 cybernewswire
Tel Aviv, Israel, 29th October 2025, CyberNewsWire

The Mispadu banking trojan, infamous for its attacks on Latin American countries, is aggressively broadening its targets

Industrial Espionage: The most alarming scenario is a targeted attack designed to steal sensitive data (credentials, design plans, etc.)

This vulnerability (CVE-2024-1933) affects TeamViewer Client for macOS versions earlier than 15.52.

A newly discovered malware loader is making waves in the cybercrime world, helping the notorious Agent Tesla infostealer expand its reach

Designated CVE-2024-27981, the vulnerability carries a "Critical" CVSS rating of 9.1 out of 10. It exists in self-hosted Linux installations

Security researcher Yann Gascuel has detailed a critical privilege escalation vulnerability (CVE-2023-42931) affecting the macOS versions

A serious security vulnerability (CVE-2024-1538, CVSS 8.8) has been discovered in the File Manager plugin for WordPress

GEOBOX system is designed for simplicity. With a user manual providing step-by-step instructions, even those with limited technical

Security researcher ma4ter has revealed details of a dangerous security vulnerability (CVE-2024-20767) in Adobe ColdFusion

over 170,000 Python developers have fallen victim to a sophisticated malware scheme designed to steal sensitive data

CVE-2024-29937 in Network File System (NFS) implementations used by popular BSD-derived operating systems, including OpenBSD and FreeBSD

GoFetch attack leverages a new type of chosen-input attack, ingeniously using DMP behavior to extract keys from cryptographic algorithms

OpenVPN has released critical security updates (version 2.6.10) to address a series of vulnerabilities in its Windows software

threat actors exploit malvertising and a custom malware loader built in Go to deliver the notorious Rhadamanthys information stealer.

The vulnerability (CVE-2024-23755, CVSS 8.4) affects both macOS and Windows versions of the ClickUp Desktop app.

The employment of WINELOADER, endowed with features overlapping with other APT29 malware families such as BURNTBATTER and MUSKYBEAT
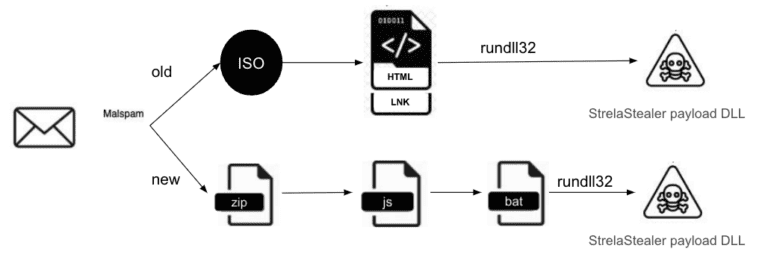
Researchers at Unit 42 have uncovered a major new attack campaign deploying an updated version of the StrelaStealer malware

CVE-2024-29190 allows attacker to trick the MobSF server into making requests to internal or otherwise inaccessible resources within your network

AcidPour malware, like its predecessor, is tailored to attack Linux-based systems. This broad category includes everything

A serious security vulnerability (CVE-2024-30156) has been uncovered in Varnish Cache, a widely used tool for boosting website speed
For years, drones have been seen as a technological marvel, offering a new perspective for photography, delivery,...

a trend in China-linked cyberattacks: a sustained focus on compromising Operational Technology environments within critical infrastructure