Skip to content
October 16, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Blackout for ALPHV: DOJ Shuts Down Notorious Ransomware Gang ALPHV ransomware
  • Cyber Security

Blackout for ALPHV: DOJ Shuts Down Notorious Ransomware Gang

Do Son December 19, 2023 0
The U.S. Department of Justice has announced the FBI’s successful infiltration into the infrastructure of the ransomware...
Read More Read more about Blackout for ALPHV: DOJ Shuts Down Notorious Ransomware Gang
HAECHI IV Bites: Global Operation Snags 3,500 Cybercriminals, Seizes Millions Operation HAECHI IV
  • Cyber Security

HAECHI IV Bites: Global Operation Snags 3,500 Cybercriminals, Seizes Millions

Do Son December 19, 2023 0
Interpol announced that the international law enforcement operation “Operation HAECHI IV,” aimed at combating financial crimes online,...
Read More Read more about HAECHI IV Bites: Global Operation Snags 3,500 Cybercriminals, Seizes Millions
Cyberattackers Target South Korean Inboxes with LNK Weaponry Konni group
  • Cyber Security
  • Malware

Cyberattackers Target South Korean Inboxes with LNK Weaponry

Do Son December 19, 2023 0
Cybersecurity specialists at Qi An Xin have unearthed malicious LNK files specifically targeting users in South Korea....
Read More Read more about Cyberattackers Target South Korean Inboxes with LNK Weaponry
The Triple Threat Found in Apache Superset CVE-2023-49734
  • Vulnerability

The Triple Threat Found in Apache Superset

Do Son December 19, 2023 0
Apache Superset, a cutting-edge business intelligence web application, has recently been under the cybersecurity spotlight due to...
Read More Read more about The Triple Threat Found in Apache Superset
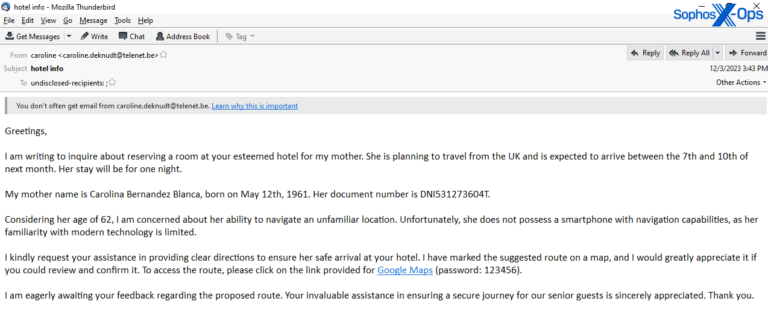
Sophos X-Ops Alerts: ‘Inhospitality’ Malspam Targets Hotels with Deceptive Tactics Inhospitality malspam
  • Malware

Sophos X-Ops Alerts: ‘Inhospitality’ Malspam Targets Hotels with Deceptive Tactics

Do Son December 19, 2023 0
Sophos X-Ops is warning the hospitality industry that the “Inhospitality” malspam campaign represents a cunning blend of...
Read More Read more about Sophos X-Ops Alerts: ‘Inhospitality’ Malspam Targets Hotels with Deceptive Tactics
Iranian Espionage Seedworm Targets Egypt, Sudan, and Tanzania Iranian Espionage Seedworm group
  • Cyber Security
  • Malware

Iranian Espionage Seedworm Targets Egypt, Sudan, and Tanzania

Do Son December 19, 2023 0
In the evolving landscape of cyber threats, the Iranian espionage group Seedworm (also known as Muddywater) has...
Read More Read more about Iranian Espionage Seedworm Targets Egypt, Sudan, and Tanzania
Secret Code in Commits: GitHub Hackers Exposed abuse GitHub Gists
  • Malware

Secret Code in Commits: GitHub Hackers Exposed

Do Son December 19, 2023 0
Researchers from ReversingLabs have identified two novel techniques: one involves misusing GitHub Gists, and the other utilizes...
Read More Read more about Secret Code in Commits: GitHub Hackers Exposed
Cyber Alert: Smishing Triad Gang’s Fake UAE Authority SMS Scam Smishing Triad Gang
  • Cyber Security
  • Malware

Cyber Alert: Smishing Triad Gang’s Fake UAE Authority SMS Scam

Do Son December 19, 2023 0
In a recent revelation, cybersecurity firm Resecurity has uncovered a sinister fraudulent campaign orchestrated by the notorious...
Read More Read more about Cyber Alert: Smishing Triad Gang’s Fake UAE Authority SMS Scam
Inside TeraLeak: Exploring Thousands of Terabytes of Apple’s Hidden iOS Prototypes Apple TestFlight leak
  • Data Leak

Inside TeraLeak: Exploring Thousands of Terabytes of Apple’s Hidden iOS Prototypes

Do Son December 19, 2023 0
Data collected from the servers of Apple TestFlight service between 2012 and 2015 has been leaked online....
Read More Read more about Inside TeraLeak: Exploring Thousands of Terabytes of Apple’s Hidden iOS Prototypes
CVE-2023-6817: Linux Kernel NetFilter Flaw Opens Root Access CVE-2023-6817
  • Vulnerability

CVE-2023-6817: Linux Kernel NetFilter Flaw Opens Root Access

Do Son December 19, 2023 0
Recently, a significant security vulnerability in the Linux NetFilter kernel has been discovered, allowing unprivileged local users...
Read More Read more about CVE-2023-6817: Linux Kernel NetFilter Flaw Opens Root Access
Adobe’s Critical Response: Patching the CVE-2023-50164 Vulnerability in AEM Forms CVE-2023-50164 AEM Forms
  • Vulnerability

Adobe’s Critical Response: Patching the CVE-2023-50164 Vulnerability in AEM Forms

Do Son December 18, 2023 0
In a proactive response to a newly discovered security flaw, Adobe has taken decisive action by releasing...
Read More Read more about Adobe’s Critical Response: Patching the CVE-2023-50164 Vulnerability in AEM Forms
Patch Now! Ladon, AnyDesk, and More Lurk in Unpatched ActiveMQ Servers AnyDesk
  • Cyber Security
  • Vulnerability

Patch Now! Ladon, AnyDesk, and More Lurk in Unpatched ActiveMQ Servers

Do Son December 18, 2023 0
In November 2023, the cybersecurity landscape faced a formidable challenge when the AhnLab Security Emergency Response Center...
Read More Read more about Patch Now! Ladon, AnyDesk, and More Lurk in Unpatched ActiveMQ Servers
CVE-2023-48795: SSH Flaw Lets Hackers Strip Secrets From Your Connection CVE-2023-48795 - Terrapin Attack OpenSSH RCE, ProxyCommand Injection
  • Vulnerability

CVE-2023-48795: SSH Flaw Lets Hackers Strip Secrets From Your Connection

Do Son December 18, 2023 0
In the ever-evolving landscape of cybersecurity, a new threat has emerged, targeting the integrity of Secure Shell...
Read More Read more about CVE-2023-48795: SSH Flaw Lets Hackers Strip Secrets From Your Connection
Smart Contract Breach: Hacker Cracks Code, Faces Justice hacker Crypto Exchange
  • Cyber Security

Smart Contract Breach: Hacker Cracks Code, Faces Justice

Do Son December 18, 2023 0
Former senior cybersecurity engineer of an American IT company, Shakeeb Ahmed, has admitted his guilt in hacking...
Read More Read more about Smart Contract Breach: Hacker Cracks Code, Faces Justice
Phishing Feast: Storm-0539 Targets Retailers for Holiday Haul Storm-0539 group
  • Cyber Security

Phishing Feast: Storm-0539 Targets Retailers for Holiday Haul

Do Son December 18, 2023 0
Microsoft has issued a warning about the escalating activities of the cybercriminal group Storm-0539, which specializes in...
Read More Read more about Phishing Feast: Storm-0539 Targets Retailers for Holiday Haul
Atlassian Companion Update Now! PoC for CVE-2023-22524 Puts Businesses on High Alert CVE-2023-22524 PoC
  • Vulnerability

Atlassian Companion Update Now! PoC for CVE-2023-22524 Puts Businesses on High Alert

Do Son December 18, 2023 0
A recent revelation has shed light on a critical flaw within the Atlassian Companion App, an optional...
Read More Read more about Atlassian Companion Update Now! PoC for CVE-2023-22524 Puts Businesses on High Alert
32% Surge in US Mobile Fraud! Banking Malware Run Rampant as Market Booms Mobile Banking malware
  • Malware

32% Surge in US Mobile Fraud! Banking Malware Run Rampant as Market Booms

Do Son December 18, 2023 0
In the fast-evolving world of mobile banking, a new report sheds light on a growing peril –...
Read More Read more about 32% Surge in US Mobile Fraud! Banking Malware Run Rampant as Market Booms
Data Breach Alert: MongoDB Customer Hit, Logs Accessed MongoDB data breach
  • Cyber Security
  • Data Leak

Data Breach Alert: MongoDB Customer Hit, Logs Accessed

Do Son December 18, 2023 0
MongoDB, a company specializing in the development of database software, disclosed on December 16 an unauthorized breach...
Read More Read more about Data Breach Alert: MongoDB Customer Hit, Logs Accessed
Backup Migration Plugin Breach: Hackers Target WordPress Sites (Public PoC) CVE-2023-6553 PoC
  • Vulnerability

Backup Migration Plugin Breach: Hackers Target WordPress Sites (Public PoC)

Do Son December 16, 2023 0
Hackers are attempting to exploit a recently patched critical vulnerability (CVE-2023-6553) in the WordPress Backup Migration plugin...
Read More Read more about Backup Migration Plugin Breach: Hackers Target WordPress Sites (Public PoC)
CVE-2023-49954: Critical SQL Injection Vulnerability in 3CX CRM Integration CVE-2023-49954
  • Vulnerability

CVE-2023-49954: Critical SQL Injection Vulnerability in 3CX CRM Integration

Do Son December 16, 2023 0
In the fast-paced world of Internet communications, staying ahead of security threats is not just a choice...
Read More Read more about CVE-2023-49954: Critical SQL Injection Vulnerability in 3CX CRM Integration
IDEMIA’s Big Glitch: Critical Vulnerabilities Expose Biometric Terminals IDEMIA Vulnerabilities
  • Vulnerability

IDEMIA’s Big Glitch: Critical Vulnerabilities Expose Biometric Terminals

Do Son December 16, 2023 0
IDEMIA, a prominent player in this field, recently issued an advisory that highlights critical vulnerabilities in its...
Read More Read more about IDEMIA’s Big Glitch: Critical Vulnerabilities Expose Biometric Terminals
PoC Released for SharePoint Pre-Auth RCE Chain (CVE-2023-29357 & CVE-2023-24955) CVE-2023-29357 & CVE-2023-24955 PoC
  • Vulnerability

PoC Released for SharePoint Pre-Auth RCE Chain (CVE-2023-29357 & CVE-2023-24955)

Do Son December 16, 2023 0
Two vulnerabilities in Microsoft SharePoint Server have recently come under the spotlight, thanks to the detailed work...
Read More Read more about PoC Released for SharePoint Pre-Auth RCE Chain (CVE-2023-29357 & CVE-2023-24955)
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-102764CVSS 9.3
    The vulnerability exists within internal components of BeyondTrust’s Remote Support product. The components did not adequately validate the...
    Admin intel📅 Updated: Oct 16, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    Watchtower Verified📅 Updated: Oct 16, 2026
  • CVE-2020-13125CVSS 7.2
    An issue was discovered in the "Ultimate Addons for Elementor" plugin before 1.24.2 for WordPress, as exploited in...
    Watchtower Verified📅 Updated: Oct 16, 2026
  • CVE-2020-13126CVSS 9.9
    An issue was discovered in the Elementor Pro plugin before 2.9.4 for WordPress, as exploited in the wild...
    Watchtower Verified📅 Updated: Oct 16, 2026
  • CVE-2019-20180CVSS 8.0
    The TablePress plugin for WordPress is vulnerable to CSV Injection in versions up to and including 1.14 via...
    Watchtower Verified📅 Updated: Oct 16, 2026
  • CVE-2026-106931CVSS 8.5
    SiteGuard Server Edition contains an OS command injection vulnerability, which may allow an attacker to execute arbitrary OS...
    Admin intel📅 Updated: Oct 15, 2026
  • CVE-2025-61624CVSS 6.0
    An Improper Limitation of a Pathname to a Restricted Directory (\'Path Traversal\') [CWE-22] vulnerability in Fortinet FortiOS 7.6.0...
    Admin intel📅 Updated: Oct 15, 2026
  • CVE-2026-110447CVSS 9.2
    Collabora Online Built-in CODE Server before 26.4.303 (richdocumentscode), a Nextcloud app, allows remote code execution, as exploited in...
    Watchtower Verified📅 Updated: Oct 15, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-102764CVSS 9.3
    The vulnerability exists within internal components of BeyondTrust’s Remote Support product. The components did not adequately validate the...
    Admin intel📅 Updated: Oct 16, 2026
  • CVE-2026-94169CVSS 10.0
    Improper Control of Generation of Code ('Code Injection') vulnerability in Theme-one The Grid the-grid allows Command Injection.This issue...
    📅 Updated: Oct 16, 2026
  • CVE-2026-94388CVSS 9.3
    Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in halfdata Green Popups halfdata-green-popups...
    📅 Updated: Oct 16, 2026
  • CVE-2026-104730CVSS 9.8
    The Sunshine Photo Cart – Client Photo Gallery & Photo Proofing for Photographers plugin for WordPress is vulnerable...
    📅 Updated: Oct 16, 2026
  • CVE-2026-89079CVSS 9.8
    The Theme My Login plugin for WordPress is vulnerable to privilege escalation via account takeover in versions up...
    📅 Updated: Oct 16, 2026
  • CVE-2026-103768CVSS 9.8
    The ELEX WordPress HelpDesk & Customer Ticketing System plugin for WordPress is vulnerable to Arbitrary File Upload in...
    📅 Updated: Oct 16, 2026
  • CVE-2026-16438CVSS 9.4
    Incorrect Privilege Assignment vulnerability in Mitsubishi Electric GENESIS64 versions 10.97.3 and prior, ICONICS Suite versions 10.97.3 and prior,...
    📅 Updated: Oct 16, 2026
  • CVE-2026-16436CVSS 9.2
    Weak Password Recovery Mechanism for Forgotten Password vulnerability in Mitsubishi Electric GENESIS versions 11.03 and prior, GENESIS64 versions...
    📅 Updated: Oct 16, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.