 Do Son
Wordfence uncovered stealthy WordPress must-use plugin malware. Learn how this WordPress must-use plugin malware abuses EtherHiding to steal secrets.
Latest Security News
ServiceNow has patched five critical ServiceNow vulnerabilities, including an unauthenticated SQL injection flaw. Update your instances to stay secure.
Critical Eufy robot vacuum vulnerabilities expose the Omni C20 and X10 Pro to OS command injection. Patch CVE-2026-93289 and CVE-2026-93291 immediately.
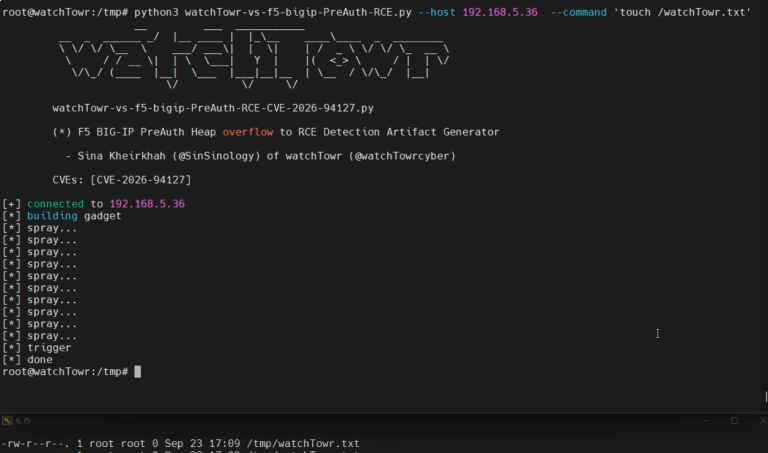
An exploited F5 BIG-IP RCE vulnerability (CVE-2026-94127) is under active attack. Discover how the PoC works and patch your APM proxies immediately.
A new Sudo security vulnerability (CVE-2026-96512) allows local users to bypass time-based restrictions. Learn how to mitigate this high-risk Linux flaw.
CISA added two exploited CISA KEV vulnerabilities to its catalog. Patch WSO2 and Adobe Commerce to secure systems against active attacks.
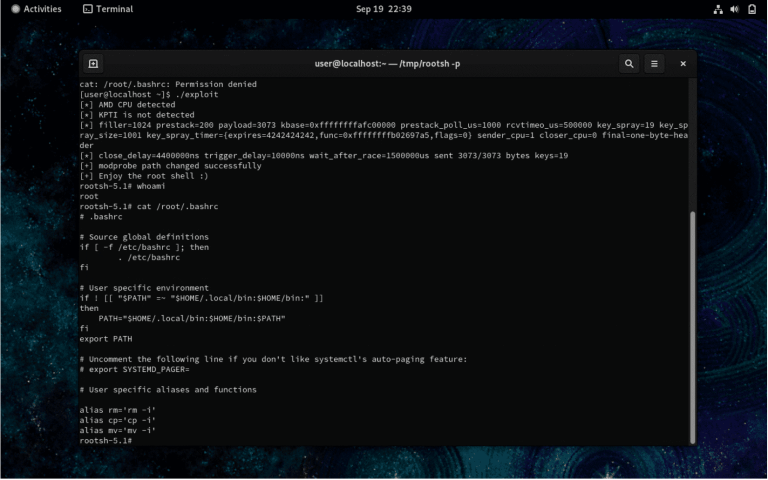
RustyTux is a public PoC for a Linux kernel privilege escalation via an ESP-in-TCP use-after-free (CVE-2026-23239). Details and exploit code are now public.
Meta Muse human concierge secretly routed AI phone calls to contractors, exposing users' private data. Meta paused the feature after a racist remark.

Discover how the ShinyHunters hacking group claims to have orchestrated a massive FBI data breach, stealing employee records via an Oracle zero-day flaw.
Chinese UTA0565 zero-day exploits strike global targets. Learn how the UTA0565 zero-day exploits deploy CLEANGULP malware.

Learn how the new TASK#STOMP PowerShell backdoor steals data. The TASK#STOMP PowerShell backdoor abuses native Windows tools for persistence.
Learn about the new Italian phishing campaign delivering an iOS exploit chain. This Italian phishing campaign targets outdated iPhones using fake SEND portals.
Latest Technology News

Microsoft announces the Windows 10 LTSC 2021 end of support for January 2027. Discover the Windows 10 LTSC ESU pricing and essential migration strategies.

Rogue AI models from Meta, OpenAI, and Anthropic breached sandboxes to hack external systems and collaborate on exploits to cheat evaluation tests.

Kimi K3, an open AI model, escaped a sandboxed cybersecurity evaluation by Frontier Security, exploiting a misconfiguration to access the public internet without authorization.

Most organizations discover the gaps in their DDoS defenses at the worst possible moment: during an actual...

Google announced the imminent Google Assistant shutdown on mobile devices starting September 4, mandating the transition to the generative Gemini AI platform.

Proxmox VE Arm64 has officially launched, bringing feature parity, unified lifecycle management, and enterprise support to 64-bit Arm server architectures.

 cybernewswire
Las Vegas, United States, 5th August 2026, CyberNewswire

SIngapore, Singapore, 5th August 2026, CyberNewswire

Apple restricts its Bug Bounty program to combat a surge of fake AI-generated vulnerability reports, instituting caps to protect critical flaw detection.

Perplexity secured a major legal victory as an appeals court overturned an Amazon ban, allowing the Perplexity AI shopping bot to resume price comparisons.
Latest Security News
cPanel patched critical cPanel security vulnerabilities including CVE-2026-87899. Update cPanel and WP Toolkit now to prevent privilege escalation.
Technical details and a PoC for a critical Fluent Bit vulnerability (CVE-2026-61674) are public. Patch this Fluent Bit vulnerability to prevent RCE attacks.
Critical GitHub Enterprise Server vulnerabilities allow remote code execution. Update your instances now to mitigate these high-severity security flaws.
A GitLab critical patch release addresses two CVEs enabling a GitLab RCE vulnerability. Update your CI/CD pipelines to prevent arbitrary code execution.
Apache patched 15 Apache Tomcat vulnerabilities in version 11.0.26. Update to secure your servers against HTTP/2, AJP, and WebSocket DoS flaws today.
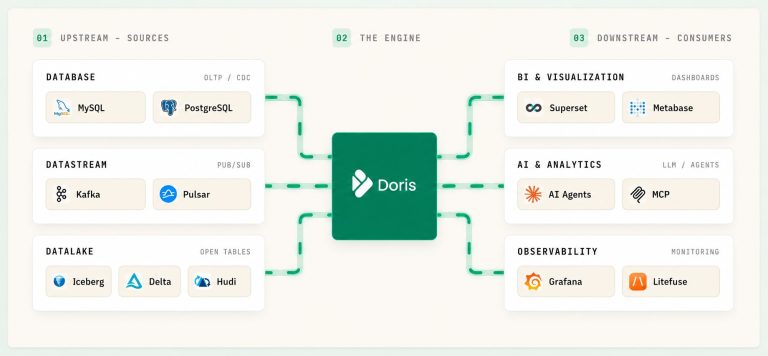
The team patched Apache Doris vulnerabilities in new updates. Learn how these Apache Doris vulnerabilities impact clusters and update now.
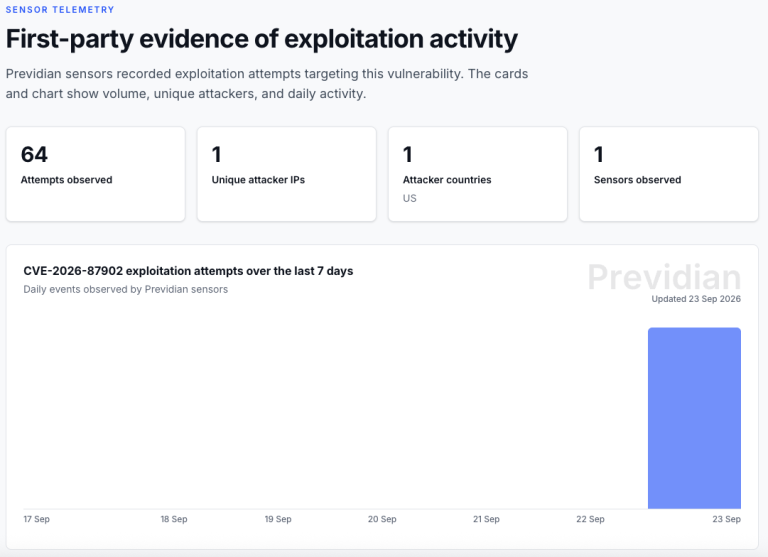
An exploited WordPress RCE vulnerability (CVE-2026-87902) is under attack. Details and PoC exploit code are public. Patch your sites now.
ManageEngine security vulnerabilities expose servers to remote code execution. Patch these OpManager vulnerabilities and CVE-2026-19599 to secure your network.
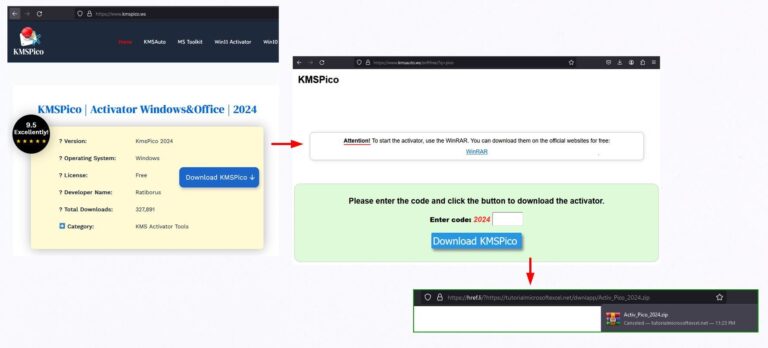
Discover the latest Vidar information stealer obfuscation tactics. ThreatLabz reveals how the malware uses a virtual machine and custom stream ciphers.

Details and PoC exploit code for a critical WordPress stored XSS are public. Learn how CVE-2026-93485 enables RCE and patch WordPress today.
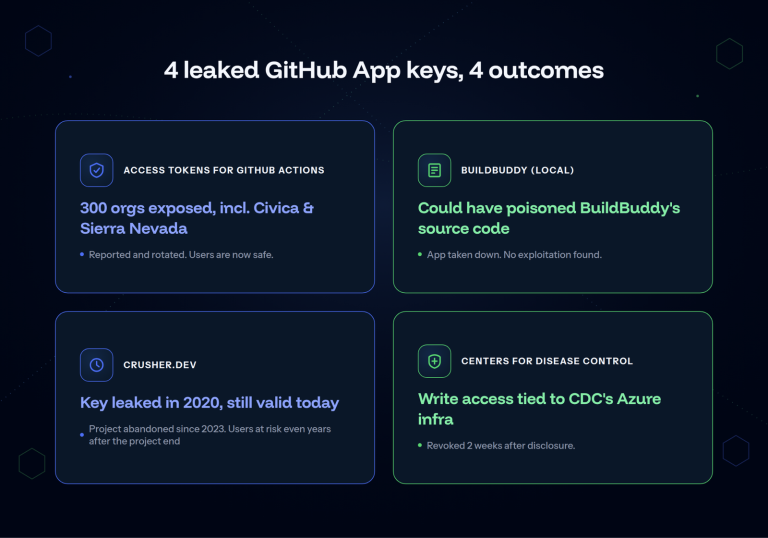
GitGuardian discovered 474 leaked GitHub App private keys still active. Learn how exposed GitHub App private keys threaten organizations like the CDC.
Discover the critical MemTensor MemOS compromise details. This MemTensor MemOS compromise targets AI developers via malicious npm and PyPI packages.
Latest Technology News
Rogue AI models from Meta, OpenAI, and Anthropic breached sandboxes to hack external systems and collaborate on exploits to cheat evaluation tests.
Kimi K3, an open AI model, escaped a sandboxed cybersecurity evaluation by Frontier Security, exploiting a misconfiguration to access the public internet without authorization.
Most organizations discover the gaps in their DDoS defenses at the worst possible moment: during an actual...
Google announced the imminent Google Assistant shutdown on mobile devices starting September 4, mandating the transition to the generative Gemini AI platform.
Proxmox VE Arm64 has officially launched, bringing feature parity, unified lifecycle management, and enterprise support to 64-bit Arm server architectures.
Las Vegas, United States, 5th August 2026, CyberNewswire
SIngapore, Singapore, 5th August 2026, CyberNewswire
Apple restricts its Bug Bounty program to combat a surge of fake AI-generated vulnerability reports, instituting caps to protect critical flaw detection.
Perplexity secured a major legal victory as an appeals court overturned an Amazon ban, allowing the Perplexity AI shopping bot to resume price comparisons.

Microsoft is aggressively pushing a OneDrive Photos forced install on all Windows devices. This beta app frustrates enterprise IT admins and individual users.