 Do Son
SolarWinds Observability vulnerabilities allow RCE via CVE-2026-28324. Update to version 2026.2.3 to secure your monitoring infrastructure today.
Latest Security News
Technical details and a PoC for the D-Link DAP-1360 vulnerability (CVE-2026-95675) are public. Learn how this unauthenticated flaw impacts legacy routers.
NVIDIA patched critical NVIDIA Infrastructure Controller vulnerabilities across Linux builds. Learn how CVE-2026-65113 impacts systems and update now.
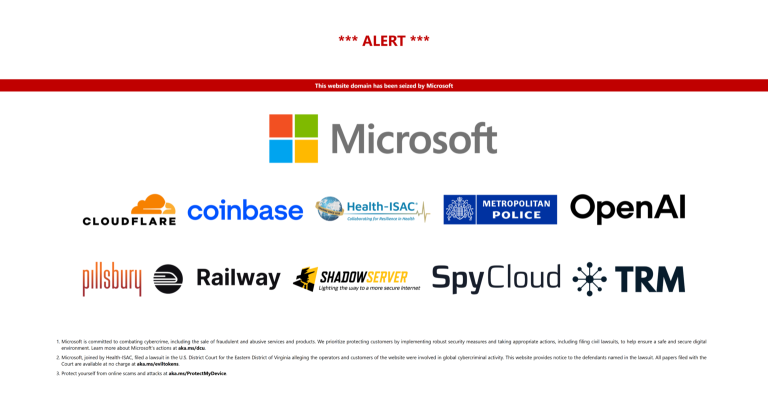
Microsoft led a coalition disrupting EvilTokens cybercrime platform. Learn how the EvilTokens cybercrime platform used AI and device code phishing.
An exploited BIG-IP APM vulnerability tracked as CVE-2026-94127 allows RCE attacks. Secure your BIG-IP APM vulnerability deployments with new F5 hotfixes.
A critical ManageEngine ADSelfService Plus vulnerability (CVE-2026-74849) allows system compromise. Update to build 7001 to secure your endpoints.
An exploited Check Point VPN vulnerability allows remote code execution. Patch this Check Point VPN vulnerability now to block active in-the-wild attacks.
WordPress 7.1.2 patches a critical WordPress RCE vulnerability (CVE-2026-87902). Update your site to prevent conditional remote code execution.
A critical exploited Check Point Management vulnerability (CVE-2026-93616) allows attackers to execute arbitrary scripts. Secure your servers now.
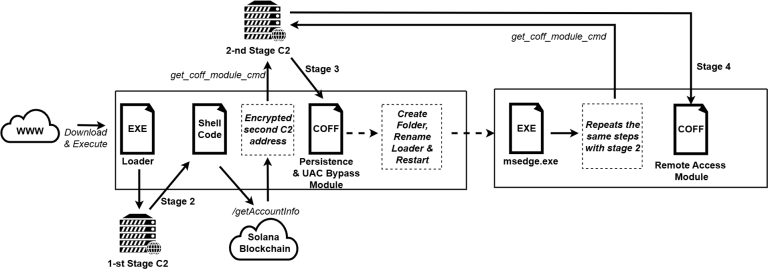
Learn how the MovieReaper malware compromises torrents. Experts warn that MovieReaper malware torrent attacks use Solana blockchain for command and control.
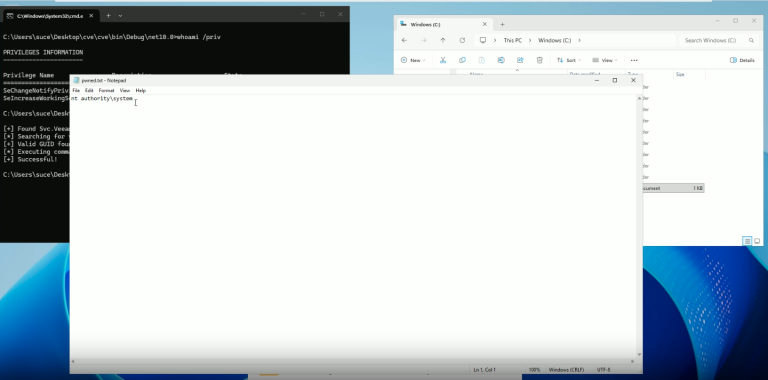
A critical exploited Veeam Agent vulnerability (CVE-2026-32996) is under active attack. Public PoC exploit code has been disclosed. Update systems now.

Explore how the Operation RapidRust APT36 malware campaign by Zscaler ThreatLabz exposes new tools like RUSTYSHADE and RUSTYMOVE targeting governments.
Latest Technology News
Microsoft explicitly names 8 GB RAM as an optimization target for Windows 11, driven by soaring memory prices that force OEMs back to lower configs.

OpenAI found more AI agent containment escapes while probing the Hugging Face hack, and Anthropic disclosed three live-system breaches of its own.
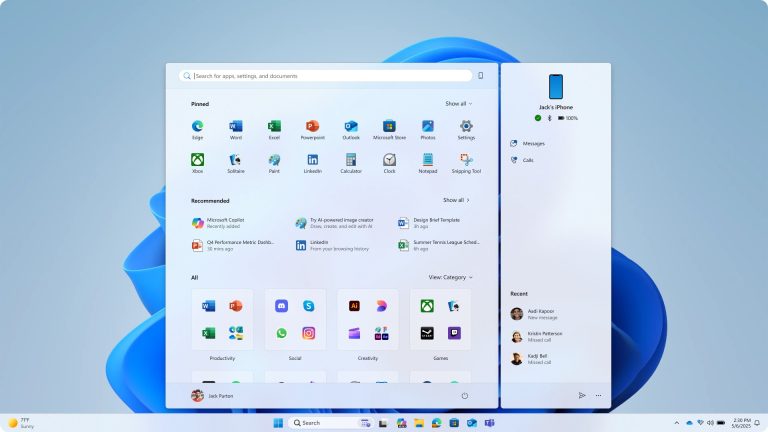
Microsoft outlines progress on its Windows 11 quality pledge: movable taskbar, cleaner search, trimmed AI bloat, and better File Explorer stability.
Google fixed 1,442 Chrome vulnerabilities across versions 149-151, surpassing the combined total of 23 prior releases, driven largely by AI-powered discovery.
The growing Reddit Google AI conflict highlights how AI Overviews crush organic traffic. Discover why Steve Huffman is rethinking their content partnership.
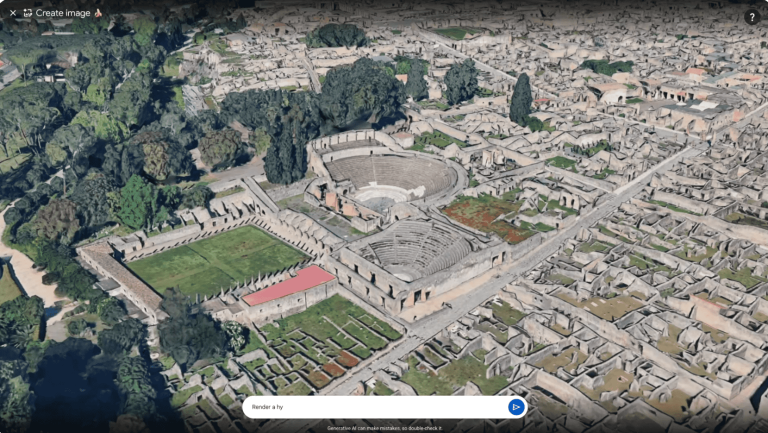
Google Earth AI withdrawal reveals the dangers of AI generated deepfake satellite imagery, prompting a swift rollback of the Nano Banana tool.
There is a category of vulnerability that almost every automated security tool is structurally incapable of finding,...
The FCC has banned the import and sale of new foreign-made robot vacuums in the US, citing broad definitions of advanced robotic devices and national security.
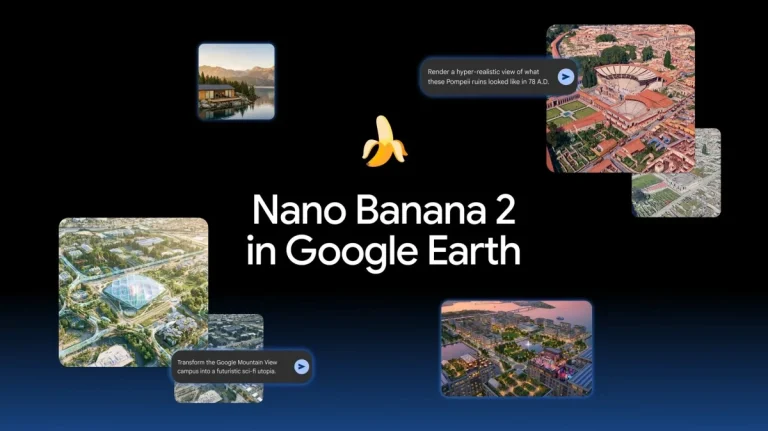
Google integrates its Nano Banana 2 AI image generator into Google Earth, allowing users to visualize historical scenes and future real estate projects.
Anthropic found three incidents where Claude cybersecurity evaluations reached the real internet and breached three organizations. Here's what happened.
Latest Security News
Pega patched a SAML authentication bypass in Pega Platform, rated Critical 9.5 and High 7.0. No CVE, no known compromise. See affected versions and fixes.
CISA warned of an exploited Zyxel switch vulnerability in GS1900 devices. Patch the Zyxel switch vulnerability now to prevent network compromise.
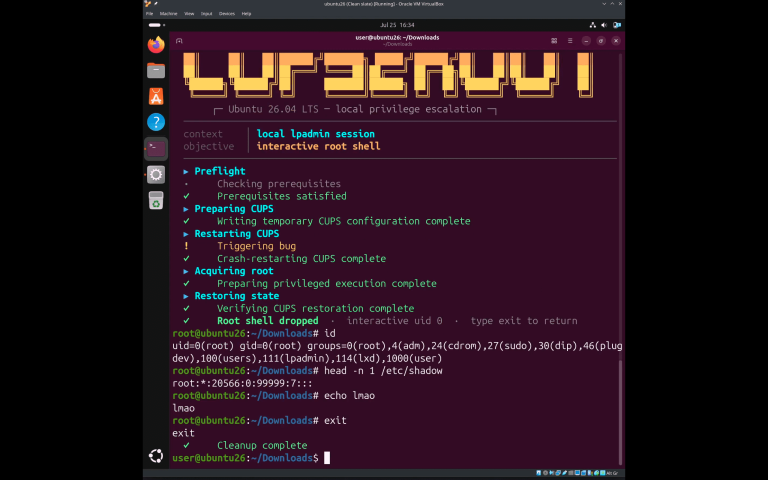
A public PoC exploit, cups2root, chains a CUPS privilege escalation to take lpadmin users to root. No CVE or patch yet. See the mechanism and mitigations.
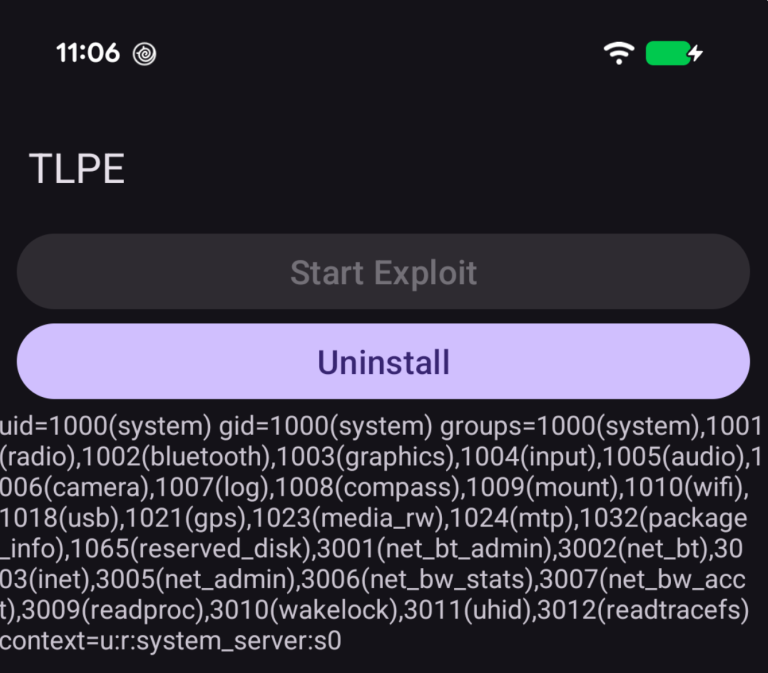
A critical Android Telecom vulnerability (CVE-2026-49881) allows remote code execution. Read the analysis and learn how to secure your device today.
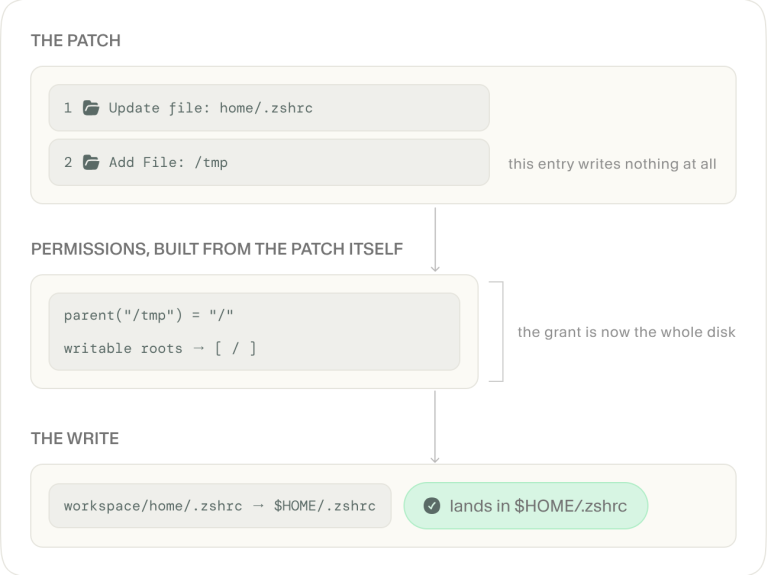
Discover the critical OpenAI Codex sandbox escape vulnerability. Learn how attackers bypass read-only modes and how to patch your CLI and desktop apps now.
Learn how the LLM-generated PhantomRaven information stealer targets developers. The PhantomRaven information stealer uses npm to hijack CI/CD secrets.
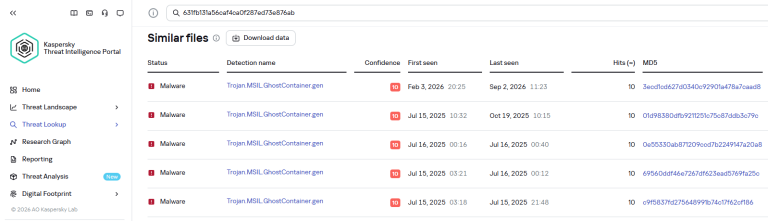
Learn how the NightEagle APT GhostContainer attacks exploit Exchange servers in Russia. Protect your network from the NightEagle APT.
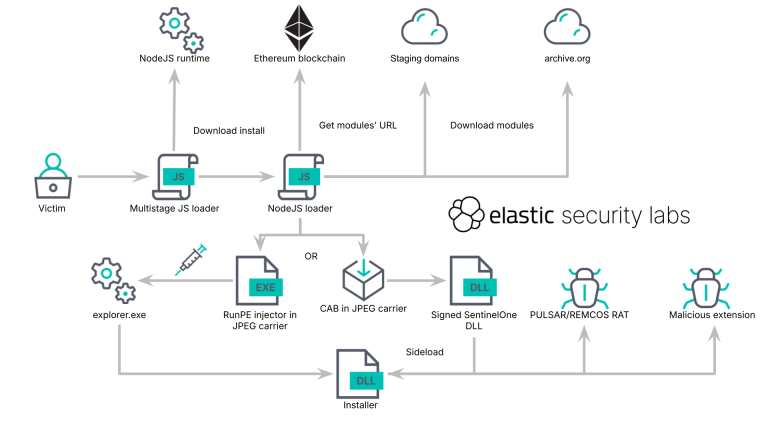
Learn how Brazilian KREMLIN banking malware steals credentials using fake browser extensions. Elastic Security Labs details the KREMLIN banking malware.
Discover how a Google undercover analyst successfully infiltrated the TeamPCP hacking gang to prevent massive supply chain attacks and secure corporate data.
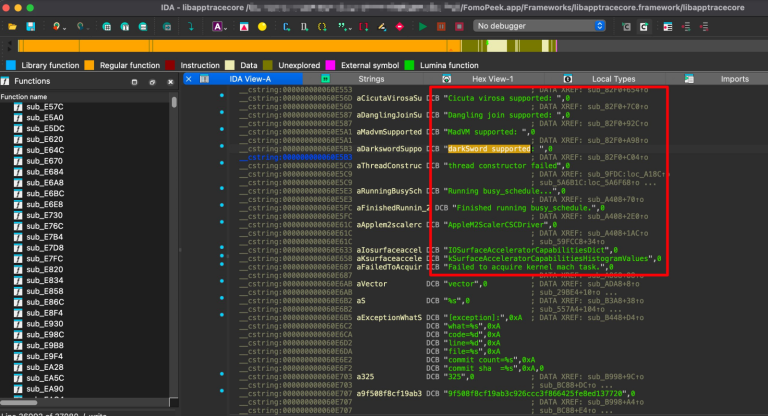
SlowMist warns the FomoPeek malware hides an iOS kernel exploit that steals crypto private keys and seed phrases. Update iOS and move funds now.
Multiple critical IBM Guardium vulnerabilities expose servers to remote attacks. Update to fix these IBM Guardium vulnerabilities and secure your data.
Critical MongoDB driver vulnerabilities, including CVE-2026-93762, expose systems to data loss and DoS. Learn about these flaws and patch immediately.
Latest Technology News
OpenAI found more AI agent containment escapes while probing the Hugging Face hack, and Anthropic disclosed three live-system breaches of its own.
Microsoft outlines progress on its Windows 11 quality pledge: movable taskbar, cleaner search, trimmed AI bloat, and better File Explorer stability.
Google fixed 1,442 Chrome vulnerabilities across versions 149-151, surpassing the combined total of 23 prior releases, driven largely by AI-powered discovery.
The growing Reddit Google AI conflict highlights how AI Overviews crush organic traffic. Discover why Steve Huffman is rethinking their content partnership.
Google Earth AI withdrawal reveals the dangers of AI generated deepfake satellite imagery, prompting a swift rollback of the Nano Banana tool.
There is a category of vulnerability that almost every automated security tool is structurally incapable of finding,...
The FCC has banned the import and sale of new foreign-made robot vacuums in the US, citing broad definitions of advanced robotic devices and national security.
Google integrates its Nano Banana 2 AI image generator into Google Earth, allowing users to visualize historical scenes and future real estate projects.
Anthropic found three incidents where Claude cybersecurity evaluations reached the real internet and breached three organizations. Here's what happened.
 cybernewswire