 Do Son
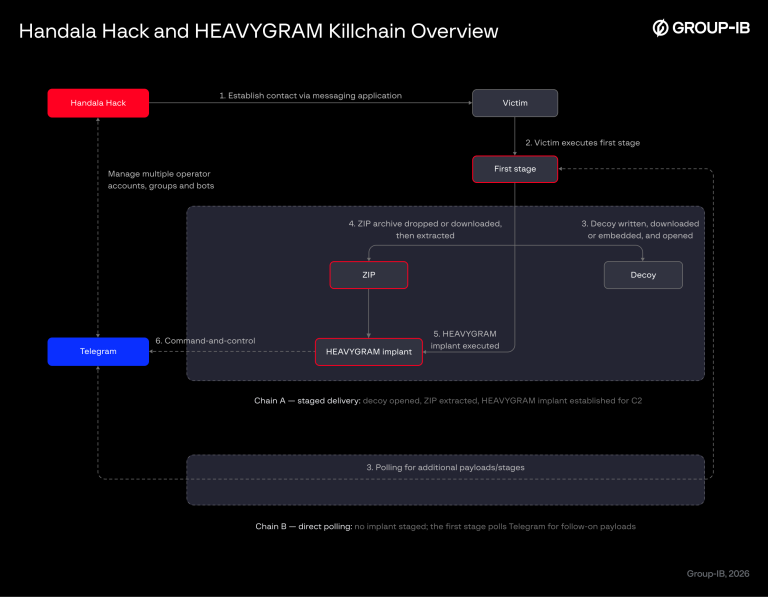
Group-IB uncovered Iranian HEAVYGRAM malware campaigns. The HEAVYGRAM malware abuses Telegram channels for command execution and data theft.
Latest Security News
An exploited VeloCloud vulnerability with a 10.0 CVSS score hits Arista appliances. Patch the critical VeloCloud vulnerability to stop active attacks.
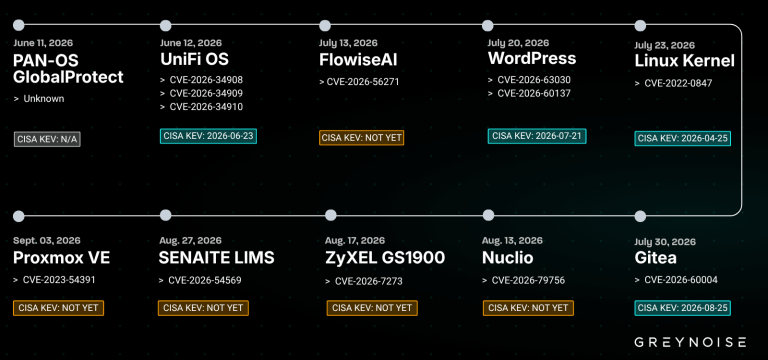
New Kapibala WordPress exploitation attacks steal records. GreyNoise warns that Kapibala WordPress exploitation hits governments.
Public PoC exploit details emerge for critical D-Link DIR-822A vulnerabilities. Learn how these D-Link DIR-822A vulnerabilities impact unpatched devices.
Pega patched a SAML authentication bypass in Pega Platform, rated Critical 9.5 and High 7.0. No CVE, no known compromise. See affected versions and fixes.
CISA warned of an exploited Zyxel switch vulnerability in GS1900 devices. Patch the Zyxel switch vulnerability now to prevent network compromise.
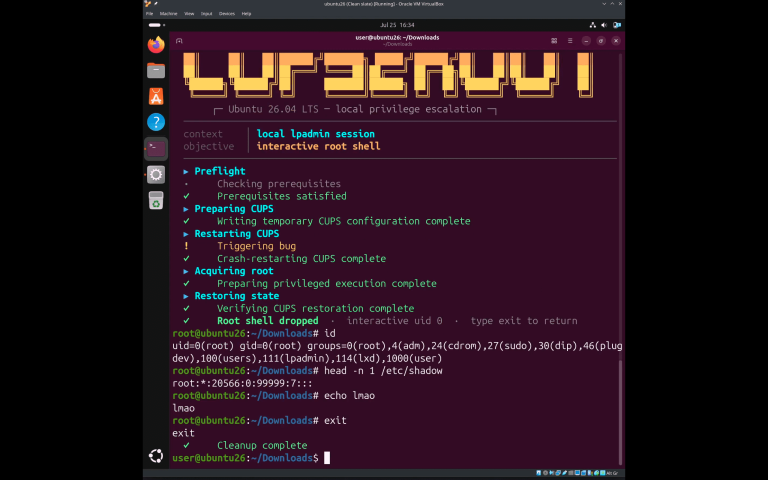
A public PoC exploit, cups2root, chains a CUPS privilege escalation to take lpadmin users to root. No CVE or patch yet. See the mechanism and mitigations.
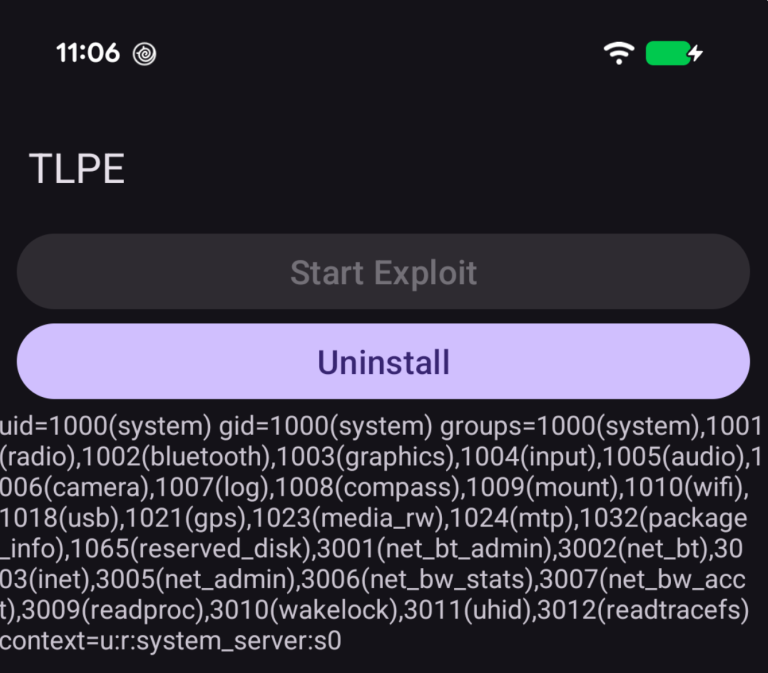
A critical Android Telecom vulnerability (CVE-2026-49881) allows remote code execution. Read the analysis and learn how to secure your device today.
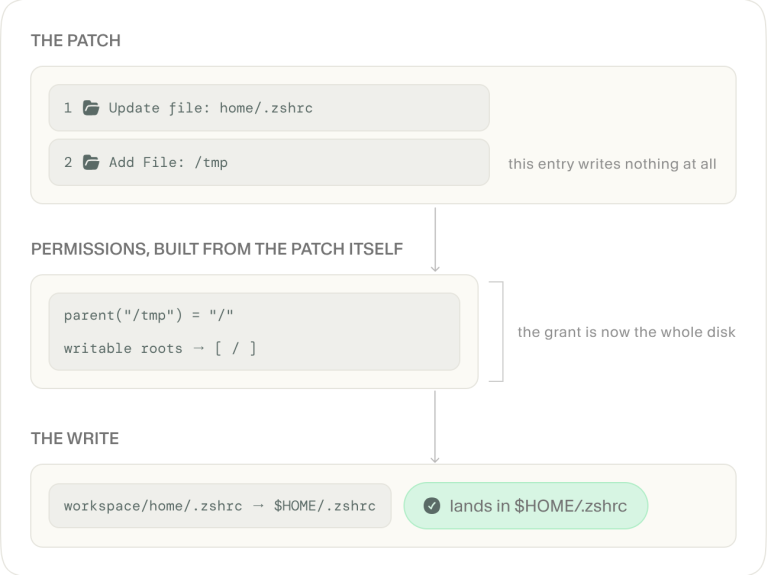
Discover the critical OpenAI Codex sandbox escape vulnerability. Learn how attackers bypass read-only modes and how to patch your CLI and desktop apps now.
Learn how the LLM-generated PhantomRaven information stealer targets developers. The PhantomRaven information stealer uses npm to hijack CI/CD secrets.
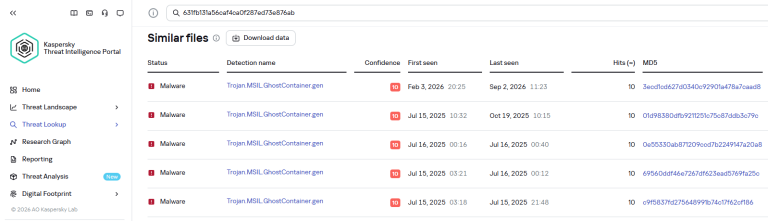
Learn how the NightEagle APT GhostContainer attacks exploit Exchange servers in Russia. Protect your network from the NightEagle APT.
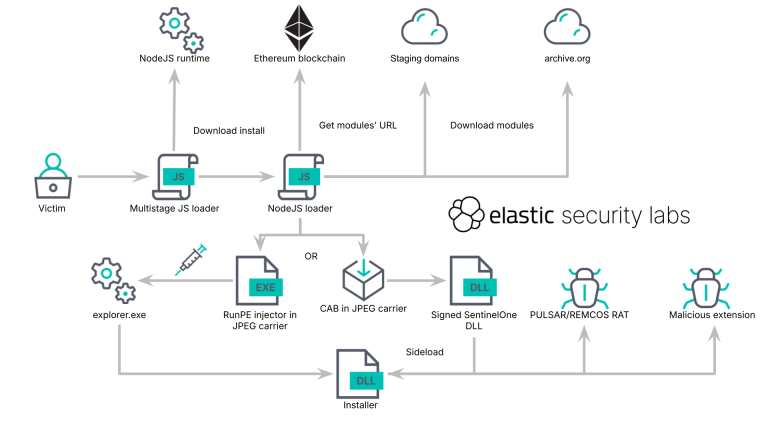
Learn how Brazilian KREMLIN banking malware steals credentials using fake browser extensions. Elastic Security Labs details the KREMLIN banking malware.
Latest Technology News
 cybernewswire
OpenAI is testing a 'Sign in with ChatGPT' feature across select platforms, enabling seamless single sign-on while preserving user account security.

Google's official Pixel 11 Pro teaser reveals a mysterious spinning colored light on the camera bar, hinting at advanced Gemini AI status integration.

Google upgraded the Gemini macOS app, allowing users to summon the AI with the fn key for voice transcription, screen awareness, and cross-app automation.


The Model Context Protocol (MCP) undergoes a massive update to a stateless architecture, eliminating session IDs and introducing multi-round requests.

Silver Spring, MD, USA, 28th July 2026, CyberNewswire

Microsoft's Project Perception is an agentic security system with red, blue, and green AI teams, reaching public preview on 3 August for the AI-attack era.

Moonshot AI open-weights Kimi K3, the first 3T-class open model, and reveals training agents that triggered kernel panics, prompting a microVM sandbox rebuild.

Windows 11 Experimental Future Platforms builds expire on 11 August, triggering time-bomb popups. Update to Build 29634.1000 to avoid forced alerts.
Latest Security News
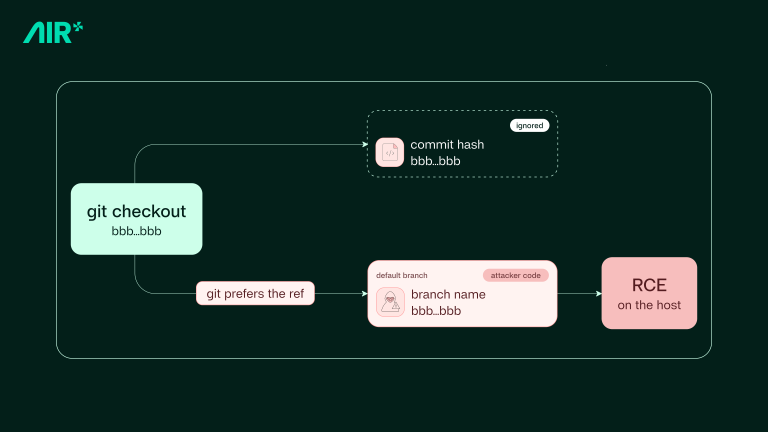
Plugin4Shell is a zero-click RCE hitting every major AI coding agent via a SHA pinning bypass. Claude Code and Codex are patched; Copilot and Gemini CLI are not.
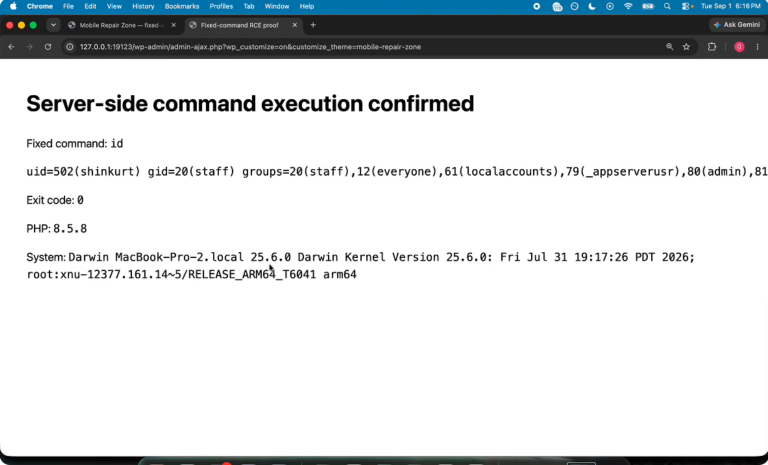
The WordPress Click2Shell vulnerability enables remote code execution via theme preview injection. Learn how this flaw works and update to version 7.1.1.
Exim 4.100.1 patches a serious Exim vulnerability set: Proxy Protocol heap flaws, a GnuTLS use-after-free, and SMTP smuggling (CVE-2026-94054). Upgrade now.
Critical IBM MQ vulnerabilities allow remote code execution. Learn how CVE-2026-10747 and CVE-2026-10858 hit 10.0 CVSS and require urgent patching.
CISA warned of exploited Linux kernel vulnerabilities in the KEV catalog. Patch these Linux kernel vulnerabilities to block privilege escalation.
Synology fixed 8 DSM vulnerabilities, including two critical unauthenticated flaws (CVE-2026-13684, CVE-2026-13639) on DiskStation Manager. Update now.
HCL Software patched critical HCL BigFix vulnerabilities, including CVE-2026-67100 and CVE-2026-18963. Patch now to prevent total account takeovers.
Four Linux kernel privilege escalation flaws were disclosed with public PoC exploits granting local root. Details and patches are now out. Update now.
Security researchers uncovered the new PAPERMILL cybercrime cluster. Learn how the PAPERMILL cybercrime cluster uses tax lures to deploy VenomRAT.
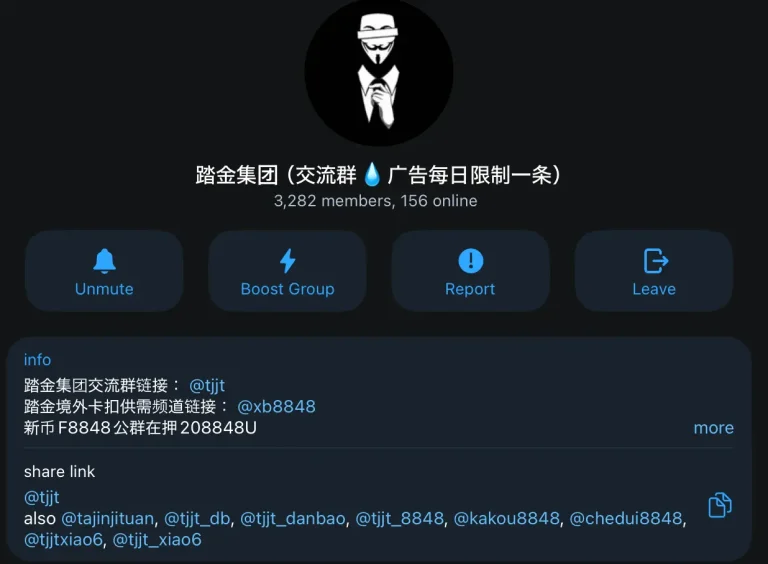
A new Tajin Group phishing network emerged on Telegram. Discover how Tajin Group money laundering fuels illicit guarantee marketplaces across the globe.
Google patched critical Google Chrome vulnerabilities. Update now to address multiple Google Chrome vulnerabilities like CVE-2026-93374 and stay secure.
A critical Dokploy OS command injection flaw exposes servers to root takeover via backups. Patch this Dokploy OS command injection now.
Latest Technology News
OpenAI is testing a 'Sign in with ChatGPT' feature across select platforms, enabling seamless single sign-on while preserving user account security.
Google's official Pixel 11 Pro teaser reveals a mysterious spinning colored light on the camera bar, hinting at advanced Gemini AI status integration.
Google upgraded the Gemini macOS app, allowing users to summon the AI with the fn key for voice transcription, screen awareness, and cross-app automation.
The Model Context Protocol (MCP) undergoes a massive update to a stateless architecture, eliminating session IDs and introducing multi-round requests.
Silver Spring, MD, USA, 28th July 2026, CyberNewswire
Microsoft's Project Perception is an agentic security system with red, blue, and green AI teams, reaching public preview on 3 August for the AI-attack era.
Moonshot AI open-weights Kimi K3, the first 3T-class open model, and reveals training agents that triggered kernel panics, prompting a microVM sandbox rebuild.
Windows 11 Experimental Future Platforms builds expire on 11 August, triggering time-bomb popups. Update to Build 29634.1000 to avoid forced alerts.

Google has quietly released a native Chrome for Linux Arm64 build with account sync and Widevine DRM, a boon for Raspberry Pi desktop users.