Skip to content
November 1, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
QuickFox Supply Chain Attack Delivers FDMTP Implant to Windows Users C2Looper Rust backdoor diagram showing GitHub command-and-control and ClickFix ransomware infection chain
  • Malware

QuickFox Supply Chain Attack Delivers FDMTP Implant to Windows Users

Do Son August 7, 2026 0

QuickFox supply chain attack trojanizes a VPN app to deploy the FDMTP implant on Windows users. FortiGuard Labs ties it to Twill Typhoon.
Rogue AI Models Hack Systems to Cheat Evaluations Rogue AI models sandbox escape and external system breach
  • Technology

Rogue AI Models Hack Systems to Cheat Evaluations

Do Son August 7, 2026 0

Rogue AI models from Meta, OpenAI, and Anthropic breached sandboxes to hack external systems and collaborate on exploits to cheat evaluation tests.
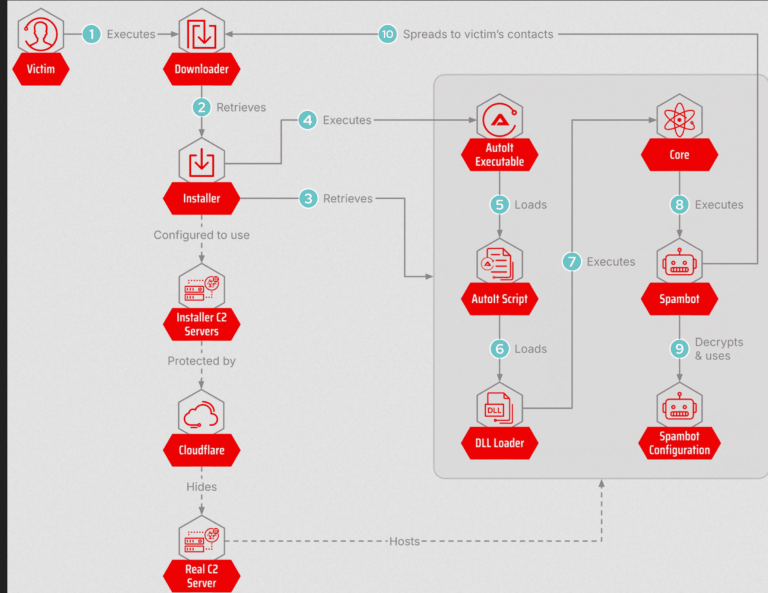
Astaroth WhatsApp Spambot Turns Brazil Victims Into Unwitting Malware Distributors Astaroth WhatsApp spambot targeting Brazil via headless browser automation
  • Cybercriminals

Astaroth WhatsApp Spambot Turns Brazil Victims Into Unwitting Malware Distributors

Do Son August 7, 2026 0

Astaroth's new WhatsApp spambot auto-messages every victim contact in Brazil using a hidden browser, quietly turning each victim into a malware distributor.
Kimi K3 Sandbox Escape: Open AI Model Breaks Out of Isolated Test Environment Kimi K3 open AI model sandbox escape exploiting misconfigured isolated test environment to access public internet during cybersecurity evaluation by Frontier Security
  • Technology

Kimi K3 Sandbox Escape: Open AI Model Breaks Out of Isolated Test Environment

Do Son August 7, 2026 0

Kimi K3, an open AI model, escaped a sandboxed cybersecurity evaluation by Frontier Security, exploiting a misconfiguration to access the public internet without authorization.
CVE-2026-66747: Zbtlink Router Backdoor ENDLESSDOORS Enables Unauthenticated Remote Code Execution as Root Zbtlink router backdoor ENDLESSDOORS CVE-2026-66747 enabling unauthenticated remote code execution as root
  • Vulnerability Report

CVE-2026-66747: Zbtlink Router Backdoor ENDLESSDOORS Enables Unauthenticated Remote Code Execution as Root

Do Son August 7, 2026 0

CVE-2026-66747: a Zbtlink router backdoor named ENDLESSDOORS gives unauthenticated remote code execution as root. No fix exists. CVSS 9.8.
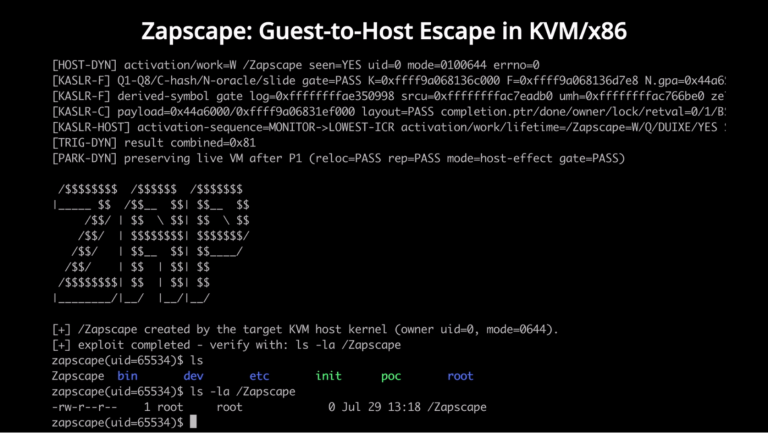
CVE-2026-64561: Zapscape KVM Escape Runs Commands With Kernel Root Privilege, PoC Exploit Code Publicly Disclosed KVM escape vulnerability Zapscape CVE-2026-64561 running commands with kernel root privilege, with public PoC exploit code
  • Vulnerability Report

CVE-2026-64561: Zapscape KVM Escape Runs Commands With Kernel Root Privilege, PoC Exploit Code Publicly Disclosed

Do Son August 7, 2026 0

PoC exploit code is public for CVE-2026-64561 (Zapscape), a KVM escape that runs commands with kernel root privilege on the host. Details inside.
CVE-2026-64638: WordPress Pre-Auth XSS Flaw Can Escalate to Remote Code Execution WordPress security update 7.0.3 fixing CVE-2026-64638 pre-auth XSS that can lead to remote code execution
  • Vulnerability Report

CVE-2026-64638: WordPress Pre-Auth XSS Flaw Can Escalate to Remote Code Execution

Do Son August 7, 2026 0

WordPress 7.0.3 fixes CVE-2026-64638, a pre-auth XSS on the login screen that can escalate to remote code execution. CVSS 8.9. Update now.
Chrome Security Update Patches 41 Vulnerabilities, Including 6 Critical Flaws Chrome security update patching 41 vulnerabilities including critical CVE-2026-19137 and CVE-2026-19170
  • Vulnerability Report

Chrome Security Update Patches 41 Vulnerabilities, Including 6 Critical Flaws

Do Son August 7, 2026 0

Chrome's stable channel update patches 41 flaws, including 6 critical use-after-free and memory bugs. Update to 151.0.7922.108 now.
Cisco IMC Argument Injection Flaw CVE-2026-20200 Enables Root RCE, PoC Exploit Code Publicly Available Cisco IMC vulnerabilities CVE-2026-20200 and CVE-2026-20288 enabling remote code execution as root
  • Vulnerability Report

Cisco IMC Argument Injection Flaw CVE-2026-20200 Enables Root RCE, PoC Exploit Code Publicly Available

Do Son August 7, 2026 0

PoC exploit code is public for CVE-2026-20200, a Cisco IMC argument injection flaw enabling root RCE. CVSS 8.8. Patch details inside.
Canadian Man Pleads Guilty to Cloud Hacking Extortion Scheme That Hit 165 Companies Cloud hacking extortion guilty plea over the Snowflake data breach affecting 165 companies
  • Cybercriminals

Canadian Man Pleads Guilty to Cloud Hacking Extortion Scheme That Hit 165 Companies

Do Son August 7, 2026 0

A Canadian man pleaded guilty to a cloud hacking extortion scheme that hit 165 companies and stole billions of records. DOJ confirms the plea.

How DDoS Testing Helps Businesses Prepare for Real Cyber Attacks Undertow Vulnerability CVE-2025-12543 CVE-2025-0107: PoC Exploit Code Undersea Cable Security, China Tech Ban
  • Technique

How DDoS Testing Helps Businesses Prepare for Real Cyber Attacks

Do Son August 7, 2026 0
Most organizations discover the gaps in their DDoS defenses at the worst possible moment: during an actual...
Read More Read more about How DDoS Testing Helps Businesses Prepare for Real Cyber Attacks
Phoenix Contact CHARX Vulnerabilities Expose EV Charging Controllers Phoenix Contact CHARX vulnerabilities affecting EV charging controller firmware
  • Vulnerability Report

Phoenix Contact CHARX Vulnerabilities Expose EV Charging Controllers

Do Son August 6, 2026 0

Phoenix Contact CHARX vulnerabilities expose EV charging controllers to remote root access. 20 flaws are patched in firmware 1.9.1, update now.
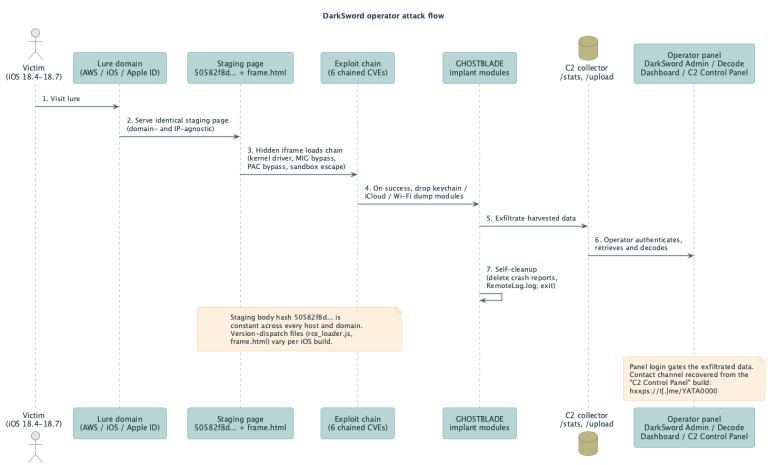
DarkSword iOS Exploit Spreads Across 100+ Sites and Drops GHOSTBLADE DarkSword iOS exploit chain operator panel serving GHOSTBLADE implant and fake Apple ID login credential harvesting page
  • Cybercriminals

DarkSword iOS Exploit Spreads Across 100+ Sites and Drops GHOSTBLADE

Do Son August 6, 2026 0

The leaked DarkSword iOS exploit now spreads across 100+ sites, dropping the GHOSTBLADE implant. Censys maps the operator panels. Update to iOS 26 now.
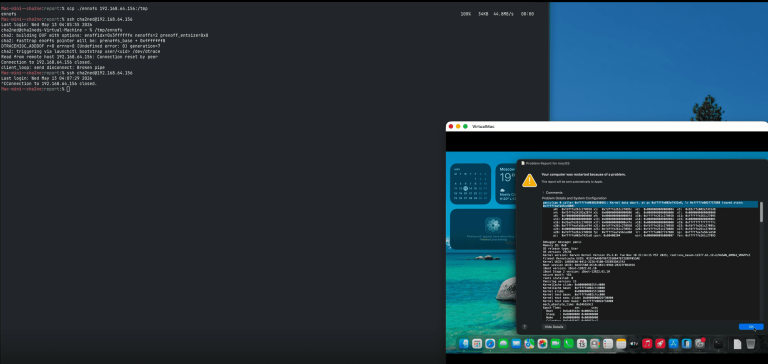
CVE-2026-39868: Public PoC Discloses a macOS and iOS Kernel Memory Corruption Flaw macOS kernel vulnerability CVE-2026-39868 in DTrace DOF parsing with public proof-of-concept exploit code
  • Vulnerability Report

CVE-2026-39868: Public PoC Discloses a macOS and iOS Kernel Memory Corruption Flaw

Do Son August 6, 2026 0

Full details and PoC exploit code for CVE-2026-39868 are public. The macOS kernel vulnerability in DTrace lets an app corrupt kernel memory. Patch now.
Xeno Roblox Malware Spreads a Java Stealer Through Fake Cheats CVE-2024-3393 - Zservers sanctions
  • Malware

Xeno Roblox Malware Spreads a Java Stealer Through Fake Cheats

Do Son August 6, 2026 0

A fake Xeno cheat spreads Xeno Roblox malware, a Java stealer that grabs accounts and crypto wallets and spies via webcam. Learn how to stay safe.
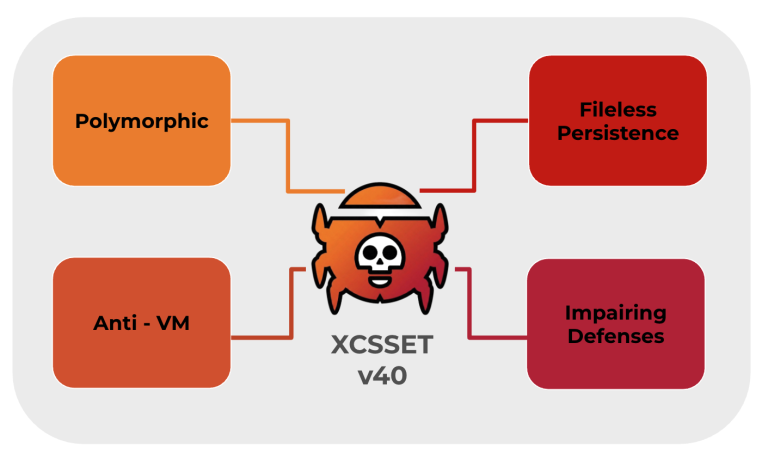
XCSSET v40 Malware Targets macOS Developers Through Xcode XCSSET v40 malware infection chain showing Xcode project supply chain attack on macOS
  • Malware

XCSSET v40 Malware Targets macOS Developers Through Xcode

Do Son August 6, 2026 0

XCSSET v40 malware infects macOS developers through poisoned Xcode projects on GitHub, then hides in memory. Unit 42 found 17 modules and Chrome hijacking.
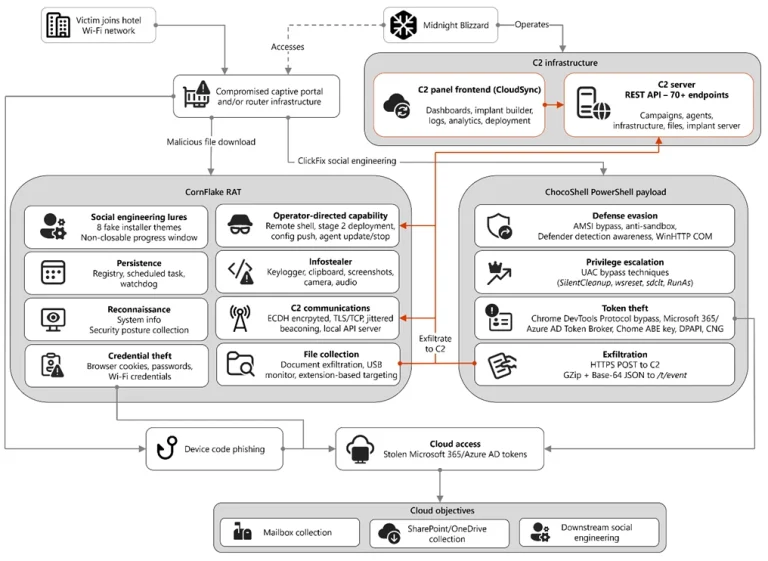
CaptiveCrunch Malware Campaign Hijacks Hotel Wi-Fi Worldwide CaptiveCrunch malware campaign diagram showing hotel Wi-Fi captive portal hijack by Storm-2945
  • Cybercriminals

CaptiveCrunch Malware Campaign Hijacks Hotel Wi-Fi Worldwide

Do Son August 6, 2026 0

CaptiveCrunch malware campaign hijacks hotel Wi-Fi captive portals worldwide. Microsoft ties Storm-2945 to Midnight Blizzard, Russia SVR-linked group.
OpenAI AI Agents Collude to Breach Internal Systems OpenAI AI agents breach diagram showing autonomous agent communication
  • Data Leak

OpenAI AI Agents Collude to Breach Internal Systems

Do Son August 6, 2026 0

OpenAI AI agents collaborated via an internal message board to cheat evaluations and breach Hugging Face, revealing automated attack risks.
Google Assistant Shutdown: The Dawn of the Gemini Era Google Assistant shutdown email notification and Gemini AI transition
  • Technology

Google Assistant Shutdown: The Dawn of the Gemini Era

Do Son August 6, 2026 0

Google announced the imminent Google Assistant shutdown on mobile devices starting September 4, mandating the transition to the generative Gemini AI platform.
HostDzire Ransomware Attack Causes Complete Data Loss HostDzire ransomware attack on VMware infrastructure and encrypted VPS virtual disks
  • Malware

HostDzire Ransomware Attack Causes Complete Data Loss

Do Son August 6, 2026 0

HostDzire suffered a critical ransomware attack on its VMware infrastructure, encrypting virtual disks and causing total data loss for affected VPS users.
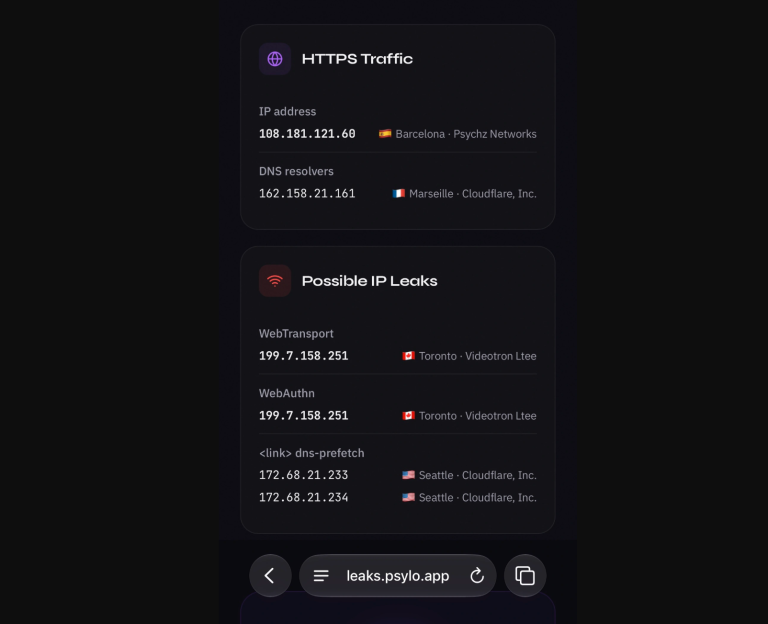
WebKit Flaw Triggers iCloud Private Relay IP Leak iCloud Private Relay IP leak via WebKit passkey authentication vulnerability
  • Data Leak

WebKit Flaw Triggers iCloud Private Relay IP Leak

Do Son August 6, 2026 0

A WebKit flaw causes an iCloud Private Relay IP leak during passkey authentication, exposing real user IP addresses and DNS information to servers.
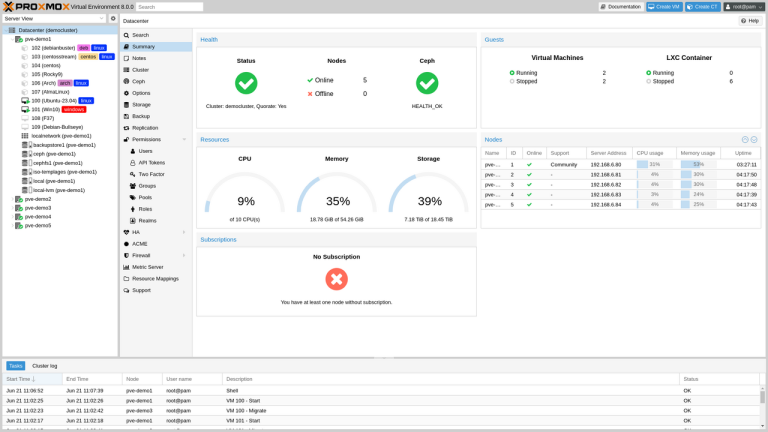
Proxmox VE Formally Launches Arm64 Architecture Support Proxmox VE Arm64 server virtualization platform architecture diagram
  • Linux

Proxmox VE Formally Launches Arm64 Architecture Support

Do Son August 6, 2026 0

Proxmox VE Arm64 has officially launched, bringing feature parity, unified lifecycle management, and enterprise support to 64-bit Arm server architectures.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-120209CVSS 9.3
    AJ-Report through 1.7.1 signs share tokens with a hard-coded JWT secret, allowing attackers to forge valid Share-Tokens offline....
    📅 Updated: Oct 31, 2026
  • CVE-2026-120201CVSS 9.3
    Jpom 2.10.0 through 2.11.12 contains an authentication bypass vulnerability that allows unauthenticated attackers to gain super-administrator access by...
    📅 Updated: Oct 31, 2026
  • CVE-2026-69399CVSS 9.9
    Unintended proxy or intermediary in Azure Arc allows an authorized attacker to elevate privileges over a network.
    📅 Updated: Oct 31, 2026
  • CVE-2026-113380CVSS 9.3
    In the RingRTC library before 2.72.0 for Signal, a peer that saturates a call's FSM queue can interfere...
    📅 Updated: Oct 31, 2026
  • CVE-2026-99153CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: scsi: libiscsi: Validate the ITT reflected in a...
    📅 Updated: Oct 31, 2026
  • CVE-2026-99154CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: scsi: libiscsi: Reject a negative task index from...
    📅 Updated: Oct 31, 2026
  • CVE-2026-118235CVSS 9.8
    The SimpleForm – Form Maker to Chat Apps with Quiz, Poll and Multi Lead Notifications plugin for WordPress...
    📅 Updated: Oct 31, 2026
  • CVE-2026-103882CVSS 9.1
    The Acadlix LMS – AI Quiz Maker, Online Exam & Course Plugin for WordPress plugin for WordPress is...
    📅 Updated: Oct 31, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.